How are software updates managed in a virtual desktop?
Software updates in a virtual desktop are managed centrally, allowing administrators to test patches, schedule their deployment and apply them consistently across users’ virtual machines. Updates can be prioritised according to security and business requirements, with compatibility checks and monitoring used to reduce disruption.
Software updates in a virtual desktop are managed through the desktop platform’s underlying images, application packages and user policies, rather than by updating each physical computer separately. This gives administrators control over what is installed, which users receive it, and how the environment is returned to a known working state if an update causes a problem.
The process normally starts with an inventory of the software used in the environment. This identifies operating system components, business applications, plug-ins, drivers and supporting services, along with their owners and dependencies. Keeping this information current helps distinguish essential security updates from optional feature releases and makes it easier to identify systems that need special handling.
Most virtual desktop environments use a controlled base image. The image contains the operating system, core configuration and software shared by a group of users. When the approved version of that image is published, new virtual desktops can be built from it and existing desktops can be refreshed or updated according to the organisation’s chosen operating model. This avoids relying on undocumented changes made separately within individual desktops.
Applications may be managed separately from the base image. A packaged application can be replaced with a newer version without rebuilding every part of the desktop, provided its dependencies and configuration are supported. This approach is useful where different teams need different applications or where an application has a separate release cycle from the operating system. User-specific applications may require an additional policy so that staff do not install conflicting or unauthorised versions.
A well-managed update process usually includes the following controls:
- Change records: each update is recorded with its version, purpose, affected components, dependencies and implementation instructions.
- Release groups: users or desktops can be divided into controlled groups so that an update is introduced in stages rather than to the whole environment at once.
- Configuration control: settings, policies and application versions are maintained as part of the approved desktop configuration.
- Session management: users are informed when a sign-out or restart is required, with policies determining how active sessions and unsaved work are handled.
- Validation checks: administrators confirm that the updated desktop starts correctly, required applications launch, profiles load and key business functions remain available.
- Recovery procedures: the previous image or application package is retained where practical so that the change can be reversed if a defect is identified.
Security updates are generally treated differently from feature updates. A vulnerability affecting the operating system or an installed application may need a more urgent assessment, while a feature release can be reviewed for operational value before it is introduced. The decision should consider the severity of the issue, the exposure of the affected service, available vendor guidance, application dependencies and the organisation’s risk policy.
Updates also need to account for user profiles and business data. In a properly designed virtual desktop, documents and personal settings are usually stored separately from the disposable operating system layer. This means the desktop image can be replaced without treating the update as a migration of the user’s files. The exact behaviour depends on the environment, so profile storage, mapped resources, local caches and application data should be included in the update assessment.
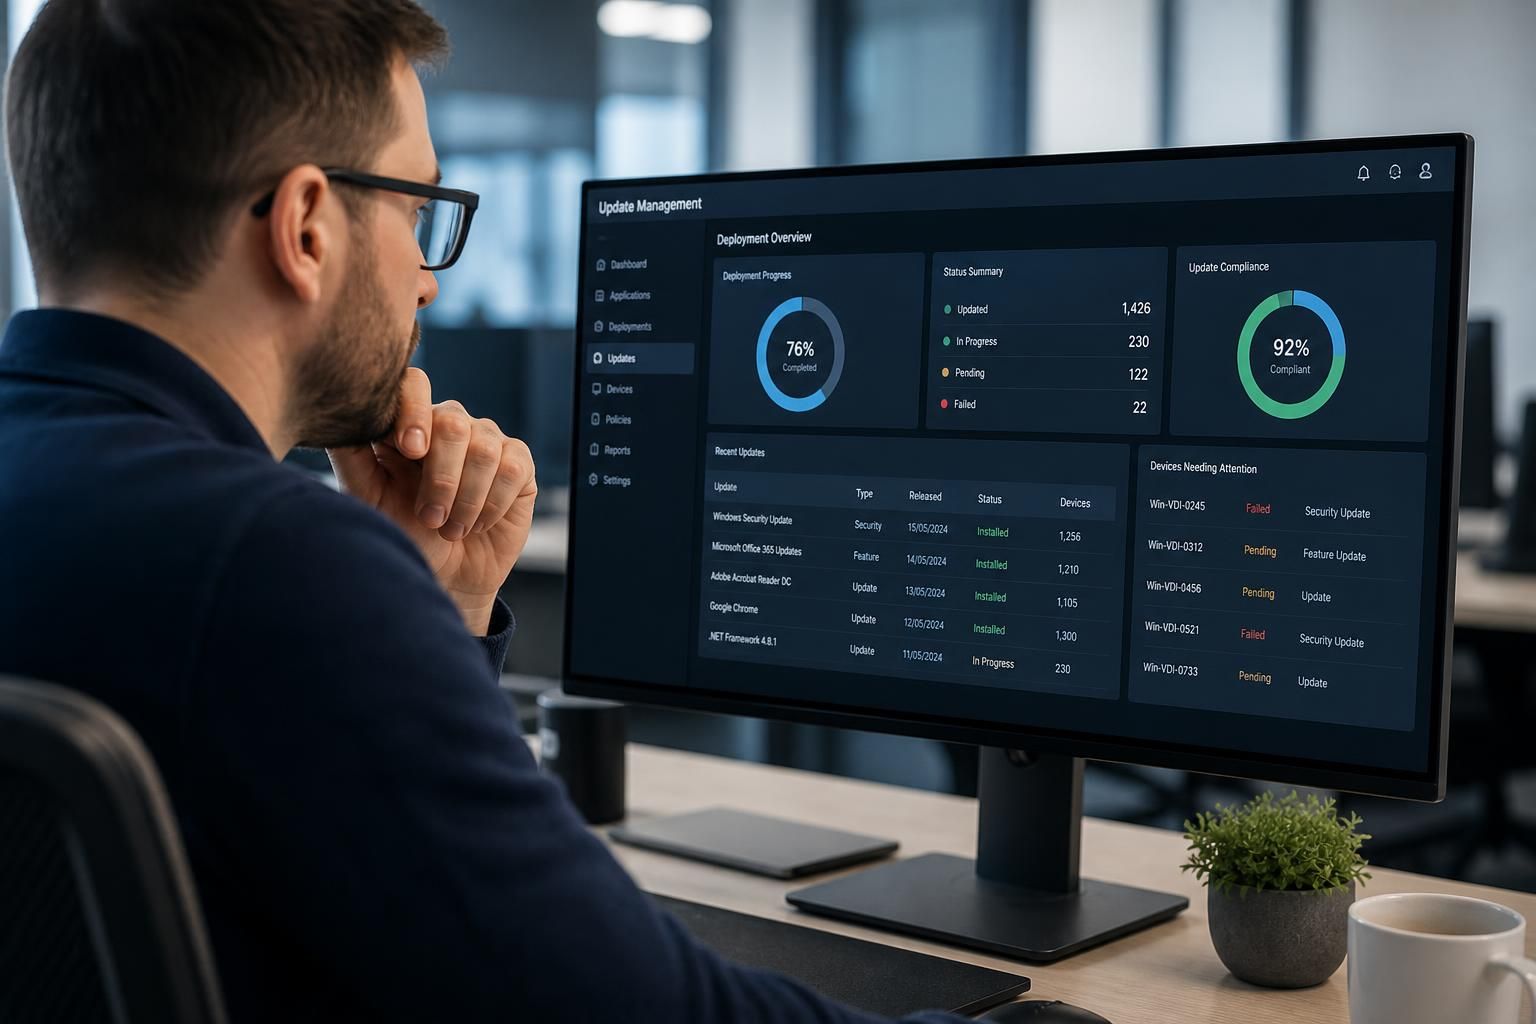
After deployment, administrators review more than whether the update installed successfully. They can examine installation records, failed sessions, application launch errors, resource consumption and user support incidents. A change that completes technically but causes printing, authentication, peripheral or line-of-business application issues still needs investigation. Clear records make it easier to identify a common cause and remove or revise the affected package.
Some software cannot be updated in the same way as a standard desktop application. Older applications, specialist peripherals, tightly coupled databases and software with restrictive licensing may need a separate virtual desktop group or a different packaging method. Exceptions should be documented rather than handled through unrecorded manual changes, because unmanaged alterations make later updates and troubleshooting less predictable.
For a small business, the practical objective is to create a repeatable update process that balances security, compatibility and user disruption. This normally involves maintaining an accurate software inventory, separating shared desktop components from user data, documenting changes, retaining a recovery option and reviewing the environment after each release. A managed IT provider can help define these controls and align them with the organisation’s applications, access requirements and risk tolerance.
Update scheduling determines when an approved software change becomes available to users and how much control they have over its installation. Administrators typically plan routine updates around business activity, avoiding periods such as month-end processing or production deadlines. This reduces the chance that a restart, sign-out or temporary application interruption affects important work.
A practical schedule may include a maintenance window, advance user notifications and a final installation deadline. Limited deferrals can give staff time to save work, while preventing updates from being postponed indefinitely. Urgent security patches may follow a shorter approval route, but should still be recorded with the reason for the expedited deployment. Reviewing missed installations and deferred updates helps administrators identify desktops that need attention without changing the approved software configuration manually.