
Cyber Security Services for SMEs
Cyber security services for SMEs combine risk assessment, security controls, monitoring and incident planning to protect business systems, users and data. S2 Technology Group can also support an IT ticketing system and asset management approach, improving visibility of technology-related risks.
What Effective Cyber Security Delivers for SMEs
For SMEs, the value of cyber security is measured through practical business outcomes: clearer priorities for investment, safer user behaviour, stronger governance evidence, fewer avoidable weaknesses, and a more structured basis for managing technology-related risk as the organisation grows.
A Clearer View of Security Risk
Risk assessments, asset records and ticketing information help identify which systems, users and data require the most attention, giving SMEs a more structured basis for security decisions.
Fewer Unmanaged Weaknesses
Ongoing review of systems and security controls helps uncover outdated configurations, unaddressed vulnerabilities and gaps in access management before they become harder to manage.
Safer User Practices
Security guidance and awareness measures help staff recognise suspicious messages, protect account credentials and handle business information according to agreed processes.
Better Protection for Business Data
Appropriate security controls reduce the likelihood of unauthorised access to business systems, customer information and operational data across office, cloud and remote environments.
A Defined Incident Process
Incident planning establishes what should happen when a security event is suspected, including how to assess the issue, limit its impact and coordinate the next steps.
Stronger Governance Evidence
Documented policies, assessments, asset information and security actions give an SME clearer evidence of how technology risks are identified, reviewed and managed.
More Consistent Security as the Business Grows
A structured cyber security approach makes it easier to apply suitable controls when the organisation adds users, devices, locations, cloud services or remote access requirements.
Practical Cyber Security Guidance for Your Business
Cyber security for an SME is a practical discipline that connects technology, people and business processes. Effective protection depends on understanding how staff work, where important information is held, and which activities would be most disruptive if compromised.
S2 Technology Group takes time to explain technical issues in clear terms, so business owners and employees can make informed decisions. Advice should reflect the organisation’s size, working practices and future plans rather than apply a generic checklist.
Good security also depends on everyday habits. Clear guidance, sensible access arrangements and constructive support help employees recognise potential problems and report concerns. This people-focused approach makes cyber security easier to manage as the business develops.
Specialist Cyber Security Expertise for SMEs
Cyber security for SMEs requires more than individual protective tools; it involves aligning identity management, device configuration, software maintenance, data handling and governance with the organisation’s actual operating model. S2 Technology Group brings these areas together to provide informed guidance on how security decisions affect users, infrastructure and business continuity.
A structured IT ticketing system and asset management process can strengthen this work by linking devices, users, changes and reported issues in one auditable record. This gives security decisions a reliable operational context, helping distinguish known assets and approved changes from unmanaged technology that may require investigation.
S2 Technology Group applies specialist IT knowledge to assess how security measures fit within wider support and infrastructure arrangements. Its approach considers technical dependencies as well as governance requirements, enabling growing organisations to develop security practices that remain understandable, maintainable and proportionate to their environment.
Questions to Ask Before Choosing SME Cyber Security Services
How Does an SME Cyber Security Provider Test Its Incident Response Plan?
Choose a provider that documents ownership, escalation routes, evidence requirements and review points. Clear accountability makes security decisions traceable and helps management assess whether controls remain appropriate as risks change.
How Does an SME Cyber Security Provider Prioritise Security Vulnerabilities?
An effective process ranks vulnerabilities by exploitability, business impact, asset importance, exposure and available remediation. It then assigns owners, records decisions and revisits priorities when systems, threats or circumstances change.
How Does an SME Cyber Security Provider Manage Supply Chain Risk?
Supply chain risk management examines suppliers’ access, security practices, dependencies and incident obligations. Due diligence, contractual controls, least-privilege access and periodic review help SMEs manage risks beyond their direct business technology environment.
How Does an SME Cyber Security Provider Assess Identity and Access Controls?
Assessment of identity and access controls examines privileged accounts, authentication, permissions, joiner-mover-leaver processes and review evidence. It should identify excessive access, dormant accounts and weak authentication, aligning permissions with responsibilities.
How Does an SME Cyber Security Provider Measure Security Awareness?
Security awareness is measured through training completion, simulated exercise outcomes, reporting behaviour, policy understanding and recurring mistakes. Results should inform targeted education while respecting privacy and avoiding blame or embarrassment.
Risk-Led Protection
Linking cyber security advice with an IT ticketing system and asset management process gives SMEs auditable view of technology-related risk.
Organisations We Support with Cyber Security
Professional Services Organisations
Professional services firms often manage confidential client information through email, cloud applications and shared document systems. Cyber security guidance can focus on account protection, access permissions, secure file handling and practical steps for identifying suspicious activity.
Manufacturing Businesses
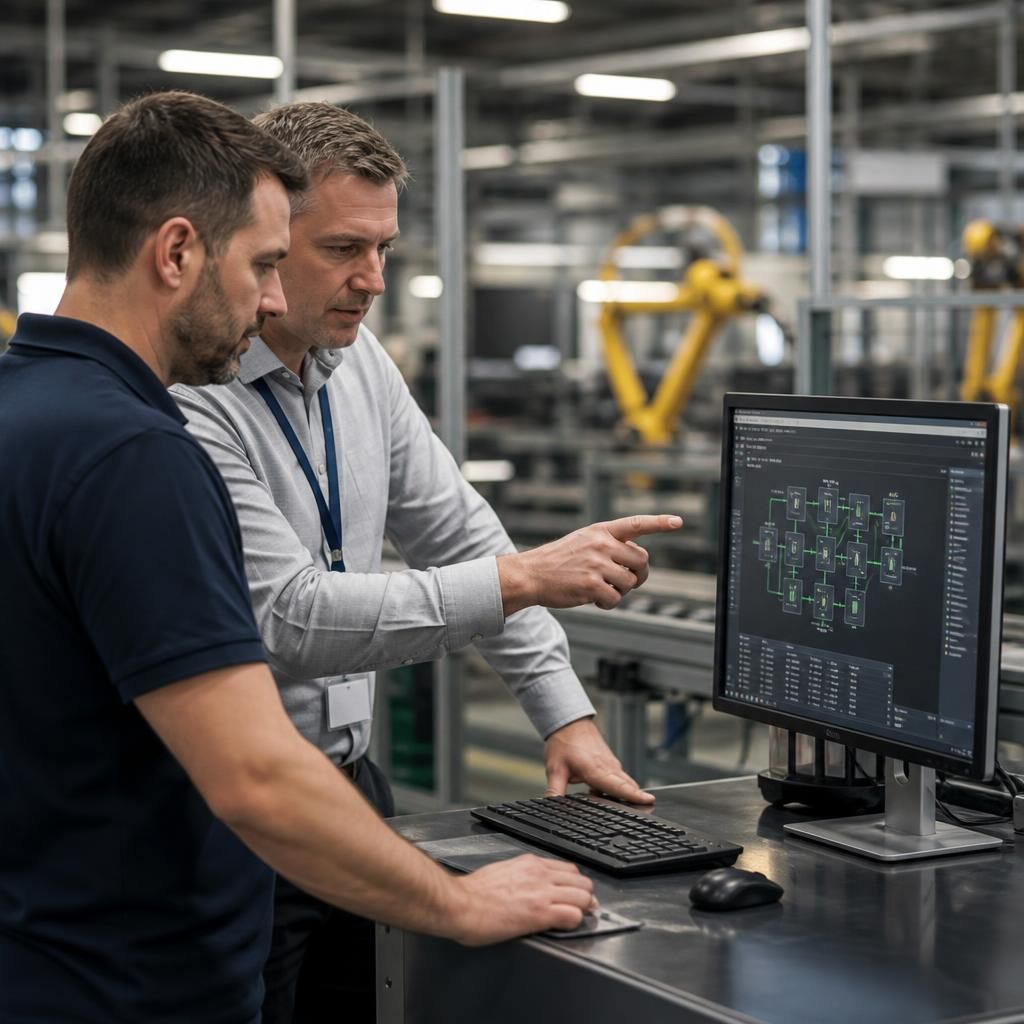
Manufacturing environments may connect office technology with operational systems, suppliers and production processes. Security planning should consider user access, device visibility, network separation and incident procedures that reduce disruption to important business activities.
Logistics Organisations
Logistics businesses depend on connected systems for coordinating people, vehicles, suppliers and customer information. A structured cyber security review can examine account controls, remote access, asset records and the handling of operational data across the organisation.
Multi-Site Businesses
Organisations with several offices or operational locations need consistent security controls without overlooking local differences. Useful measures include clear access responsibilities, reliable asset information, secure connectivity and documented incident planning for each site.
Cyber Security Support for Common SME Challenges
Cyber security services for SMEs can be shaped around the way an organisation operates, whether it is reviewing its current controls, introducing cloud applications, supporting remote users, or strengthening protection for sites, devices and sensitive business information.
Reviewing Existing Security Controls
Suitable for SMEs that need to understand current cyber risks, identify control gaps and establish practical priorities for improving protection.
Introducing Cloud Applications
Supports businesses adopting cloud services by considering account security, access permissions, data handling and the risks associated with connected applications.
Supporting Remote and Mobile Users
Helps organisations assess how employees access systems and information away from the office, including authentication, device use and secure working practices.
Protecting Sensitive Business Information
Relevant to businesses handling confidential client, employee, financial or operational data that requires appropriate access controls and security processes.
Securing Multiple Sites and Devices
Fits organisations with several premises, shared systems or a growing device estate that need a consistent view of technology-related security risks.
Preparing for Security Incidents
Useful for SMEs that want to define how suspected breaches, compromised accounts or other cyber security concerns should be identified, recorded and managed.
Cyber Security Questions Answered
What Should an SME Cyber Security Policy Include?
SMEs need cyber security because attackers target weaknesses in accounts, devices, applications and processes, not company size; proportionate controls reduce exposure while supporting compliant, dependable day-to-day operations and business continuity.
How Can SMEs Protect Business Email From Cyber Threats?
Protect business email with multi-factor authentication, strong password policies, phishing awareness, configuration, and verified backup procedures. Email filtering and domain authentication records can also reduce spoofing and malicious message delivery.
How Should SMEs Secure Devices Used Away From the Office?
Secure devices used away from the office through encryption, screen locks, automatic updates, endpoint protection, restricted administrator rights, secure connections, and remote-wipe capability, supported by clear user procedures for staff.
How Should SMEs Protect Backups From Cyber Threats?
Protect backups by separating them from everyday systems, restricting access, encrypting copies, testing restoration, retaining versions, and documenting recovery procedures so ransomware or accidental deletion does not destroy recovery options.
How Can SMEs Detect Suspicious Activity Across Business Systems?
Detection relies on centralised logs, endpoint alerts, authentication records and network activity. Correlating events helps distinguish unusual behaviour from routine activity, while documented escalation routes support timely investigation of incidents.