
How does cloud computing support business compliance requirements?
Cloud computing supports business compliance by providing controlled access, encryption, audit logs, data-retention settings and documented security processes that help organisations manage and evidence how information is handled. Compliance is not automatic, however: the business remains responsible for selecting suitable cloud services, configuring them correctly and applying the controls required by relevant laws, regulations and contractual obligations.
Cloud computing supports business compliance by turning many information-handling requirements into repeatable processes that can be governed, reviewed and evidenced. It can help an organisation apply consistent policies across users, devices, applications and locations, but compliance still depends on the business choosing an appropriate service, understanding its responsibilities and operating the environment properly.
The starting point is to identify which obligations apply to the organisation. These may arise from the UK GDPR and Data Protection Act 2018, sector-specific rules, customer contracts, insurance conditions or internal governance policies. The relevant requirements depend on the type of information being processed, the organisation’s role, where people are located and how data is shared. Cloud adoption should therefore follow a documented assessment rather than an assumption that a well-known service is automatically suitable.
A useful compliance assessment considers:
- what personal, confidential, financial or commercially sensitive information is stored;
- which people and systems need to use it, and for what business purpose;
- how information enters, moves through and leaves the cloud service;
- which provider, subcontractors or integrated applications can process it;
- where data and backups are held, including any international transfers; and
- how information should be returned, archived or securely removed when it is no longer required.
Cloud provider due diligence is also important. Organisations should review the provider’s security documentation, service terms, data-processing arrangements, sub-processor information, incident procedures and approach to service changes. Contracts should clearly define responsibilities and address matters such as confidentiality, assistance with data-subject requests, breach notification, data return, deletion and the organisation’s ability to obtain appropriate assurance.
This is commonly described as the shared-responsibility model. The provider may secure the underlying infrastructure and operate parts of the platform, while the customer remains responsible for its users, business data, configurations, connected systems and internal procedures. The division varies between infrastructure, platform and software services, so it should be recorded for each service rather than treated as a general assumption.
Cloud environments can also support privacy governance. For example, a business can document the purpose for processing information, restrict unnecessary collection, assess higher-risk processing and maintain procedures for access, correction, deletion and other data-subject requests. A data protection impact assessment may be appropriate where proposed processing is likely to create a significant risk to individuals. Cloud design should support these obligations instead of making them dependent on informal actions by individual employees.
Compliance evidence needs to be maintained throughout the service lifecycle. Useful records can include the approved service assessment, configuration standards, responsibility matrix, supplier reviews, risk assessments, policy exceptions, training records, incident documentation and periodic control reviews. Evidence should show not only that a policy exists, but that it is applied, checked and updated when the service, threat environment or regulatory position changes.
Change management is particularly relevant because cloud services are frequently updated and connected to other platforms. New integrations, altered permissions, additional storage locations or changes to processing purposes can affect the organisation’s compliance position. A controlled review before significant changes helps identify whether contracts, privacy notices, risk assessments, technical safeguards or internal procedures also need updating.
Cloud computing does not by itself provide legal compliance or guarantee that an organisation will pass an audit. Misconfigured services, excessive permissions, unmanaged integrations, unsupported devices and unclear ownership can still create compliance failures. Regular reviews should test whether the documented controls match the live environment and whether staff understand the processes they are expected to follow.
A managed IT partner can help by documenting the cloud environment, mapping responsibilities, reviewing configurations and coordinating technical evidence with the organisation’s policies. The business must still decide which legal and contractual requirements apply, approve its risk position and ensure that operational practices reflect those requirements. The strongest approach treats cloud compliance as an ongoing governance process rather than a one-off setup task.
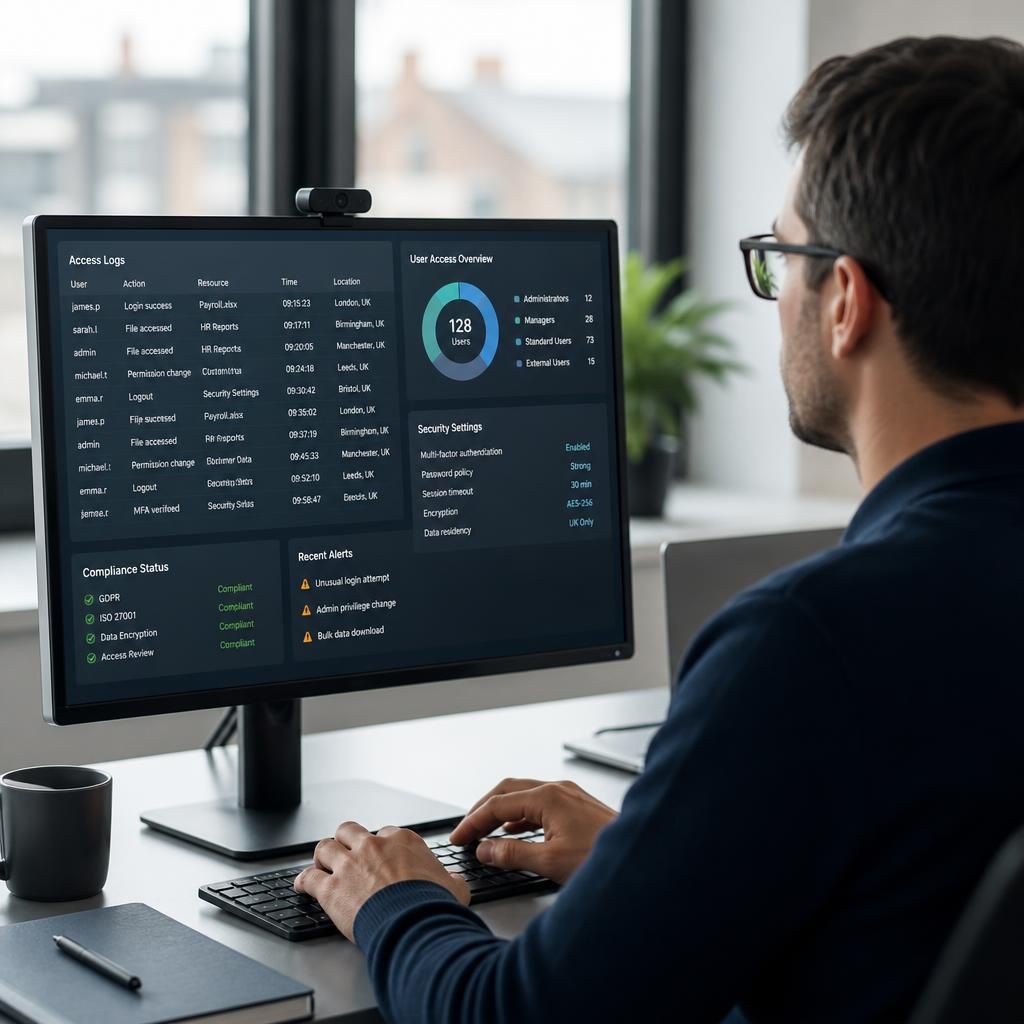
A practical way cloud computing supports compliance is by making user access easier to control throughout the employment and supplier lifecycle. Instead of relying on informal requests, an organisation can define which roles may access particular systems or types of information, then apply those permissions consistently.
Effective access governance should cover:
- granting access only when there is a documented business need;
- removing or changing permissions when someone joins, changes role or leaves;
- requiring stronger controls for privileged and administrative accounts;
- reviewing access periodically with an accountable manager; and
- recording exceptions where wider access is necessary, including an expiry or review date.
This approach helps demonstrate that access to personal, financial or commercially sensitive information is proportionate rather than based on convenience. It also highlights gaps that may otherwise be missed, such as dormant accounts, shared credentials, former suppliers retaining access or service accounts with excessive permissions. Cloud tools can support the process, but the organisation still needs clear ownership, documented approval rules and regular checks that permissions reflect current responsibilities.
Discuss Your Cloud Compliance Requirements
Discuss your cloud compliance requirements with S2 Technology Group to identify the controls, responsibilities and evidence your organisation needs to review. We can help assess your cloud environment and align its configuration with your business and regulatory obligations.