
How are changes handled during an outsourced IT project?
Changes during an outsourced IT project are managed through a formal change-control process: each request is recorded, assessed for its effect on scope, cost, timescales, security and business continuity, and approved by the appropriate decision-maker before work proceeds. The project documentation is then updated so the client and provider share a clear record of what has changed and why.
The practical objective is to distinguish a genuine project change from a clarification, correction or task already included in the agreed work. This prevents informal requests from altering the solution without the client understanding the effect, while allowing legitimate changes to be considered without unnecessarily interrupting delivery.
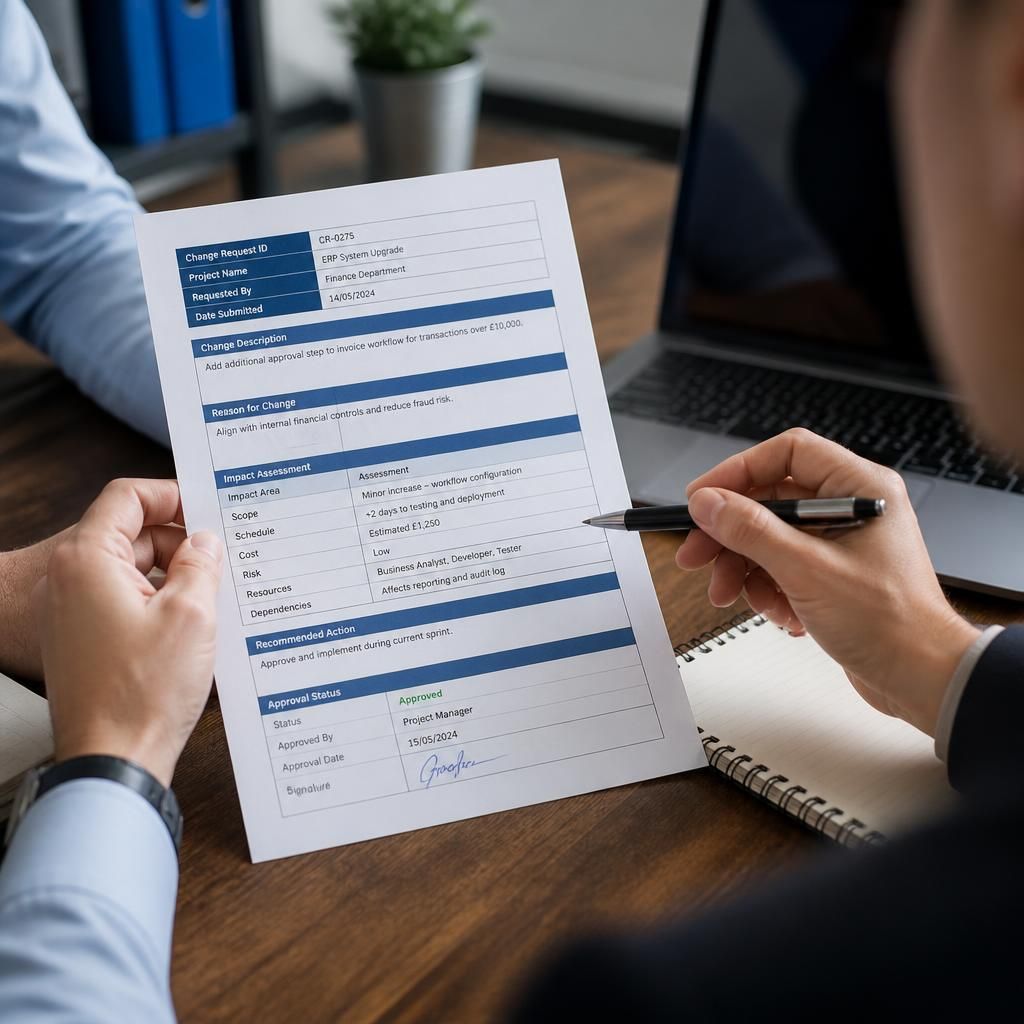
Requests are first described precisely. A useful change request identifies what is different, why it is needed and which part of the proposed solution it affects. It should also state the desired outcome, any relevant deadline, the people or systems involved, and whether the request is mandatory or simply preferred. For example, “add another approval step to the workflow” is more useful than “change the workflow”, because the provider can assess the actual technical and operational implications.
The project team will normally compare the request with the agreed scope, requirements and design documents. This comparison establishes whether the work is:
- a clarification that does not alter the agreed outcome;
- a correction to resolve an error or omission in the existing project work;
- a minor adjustment that can be absorbed within an agreed tolerance; or
- a material change requiring additional authorisation, resources or planning.
This distinction is important because not every conversation about the project should become a chargeable variation, and not every apparently small request is risk-free. A minor configuration change can affect permissions, integrations, testing or user training, particularly where several systems depend on one another.
Impact assessment should cover more than the immediate technical task. The provider will consider dependencies between systems, infrastructure capacity, licensing, data handling, access requirements, testing effort and the effect on users. It should also identify whether the change alters a design assumption or creates a new support requirement after handover. Where an internal team, third-party supplier or business process is affected, their involvement may be needed before the request can be assessed properly.
A useful assessment explains the consequences in terms the client can act on. It may set out the work required, the assumptions being made, the decision needed, the revised delivery sequence and any risks that remain. If there is more than one viable approach, the options should be compared rather than presenting a single technical answer without context. For instance, a change might be delivered within the current project by moving another task, or it might be better treated as a separate piece of work so that the original implementation remains stable.
Approval should follow an agreed authority structure. The project should define who can approve a minor adjustment, who must approve a change affecting budget or delivery commitments, and when a senior sponsor or business owner is required. This avoids two common problems: a provider proceeding on the basis of an informal instruction, or a project becoming unnecessarily slow because every low-risk clarification follows the same approval route. The appropriate authority should be clear before changes arise.
Once a change is accepted, the delivery plan is adjusted to reflect the decision. This may involve reordering tasks, revising dependencies, updating resource allocations, or creating a separate work package. The implementation team should work from the revised version rather than relying on email conversations or personal notes. If a request is declined, deferred or replaced with another option, that outcome should also be recorded so that it is not raised repeatedly or assumed to have been included.
Testing is planned around the change itself and its side effects. The level of testing should match the risk. A simple user-interface adjustment may need focused functional checks, whereas a change to identity management, networking, data flows or security controls may require integration testing, access validation and business-user acceptance. Test evidence should show what was checked, what result was obtained and whether any limitations remain before the change is released.
For changes made to live or business-critical systems, the implementation plan should define prerequisites, sequencing, responsibilities and a recovery approach. A rollback plan is particularly important where the change could affect data, connectivity or user access. The plan should explain the conditions that would trigger a reversal and how the previous state would be restored. This is not a substitute for testing; it is a safeguard if the live result differs from the expected result.
Communication should be proportionate to the effect of the change. A technical adjustment with no user impact may only require project-record updates, while a change affecting access, working practices or service availability may require advance notice, updated instructions and confirmation that affected users are ready. Internal IT teams should receive the information they need to support the altered design, including revised diagrams, configuration details and known issues.
After implementation, the provider and client should confirm whether the requested outcome was achieved and whether any follow-up work remains. The final project record may need updated requirements, designs, asset information, operating procedures, training material and acceptance criteria. Keeping these records aligned prevents the delivered environment from diverging from its documentation and gives the organisation a reliable basis for future support or further projects.
For businesses using an outsourced IT project partner, the most effective arrangement is one where the change route, approval limits, documentation standards and testing expectations are agreed at the start. S2 Technology Group can apply this type of structured approach within IT project work for small and medium-sized organisations around Stourbridge and neighbouring areas, while keeping decisions understandable to both technical and business stakeholders.
A change freeze is a defined period during an outsourced IT project when non-essential modifications are paused to protect a stable implementation baseline. It is commonly used during final testing, data migration, cutover preparation and acceptance, when introducing new variables could make faults harder to diagnose or invalidate completed checks.
The freeze should be agreed in advance and recorded in the project plan, including its start point, end point and the types of change covered. Essential security, regulatory or operational changes may still need to proceed, but they should require explicit approval from the agreed project authority and a clear explanation of their effect on testing or delivery.
Requests raised during the freeze can be placed in a controlled queue rather than lost or approved informally. After the protected period, each request should be reviewed against the implemented design and any updated business requirements; it should not be assumed that every deferred change remains suitable or belongs within the original project.
Discuss Change Control for Your Outsourced IT Project
Discuss your outsourced IT project with S2 Technology Group to establish practical change-control arrangements before work begins. We can help define approval responsibilities, documentation requirements and how proposed changes should be assessed.