
What change-control process governs outsourced IT infrastructure?
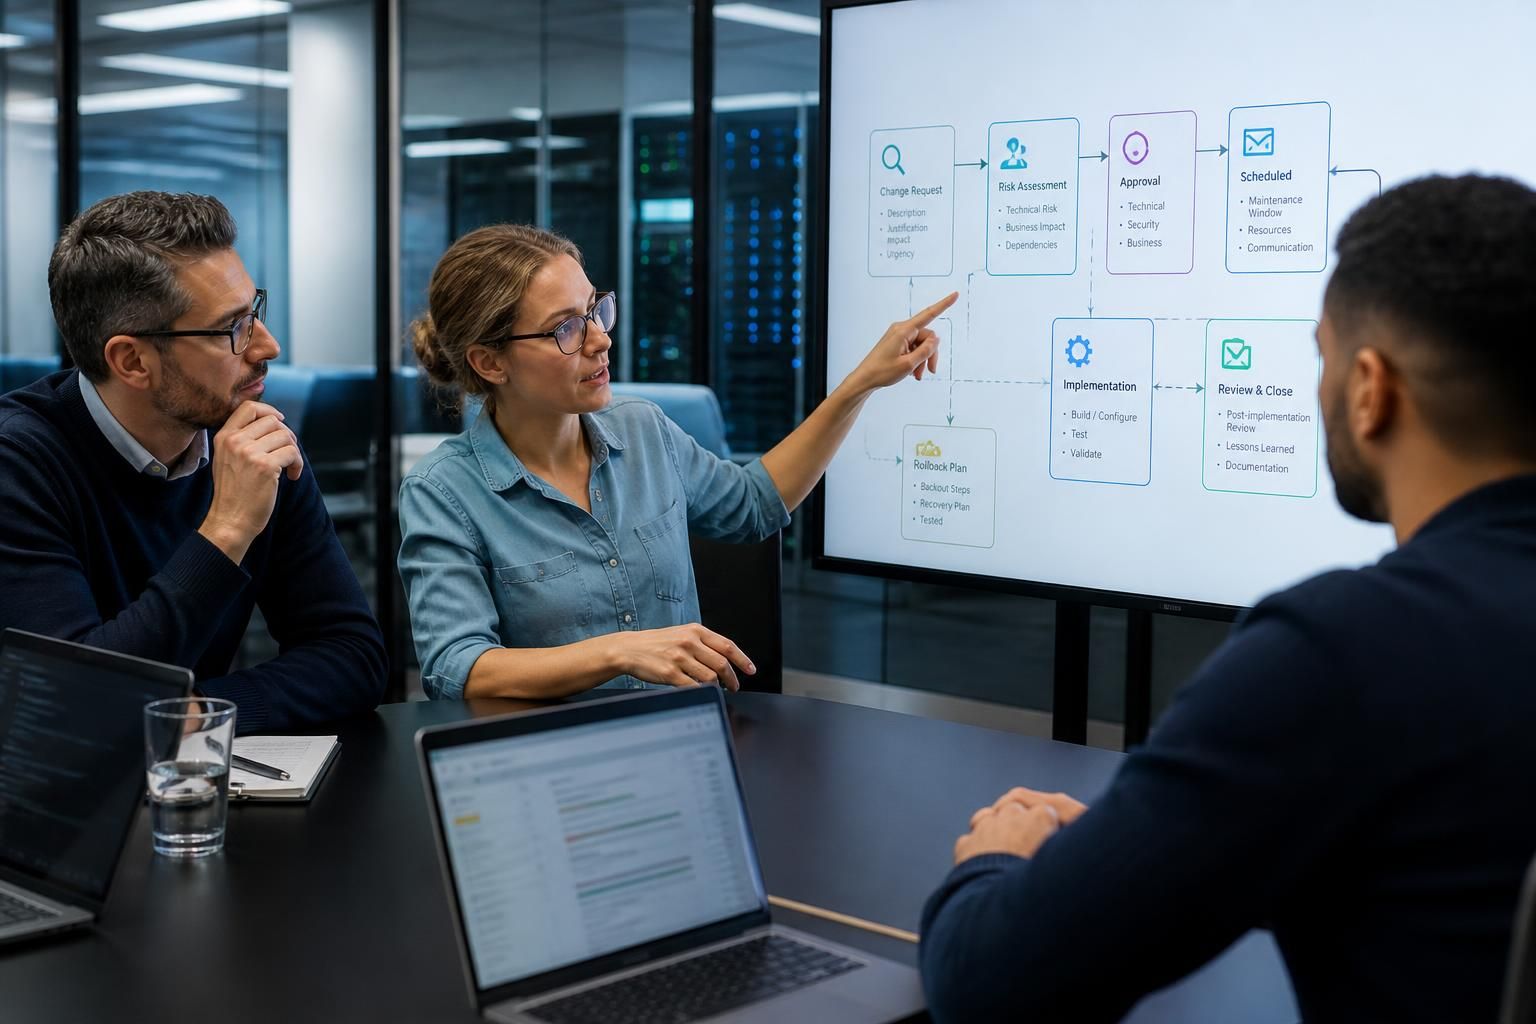
A change-control process governs outsourced IT infrastructure by requiring each proposed change to be documented, assessed for risk and business impact, approved by the appropriate parties, and scheduled before implementation. It should also define testing, communication, rollback arrangements and post-change review, creating a clear record of what changed, why it changed and who authorised it.
An outsourced IT infrastructure change-control process is a set of governance rules that determines how changes are classified, authorised, recorded and overseen across the customer’s systems and the provider’s delivery teams. Its purpose is to give both parties a consistent way to control technical work, preserve accountability and prevent unauthorised or poorly understood alterations to infrastructure.
Governance starts with clearly assigned responsibilities. The outsourcing agreement should state which decisions remain with the customer and which the provider may make under delegated authority. This commonly includes named responsibilities for the customer’s service owner, the provider’s technical lead, security representatives, application owners and relevant business stakeholders. A responsibility matrix can distinguish between the person proposing a change, the person evaluating it, the person authorising it and the person carrying it out. Separating these roles reduces the risk of one individual making and approving a change without suitable scrutiny.
The process should also define the level of authority required for different types of work. A routine infrastructure adjustment may be approved within an agreed operational framework, while a change affecting identity services, network security, critical applications or multiple sites may require customer approval. The approval threshold should be based on business impact and technical risk rather than on which supplier team is performing the work.
Changes are normally grouped into defined categories. A practical model includes:
- Standard changes: repeatable, low-risk activities carried out through a documented procedure with standing approval.
- Normal changes: changes requiring case-by-case technical and business governance because their effects or dependencies vary.
- Major changes: work with significant potential impact, such as core network redesign, identity-platform alteration, data-centre migration or changes affecting several business locations.
- Emergency changes: urgent work needed to address a serious security issue, outage or infrastructure failure. These should use an expedited route, not bypass control altogether.
Each category should have its own approval route, evidence requirements and level of oversight. Emergency work, for example, may be authorised by an on-call decision-maker designated in the contract, with a retrospective governance review to confirm what was done and whether further corrective action is needed.
The change record is the central governance artefact. It should link the proposed work to the affected services, infrastructure components, business owner, implementation team and relevant incident, problem or project record. It should also identify prerequisites, technical dependencies, access requirements and any effect on security controls or regulatory obligations. Maintaining these links makes it easier to understand the wider consequences of a change and to reconstruct events during an investigation.
Where infrastructure is represented in a configuration management database or similar inventory, the record should be connected to the relevant configuration items. Updates to that inventory should form part of the controlled process rather than being treated as an optional administrative task. Inaccurate infrastructure records can lead to incomplete impact analysis, incorrect maintenance assumptions and avoidable changes to dependent systems.
Change-control governance must align with security and compliance controls. Proposed work should be checked for effects on privileged access, network segmentation, encryption, logging, backup arrangements, vulnerability exposure and data handling. A change that alters the location or flow of business data may need review by an information-governance or legal representative. Changes involving administrative accounts should preserve appropriate separation of duties and leave an auditable record of access.
The outsourcing contract should specify how records are retained, who can inspect them and how evidence is supplied for internal or external audits. It should also set expectations for reporting unauthorised changes, investigating control failures and correcting gaps in the configuration record. These provisions matter because the customer remains accountable for many business, legal and regulatory obligations even when infrastructure operation is delegated to a provider.
Operational reporting makes the process measurable. Useful reports may show the number and type of changes, approval exceptions, emergency changes, unauthorised alterations, failed implementations, overdue reviews and repeated changes associated with incidents. The purpose is not to reward a high volume of completed work. It is to identify weak controls, recurring technical problems, unclear ownership and areas where the service design needs improvement.
A regular governance meeting can review these reports alongside upcoming infrastructure work, unresolved risks and changes that affect business projects. The meeting should have a defined agenda, recorded decisions and an action owner for each follow-up item. Where the provider operates a change advisory forum, the customer should understand its remit and retain the right to challenge decisions that could materially affect business services.
The process should be tested before it is relied upon. The customer and provider can use representative scenarios, such as a security patch on a critical server, a firewall-rule adjustment, a cloud-network change or a failed deployment, to check whether the approval route, escalation contacts and evidence requirements work in practice. Periodic audits can then test a sample of records against the agreed policy, including whether the actual implementation matched the authorised scope.
For a small or medium-sized organisation, the process does not need a large committee or excessive paperwork. It does need proportionate rules, clear decision rights, reliable records and enough technical context for the customer to understand the consequences of outsourced work. During supplier selection and contract review, organisations should ask to see the provider’s change policy, approval model, reporting format and approach to emergency changes before assigning responsibility for critical infrastructure.
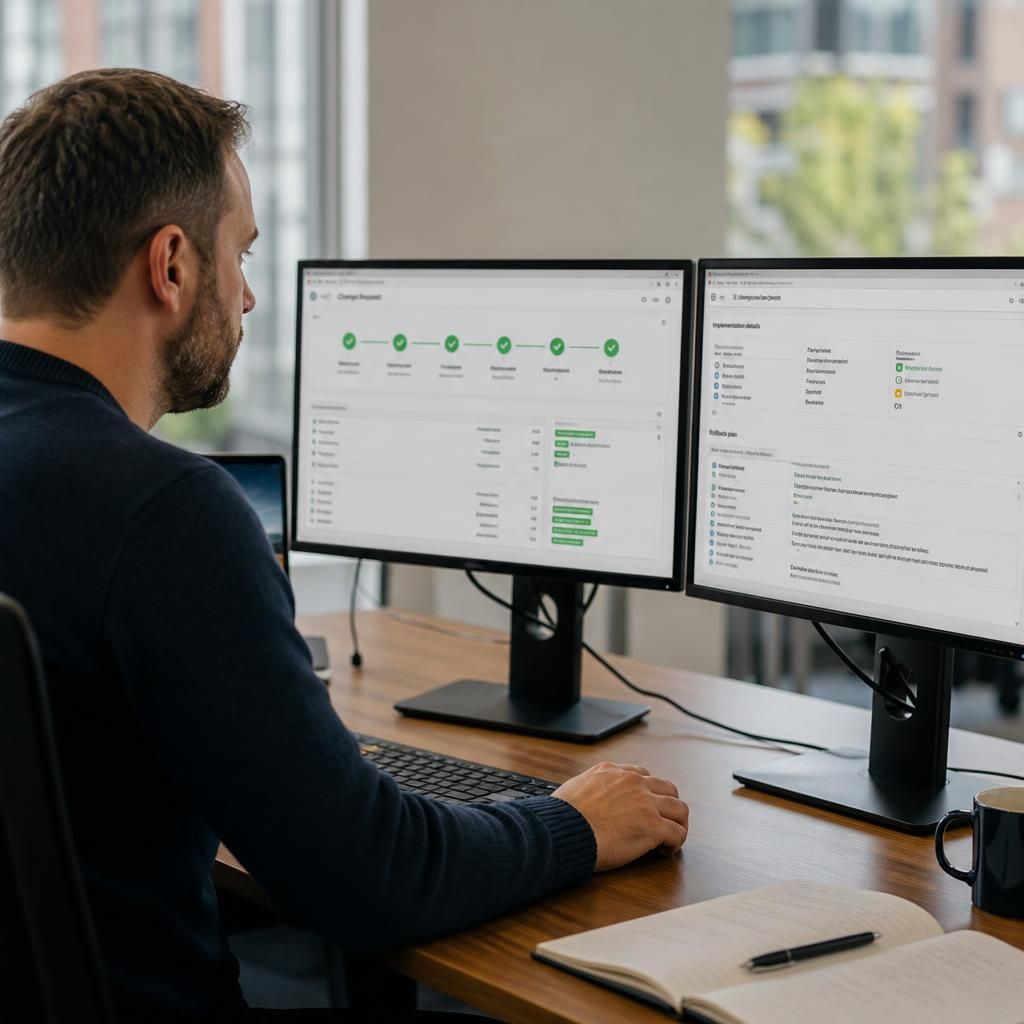
A configuration baseline gives outsourced IT infrastructure change control a defined reference point. It records the approved state of important systems, such as network rules, server settings, identity configurations and cloud resources, so that later alterations can be compared with what was authorised.
Baseline comparisons help distinguish an approved implementation from configuration drift or an undocumented modification. If the observed state differs from the approved record, the discrepancy can be investigated, corrected or raised as a new change request. This provides an additional technical check alongside written approvals and helps ensure that the infrastructure remains aligned with the organisation’s intended design.