
How is data sovereignty managed in IT infrastructure outsourcing?
Data sovereignty in IT infrastructure outsourcing is managed by controlling where data is stored and processed, which laws apply to it, and who can access it. The arrangement should define approved data locations, assess the provider’s legal and compliance obligations, and apply contractual, encryption, access-control and audit requirements to protect data throughout its lifecycle.
Data sovereignty in IT infrastructure outsourcing is managed through a documented governance framework that links each dataset to its location, applicable jurisdiction, permitted processing activities and responsible parties. The framework must remain effective across primary systems, backups, replicas, monitoring tools, support platforms and any subcontractors involved in delivering the service.
Data residency and data sovereignty are related but different. Data residency describes the physical or geographic location where information is stored. Data sovereignty concerns the laws and governmental powers that may apply to that information because of its location, the provider’s jurisdiction or the organisation handling it. Data held in the UK may therefore still raise sovereignty questions if an overseas organisation can administer it or is subject to foreign legal demands.
A suitable outsourcing assessment begins with a data map. This should identify the types of information being outsourced, where each type is created and stored, where it may be replicated, and which systems can access it. The assessment should distinguish between personal data, confidential commercial information, intellectual property, financial records and operational data, because different legal, contractual and risk requirements may apply.
The outsourcing specification can then set explicit requirements for:
- approved countries or regions for storage and processing;
- prohibited locations or jurisdictions;
- where backups, disaster-recovery copies and system logs may be held;
- which provider personnel and subcontractors may access the information;
- notification and approval requirements for any proposed location change; and
- the retention, return and deletion of data when the service changes or ends.
Provider and supply-chain due diligence is equally important. The organisation should establish which legal entities will deliver the service, where their administrators are based, which subprocessors they use and whether support access can originate from another country. Relevant evidence may include security policies, data-processing terms, audit reports, subprocessor registers, information-security certifications and records of how legal or regulatory requests are handled. A provider should be able to explain its control over the full service chain rather than only the location of its main data centre.
Contracts turn these requirements into enforceable controls. They should define the permitted processing purpose, categories of data, approved territories, access conditions, subprocessor obligations, incident notification arrangements and audit rights. They should also address international transfers where relevant, including the lawful mechanism and supplementary safeguards required for the data involved. Legal requirements can vary according to the organisation, sector and type of information, so contractual wording should be reviewed against the relevant regulatory obligations rather than copied from a generic template.
Technical controls support, but do not replace, those contractual and legal measures. Common safeguards include encryption in transit and at rest, separately managed encryption keys, role-based access, privileged-access controls, strong authentication, session logging and restrictions on copying data to unmanaged systems. Where the risk justifies it, customer-controlled keys or arrangements that limit provider access to readable data can reduce exposure. Key management must itself be considered: the location, administrators, recovery process and legal jurisdiction associated with the keys may affect the overall sovereignty position.
Operational processes should verify that the agreed position is maintained. Useful checks include reviewing provider and subprocessor changes, examining access records, testing backup and restoration locations, reconciling data-flow diagrams with the live environment and recording exceptions. A change to a hosting region, support model, backup service or ownership structure can alter the sovereignty assessment even when the primary application appears unchanged.
Data sovereignty also needs to be addressed during incidents and legal requests. The agreement should state how the provider will notify the customer of a demand from a public authority, subject to applicable law, and how it will challenge or limit disclosure where appropriate. Incident procedures should identify who assesses cross-border implications, who communicates with regulators or affected parties, and how relevant records are preserved.
Finally, the exit plan should be tested before outsourcing begins. It should specify how data will be exported in a usable format, where the export may be transferred, how replicas and backups will be removed, how deletion will be evidenced and how access credentials and encryption keys will be revoked. This prevents sovereignty controls from applying only during the active contract and ensures that data remains governed during migration to another provider or back to internal systems.
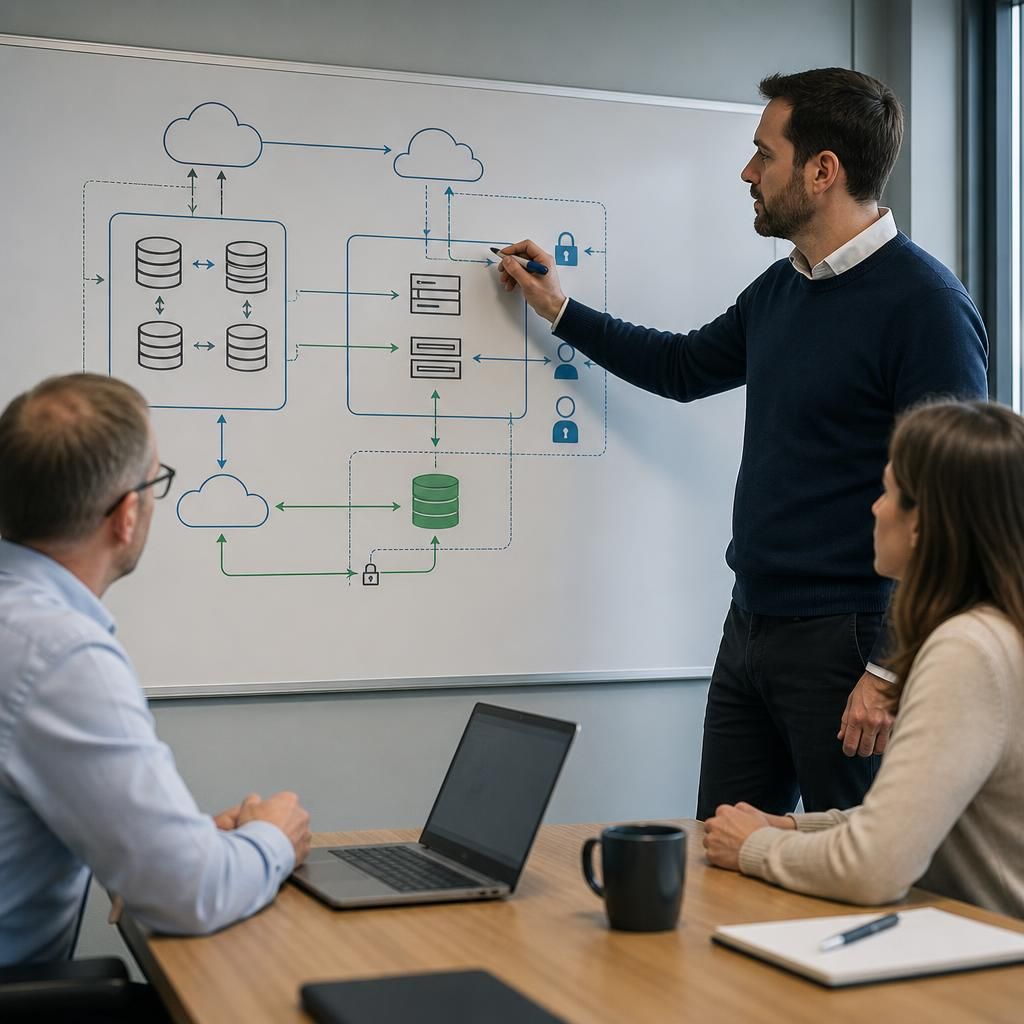
Data sovereignty management also depends on assigning accountability clearly between the customer and the outsourced provider. Outsourcing the operation of infrastructure does not automatically transfer the organisation’s legal or governance responsibilities for the information it controls. The customer should therefore retain oversight of data-handling decisions, while the provider’s responsibilities are defined for hosting, administration, support and evidence production.
This division should be reflected in an accountability matrix covering approval of processing activities, response to information requests, regulatory engagement, risk acceptance and review of sovereignty-related controls. It should also identify the evidence the provider must supply, such as processing records, access information and relevant control attestations. Clear ownership prevents assumptions that a provider’s standard hosting arrangement is sufficient for every dataset or regulatory context.