
How are Microsoft 365 Backup permissions controlled?
Microsoft 365 Backup permissions are controlled through role-based access, so only authorised administrators and recovery operators can manage backup settings or restore data. Access is limited according to each user’s responsibilities, with administrative activity logged to support oversight and accountability.
Microsoft 365 Backup permissions are controlled by assigning specific administrative roles to named users, then applying the organisation’s identity and security policies to those accounts. This determines who can configure protection, view backup information, start a recovery, or change settings, while ordinary Microsoft 365 users retain no additional access to backup data simply because their content is protected.
Role-based access is the central control. A tenant administrator can assign the Microsoft 365 Backup administration role to the people responsible for managing the service. A global administrator has broader authority across the tenant, but using that account for routine backup work gives the user more access than is normally necessary. A more controlled design assigns backup responsibilities to a dedicated administrator or recovery operator with the narrowest suitable role.
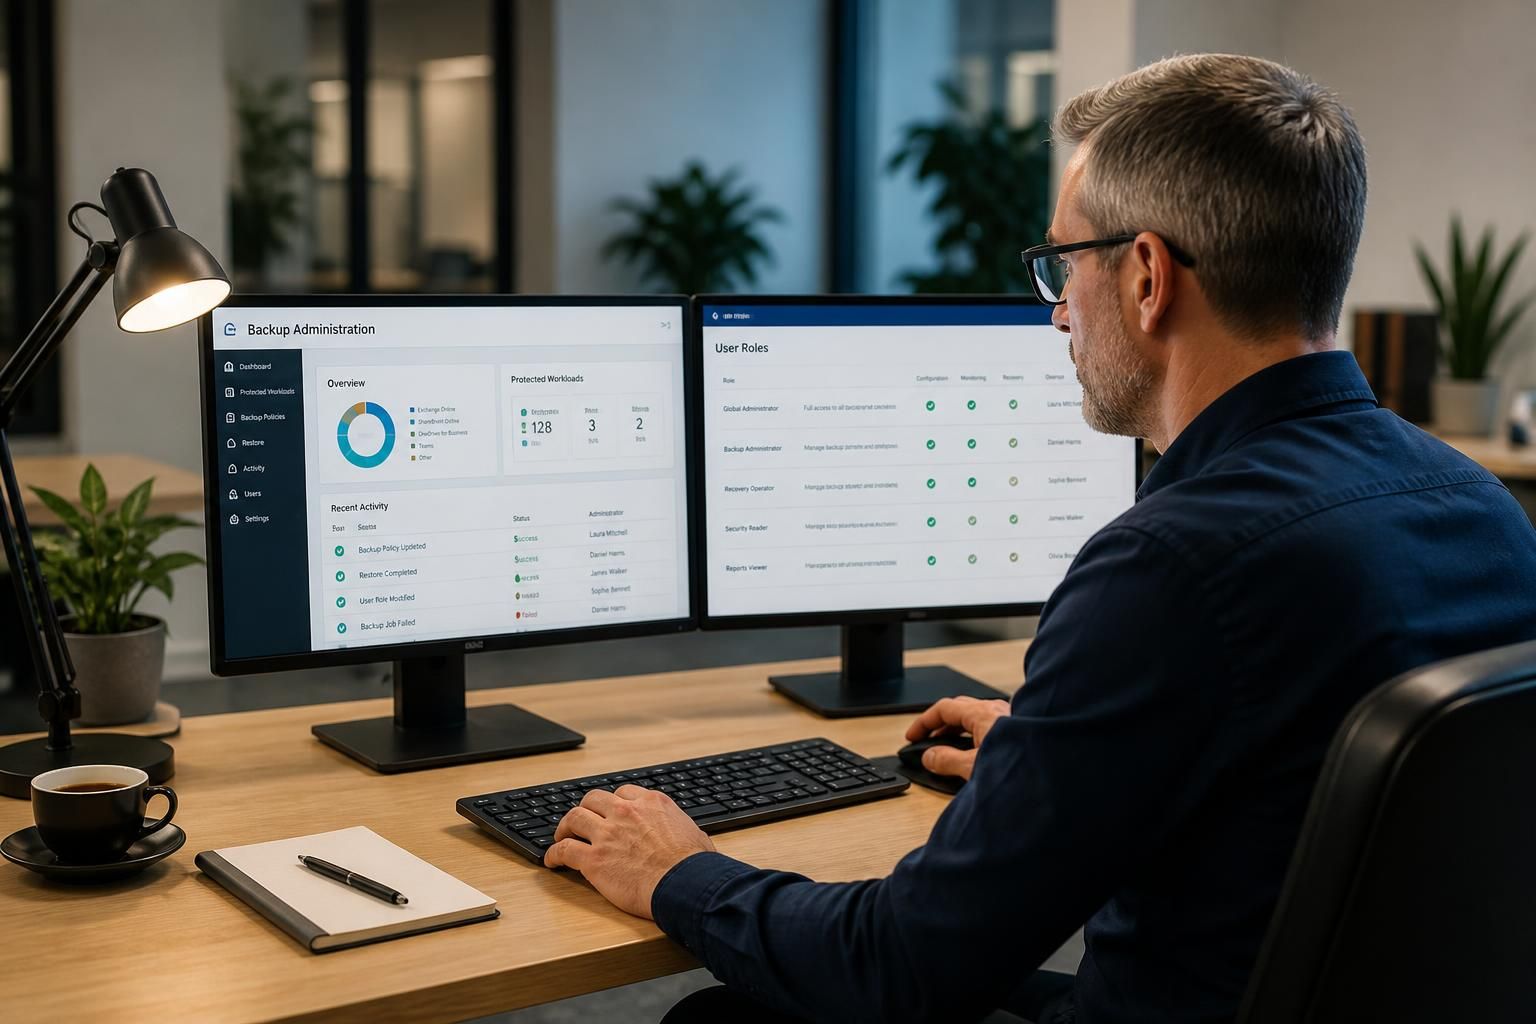
Permissions should be separated according to the actions each person needs to perform. Typical responsibilities include:
- Configuration: creating or changing backup policies, protected workloads and service settings.
- Monitoring: reviewing protection status, completed operations, failures and available recovery points.
- Recovery: selecting a recovery point and initiating the restoration of files, mail, sites or other supported data.
- Oversight: reviewing administrative activity and approving sensitive changes or recoveries.
Not every role has to include all four responsibilities. Separating configuration from recovery can reduce the risk of an unauthorised policy change being followed by an inappropriate restoration. In smaller organisations, one administrator may perform several functions, but the assignments should still be deliberate and documented rather than relying on broad access by default.
Identity controls apply before the backup permissions are evaluated. Administrative accounts should use strong authentication, especially multi-factor authentication, and should not be shared between members of the IT team. Conditional access rules can restrict administration based on factors such as device compliance, sign-in risk or the network from which an administrator connects. Privileged access management can also provide administration rights only for an approved period, rather than leaving high-level permissions permanently active.
The backup service does not replace the permissions already used to access live Microsoft 365 content. A user who can read a document in SharePoint or a mailbox item may use that normal access, but this does not automatically give the user permission to browse backup copies or launch a recovery. Backup administration is a separate privileged function. Similarly, giving someone responsibility for monitoring protection does not necessarily mean that person should be able to change policies or restore content.
Recovery permissions should be considered separately from backup configuration. A recovery operator may need to select the correct workload, date and recovery point, then choose whether supported data is returned to its original location or another permitted destination. The operator should have access to the recovery controls without receiving unnecessary rights over unrelated tenant settings. The permissions applied to the recovered content will depend on the workload and the selected recovery method, so a recovery should be checked afterwards to confirm that access has not been broadened unintentionally.
Administrative actions should be recorded in audit information, including changes to protection settings and recovery activity. Audit records help establish who performed an action, what was changed and when it occurred. They are useful for investigating unexpected activity, checking that recovery procedures were followed and demonstrating appropriate oversight during an internal or regulatory review. Audit retention and available event detail depend on the tenant’s wider auditing configuration, so the records should be included in the organisation’s monitoring and retention plan.
A practical permissions review should cover the following points:
- List every account with backup administration or recovery authority.
- Confirm that each assignment matches the person’s current responsibilities.
- Remove access from leavers, role changes and dormant administrative accounts.
- Check that privileged accounts use the organisation’s required authentication and access policies.
- Review recent configuration and recovery activity for unusual or unexplained actions.
- Test the approval and recovery process without granting wider permissions than necessary.
Permissions therefore form part of a wider control framework rather than acting as the sole protection for backup data. Role assignment limits what an administrator can do, identity policies help prevent account misuse, and audit records provide accountability after an action takes place. Together, these controls support a recovery process that can be operated by authorised personnel without exposing backup management or protected business data to every Microsoft 365 user.
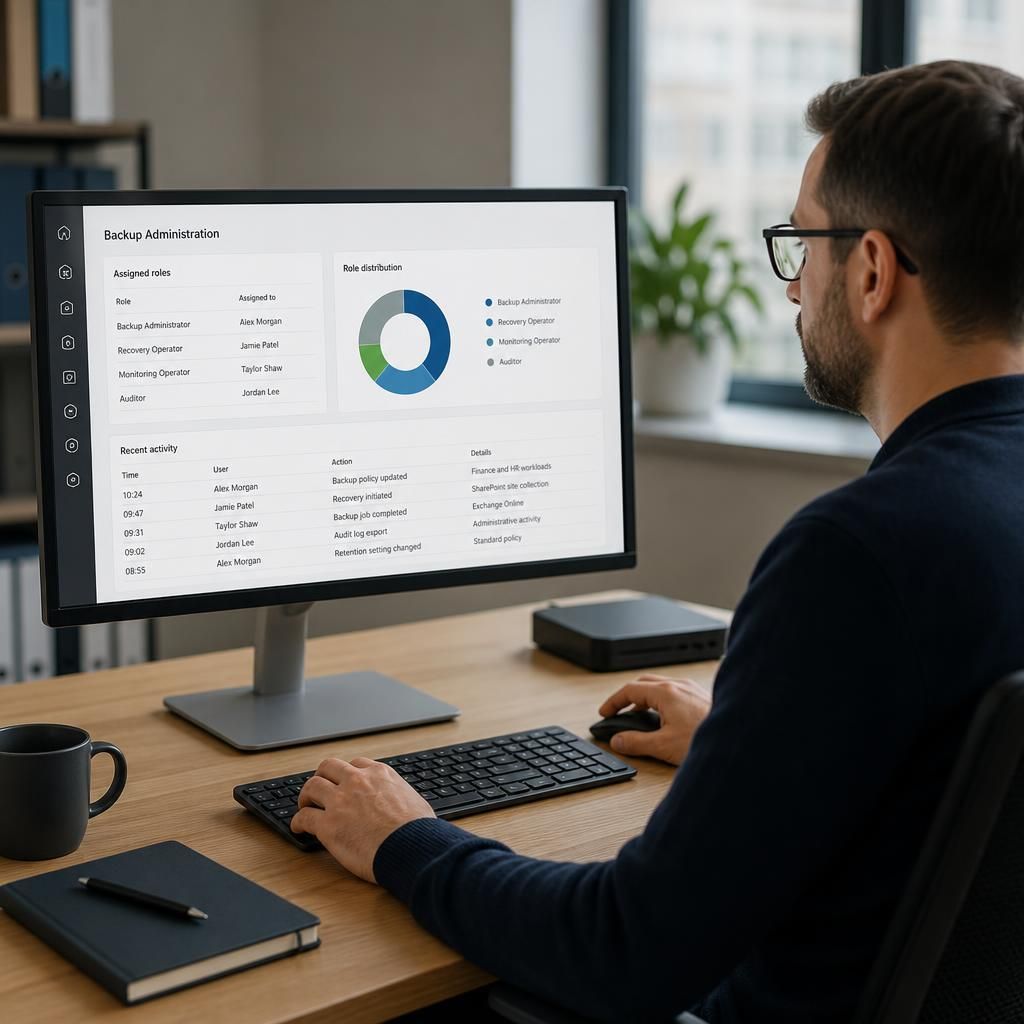
A recovery does not automatically make the person who started it the owner of the restored information. Access to recovered content is governed by the permissions of the destination and the workload’s restoration method. This means a recovery operator may be authorised to initiate a restore without receiving ongoing access to the documents, messages or sites being recovered.
For sensitive recoveries, choose the destination carefully. A restricted location can be used for validation before information is returned to its normal business location. The responsible administrator can then confirm that ownership, sharing links, group membership and inherited permissions match the intended access model. This prevents a restore from unintentionally exposing confidential content to a wider group of users.