
What happens during the transition to fully managed IT support?
The transition to fully managed IT support usually starts with an assessment of your existing systems, risks and priorities, followed by a documented onboarding plan. Access, monitoring, security controls and support processes are then introduced in stages, with knowledge transferred and responsibilities clearly confirmed before ongoing management begins.
The transition to fully managed IT support is a controlled handover of day-to-day technology responsibilities from an internal team, existing supplier or ad hoc arrangement to a managed service provider. It involves establishing an accurate view of the environment, agreeing how work will be governed, correcting significant weaknesses and validating the support model before it becomes the normal way of managing IT.
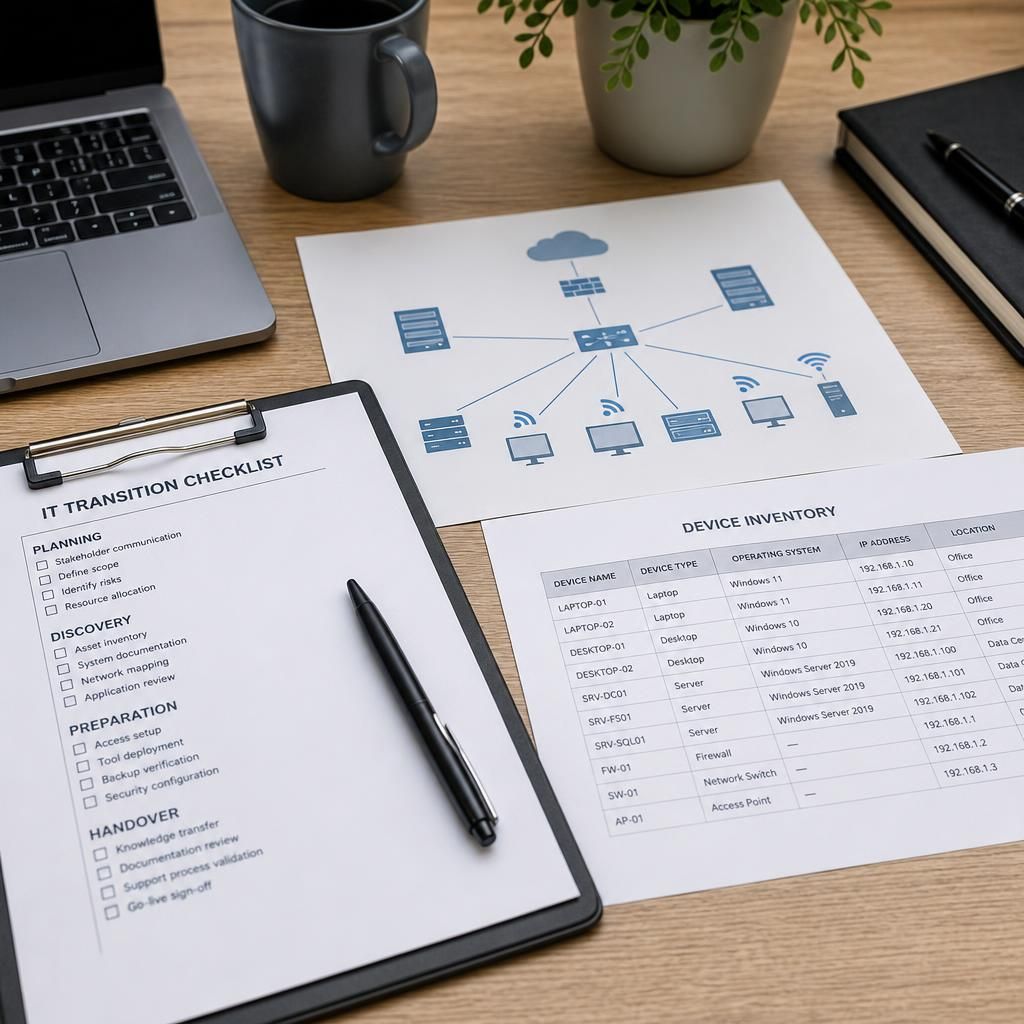
A well-managed transition separates discovery, preparation and operational handover rather than attempting to change everything at once. The precise sequence depends on the organisation’s systems, locations, users and risk profile, but the main activities usually include:
- Defining the service boundary: The parties confirm which users, devices, applications, infrastructure, locations and suppliers are included. Responsibilities for areas such as user administration, backups, connectivity, cybersecurity, software and line-of-business applications should be recorded, including any items that remain with the organisation or another specialist provider.
- Building an accurate baseline: The provider verifies the equipment, operating systems, network arrangements, cloud services, contracts, licences and important business applications in use. Dependencies are particularly important; for example, a business application may rely on a particular server, database, identity service or network connection. This baseline provides a reference for future changes and helps expose undocumented technology.
- Assessing risk and priority: The transition should identify unsupported systems, unprotected accounts, weak access arrangements, missing patches, inadequate backup coverage and single points of failure. Issues are normally classified by business impact and urgency. Not every historical problem has to be resolved before handover, but material risks need an agreed treatment plan and owner.
- Agreeing governance: The organisation and provider establish who can approve changes, who authorises new users, how incidents are escalated and how priorities are assigned. Reporting arrangements, review meetings, documentation standards and decision-making contacts should be clear before routine management starts.
Preparation then focuses on making the environment manageable and supportable. This can include standardising device configurations, removing obsolete accounts, improving administrative access, confirming backup arrangements and documenting network or application dependencies. Where upgrades or replacements are required, they should be planned as separate work packages rather than hidden within the support transition. Separating them makes it easier to distinguish the cost and risk of remediation from the cost of ongoing management.
Technical integration is another important part of the process. The provider may need to connect its service desk, monitoring, endpoint management, backup administration, security tools and reporting systems to the organisation’s environment. Administrative access should be limited to what is necessary, assigned to named roles and protected by appropriate authentication controls. Existing supplier relationships also need attention: contracts, renewal dates, support credentials, warranties and escalation routes should be collected so that responsibility does not become unclear during the changeover.
People and business processes require equal consideration. Employees should know how to raise requests, report suspected security incidents and obtain assistance with common tasks. Internal managers should understand what information is needed to approve access or changes. If the organisation has an internal IT contact, that person’s continuing responsibilities should be documented rather than assumed. Clear communication reduces duplicated requests and prevents important issues from being passed between parties without ownership.
Before the service is treated as fully operational, the transition should be tested against realistic scenarios. Useful checks may include:
- creating and resolving a test support request;
- checking that priority and escalation paths reach the correct people;
- confirming that new and departing user processes work as intended;
- verifying that monitoring produces meaningful alerts rather than excessive noise;
- testing access to essential systems using approved administrative accounts;
- reviewing whether backup jobs, security events and device status information are visible to the responsible team; and
- confirming that documentation is sufficiently detailed for another authorised technician to follow.
The formal handover should leave an auditable record of what has transferred, what remains outstanding and who owns each open action. This record may include the verified asset information, network and application documentation, risk register, agreed service scope, access approvals, supplier details, change procedures and planned improvement work. It should also state any assumptions or limitations, such as systems that could not yet be inspected or services controlled by a third party.
After handover, the first operational review is used to compare actual support activity with the agreed model. Recurring requests may indicate a training need, a configuration problem or an inefficient process. Repeated alerts may require monitoring to be refined, while unresolved risks may need to move into a prioritised improvement plan. This makes the transition a continuing process of verification and improvement rather than a single date on which responsibility changes.
For a small or medium-sized organisation, the most useful sign of a sound transition is not simply that a provider has access to its systems. It is that the organisation can explain what is managed, how decisions are made, how risks are tracked and what happens when a user, device, application or supplier falls outside the expected process. Fully managed IT support is properly established when those arrangements are documented, tested and understood by the people who rely on them.
A transition to fully managed IT support should include a controlled cutover plan for any changes that could affect users or critical systems. Non-essential upgrades, configuration changes and migrations should be kept separate from the transfer of responsibility wherever possible, so that problems can be traced to the correct activity.
For each significant cutover, the plan should identify the systems affected, the person authorised to approve the change, the validation checks to complete afterwards and the steps for reverting it if the expected result is not achieved. A short period of closer observation after the change can then confirm that authentication, connectivity, business applications and security controls continue to operate as intended. This approach reduces the risk that a support transition becomes confused with an unplanned technology overhaul.