How does DNS affect business connectivity?
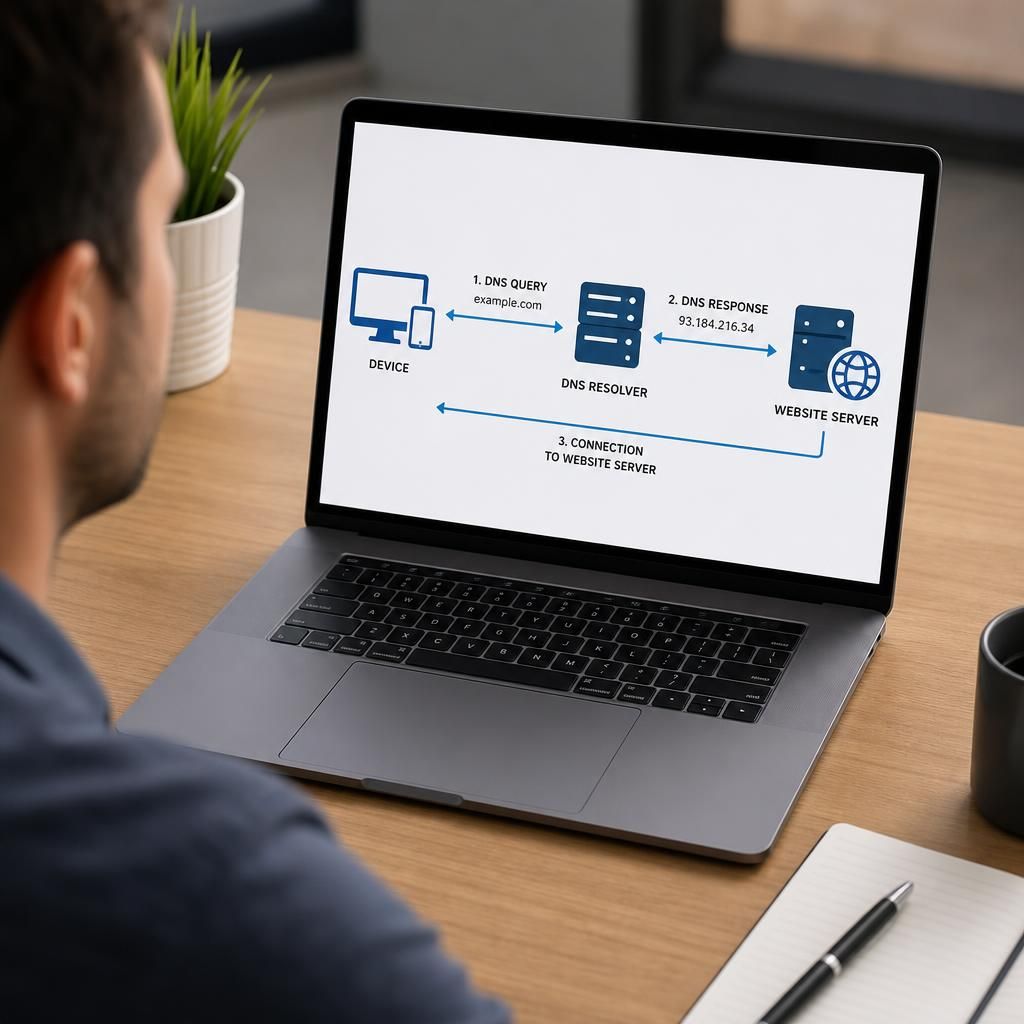
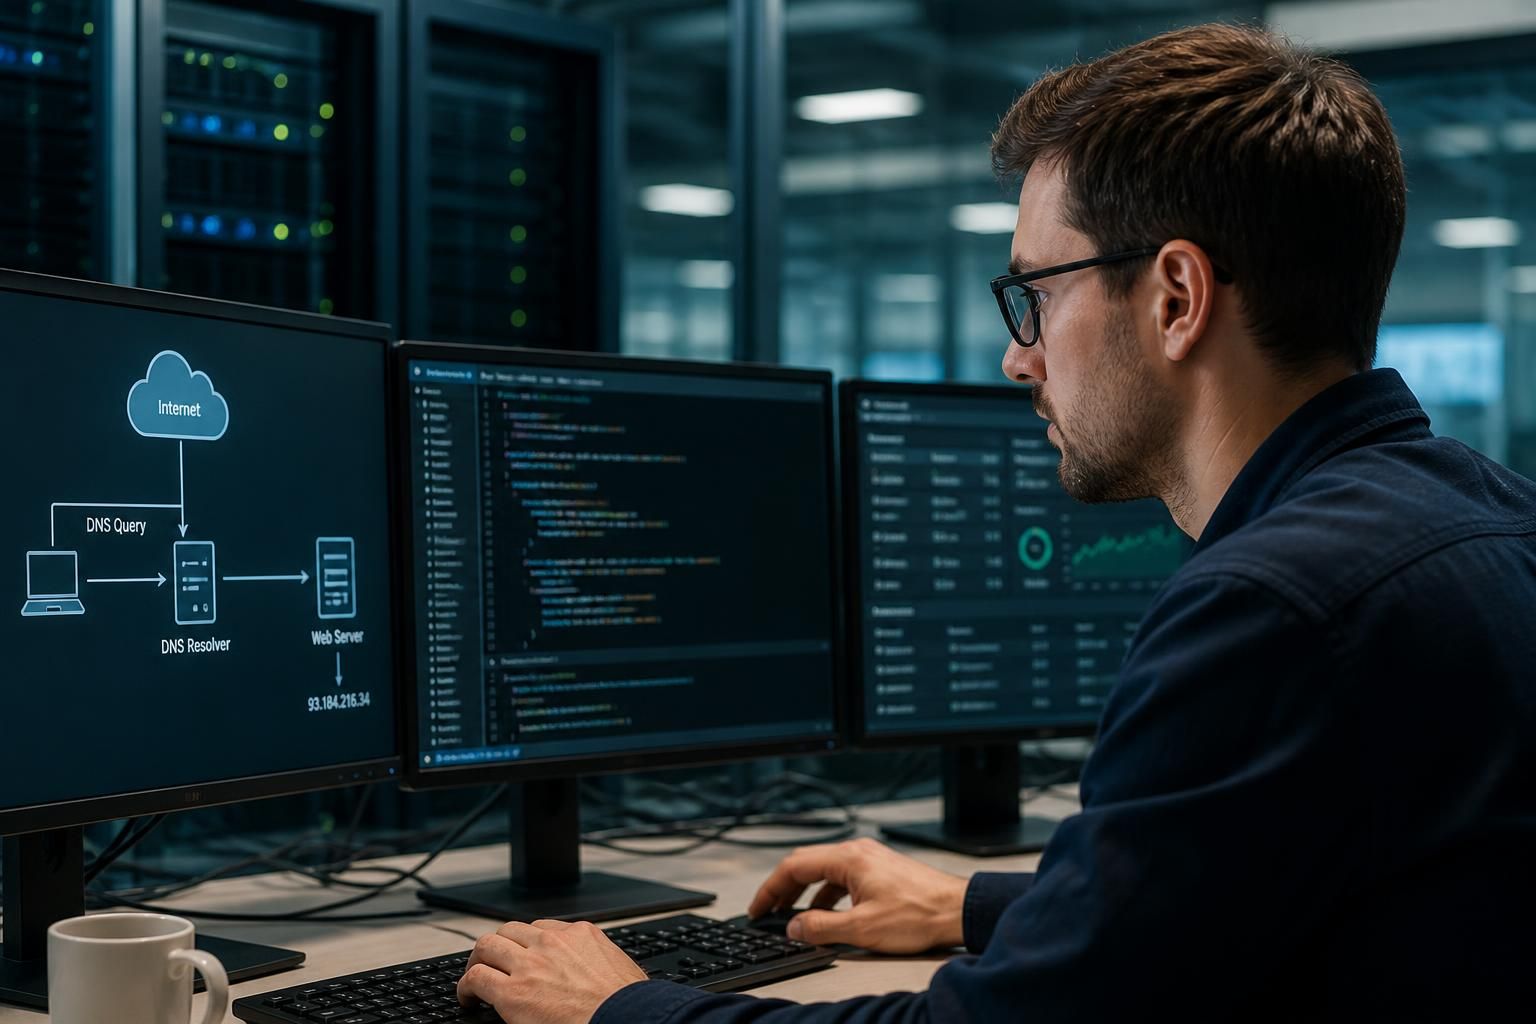
DNS translates domain names into the IP addresses that devices use to reach websites, email systems, cloud platforms and other online services. Responsive, reliable DNS supports consistent access, while slow, misconfigured or unavailable DNS can delay connections or prevent services from being reached.
DNS affects business connectivity as the naming and service-discovery layer that allows users, devices and applications to locate network services. It does not carry the main data traffic itself, but a DNS problem can stop a device from finding the correct destination, making websites, cloud applications, email, remote access and other services appear unavailable.
DNS influences several parts of a business network:
- Web access: browsers must resolve a website’s domain before they can establish a connection. Incorrect records, expired registrations or unavailable DNS servers can therefore prevent access even when the internet circuit is functioning.
- Cloud applications: software-as-a-service platforms often use multiple domain names for authentication, application traffic, storage, updates and security controls. Blocking or misdirecting one of these names can cause partial failures that are harder to diagnose than a complete outage.
- Email: mail delivery relies on DNS records, including MX records that identify receiving mail servers. Sender policies and email authentication records are also published through DNS, so errors can affect delivery, validation and protection against spoofing.
- Remote access: VPN gateways, virtual desktops and other externally hosted access points commonly use DNS names. A user may have a working network connection but still be unable to reach the remote service if its name cannot be resolved.
- Internal services: internal DNS can identify file servers, printers, applications, authentication systems and other resources without exposing their addresses publicly. Poorly maintained internal records can disrupt office-based users and site-to-site communication.
Resolution speed is not the same as internet speed. When a resolver has a valid answer in its cache, a device may receive the address quickly. If the answer is not cached, the resolver has to obtain it from other DNS servers. A slow or overloaded resolver can add delay before a connection begins, while a failed resolver can make services unreachable even though bandwidth and routing remain available. Once the destination has been found, DNS is generally no longer responsible for the performance of the data transfer itself.
Businesses typically use recursive DNS resolvers for users and devices, while authoritative DNS servers hold the official records for a domain. Resolvers may retain answers for the period specified by a record’s time to live, or TTL. This caching reduces repeated lookups, but it also means that a DNS change is not necessarily reflected everywhere immediately. Planning a service migration therefore requires accurate records, suitable TTL values and an understanding of which systems may still hold an older answer.
Common DNS-related connectivity faults include:
- incorrect A or AAAA records pointing users to the wrong IPv4 or IPv6 address;
- missing or incorrect MX records affecting email routing;
- an expired domain or delegated nameserver arrangement;
- internal and external DNS views returning unsuitable answers to the same user;
- firewalls blocking DNS requests or replies;
- devices receiving inconsistent resolver settings through DHCP;
- DNS records that do not match changes to hosting, firewalls or cloud services; and
- DNS filtering that blocks a legitimate domain or a dependency used by an application.
Split DNS is particularly relevant to organisations with private systems or multiple locations. Internal users may need a private address for a service, while external users require a public address. The DNS design must return the appropriate answer based on where the request originates. If this arrangement is incomplete, users may be directed over an unsuitable route, denied access, or inadvertently exposed to an internal service.
DNS also has a security role. Resolver filtering can block requests to domains associated with malware, phishing or other unwanted activity, although filtering rules need careful management to avoid interrupting legitimate business applications. DNSSEC can help validate that signed DNS responses have not been altered, but it must be configured consistently across the domain and the validating resolvers. Encrypted DNS can protect the contents of DNS requests in transit, but businesses still need suitable policies for logging, filtering and troubleshooting.
A practical DNS review should cover four areas:
- Record accuracy: check public and internal records against the services they are intended to reach, including web hosting, email, remote access and cloud platforms.
- Resolver resilience: confirm that devices and network equipment have dependable resolver options and that a single failed DNS component cannot affect every user or site.
- Change control: record who can alter DNS, require review for high-impact changes and consider TTL and caching before moving a service.
- Monitoring and testing: monitor resolution failures, response times and unexpected record changes from relevant locations, then test both internal and external paths.
When troubleshooting, first establish whether the fault affects one device, one site, a particular domain or multiple services. Checking the device’s configured resolver, querying the name directly, and comparing results from internal and external resolvers can distinguish a local configuration issue from a public DNS problem. It is also important to test the resolved address, routing, firewall policy and application service separately; a successful DNS lookup confirms only that a name was resolved, not that the destination is healthy.
For a business, the aim is not simply to choose a fast resolver. DNS should be treated as part of the connectivity architecture, with controlled administration, documented dependencies, appropriate security controls and monitoring that can identify failures before they are mistaken for a general internet outage. This approach helps separate DNS faults from problems with circuits, routing, firewalls or the applications themselves.
DNS can influence where business traffic is sent when a domain has more than one destination, such as separate hosting locations, application instances or connectivity routes. However, returning a different IP address does not move an existing session, and client or resolver caching means that users may continue receiving an earlier answer for a period of time.
For this reason, DNS-based traffic distribution should not be treated as a complete failover mechanism. A sound design considers whether each destination is genuinely available, how unhealthy destinations are removed from DNS responses, and how applications handle interrupted connections. Connectivity testing should therefore assess the complete path from name resolution through to the service, rather than assuming that a changed DNS record alone will restore access.