How does a SIEM protect the logs it collects?
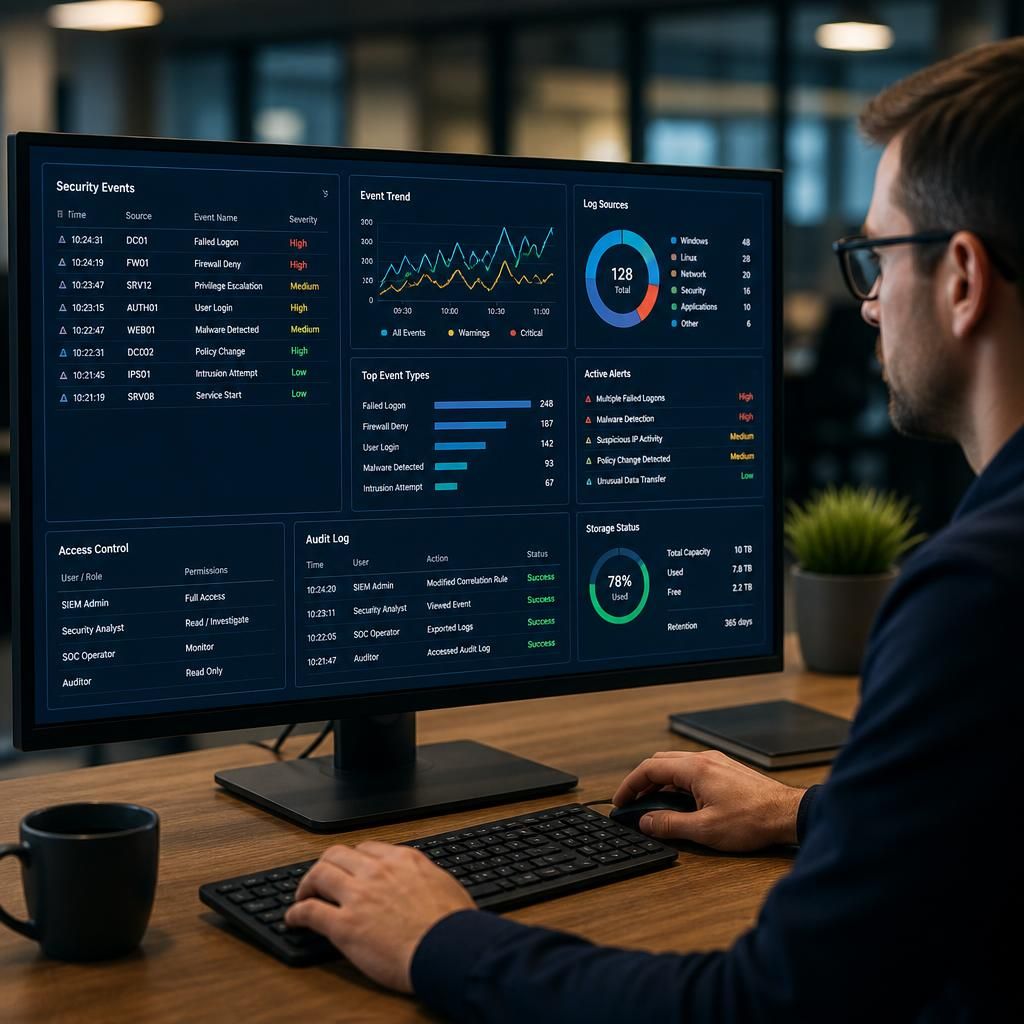
A SIEM protects the logs it collects through encryption, strict access controls and secure storage. These measures help prevent unauthorised disclosure, alteration or deletion, preserving the integrity of the evidence used for security investigations.
A SIEM protects collected logs through a combination of integrity checks, controlled ingestion, tamper-evident storage, resilient architecture and continuous oversight. The aim is not only to keep log content confidential, but also to demonstrate that records are complete, attributable and reliable enough to support detection, investigation and compliance activities.
Integrity protection begins during collection. Log sources should be identified and authenticated before they are allowed to submit data. The SIEM can then associate each event with the correct device, application, account or service. This reduces the risk of accepting fabricated records or attributing an event to the wrong source. Collection connectors should also validate message formats, reject malformed input and record failures, so that gaps in ingestion are visible rather than silently ignored.
Secure transport helps preserve logs between the source and the SIEM. Without suitable protection at this stage, an attacker positioned between systems could interfere with messages, replay old events or cause selected records to be lost. A well-designed configuration checks the identity of sending systems, detects interrupted connections and raises an operational alert when an expected source stops reporting.
Tamper evidence is a further safeguard. Many SIEM platforms use hashing, digital signatures, chained records or equivalent controls to make unauthorised changes detectable. A hash creates a distinct value from a log record or group of records. If the content is altered later, the calculated value no longer matches the original. Chaining records together can also reveal the insertion or removal of events from a sequence. These techniques do not necessarily prevent every change, but they provide evidence that the data has been modified.
For investigations, preserving the original event is important. Normalisation converts different log formats into common fields, such as source address, user, timestamp and event type, so that the SIEM can correlate them. However, the original message should generally remain available alongside the normalised representation. This allows an analyst to verify how the platform interpreted the event and reduces the risk that useful detail is lost during parsing.
Separation of duties limits the impact of a compromised account. The people and services that administer the SIEM should not automatically have unrestricted ability to remove or rewrite historical records. Administrative activity should itself be logged, including changes to collection rules, retention settings, alert logic and integrations. Where appropriate, approvals and dual authorisation can be used for sensitive actions such as deleting evidence or changing the destination for archived logs.
Resilience also forms part of log protection. A SIEM should be designed to cope with temporary loss of a collector, a failed storage component or a network interruption without silently discarding events. Common measures include:
- buffering events at the source or collector while the central service is unavailable;
- replicating important data across separate infrastructure components;
- backing up configuration and log data to a suitably protected location;
- monitoring storage capacity before it becomes exhausted; and
- testing restoration procedures rather than assuming that an untested backup is usable.
These measures should distinguish between the live searchable copy and any preserved copy used for recovery or formal investigation. If both copies depend on the same system or administrator, a single compromise could affect them together. A separate preservation path can provide stronger assurance, particularly for records relating to suspected attacks.
The SIEM must also protect itself from log-based attacks. Attackers may generate very large volumes of events to exhaust storage, obscure meaningful activity or increase processing costs. They may also insert misleading text into fields that analysts or downstream tools trust. Rate monitoring, input validation, source quotas and detection of abnormal ingestion patterns help identify this behaviour. Parsing rules should treat log fields as data rather than executable instructions, especially where records may later be displayed or exported.
Accurate time is essential to the evidential value of logs. Systems should use a controlled time source and record the relevant time zone or offset. The SIEM should identify sources whose clocks drift beyond an acceptable tolerance. If timestamps cannot be trusted, the sequence of events becomes harder to establish and correlations between systems may be misleading.
Protection must also account for personal and commercially sensitive information. Logs can contain usernames, email addresses, device identifiers, client references, network addresses or application data. Collection should therefore be limited to information that supports a defined security or operational purpose. Sensitive fields may need masking, filtering or restricted viewing, while retention and disposal rules should remove records when there is no continuing requirement to keep them.
Finally, the protection controls themselves require monitoring and testing. Useful checks include detecting a stopped log source, an unexpected change in an ingestion rule, failed backup jobs, altered integrity markers, unusual administrative activity and attempts to access preserved records. Periodic reviews should confirm that the SIEM still receives the intended sources, that recovery copies can be restored and that authorised staff can explain how a record was collected and preserved.
A SIEM is therefore only as trustworthy as its surrounding design and governance. Correct configuration, reliable source connectivity, preserved originals, tamper detection, resilient copies, accurate timestamps and auditable administration work together to ensure that collected logs remain dependable evidence rather than merely searchable event data.
Encryption protects SIEM logs by making their content unreadable to anyone who obtains the storage media, backup files or intercepted data without the relevant decryption key. It should cover both data being transferred into the SIEM and data held in live, archived or recovery storage.
Encryption is only as effective as its key management. Decryption keys should be kept separate from the log data, with access limited to specifically authorised services and administrators. Key use should be auditable, and rotation or replacement procedures should be defined so that a compromised key does not provide indefinite access to historical records.
Organisations should also confirm that encryption remains active across every copy of the logs, including exports and backups. A recovery test should verify that authorised personnel can decrypt preserved records when required, without giving routine administrators unrestricted access to the underlying keys.