
How do cyber security services prioritise vulnerabilities for remediation?
Cyber security services prioritise vulnerabilities by assessing how easily they can be exploited, the importance and exposure of the affected systems, and the potential impact on the organisation. Remediation usually starts with actively exploited or high-impact weaknesses, followed by lower-risk issues, while considering available mitigations, dependencies and the time needed to apply and verify each fix.
Cyber security services prioritise vulnerabilities through risk-based triage rather than treating every finding as equally urgent. The process combines technical severity with evidence about exploitation, affected assets, business importance, exposure, available controls and the practical consequences of leaving the weakness unresolved. This produces a remediation order that directs effort towards the vulnerabilities most likely to cause meaningful harm.
The first step is to establish what has actually been found and where it exists. Security teams consolidate results from vulnerability scanners, penetration tests, endpoint tools, cloud platforms, identity systems and threat intelligence. They remove duplicate findings, investigate false positives and confirm the affected software, device, account or service. An unverified scan result should not automatically receive the same priority as a confirmed weakness on a production system.
Technical scoring systems, such as the Common Vulnerability Scoring System (CVSS), provide a useful starting point. They can describe factors including the complexity of an attack, whether user interaction is needed and the consequences for confidentiality, integrity or availability. However, a base score does not describe the whole business risk. A medium-scoring vulnerability on an internet-facing system supporting sensitive operations may deserve attention before a higher-scoring issue on an isolated, well-controlled test device.
Effective triage normally considers the following questions:
- Is the vulnerability being actively exploited, associated with known attack activity or likely to attract attention from attackers?
- Can it be reached from the internet, a partner network, a user workstation or another compromised system?
- Does the affected asset support important business processes or hold sensitive information?
- Could exploitation allow account takeover, unauthorised access, data alteration, ransomware deployment or disruption?
- Are reliable controls already reducing the likelihood or impact, such as network isolation, strong access controls, endpoint protection or multi-factor authentication?
- Is a suitable patch, configuration change, compensating control or decommissioning option available?
- Could applying the fix interrupt a critical service or create compatibility issues that require testing and planning?
Asset context is particularly important. Organisations should maintain an accurate inventory linking systems to owners, locations, data types and business processes. The same vulnerability can have different priorities depending on whether it affects a public-facing application, a domain controller, a file server, an employee laptop or an unused device. Business owners and technical teams may also identify dependencies that are not visible in an automated scan, such as a system required for manufacturing, logistics or access to essential records.
Threat intelligence adds another layer of context. A vulnerability may move up the queue when credible information shows that attackers are exploiting it in the wild, when exploit code is publicly available or when it is commonly used as part of an attack chain. This does not mean every newly disclosed vulnerability requires immediate emergency action. It means the organisation should reassess its existing order when the threat landscape changes, particularly where vulnerable systems are exposed or poorly protected.
Prioritisation should distinguish between remediation and temporary risk reduction. The preferred response is often to install a tested security update, upgrade unsupported software, correct an insecure configuration or remove the affected service. Where that cannot be done immediately, a service may recommend measures such as restricting network access, disabling an unnecessary feature, applying stricter authentication, isolating the system or increasing monitoring. These controls reduce risk but should be recorded as interim measures rather than treated as a permanent replacement for fixing the underlying weakness.
Remediation plans also need ownership and evidence. Each significant finding should have an assigned person or team, a target date based on its risk, the selected treatment and any dependencies. Exceptions should be formally documented with the reason for delay, the controls in place, the responsible approver and a review date. This prevents accepted risk from becoming invisible and allows management to understand where exposure remains.
After a fix is applied, security teams verify that the vulnerability has genuinely been resolved. Verification may involve rescanning, checking the installed version, reviewing configuration, testing access restrictions or conducting a focused manual assessment. A ticket marked as complete is not proof of remediation: the update may have failed, the wrong asset may have been changed or the vulnerable component may still be present elsewhere. Verification results should be linked to the original finding so that the audit trail remains clear.
Priorities should be recalculated regularly rather than set once and left unchanged. New assets, changes to network exposure, newly discovered exploits, failed controls and changes in business importance can all alter the order. Useful reporting separates urgent open vulnerabilities from overdue items, recurring weaknesses, temporary mitigations and trends by asset owner or technology type. This helps an organisation address both immediate exposure and the process weaknesses that cause similar findings to return.
For a growing business, a practical vulnerability management process should be proportionate but disciplined: maintain an asset inventory, collect findings from relevant sources, validate them, apply consistent risk criteria, assign ownership, record exceptions and verify closure. Cyber security services can support this through ongoing monitoring, structured remediation advice and regular reviews, while decisions about operational impact and acceptable risk remain aligned with the organisation’s business priorities.
Cyber security services can improve vulnerability prioritisation by examining how individual weaknesses combine into an attack path. A lower-severity issue may become more significant when it provides access to a system, account or network segment that can be used to reach a more valuable target.
This approach also helps identify root causes. For example, several findings may result from one outdated platform, excessive privilege or insecure network rule. Correcting the underlying condition can reduce several related exposures at once, whereas addressing each scan result separately may leave the wider route open.
Prioritisation should therefore consider both the individual vulnerability and its relationship with other weaknesses. Security teams can group connected findings, identify the control that would most effectively interrupt the path, and give the responsible team a remediation plan that addresses the broader source of risk.
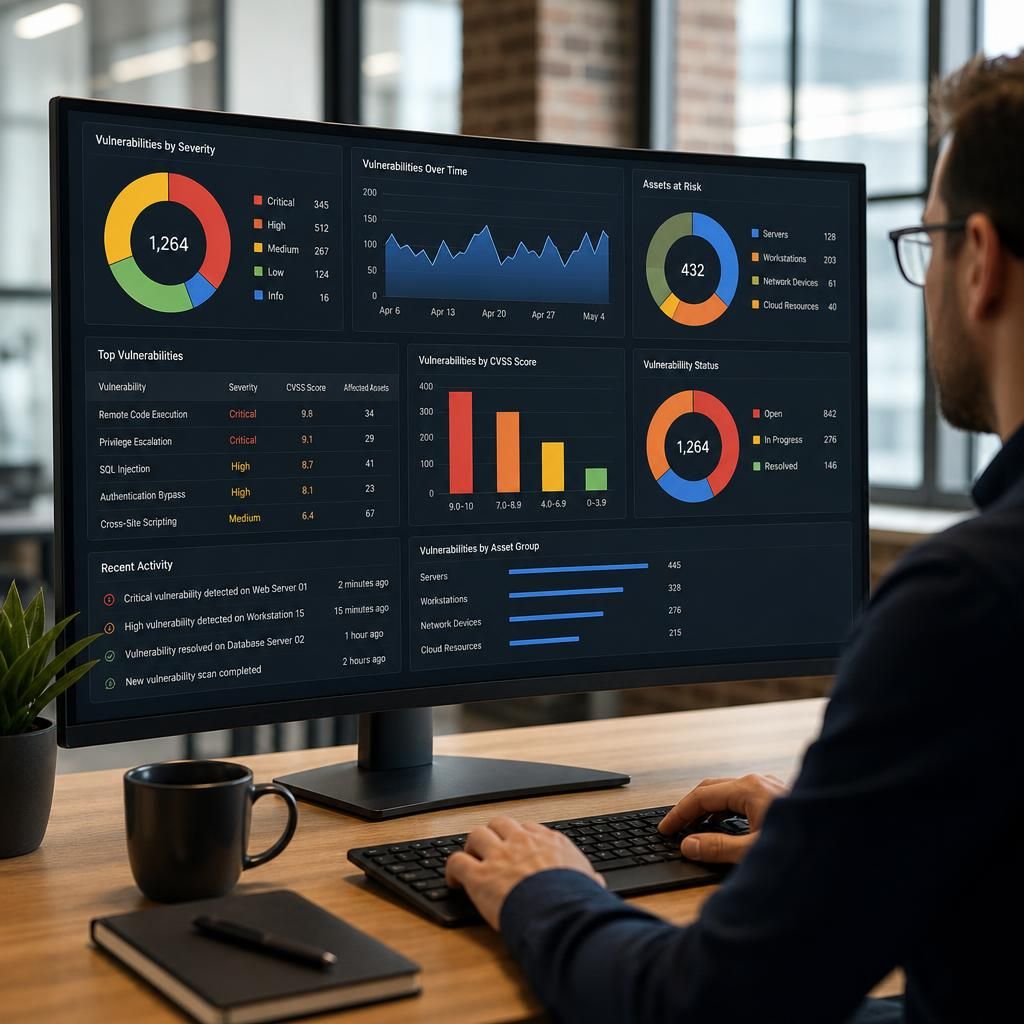
Discuss Your Vulnerability Remediation Priorities
Discuss your vulnerability remediation priorities with S2 Technology Group to assess whether your current process aligns security effort with business risk. You can then identify practical improvements to vulnerability management, reporting and remediation governance.