
What should a cyber risk assessment say about acceptable residual risk?
A cyber risk assessment should state which risks remain after controls are applied, why they are considered acceptable, who has formally accepted them and when the decision will be reviewed. Acceptable residual risk is not zero risk; it is the level remaining within the organisation’s defined risk appetite, supported by documented evidence, ownership and a clear treatment or monitoring plan.
Acceptable residual risk is a consciously tolerated level of exposure that remains after reasonable safeguards have been implemented. A useful cyber risk assessment should show that the organisation has evaluated this remaining exposure against its risk appetite, understood the possible consequences and made a proportionate decision about whether to tolerate, reduce, transfer or avoid it.
The assessment should not describe a risk as acceptable simply because eliminating it would be difficult or expensive. Acceptance requires a reasoned comparison between the potential impact, the likelihood of occurrence, the effectiveness of existing controls and the cost or practicality of further treatment. The decision should also take account of legal duties, contractual commitments, regulatory expectations, insurance conditions and the organisation’s obligations to customers, employees and other stakeholders.
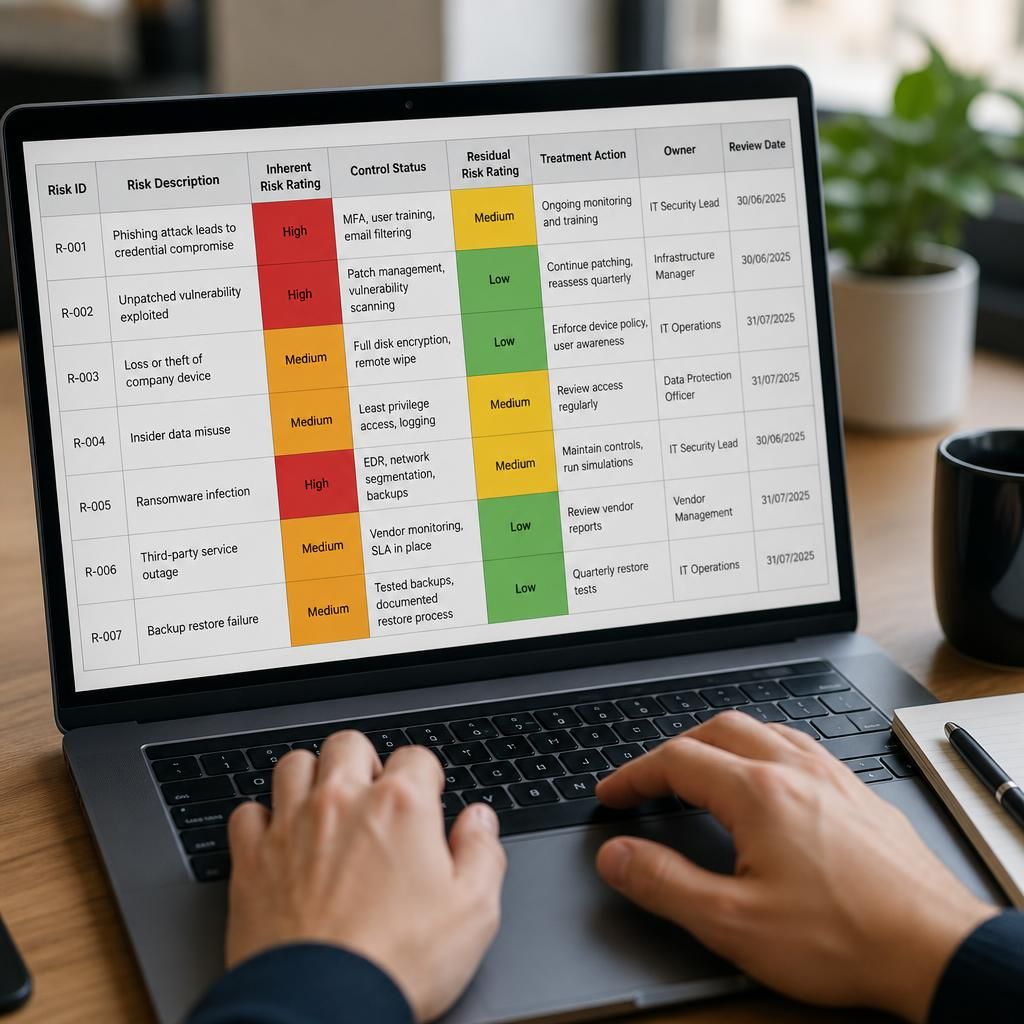
A clear residual-risk record should include:
- The original risk: what could happen, which asset or process is exposed and how the threat might occur.
- Existing controls: the technical, procedural and physical measures already in place, such as access controls, backups, security monitoring, staff training or network segregation.
- Remaining exposure: the risk that persists after those controls operate, including any known limitations, gaps or dependencies.
- Potential consequences: the effect on confidentiality, integrity and availability, together with operational, financial, legal, safety or reputational consequences where relevant.
- Likelihood reasoning: the factors supporting the likelihood rating, rather than an unexplained numerical score.
- Risk appetite comparison: the approved threshold or criteria used to determine whether the remaining exposure is within tolerance.
- Decision and authority: whether the risk is accepted, further treated, transferred or avoided, and the named person or body authorised to make that decision.
- Conditions: any safeguards, monitoring, restrictions or assumptions that must remain in place for acceptance to continue.
- Review arrangements: the circumstances and date for reconsidering the decision.
Risk appetite should be specific enough to support consistent decisions. An organisation might tolerate limited disruption to a low-impact internal service but have very little tolerance for unauthorised access to personal data, interruption to a critical production process or compromise of a system used for regulated activities. The assessment should explain these distinctions instead of applying one broad tolerance level to every system.
Where an organisation uses scoring, the method should be defined. It should be clear what each likelihood and impact category means, how scores are combined and what score ranges require escalation. A score by itself does not prove that risk is acceptable. A low likelihood may still be unsuitable for acceptance if the consequence would be severe, while a frequent but minor issue may be tolerable if effective safeguards and recovery arrangements are present.
Acceptance should be conditional where controls are essential. For example, a business may tolerate a known limitation in a legacy application only while network isolation, restricted administrative access, tested backups and a replacement plan remain in place. If one of those conditions changes, the original acceptance may no longer be valid. The assessment should therefore identify control dependencies and state what would cause the risk to be escalated.
Residual risk should normally be rejected or escalated where it exceeds approved tolerance, relies on an unverified assumption, conflicts with a legal or contractual requirement, or could cause consequences that the organisation has explicitly stated it will not accept. Acceptance by someone without suitable authority is not effective governance, even if the person understands the technical issue.
The person accepting the risk should have sufficient responsibility for the affected service or business process. Technical staff can explain the vulnerability and recommend treatment, but business ownership is usually needed to judge the operational consequences. For material risks, acceptance may require review by senior management, a risk committee, the board or another designated governance body.
The assessment should also distinguish between current residual risk and target residual risk. Current residual risk describes the exposure after controls that are already operating. Target residual risk describes the exposure expected after planned improvements. A planned control must not be treated as effective until it has been implemented, configured correctly and, where appropriate, tested. Otherwise, the assessment may give a misleading impression of the organisation’s present security position.
Monitoring is part of the acceptance decision. Useful indicators may include unresolved vulnerabilities, failed backup tests, unusual access activity, control exceptions, security incidents, supplier changes or deterioration in system performance. The chosen indicators should relate directly to the reason the risk was accepted. A formal review should be triggered when the threat landscape, technology, business process, supplier arrangement or relevant regulation changes, and after a significant incident or control failure.
A well-written conclusion might state that the identified exposure is within the approved tolerance because specified safeguards are operating, the possible impact has been assessed, no mandatory requirement is being breached and the accountable owner has approved the decision subject to defined monitoring and review. It should also record any actions that are still due, their owners and the consequences of not completing them.
Keeping this information together makes the decision auditable and prevents risk acceptance from becoming an informal verbal agreement. It gives management a basis for challenging assumptions, comparing risks across the business and deciding where further investment is justified. S2 Technology Group can help organisations assess these factors as part of a structured cyber security and IT risk management approach, with recommendations matched to their systems, processes and operating environment.
Acceptable residual risk should also be considered in aggregate, not only one risk at a time. Several individually tolerable exposures may combine to create a material business risk, particularly when they affect the same identity system, network segment, supplier, data set or recovery process.
The assessment should identify material dependencies and consider whether controls share a common point of failure. For example, separate risks involving account compromise, inadequate monitoring and limited recovery access may be more serious together than their individual ratings suggest. Management should therefore review concentrations, linked attack paths and the cumulative effect on critical services before confirming that residual risk remains within tolerance.
Where aggregation changes the overall judgement, the register should record the combined risk, the affected business services and the additional treatment or governance required. This prevents acceptance decisions from appearing reasonable in isolation while the organisation’s wider exposure exceeds what it is prepared to tolerate.
Discuss acceptable residual risk in your cyber risk assessment
Discuss your organisation’s approach to documenting and governing acceptable residual risk with S2 Technology Group. We can help you identify the information needed for a structured cyber risk assessment and align the process with your business requirements.