
How is small business backup data protected from ransomware?
Small business backup data is protected from ransomware by keeping isolated, access-controlled copies that malware cannot easily alter or delete, alongside encryption and monitored backup activity. Retaining multiple recovery points and regularly testing restoration helps the business recover from a clean version if files or systems are encrypted.
Small business backup data is protected from ransomware through layered controls that prevent an attacker from reaching every recovery copy, limit what compromised accounts can do, and preserve earlier versions of data. Effective protection depends on the design and administration of the backup system, not simply on having a backup job configured.
Keep backup systems separate from everyday user access. A ransomware infection often begins with a compromised user account, endpoint or server. If the same credentials and permissions can control the backup repository, an attacker may be able to erase recovery data as well as encrypt live files. Backup administration should therefore use separate accounts, minimum necessary permissions and multi-factor authentication where supported. Backup consoles, storage locations and management interfaces should not be exposed more widely than required.
Use immutability and deletion safeguards. An immutable recovery point cannot be changed during its protected period, including by an administrator or malware using a compromised account. Retention locks, write-once storage features and delayed deletion controls can reduce the risk of an attacker removing recent backups. These controls need careful configuration: an immutable copy that expires too soon, or a repository with an unprotected management account, may not provide useful ransomware resilience.
Separate at least one recovery copy from the normal attack path. A backup stored on a permanently connected network share can be affected if ransomware spreads through mapped drives or administrative credentials. A logically separated repository, removable copy managed under controlled procedures, or other isolated storage arrangement creates a boundary between production systems and recovery data. The appropriate design depends on the organisation’s infrastructure, the data being protected and how quickly it needs to be recovered.
Preserve history rather than relying on a mirror. A synchronised folder or real-time replica may copy an encrypted file, corrupted database or malicious change immediately. Backup protection should retain historical states so that recovery is not limited to the latest version. Retention should reflect how long an infection might remain unnoticed; keeping only very recent copies can leave no usable version if the attack is discovered late.
Protect the backup service itself. Backup agents, servers and storage appliances require security updates, restricted network access and appropriate endpoint protection. Administrative activity should be recorded so that unexpected changes to schedules, destinations, retention settings or deletion policies can be investigated. Alerts should identify failures and significant configuration changes, rather than treating a completed transfer as proof that the data can be recovered.
Check that recovery points are usable. A backup can appear successful while containing an unreadable file, an incomplete application database or credentials that are no longer valid. Recovery procedures should account for dependencies such as domain services, business applications, permissions and encryption keys. Where possible, restoration should be performed in a controlled environment before affected systems are returned to production, reducing the risk of reintroducing malware or damaging evidence from an incident.
Define a ransomware recovery procedure in advance. The process should state who can declare an incident, how infected devices are isolated, which systems are prioritised and how a clean recovery point is selected. It should also cover communication with staff, suppliers and relevant professional advisers, together with investigation of the original entry point. Restoring files without addressing the compromised account, exposed service or vulnerable device can allow the attacker to regain access.
For a small business, the practical objective is a backup design with separate privileges, protected history, an independent recovery path and a documented restoration process. S2 Technology Group can review these controls as part of a wider managed IT and cyber security assessment, helping organisations around Stourbridge and neighbouring areas identify weaknesses in their backup arrangements.
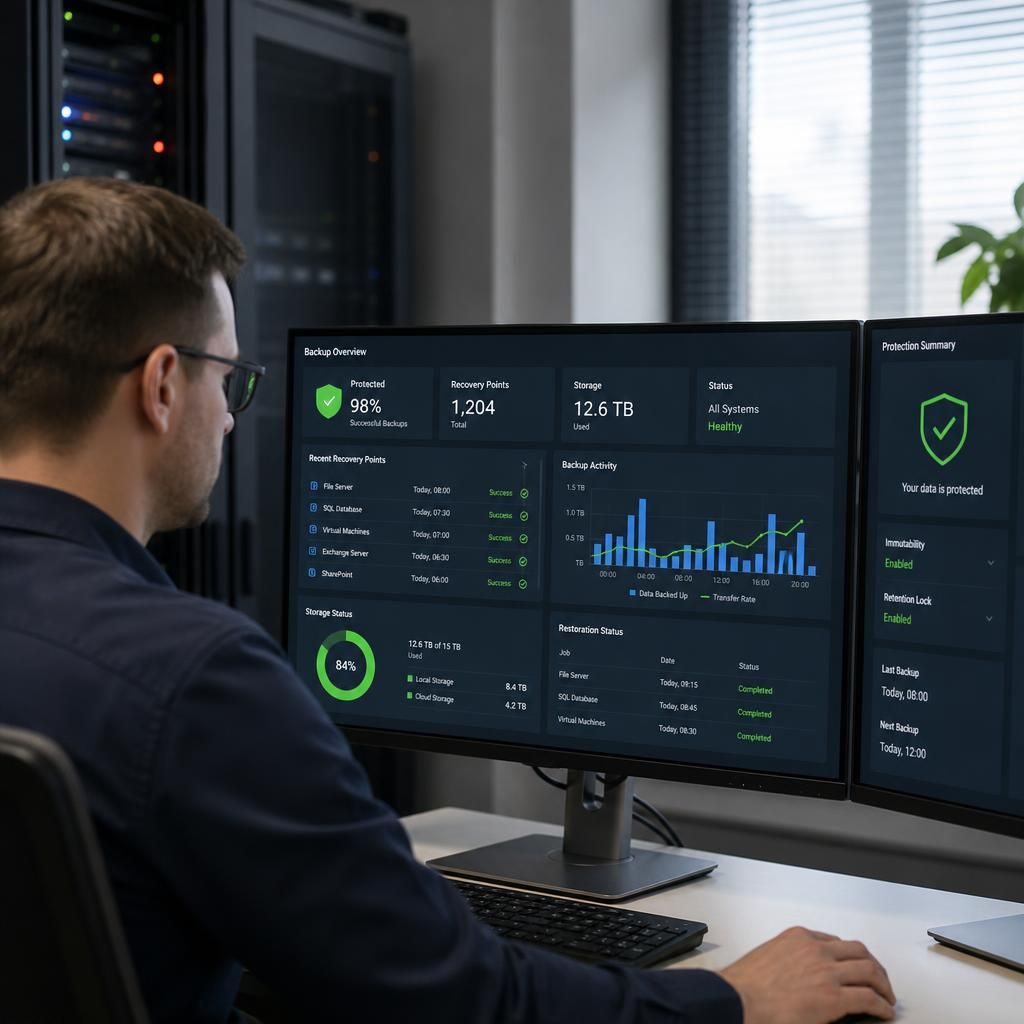
Encryption protects backup data from unauthorised access if a repository, device or transfer channel is exposed. Data should be encrypted both while it is moving from business systems to the backup location and while it is stored. Encryption keys should be managed separately from the backup files, with access limited to authorised administrators.
Encryption is a confidentiality control, not ransomware protection on its own. If malware or a compromised administrator can use the backup system’s legitimate permissions, it may still be able to alter or delete unencrypted recovery points—or access them after decryption. Ransomware resilience therefore requires encryption to be combined with restricted administration, protected retention and an independent recovery copy.