
What is the difference between backup and disaster recovery?
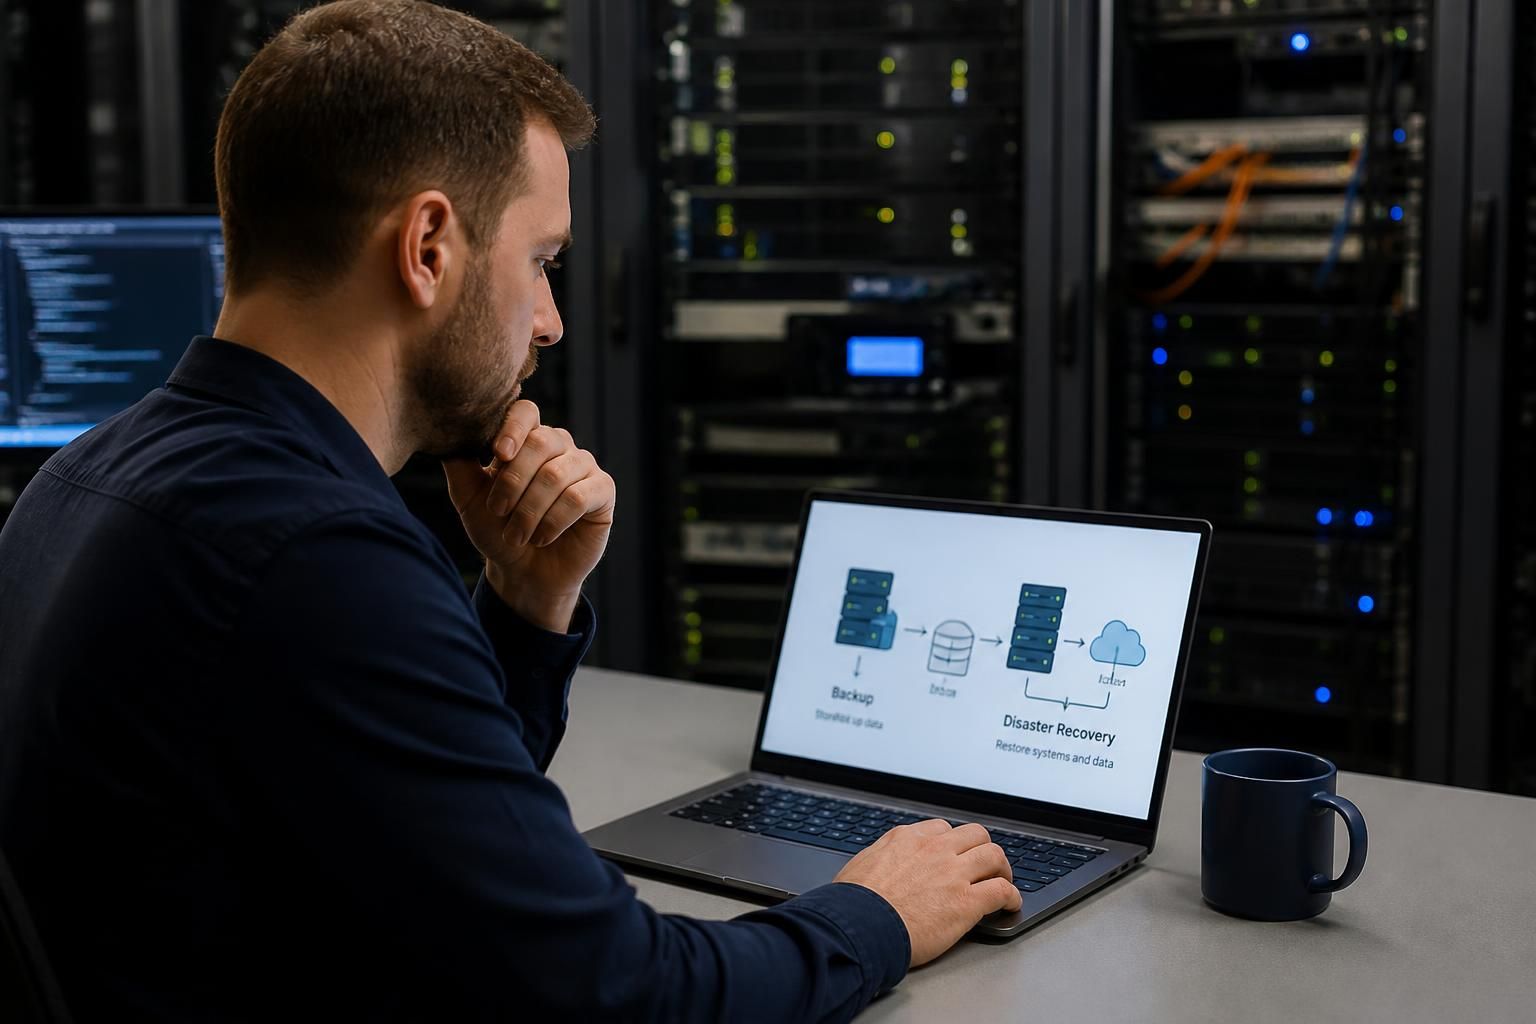
Backup is a copy of data held separately so it can be restored after deletion, corruption or hardware failure. Disaster recovery is the wider plan for restoring data, systems and business operations after a serious disruption, using backups as one part of the process.
The practical distinction is that backup addresses the preservation of information, while disaster recovery addresses the restoration of usable technology services. A business may have several copies of its files and databases yet still lack a workable disaster recovery capability if it has not established how applications, user access, infrastructure and business processes will be brought back together.
Backup is primarily about recoverable data. It involves creating and maintaining copies of files, databases, system configurations or other information so that an earlier state can be retrieved. This is useful after accidental deletion, file corruption, malware activity, a failed device or an incorrect change. The backup process normally considers what is copied, where copies are stored, how often copies are created, how long they are retained and how access to them is controlled.
A backup does not necessarily provide a complete working environment. Restoring a database, for example, may recover the data but not the server that hosts it, the application that reads it, the user permissions that control access or the network connections required by other systems. These additional dependencies are why a successful backup job report is not the same as proof that the business can resume operations.
Disaster recovery is a coordinated restoration capability. It covers the people, procedures, technology and decisions required after a major disruption. The disruption could affect a server, site, cloud service, network, identity platform or several connected systems at once. A disaster recovery arrangement should identify which services are critical, the order in which they should be restored, the resources needed for restoration and how users will be given access to those services.
Disaster recovery can include backup restoration, but it may also involve replicated systems, standby infrastructure, alternative connectivity, documented configuration, replacement equipment, recovery environments and communication procedures. Its scope is therefore wider than the backup repository. The aim is not merely to locate a file; it is to re-establish the technology functions on which the organisation depends.
The two concepts are linked but not interchangeable. Backup supplies recovery points. Disaster recovery defines how those recovery points, together with other resources, are used to restore operations. A disaster recovery plan without usable copies of current data may restore systems containing incomplete or outdated information. Backups without a tested recovery plan may leave the organisation uncertain about what can be restored, in what order and with which dependencies.
Two measures help clarify the difference:
- Recovery point objective (RPO): the acceptable amount of data that could be lost, expressed as a period between the latest usable copy and the disruption. RPO influences backup frequency, replication and the choice of data that needs more frequent protection.
- Recovery time objective (RTO): the target time for restoring a service or system to an agreed level of operation. RTO influences the recovery method, available infrastructure, restoration sequence and the degree of preparation required.
These objectives should be set according to business impact rather than applied uniformly. A customer database, production system or finance platform may require different recovery priorities from archived documents or non-essential applications. Prioritisation should consider legal and contractual obligations, operational dependencies, financial consequences and the effect of an outage on customers and staff.
Consider a server failure. A backup may allow the business to restore the files held on that server. A disaster recovery process would also address how the replacement or recovery environment is prepared, how the operating system and applications are restored, how identity and permissions are reconnected, how data consistency is checked and how users confirm that the service is functional. If the server supported other systems, those relationships would need to be included in the recovery sequence.
Consider a ransomware incident. The recovery question is not simply whether a copy exists. The organisation must determine which recovery points pre-date the compromise, prevent the threat from reaching protected copies, verify that restored data is suitable, rebuild or clean affected systems and control the return of users and devices. This is a disaster recovery activity supported by secure, independently usable backups.
Good practice treats recovery as a process that requires evidence. Backup copies should be checked for integrity, recovery procedures should be tested, restoration dependencies should be documented and the results should be reviewed when systems or business requirements change. Testing can reveal issues such as missing credentials, undocumented applications, unsuitable retention periods, incompatible configurations or restoration times that do not meet operational needs.
In summary, backup is one component of resilience: it preserves information that may need to be retrieved. Disaster recovery is the wider capability for deciding what must be restored, preparing the necessary environment, carrying out the restoration and validating that business services can operate again. S2 Technology Group can help organisations assess these requirements as part of its managed IT, cyber security and cloud services, with the focus on aligning protection and recovery arrangements with the systems the business actually relies on.
Backup is a preventative activity carried out before disruption, while disaster recovery is an event-driven capability used when a service or system needs to be brought back into operation. Backup work can continue as part of normal IT administration even when no incident has occurred; disaster recovery planning becomes relevant when deciding how to respond to a failure, attack or major interruption.
This difference also affects responsibility. Backup administration usually centres on storage, schedules, retention and protected copies. Disaster recovery requires wider coordination between IT, system owners and business decision-makers, including agreement on which services take priority and when they are fit to return to use. Treating these as separate but connected disciplines makes it easier to identify gaps that a backup report alone cannot show.