
How is backup access protected from compromised administrator accounts?
Backup access is protected by separating backup administration from ordinary user accounts, enforcing multi-factor authentication and applying least-privilege permissions. Additional safeguards can include separate credentials, approval for sensitive actions, activity monitoring and rapid access revocation if an administrator account is compromised.
Backup access is best protected from a compromised administrator account by ensuring that no single account can independently reach, alter or delete every backup copy. This requires separation between the systems that manage production IT and those that control backup infrastructure, together with independent recovery controls that remain usable if the main administrator identity is taken over.
Keep backup administration outside the normal domain. If the backup management server, storage platform and administrator identities are all dependent on the same directory service, an attacker who controls that directory may be able to attack the backups as well as live systems. Backup administration should therefore use a separately managed security boundary where practical. This can include an independent identity service, a dedicated management network and backup infrastructure that is not routinely administered from ordinary user workstations.
The design should also prevent a compromised production administrator from changing the settings that govern every copy. For example, backup storage can be placed in a separate account, subscription or security domain, with its own ownership and recovery arrangements. This limits the effect of an attack on the organisation’s main administrative environment.
Use dual control for destructive operations. Deleting backup chains, shortening retention, disabling protection or changing storage destinations should require more than one trusted person or approval path. A second administrator can verify that the request is legitimate before the action is completed. This is particularly important for changes affecting immutable or otherwise protected copies, because such changes may directly determine whether recovery remains possible after an incident.
Where the platform supports it, sensitive actions should be time-limited and granted only for the specific task. This reduces the period in which a powerful account can be abused and creates a clear record of why elevated access was used. Emergency access should be treated as a controlled break-glass process: its credentials must be stored securely, access should be restricted to named individuals, and use should trigger a formal review.
Protect the recovery authority separately from the backup operator. The person who runs or maintains backup jobs does not necessarily need authority to release protected copies, alter retention, or obtain encryption keys. Separating these responsibilities reduces the damage that can result from one stolen account and helps prevent an attacker from both compromising backups and concealing the change.
Encryption provides another layer of protection, but its keys must not be controlled solely through the same administrator account as the backup data. Key management should have its own access policy, recovery procedure and safeguards. Losing the keys can make a valid backup unusable, while allowing a compromised administrator to obtain both data and keys undermines the value of encryption.
Network controls should restrict where backup management interfaces can be reached from. Administrative access can be limited to approved management devices or networks, with direct access from general office endpoints blocked where possible. Backup storage should also be prevented from initiating unnecessary connections back into the production environment. These measures reduce the routes available to an attacker who has taken over a workstation or server administrator account.
Access protection is incomplete without a tested response procedure. The procedure should identify which accounts and sessions must be disabled, how backup administration is isolated, how protected copies are checked, and how clean recovery access is established. It should also cover the possibility that an attacker has changed backup settings without deleting data, such as altering retention, schedules or destinations.
- Review who can administer backup infrastructure, protected storage and encryption keys.
- Check whether those permissions depend on the organisation’s ordinary domain or administrator accounts.
- Verify that destructive changes require an independent approval or equivalent control.
- Confirm that emergency credentials can be accessed by authorised staff without relying on a potentially compromised identity system.
- Test administrative isolation and recovery access as part of a documented incident exercise.
For small and medium-sized organisations, these controls should be proportionate but deliberate. A managed IT provider such as S2 Technology Group can help businesses around Stourbridge review the relationship between their production identities, backup platform and recovery permissions, then document a design that limits the consequences of a compromised administrator account.
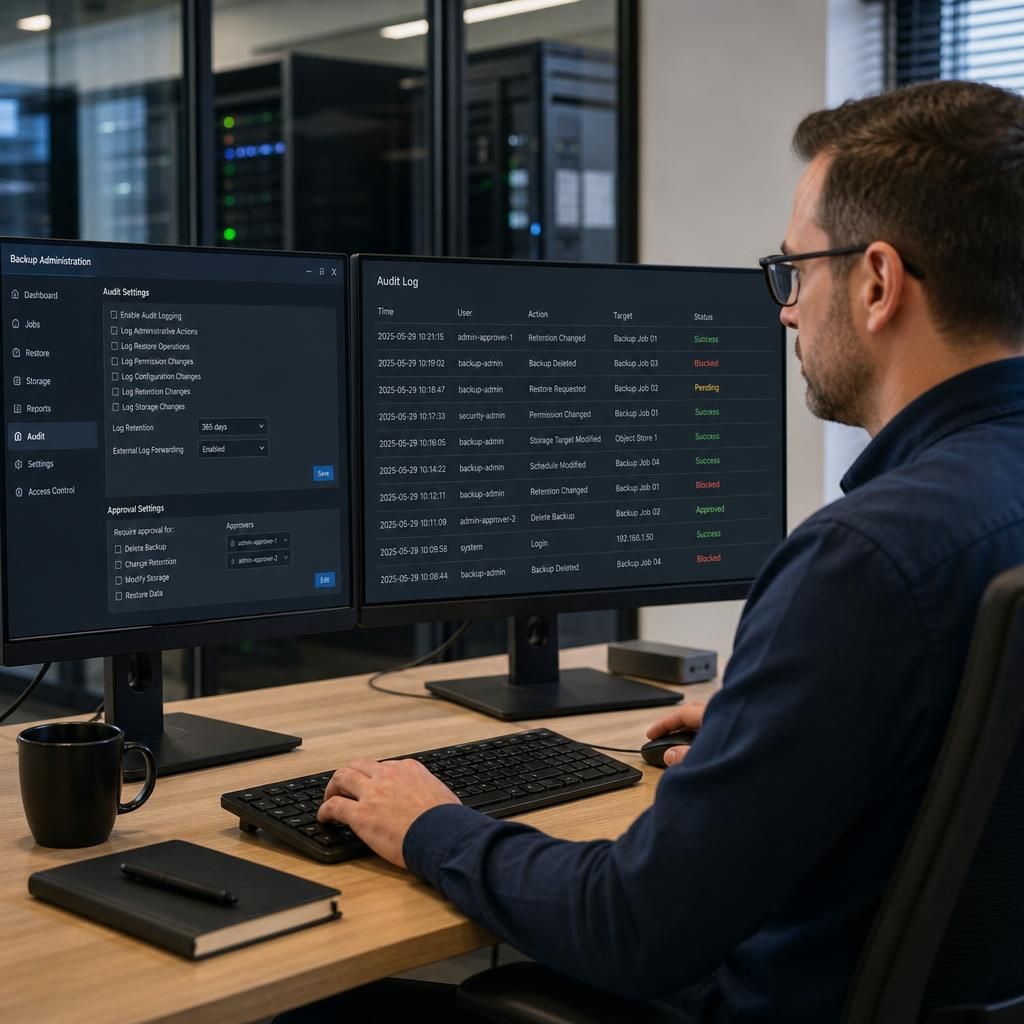
Audit records should be protected from the administrator accounts they monitor. Backup activity logs can show changes to retention, schedules, storage targets, permissions and recovery requests, but they are less useful if a compromised administrator can edit or delete them. Forwarding relevant events to a separately controlled logging system preserves evidence outside the backup platform.
Monitoring should highlight unusual administrative behaviour, such as access from an unapproved management device, repeated failed authentication, sudden permission changes or attempts to remove protected data. Alerts should be reviewed through an independent route, allowing the organisation to investigate suspicious activity before it affects recovery. Log retention and access should be included in the backup security review so that records remain available during an incident.