How are backup exclusions identified and reviewed?
Backup exclusions are identified by comparing the proposed exclusion list with the organisation’s data inventory, backup policy and recovery requirements. They should be reviewed when systems, applications or data locations change, with each exclusion documented, approved by an appropriate owner and periodically checked to confirm that it remains justified.
Backup exclusions are identified and reviewed through a controlled assessment of what data is omitted, why it is omitted and what effect that omission would have on recovery. The process should distinguish between data that is genuinely unsuitable for backup and data that has been overlooked, assumed to be reproducible or excluded only because of a technical limitation.
The initial assessment should examine how the backup configuration defines exclusions. These may be based on folders, file extensions, storage volumes, application types, user accounts, devices or data locations. Reviewing the configuration in this detail helps reveal exclusions that are broader than intended, such as an entire directory being omitted when only temporary files were meant to be excluded. It also identifies rules that may apply differently across servers, workstations, virtual machines or remote devices.
Each exclusion should then be assessed against the nature of the data it contains. Common candidates for exclusion include operating system caches, temporary files, transient processing data and other material that can be recreated without relying on a backup. By contrast, databases, configuration files, application content, shared working documents, security records and data held on locally attached or remote storage require closer scrutiny. A file that appears replaceable may still contain unique settings, audit information or the latest version of a business record.
Identification should not rely solely on the backup console. Useful evidence can come from storage reports, application owners, system administrators, data protection records, access reviews and recovery documentation. Comparing these sources can expose data that is used by the business but is not included in the configured backup scope. It can also identify duplicate copies, obsolete repositories and locations created by new software or changes to the way staff work.
Exclusions should be treated as risk decisions rather than merely performance settings. Relevant questions include:
- Could the data be recreated from a known source, or would its loss require manual reconstruction?
- Would losing it affect financial records, contractual obligations, regulated information or operational processes?
- Does an application depend on the excluded data to start, authenticate users or restore its configuration?
- Is another protection method documented and actually usable, or is the exclusion relying on an assumption?
- Could the exclusion expose sensitive information to an inappropriate storage location, or does it leave that information without suitable protection?
Reviewers should pay particular attention to exclusions introduced by default templates, inherited settings and exceptions added to resolve failed backup jobs. An exclusion created to bypass a locked file, excessive data volume or recurring error may conceal a deeper issue. The underlying cause should be investigated before the exclusion is accepted as a permanent configuration choice. Similarly, broad wildcard rules and exclusions applied to whole user or application directories warrant evidence that their full contents are non-essential.
A sound review also considers dependencies. A database may require its transaction logs, application configuration and encryption keys to be recoverable together. A virtual machine may be backed up at image level while still requiring separate consideration of hosted databases or externally connected storage. Cloud applications and synchronised folders can create further ambiguity because a visible copy does not necessarily represent an independent, recoverable backup.
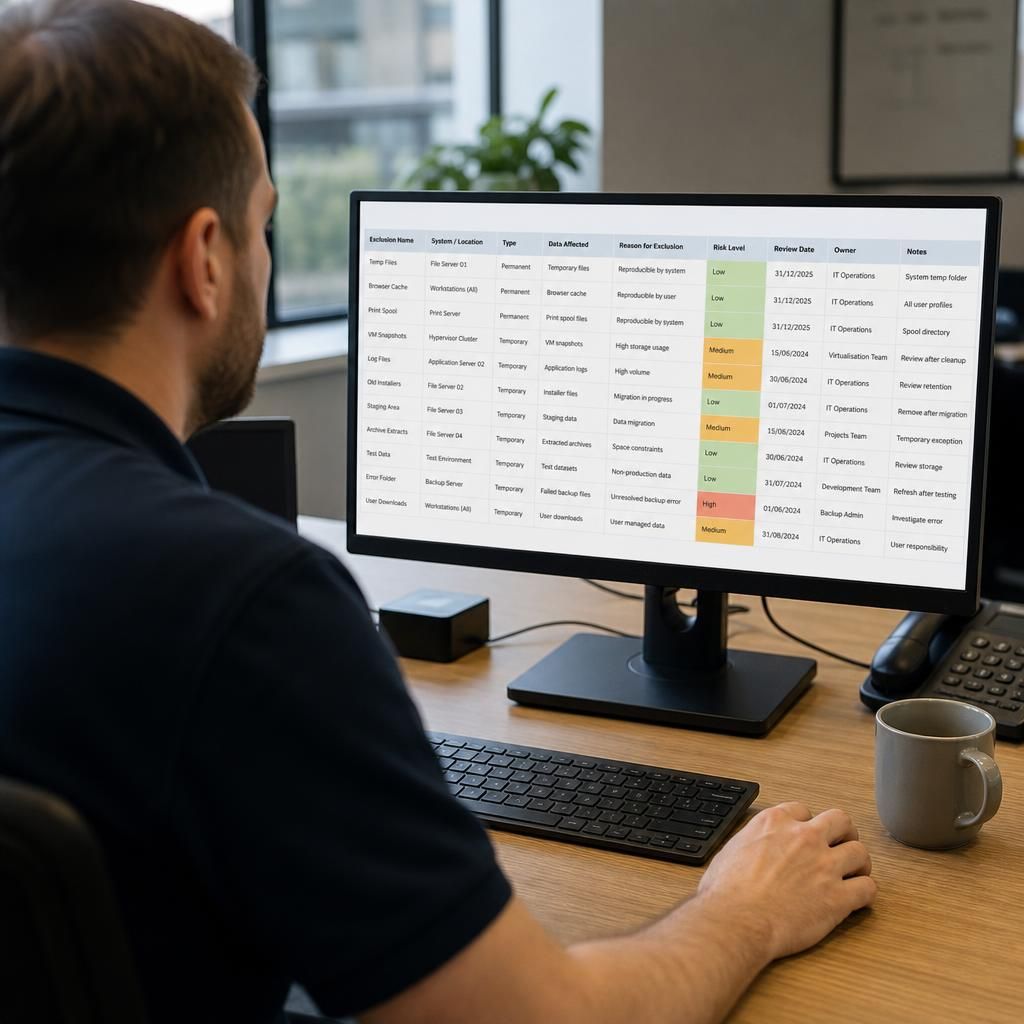
Review activity should record the precise rule, affected systems, data types, reason for exclusion, associated risk and any alternative protection. The record should identify who assessed the exclusion and what evidence supported the decision. Where the decision is conditional, it should state the required safeguard, such as replication, export, archiving or a documented rebuild procedure, rather than describing an unverified assumption as protection.
Technical checks provide an important second line of assurance. A report can show that a job completed while still failing to reveal that valuable data was excluded before processing began. File and folder comparisons, application-aware checks, inventory changes and recovery exercises can help verify that the intended scope is actually being protected. If an exclusion is removed or narrowed, the next backup cycle should be checked to confirm that the change took effect and did not introduce new errors.
Reviews should also be triggered by events that alter data use or recovery needs. Examples include a new application, migration to different storage, organisational restructuring, changes to legal or contractual requirements, replacement of an in-house system and the discovery of previously unknown data repositories. A scheduled governance review remains useful, but event-driven checks are important because an exclusion can become unsuitable as soon as the surrounding system changes.
For small and medium-sized organisations, a practical approach is to maintain a central exclusion register, link each entry to the relevant backup configuration and review high-risk entries with the people responsible for the affected systems. This creates an auditable trail without requiring every technical detail to be reassessed in the same way. Entries involving critical applications, unique business data or uncertain recovery methods should receive more scrutiny than exclusions covering demonstrably disposable temporary content.
Backup exclusions should be classified as either permanent rules or temporary exceptions. A permanent exclusion applies to data that is consistently reproducible and unsuitable for backup, such as disposable processing files. A temporary exception usually exists because of a migration, troubleshooting activity, storage constraint or unresolved backup error, and should not be allowed to become a lasting omission by default.
Temporary exclusions should have a defined review date or a clear condition for removal. When that point is reached, the responsible person should confirm whether the underlying issue has been resolved and whether the exclusion can be narrowed or removed. If it still appears necessary, it should be reassessed rather than automatically renewed, with the reason, current risk and any compensating protection recorded. This prevents short-term technical workarounds from quietly creating long-term gaps in recoverable business data.