What should cyber security services include in an incident response plan?
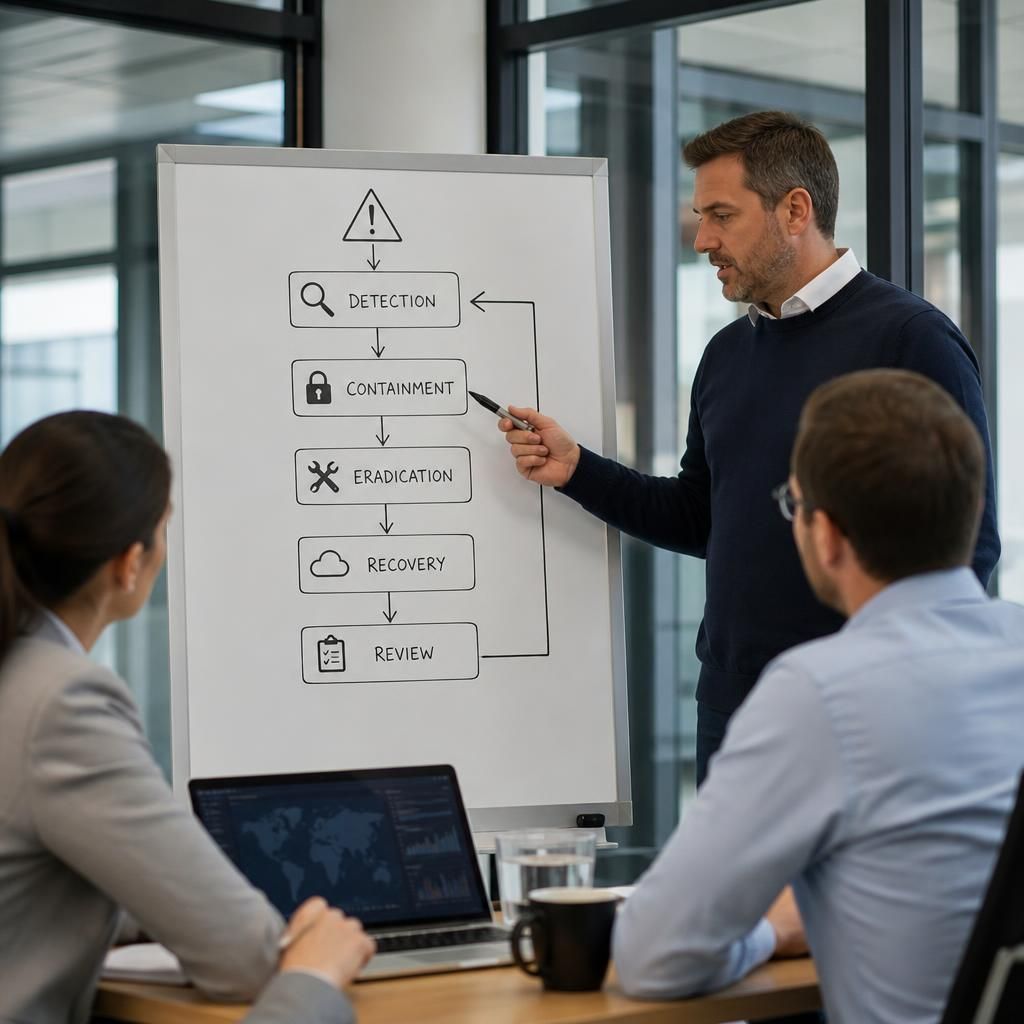
Cyber security services should include an incident response plan covering preparation, threat detection, containment, eradication, recovery and post-incident review. It should also define responsibilities, escalation routes, communication procedures, evidence handling and testing arrangements so a business can respond in a controlled, consistent way.
An effective incident response plan is a practical set of instructions for making consistent decisions when a security event affects systems, accounts, data or business operations. It should be specific enough to guide people under pressure, while flexible enough to apply to different incidents and technology environments.
Define the plan’s scope and assumptions. Set out which locations, networks, cloud services, devices, applications, data stores and third-party connections are covered. The plan should also record important assumptions, such as whether the organisation has access to administrative accounts, offline backups, centralised logs or external technical support. This prevents the response from relying on resources that may be unavailable during an incident.
Use clear incident categories and severity levels. A suspected phishing email, a lost device, a compromised administrator account and a ransomware outbreak do not require identical actions. The plan should describe common event types and provide criteria for classifying their impact. Useful criteria include the sensitivity of affected data, the number of users or systems involved, whether unauthorised access is ongoing, and whether essential business processes are disrupted.
Severity criteria should lead to defined decision points. For example, a suspected account compromise may require immediate credential protection and a review of sign-in activity, while a suspected data breach may also require assessment by legal, compliance or data protection specialists. Clear thresholds reduce delays and help prevent minor events from being treated as major incidents, or serious incidents from being underestimated.
Include incident-specific playbooks. A general plan is easier to use when supported by short procedures for likely scenarios, such as:
- phishing or business email compromise;
- malware or ransomware affecting endpoints or servers;
- unauthorised access to a cloud service;
- loss or theft of a laptop or mobile device;
- exposure of confidential information;
- an unknown device or account appearing on the network; and
- a security issue originating with a supplier or hosted service.
Each playbook should state the first checks to perform, the systems that may need to be isolated, the information to collect, and the conditions for moving to the next action. Procedures should avoid prescribing destructive actions, such as deleting files or rebuilding systems, before relevant evidence has been secured.
Specify technical decision rules. The plan should explain when to disable an account, revoke active sessions, reset credentials, quarantine a device, block a domain, restrict a firewall rule or suspend a connection to a supplier. It should identify who can approve those actions and how to record them. This is particularly important where an aggressive containment measure could interrupt production, remove access to essential records or affect multiple sites.
Identity-related instructions deserve particular attention. A response may need to cover privileged accounts, shared accounts, service accounts, multifactor authentication, remote access and delegated permissions. The plan should distinguish between protecting a suspected compromised account and preserving information needed to establish how it was used.
Set out the information required for investigation. Relevant sources may include authentication records, endpoint alerts, email headers, firewall events, cloud audit logs, file access records and details supplied by users. The plan should state where these records are obtained, how they are protected from alteration, and how timestamps are reconciled when systems use different time settings.
Evidence records should link each item to the incident, identify who collected it and note when and how it was obtained. This supports a reliable investigation and may be important for an insurance claim, disciplinary process, contractual dispute or regulatory enquiry. Staff should also know not to forward suspicious messages unnecessarily, edit potentially relevant files or communicate speculative conclusions as established facts.
Account for legal, contractual and insurance requirements. The plan should identify who assesses whether personal data, commercially sensitive information or regulated records are involved. It should also list relevant contracts, customer commitments, cyber insurance conditions and sector-specific obligations. A data protection lead or legal adviser can determine whether notification is required and what information should be provided. The plan should make these routes easy to find without attempting to replace professional legal advice.
Define recovery acceptance criteria. Restoring a backup or rebuilding a device does not by itself prove that a system is safe to return to use. The plan should specify checks such as confirming that unauthorised accounts have been removed, security updates are applied, protective controls are functioning, credentials have been reviewed and restored data is complete. Business owners should confirm that important processes work correctly before normal operation resumes.
It should also cover the risk of reinfection. Systems may need to be restored in a controlled order, with dependencies documented between identity services, networks, applications, file stores and operational technology. Any temporary workarounds should have an owner and a clear route to permanent resolution.
Make the plan usable and maintainable. Store a protected copy where it remains accessible if the primary network or document platform is unavailable. Remove obsolete contact details, update technology references after major changes and review the plan following incidents, exercises, acquisitions, office moves or the introduction of new cloud services. Testing should include both technical simulations and decision-making exercises, with actions recorded and assigned to named owners.
Cyber security services can support this work by reviewing the organisation’s systems and dependencies, developing scenario playbooks, checking logging and backup arrangements, and helping assess lessons from exercises or real incidents. The result should be a living operational document that reflects the business’s actual environment rather than a generic template.
Incident communications are the controlled messages shared with staff, customers, suppliers, advisers and other stakeholders while a security event is being assessed. An incident response plan should define who may approve each type of message, which audiences need to be informed, and what information must be verified before it is released.
The plan should identify trusted communication channels in case email, collaboration tools or telephony are affected or under an attacker’s control. It should also provide a concise format for updates covering the known facts, current business impact, actions underway and any required recipient action. Speculation, unverified causes and unnecessary technical detail should be excluded.
A designated communications lead can maintain a record of messages issued, approvals received and questions raised. This helps keep employees and external parties aligned, reduces conflicting statements and gives the organisation a clear record for later review. Customer, supplier and insurer communications should follow the relevant contractual and regulatory requirements.