
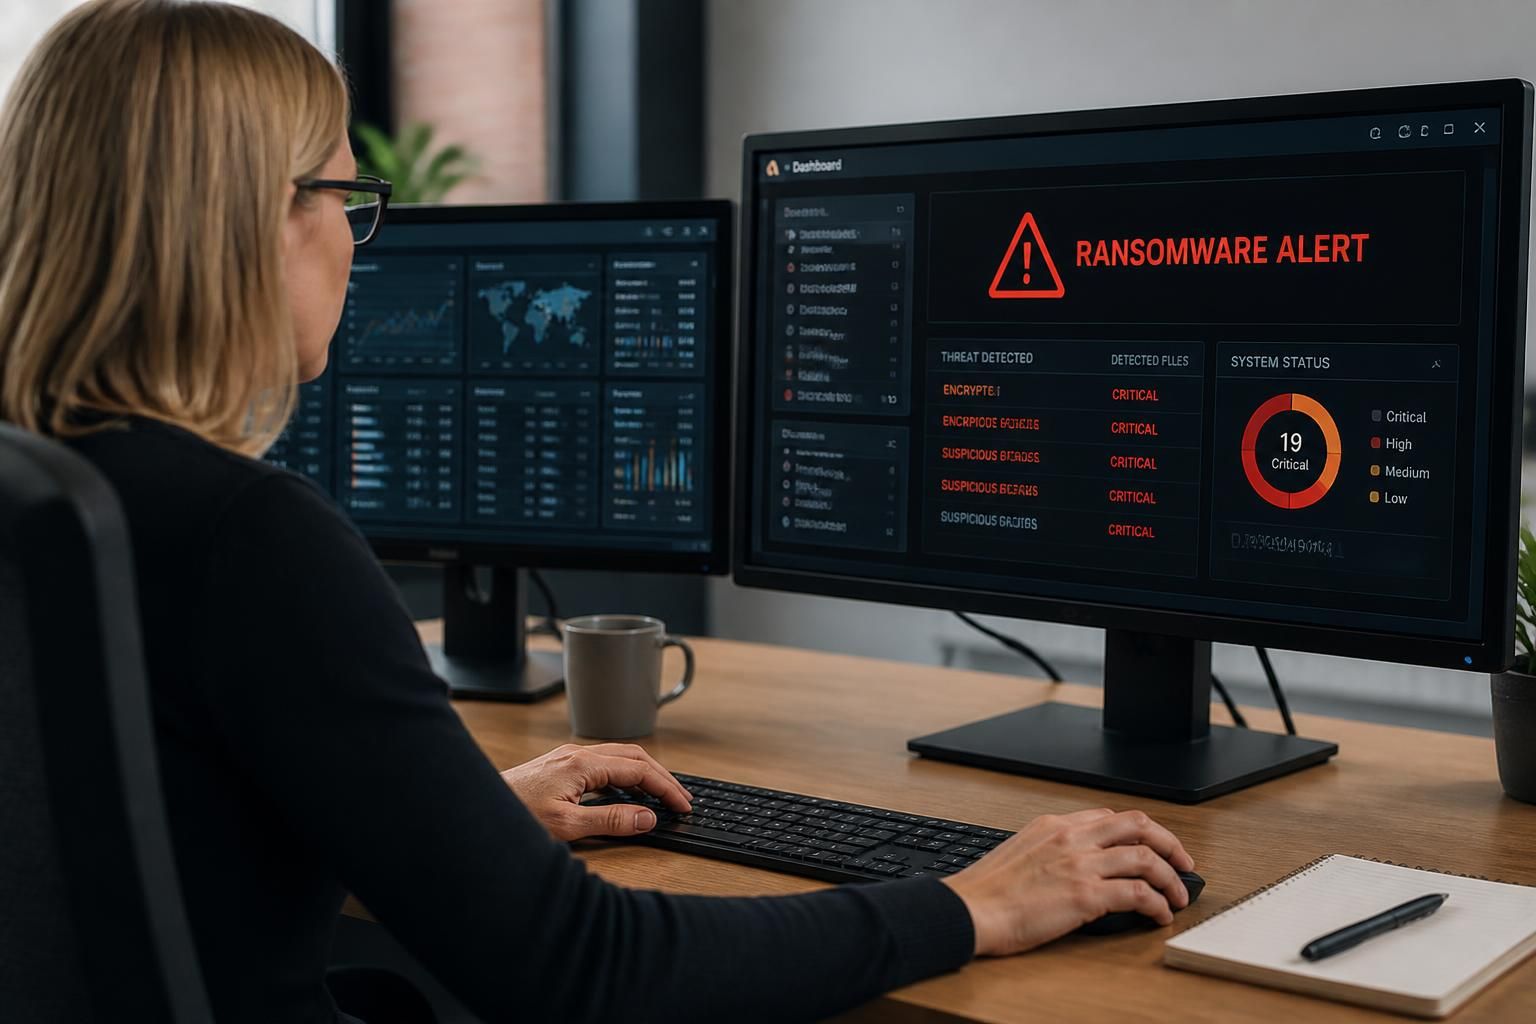
How can cyber security services protect a business from ransomware?
Cyber security services protect a business from ransomware by reducing the opportunities for malicious software to enter, spread and disrupt systems. They combine proactive monitoring, secure backups, access controls, software updates and incident response measures to help prevent attacks, limit their impact and support recovery if an infection occurs.
Cyber security services protect a business from ransomware by addressing the complete attack path, not just the malware itself. They help reduce the likelihood of initial compromise, restrict what an attacker can reach, identify suspicious activity and prepare the organisation to restore critical operations without relying on guesswork.
They begin by identifying the systems and processes that matter most. A risk assessment can map business-critical applications, sensitive data, user accounts, endpoints, cloud services and connections to suppliers. This shows where ransomware would cause the greatest disruption and which weaknesses could allow an attacker to move from one part of the environment to another. The resulting priorities should reflect the organisation’s operations rather than applying identical controls to every system.
Measures that reduce common entry routes can prevent an attack before files are encrypted. These may include email filtering, protection against malicious websites, restrictions on unsafe scripts and macros, application allowlisting, and controls that prevent unapproved executables from running. Security services can also review how internet-facing systems are configured and whether exposed services are genuinely required. Removing unnecessary exposure is often more effective than trying to respond after an attacker has gained a foothold.
Identity security is important because ransomware operators frequently abuse legitimate accounts. Multi-factor authentication, separate administrator accounts, strong password policies and carefully limited privileges make it harder for a stolen account to be used for widespread damage. Privileged activity should be restricted to approved tasks and reviewed regularly. Service accounts also need attention, particularly where they have access to servers, shared storage or business applications.
Network design can limit the spread of an infection. Segmentation separates systems according to their purpose and sensitivity, so a compromised workstation does not automatically provide a route to every server or operational device. Administrative interfaces, backups, production systems and user networks can be separated where the business’s infrastructure allows it. Restrictions on remote administration and lateral connections further reduce the number of systems an attacker can control from a single endpoint.
Endpoint protection looks for behaviour associated with ransomware rather than relying only on known malware signatures. Relevant warning signs include rapid changes to large numbers of files, attempts to disable security tools, unusual use of command-line utilities, unexpected privilege escalation and suspicious access to shared folders. Security professionals can investigate these signals, isolate affected devices and determine whether the activity is accidental, malicious or part of a wider compromise.
Recovery arrangements should be tested, not simply documented. A business needs to know which systems must be restored first, who can authorise restoration and how clean versions of data and applications will be verified. Restoration exercises can expose issues such as missing credentials, incompatible software, incomplete data or dependencies on systems that were not included in the recovery plan. Copies that are protected from unauthorised alteration are particularly valuable, but they still need to be checked for usability and integrity.
Staff procedures form another layer of ransomware protection. Employees should know how to report a suspicious attachment, unexpected login request or unusual file behaviour without attempting to investigate it themselves. Training should cover the specific ways the organisation uses email, cloud applications and shared documents. Clear reporting routes help security teams assess a potential compromise while evidence is still available.
Cyber security services also support decision-making during an incident. An effective plan assigns responsibilities for technical containment, management decisions, legal or regulatory considerations, supplier communication and communication with affected staff or customers. It should explain how to preserve logs and other evidence, when to involve specialist investigators, and how to distinguish a local device problem from a broader compromise. Exercises using realistic scenarios help test whether these responsibilities are understood.
For a small or medium-sized organisation, managed cyber security support can bring these activities together through structured risk reviews, technical configuration, security advice and ongoing management. S2 Technology Group supports businesses around Stourbridge, Kinver, Wordsley, Kingswinford, Kidderminster, Halesowen, Dudley and neighbouring areas with cyber security and managed IT services designed around their systems and operational requirements.
Secure recovery reduces the pressure to negotiate with ransomware attackers. A ransom payment does not guarantee that encrypted files will be restored, prevent stolen information from being misused, or remove the attacker’s access. Cyber security services therefore help businesses maintain independent recovery options by protecting backup copies from the same accounts, devices and network paths that ransomware could compromise.
Those recovery copies should be separated from everyday systems and governed by restricted access. Restoration should begin with verified data and carefully controlled systems, rather than reconnecting potentially compromised devices immediately. This approach helps the business make decisions based on the condition of its environment and the availability of clean recovery points, rather than relying on an attacker’s claims.