
How does backup software manage retention policies?
Backup software manages retention policies by applying rules that determine how long backup copies and recovery points are kept before they are automatically deleted or replaced. Policies can be configured around factors such as backup frequency, required recovery history, available storage and regulatory or contractual data-retention obligations.
Backup retention policies are the rules a backup system uses to select, preserve, consolidate and expire recovery points. Rather than treating every backup copy identically, the software evaluates each recovery point against the relevant workload, schedule, storage location and retention class. It then keeps copies that remain within policy and removes or replaces those that have reached the end of their defined lifecycle.
A policy normally contains several layers of retention rather than one simple deletion date. Recent recovery points may be kept for frequent operational restores, while selected points are retained for longer-term recovery. For example, a business might retain recent copies for restoring accidentally deleted files, periodic copies for recovering from issues discovered later, and less frequent copies for historical or compliance purposes. The exact structure depends on the organisation’s recovery requirements and the type of data being protected.
Common retention models include:
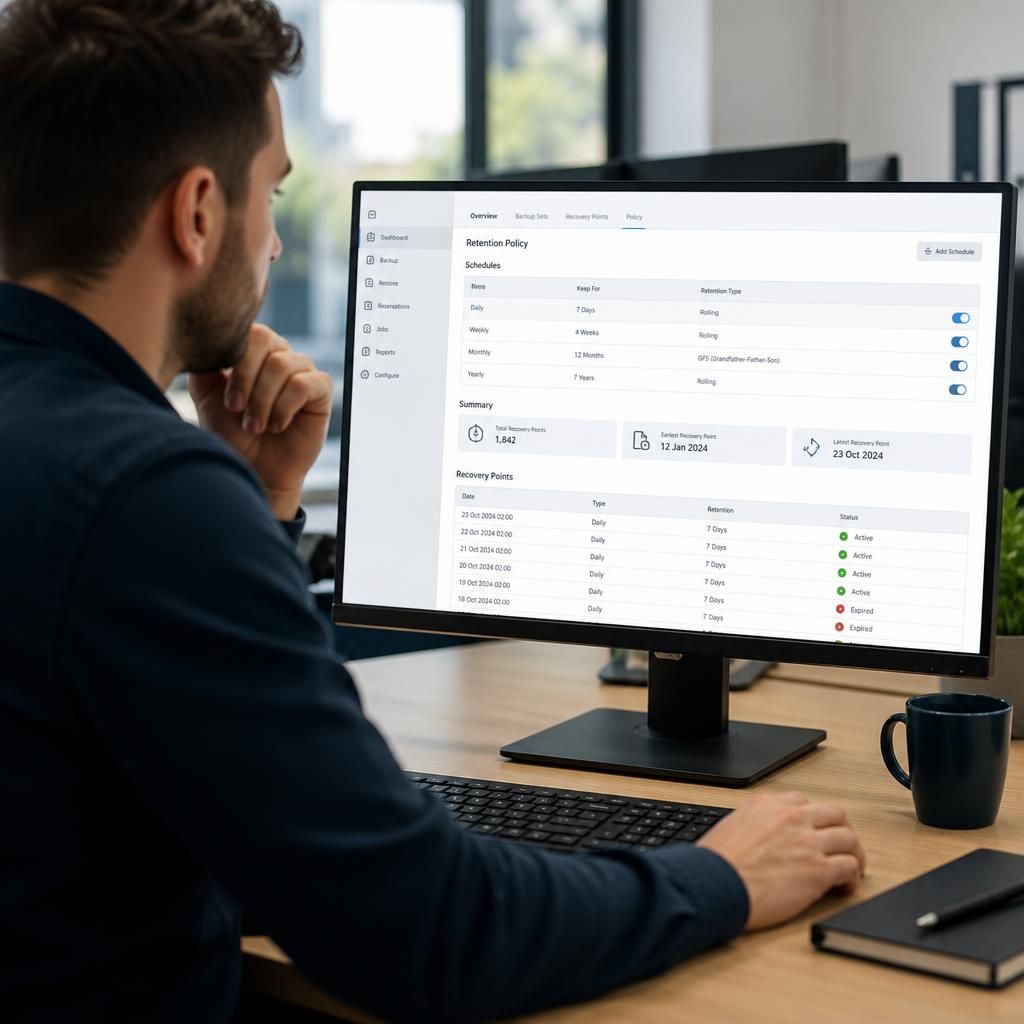
- Rolling retention: the system keeps recovery points for a defined period and removes them as they fall outside the retention window.
- Grandfather-father-son retention: selected daily, weekly and monthly copies are promoted into longer-lived groups. This preserves historical points without keeping every individual backup indefinitely.
- Version-based retention: the software retains a defined number of versions rather than using only elapsed time. This can be useful where files change frequently.
- Event-based retention: a recovery point is retained because it is associated with an event, such as a system upgrade, investigation or migration.
- Indefinite or legal-hold retention: deletion is suspended for specifically identified data until an authorised person releases the hold.
Backup software must also understand the relationship between recovery points. Some backups are full copies, while others contain only changes since an earlier backup. In a dependent backup chain, deleting one copy may make later points unusable. Retention processing therefore often involves consolidation: the software may merge dependent data into another recovery point before removing the original. This allows an old point to expire without breaking the ability to restore from newer points.
Where backups are stored in deduplicated or compressed form, the visible recovery-point count may not correspond directly to the amount of physical storage consumed. Several recovery points may share common blocks. When one point expires, the software can delete only data blocks that are no longer referenced by any retained point. This reference-aware process helps prevent premature deletion while reclaiming storage safely.
Retention is usually applied separately to different workloads or data sets. A file server, virtual machine, database, cloud service and endpoint may each have different recovery requirements. A policy can therefore assign different schedules and retention classes according to the importance, change rate and technical characteristics of the workload. Application-consistent backups may also need to be retained as complete recovery sets rather than as unrelated files, particularly where databases or transactional applications are involved.
Retention should be distinguished from backup frequency and recovery objectives. Backup frequency determines how often new recovery points are created. The recovery point objective describes how much recent data the organisation can afford to lose, while the recovery time objective concerns how quickly a service needs to be restored. Retention determines how far back usable recovery points remain available. These settings interact, but changing one does not automatically satisfy the others.
Many platforms apply retention independently at each storage tier. A local repository might hold recent points for rapid restoration, while a secondary location or cloud repository preserves selected copies for longer. If copies are replicated, the policy needs to define whether the destination follows the source policy or has its own lifecycle. Otherwise, an expired source copy might remain unexpectedly in another location, or a destination could delete data that is still required for recovery.
Deletion rules also need to account for exceptions. A recovery point may be marked as protected from automatic expiry because it is needed for an audit, a legal matter, an investigation or a planned change. Administrative permissions should control who can create, extend and release these holds. A hold that has no review process can cause storage to grow indefinitely, while a hold that is applied too narrowly may not cover all related data.
Good retention design includes safeguards around expiry. Administrators should be able to see which recovery points are due for deletion, what storage will be released, and whether any dependent recovery chains or replication jobs are affected. Some systems provide warnings, approval steps or a grace period before permanent deletion. These controls are particularly important for immutable or isolated copies, where retention may be enforced by the storage platform and cannot simply be shortened by a backup administrator.
Immutability changes how expiry works. An immutable copy cannot be altered or deleted before its enforced retention period ends, including by an administrator or ransomware affecting the backup environment. The backup application may mark the copy as expired, but the underlying storage will remove it only when the immutability period has elapsed. The effective retention period is therefore the longer of the backup policy and the storage-enforced protection period.
Retention policies should be reviewed when the organisation changes its systems, contracts or regulatory obligations. A policy designed for a small file set may become unsuitable after a database is introduced, a branch office is added or data is moved to a new platform. Review should cover:
- which workloads and data sources are included;
- which recovery points are available for recent and historical restoration;
- whether retention is applied consistently across local, off-site and cloud copies;
- how legal holds and approved exceptions are managed;
- what happens when a policy is changed or a protected workload is removed;
- whether available storage can support the resulting retention pattern; and
- whether restores have been tested from points across the full retention range.
Changing a policy does not always affect existing recovery points immediately. Depending on the platform, the new rule may apply only during the next retention run, may re-evaluate existing points, or may leave manually locked copies untouched. Administrators should confirm the platform’s behaviour before reducing retention, particularly where backups are subject to immutability, replication or legal holds.
A retention policy is effective only when it preserves recovery points that can actually be restored. Monitoring should therefore report policy violations, failed expiry jobs, unexpected storage growth, missing retention tiers, replication mismatches and recovery points approaching expiry. Periodic test restores provide additional assurance that older copies remain readable and that the required application data, permissions and dependencies are present.
For a small or medium-sized organisation, the practical objective is a documented retention design that matches business risk without keeping every copy permanently. S2 Technology Group can help businesses assess backup configuration, storage arrangements and recovery requirements so that retention rules are understandable, controlled and aligned with the systems they need to recover.
Backup retention is not the same as long-term archiving. A backup retention policy keeps recovery points available for restoring systems and data, while an archive is intended to preserve information for reference, records management or historical access. Treating backups as an archive can result in unsuitable storage costs, limited search capabilities and unclear ownership of information that must be retained.
When designing retention rules, classify data according to its purpose. Operational backups may be kept for restoring recent changes or recovering from system faults, whereas records subject to contractual, regulatory or internal requirements may need a separate archive process with defined access controls, indexing and disposal approval. This distinction helps ensure that backup software expires recovery points as intended without being used as the organisation’s only method of preserving important records.