Does Microsoft 365 security training cover security defaults administration?
Yes. Microsoft 365 security training should cover security defaults administration, including how to review, enable or disable the setting and understand its effect on baseline protections such as multi-factor authentication requirements.
Effective administration of Microsoft 365 security defaults requires more than switching a tenant-wide option on or off. Training should explain where the setting is managed, what protections it activates, which users and applications it affects, and how to assess its suitability before making a change.
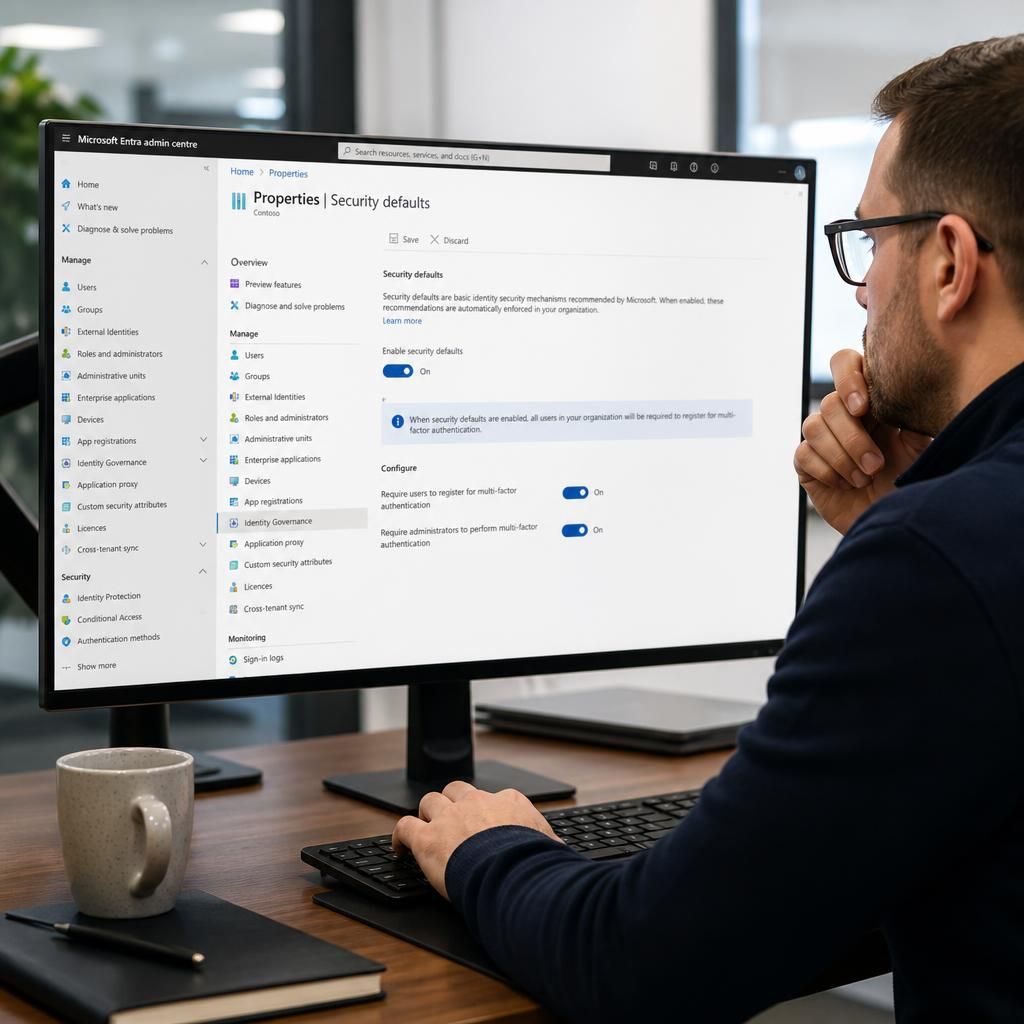
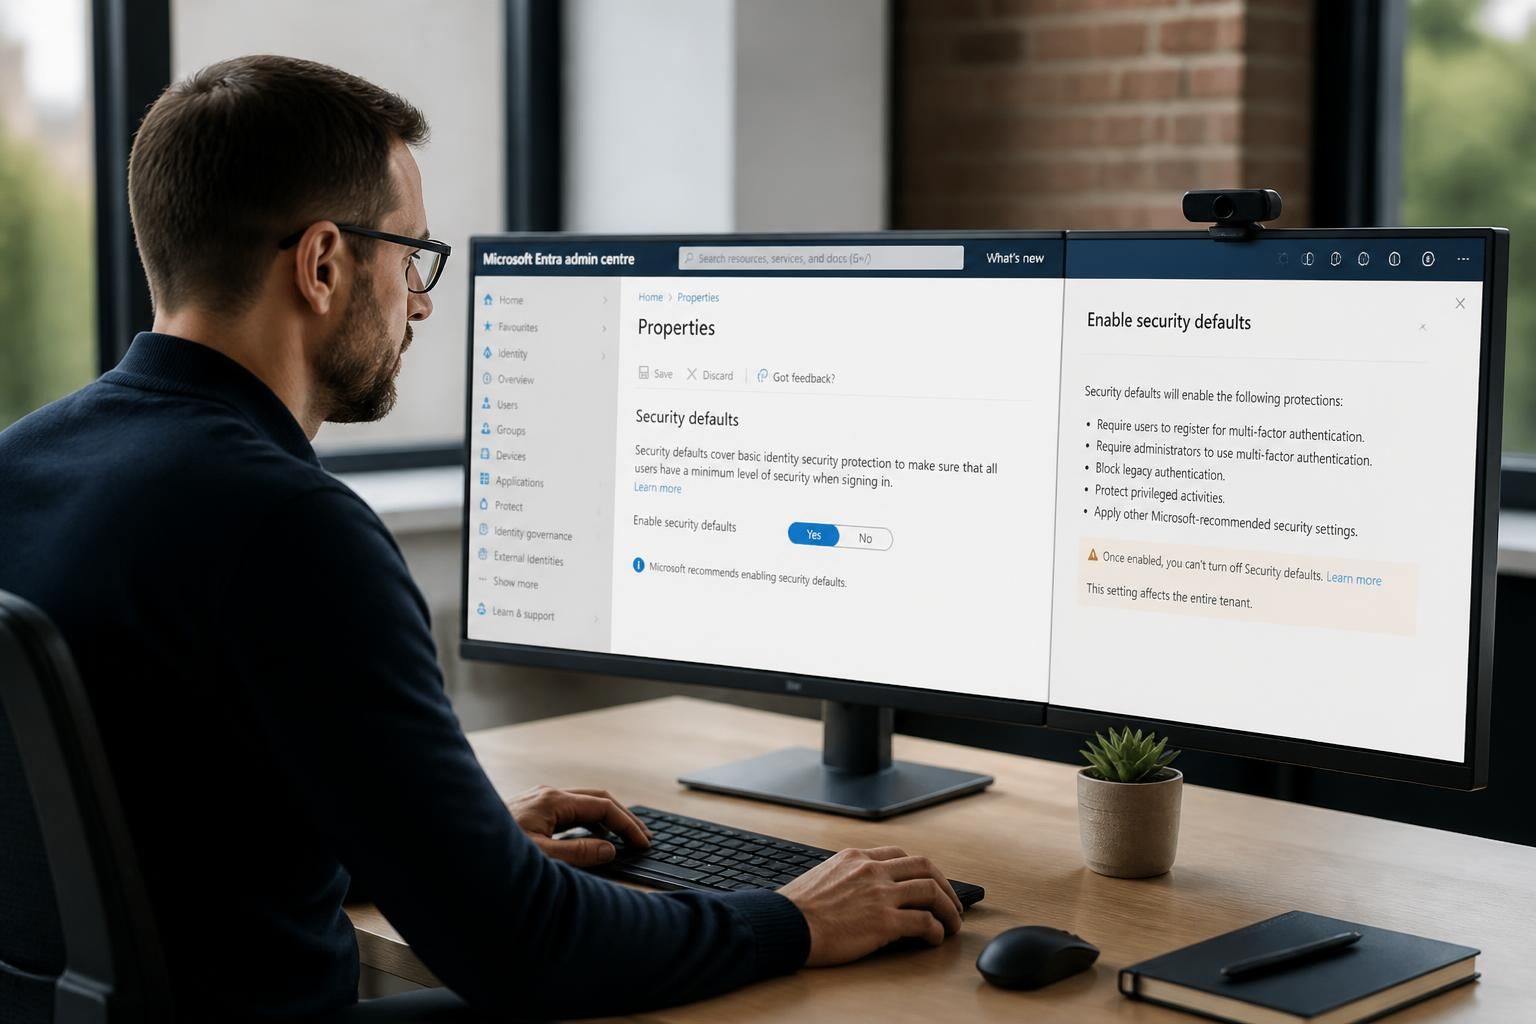
Understanding the control: Security defaults provide a Microsoft-managed baseline for tenants that do not require a more customised identity protection model. Administration training should show learners how to locate the setting in the Microsoft Entra admin centre, check its current state and confirm the scope of the change. It should also explain that the setting applies at tenant level rather than being a collection of isolated user preferences.
A practical course should cover the main protections associated with security defaults, including:
- Prompting users to register for multi-factor authentication.
- Requiring administrators to use stronger authentication protections.
- Protecting privileged activities with additional authentication requirements.
- Reducing the risk presented by legacy authentication protocols that cannot support modern controls.
- Applying baseline safeguards against common identity-based attacks.
The exact user experience can depend on account type, existing configuration and the authentication methods available in the tenant. Training should therefore cover how to prepare users, identify administrators who may be affected first and deal with registration or sign-in issues without weakening the control unnecessarily.
Enablement and assessment: Administrators should learn to review the tenant’s current authentication arrangements before enabling security defaults. This includes checking whether users can complete multi-factor authentication registration, whether service accounts or older applications rely on legacy authentication, and whether any operational process could be interrupted. A controlled change plan should record the reason for enablement, the administrator responsible, the expected user impact and the checks that will be performed afterwards.
Training should also distinguish between security defaults and Conditional Access. Security defaults are intended to provide a simpler baseline, whereas Conditional Access allows more granular decisions based on factors such as user, group, application, device, location and risk. An organisation moving to a customised Conditional Access design must understand that disabling security defaults removes that baseline and creates a responsibility to reproduce the required protections through properly tested policies. The two approaches should not be treated as interchangeable without reviewing the resulting control coverage.
Disabling the setting: Administration training should present disabling security defaults as a controlled security decision, not a routine troubleshooting step. Learners should be taught to document the reason, obtain appropriate approval and verify that equivalent or stronger protections are already configured. They should consider multi-factor authentication coverage, privileged account protection, legacy authentication blocking and exclusions before making the change.
Where a tenant is being migrated to Conditional Access or another identity security design, the course should include a comparison of the protections before and after the transition. This can reveal gaps caused by unprotected user groups, overly broad exclusions, policies that are left in report-only mode or authentication requirements that do not apply to every relevant application.
Verification and ongoing administration: Security defaults training should include post-change validation. Administrators can review sign-in activity, authentication registration status, audit records and user reports to confirm that the intended controls are taking effect. They should investigate unusual failures, repeated registration problems and unexpected access patterns rather than assuming that an enabled setting is functioning correctly in every scenario.
The setting should also form part of documented tenant administration. Useful records include its current state, the date and reason for the last change, related identity policies, known application dependencies and the process for reviewing the configuration after significant tenant changes. This helps administrators distinguish an intentional security decision from an undocumented exception.
Finally, training should use practical exercises rather than relying only on feature descriptions. Suitable exercises include reviewing a tenant with security defaults enabled, planning user registration, assessing an application that depends on legacy authentication, comparing security defaults with a Conditional Access design and writing a change record for a proposed transition. These tasks test whether an administrator can make a safe, evidence-based decision and verify the result after implementation.
Security defaults administration training should explain who is authorised to change the setting and how that authority is controlled. Learners should understand the difference between being able to view the configuration and being permitted to modify tenant-wide identity protection, with access limited to appropriate privileged administrators.
Practical guidance should cover least-privilege assignment, approval for administrative access and removal of permissions when they are no longer required. It should also address how to handle delegated administration and emergency accounts without creating permanent, unreviewed access. This ensures that managing security defaults is treated as a governed administrative responsibility rather than a setting available to every user with access to the tenant.