
When should an IT service desk ticket be escalated?
An IT service desk ticket should be escalated when its impact, urgency or technical complexity exceeds the current support level, or when progress has stalled. Escalation should move the ticket to a specialist or decision-maker with the information needed to investigate and resolve it.
In service desk practice, escalation is a documented change in ownership, authority or investigative approach. It should happen when the current resolver cannot safely, efficiently or appropriately take the ticket further, rather than simply when a user asks for a more senior technician.
Escalate when the ticket presents a material business risk. Examples include:
- A large number of users, a critical business process or a key site is affected.
- The issue prevents work from continuing, threatens a customer commitment or disrupts a time-sensitive operational activity.
- There is a suspected security incident, unauthorised access, malware infection, data exposure or loss of control over an account.
- The ticket involves data loss, service deterioration that is spreading, or a risk of permanent damage.
- The requested action requires privileged access, a significant configuration change or approval that the current support level does not hold.
A ticket can also require escalation even where its immediate impact appears limited. Repeated recurrence, multiple related tickets, an unresolved root cause or an unusual pattern may indicate a wider infrastructure or security problem. Treating each report separately can conceal the underlying issue and allow it to develop.
Escalate when investigation has reached a genuine technical boundary. This may occur when the assigned technician has completed the relevant checks but needs specialist knowledge of networking, cloud administration, identity management, applications, security or infrastructure. It may also be appropriate when the available tools cannot provide sufficient evidence, when a change must be designed by an authorised administrator, or when a third-party provider needs to investigate part of the service.
Technical difficulty alone is not a reason to pass a ticket on without preparation. Before escalation, the first-line resolver should record what the user experienced, when it started, who or what is affected, the symptoms observed, relevant error messages, troubleshooting already completed and the results of those checks. Screenshots, logs, device or account details and recent changes should be included where they are relevant and can be shared securely.
Escalate when progress has become unproductive. Warning signs include:
- The same troubleshooting steps are being repeated without producing new evidence.
- The ticket has moved between technicians without a clear decision or owner.
- Information is missing and the current resolver cannot obtain it without another team’s access or authority.
- A promised update or agreed service-level checkpoint is approaching without a credible plan.
- The user has supplied further evidence that changes the likely cause or increases the risk.
- The proposed fix could create wider disruption if carried out without specialist review.
Escalation should be based on defined decision rules rather than personal judgement alone. A service desk can use categories such as business impact, security risk, affected scope, technical complexity, elapsed investigation time and the authority required to make the next change. These rules should be available to all support staff, with examples that show the difference between a ticket that can remain at its current level and one that must move.
Use the appropriate form of escalation. A functional escalation transfers the work to a team with different technical expertise, such as network, cloud or security support. A hierarchical escalation involves a service manager or decision-maker when priorities conflict, risk needs acceptance or additional resources are required. A supplier escalation passes the relevant technical evidence to an external provider responsible for a platform, circuit or application. One ticket may need more than one of these, but the record should make clear who owns the next action.
Security-related tickets need particular care. If there is evidence of compromised credentials, suspicious access, malicious software or possible data exposure, preserve relevant evidence, restrict unnecessary access to sensitive information and follow the organisation’s incident process. Do not treat a suspected security event as an ordinary fault simply because only one user has reported it. The correct escalation route may include security leadership, senior management or legal and regulatory advisers, depending on the organisation’s procedures.
An effective handover contains more than a statement that the issue is difficult. It should include:
- A concise description of the business effect and the affected users, services or locations.
- The time the problem began, whether it is continuous or intermittent, and any known pattern.
- The actions taken, the result of each action and the evidence that supports or rules out possible causes.
- Relevant changes, alerts, dependencies or related tickets.
- The specific decision, investigation or authorisation needed from the receiving team.
- The current user communication position and any agreed next checkpoint.
- Any safety, privacy or access restrictions that apply to the investigation.
The ticket should retain a single accountable owner even after technical work moves elsewhere. That owner coordinates communication, checks that the receiving team has accepted the handover and prevents the user from having to repeat the same information. If responsibility is transferred permanently, the record should state who accepted it and why.
Escalation is not the same as increasing priority. Priority describes how the organisation should sequence work; escalation describes a change in capability, authority or management attention. A low-impact ticket may need functional escalation because it requires specialist knowledge, while a high-impact outage may remain with the original team if that team has the right expertise and authority to resolve it. The two decisions should therefore be recorded separately.
Once the cause is understood and the risk is controlled, the ticket should be reviewed to decide whether it can return to the original support level. De-escalation is appropriate when the specialist input is complete, the required change has been approved and the remaining work follows a known procedure. The record should capture the resolution, any preventative action and whether a knowledge article, monitoring rule, problem record or service improvement is needed.
Regular review of escalated tickets helps identify weaknesses in the service desk itself. Patterns may show that staff need better documentation, that access permissions are poorly designed, that a recurring fault should be managed as a problem, or that escalation criteria are unclear. The objective is not to minimise the number of escalations at all costs; it is to ensure that each ticket reaches the right level of expertise and authority without avoidable delay, duplication or loss of accountability.
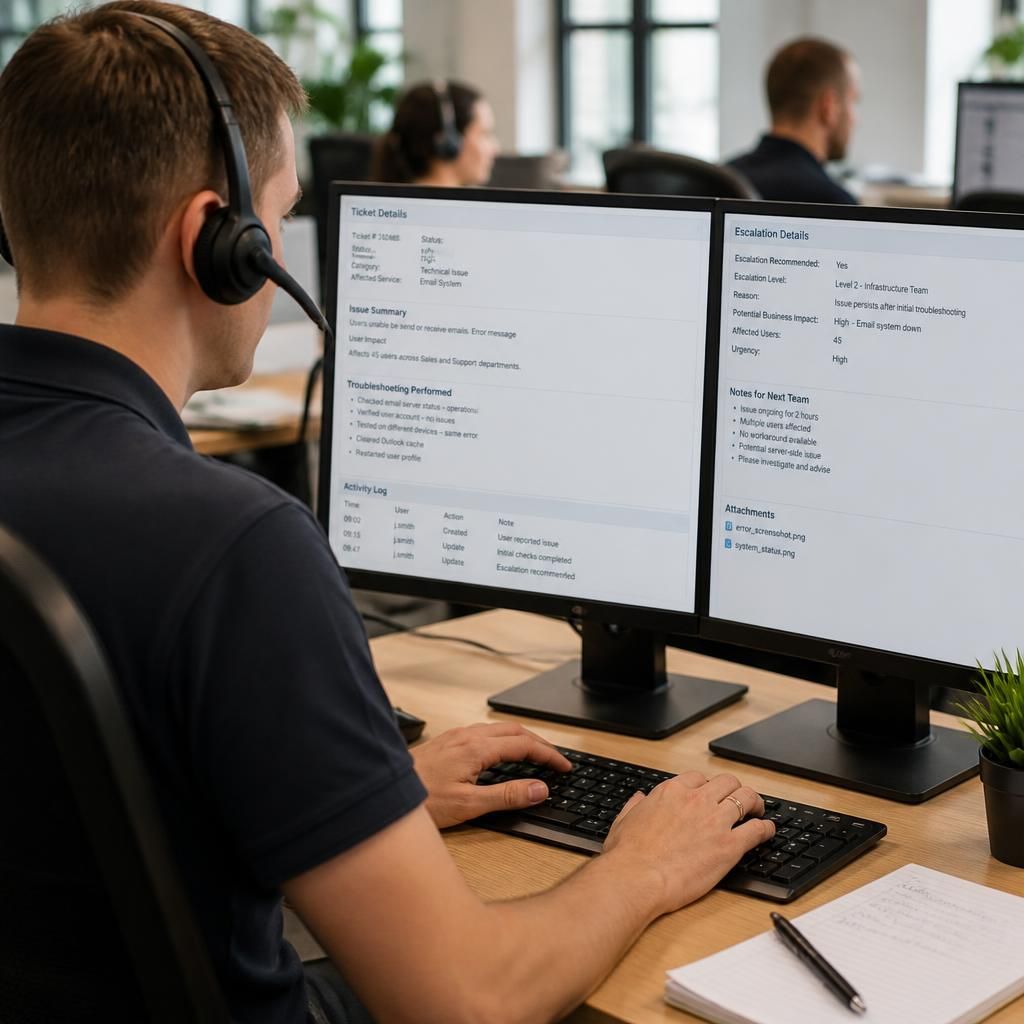
Escalation does not need to wait until the root cause is confirmed. If the potential consequences are significant but the available evidence is incomplete, the ticket should be raised to the appropriate technical or security authority while investigation continues.
This is particularly important where delaying a decision could increase exposure or restrict future options. The receiving team can then determine whether to contain the issue, collect further evidence, approve a controlled change or involve another party. The ticket should distinguish confirmed facts from working theories, so escalation supports sound decisions rather than presenting an unverified diagnosis as fact.
- Record what is known and what remains uncertain.
- Explain the consequence of taking no action while investigation continues.
- Identify any immediate safeguards already applied.
- State the decision or specialist assessment required next.