
What is the difference between a cyber risk assessment and a penetration test?
A cyber risk assessment identifies and evaluates threats, vulnerabilities and potential business impacts across an organisation, while a penetration test actively simulates attacks against defined systems to find exploitable weaknesses. An assessment provides a broader risk picture; a penetration test provides technical evidence about whether particular security controls can withstand attack.
A cyber risk assessment and a penetration test serve different purposes. A cyber risk assessment examines how an organisation could be harmed by information security threats and how well its existing safeguards manage that risk. A penetration test is a controlled technical exercise in which authorised testers attempt to exploit weaknesses in specified systems, applications or networks. One supports risk-based decision-making across the business; the other produces evidence about the security of the systems included in the test.
The main difference is breadth and method. A risk assessment considers the organisation as a whole. It can examine information assets, business processes, users, suppliers, locations, access arrangements, policies, technical controls and recovery arrangements. It considers threats such as unauthorised access, malware, data loss, fraud and service disruption, then evaluates the likelihood and potential business impact of those events.
A penetration test has a narrower, predefined scope. Testers use agreed techniques to imitate the actions of an attacker, usually against internet-facing infrastructure, internal networks, web applications, wireless networks or specific systems. Depending on the agreed rules, the test may involve attempting to obtain access, move between systems, escalate privileges or access sensitive data. Testing must be authorised and controlled so that it does not create unnecessary disruption or alter evidence.
What a cyber risk assessment reveals
- Which information and technology assets are most important to the organisation.
- Which threats are relevant to those assets and business processes.
- Where weaknesses exist in technology, procedures, governance or user practices.
- How existing controls reduce risk and where gaps remain.
- Which risks should be treated first, based on their possible business effect.
- What further controls, decisions or investigations may be appropriate.
The evidence for an assessment can include interviews, document reviews, asset information, configuration details, incident records, supplier information and technical findings. It does not necessarily involve trying to break into a system. Its purpose is to establish whether the organisation understands its risks and is managing them at a level consistent with its business responsibilities.
What a penetration test reveals
- Whether a tester can exploit a vulnerability within the agreed scope.
- How an attacker might combine several weaknesses to reach a more sensitive target.
- Whether security monitoring or protective controls detect particular attack activity.
- What information or access could be obtained if an exploit succeeded.
- Which technical weaknesses should be remediated and retested.
A penetration test report normally records the systems tested, the approach used, findings, supporting evidence, technical severity and recommended remediation. It may also describe the potential consequences of a successful attack. However, a clean test result does not prove that an organisation is free from cyber risk. It only provides assurance about the systems, conditions and attack paths covered by that particular engagement.
Neither activity replaces the other. A risk assessment can identify an important risk that is not suitable for penetration testing, such as inadequate joiner, mover and leaver procedures, weak supplier oversight or an untested recovery process. Conversely, a penetration test can expose a serious technical weakness that a high-level assessment would not identify without detailed testing. The two activities answer different questions and produce different types of evidence.
There are also limitations to consider. A risk assessment depends on the accuracy and completeness of the information provided, so undisclosed assets or misunderstood processes can affect its conclusions. A penetration test is limited by its scope, test window, available access and agreed rules of engagement. It may not assess social engineering, physical security, third-party systems or denial-of-service techniques unless these are specifically included. Testing can also identify a vulnerability without proving every possible business consequence.
Which should a business choose? A business that lacks a current understanding of its key assets, threats and control gaps will usually benefit from beginning with a cyber risk assessment. This creates a basis for deciding which systems and attack scenarios warrant deeper technical testing. A penetration test may be more appropriate when there is a clearly defined system to validate, such as a new application, externally accessible service, major infrastructure change or security control that needs independent testing.
For many organisations, the most useful approach is sequential. The assessment establishes priorities and defines the risks that matter most. A penetration test then examines selected technical controls or attack paths in greater depth. Its findings can be fed back into the risk register, remediation plan and wider security decisions. After weaknesses are addressed, a focused retest can help determine whether the specific findings have been resolved, while the broader risk assessment remains necessary to consider changes elsewhere in the organisation.
In practical terms, a cyber risk assessment answers, “What could go wrong, how would it affect the business, and how should the risk be managed?” A penetration test answers, “Can an authorised tester exploit this defined technical weakness or attack path?” Understanding that distinction helps a business commission the right activity rather than treating a technical test as a complete assessment of its cyber risk.
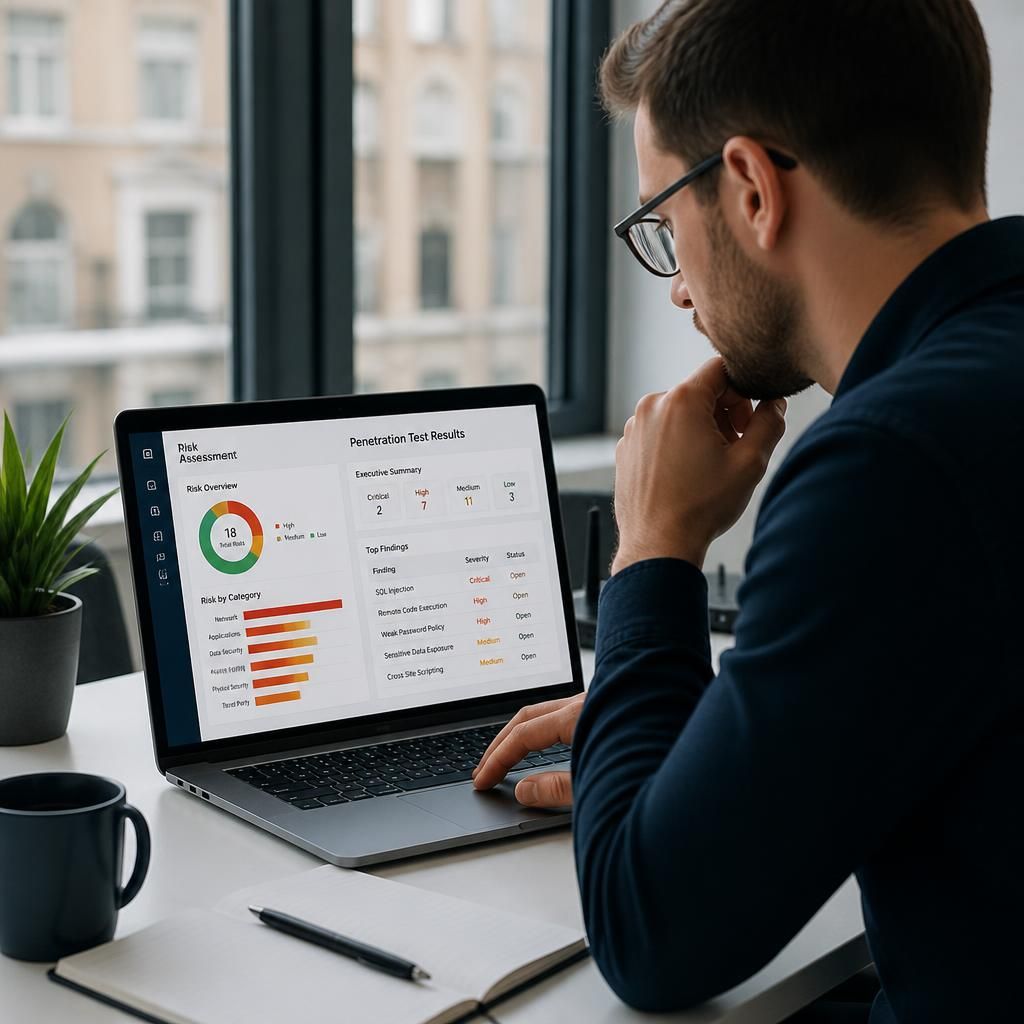
A further distinction is how the findings are interpreted. A penetration test typically describes technical severity: for example, how easily a weakness can be exploited, what access it provides and whether it can be combined with other vulnerabilities. A cyber risk assessment places those findings in business context by considering the importance of the affected asset, the information involved, existing safeguards and the consequences of disruption.
This means the most technically severe finding is not automatically the organisation’s highest business risk. A vulnerability on an isolated test system may require different treatment from a less complex weakness affecting a critical operational service or sensitive information. The assessment helps decision-makers compare technical findings with risks arising from governance, suppliers, processes and recovery arrangements, so remediation priorities reflect the organisation’s actual exposure.
When reviewing a penetration test report, the findings should therefore be mapped to the relevant assets and risks rather than considered in isolation. This provides a clearer basis for deciding whether to remediate, apply a compensating control, accept the residual risk or investigate the issue further.