How does Microsoft 365 security training cover Conditional Access policies?
Microsoft 365 security training covers Conditional Access policies by explaining how conditions such as user, location, device and application risk can trigger access controls. It also develops practical skills for designing, testing, monitoring and troubleshooting policies while reducing the risk of accidental lockouts or excessive access restrictions.
Microsoft 365 security training covers Conditional Access by teaching administrators how policies are evaluated, how controls interact, and how to introduce changes without disrupting legitimate business activity. The emphasis is on translating security requirements into manageable access rules, documenting decisions and validating the result through controlled administration.
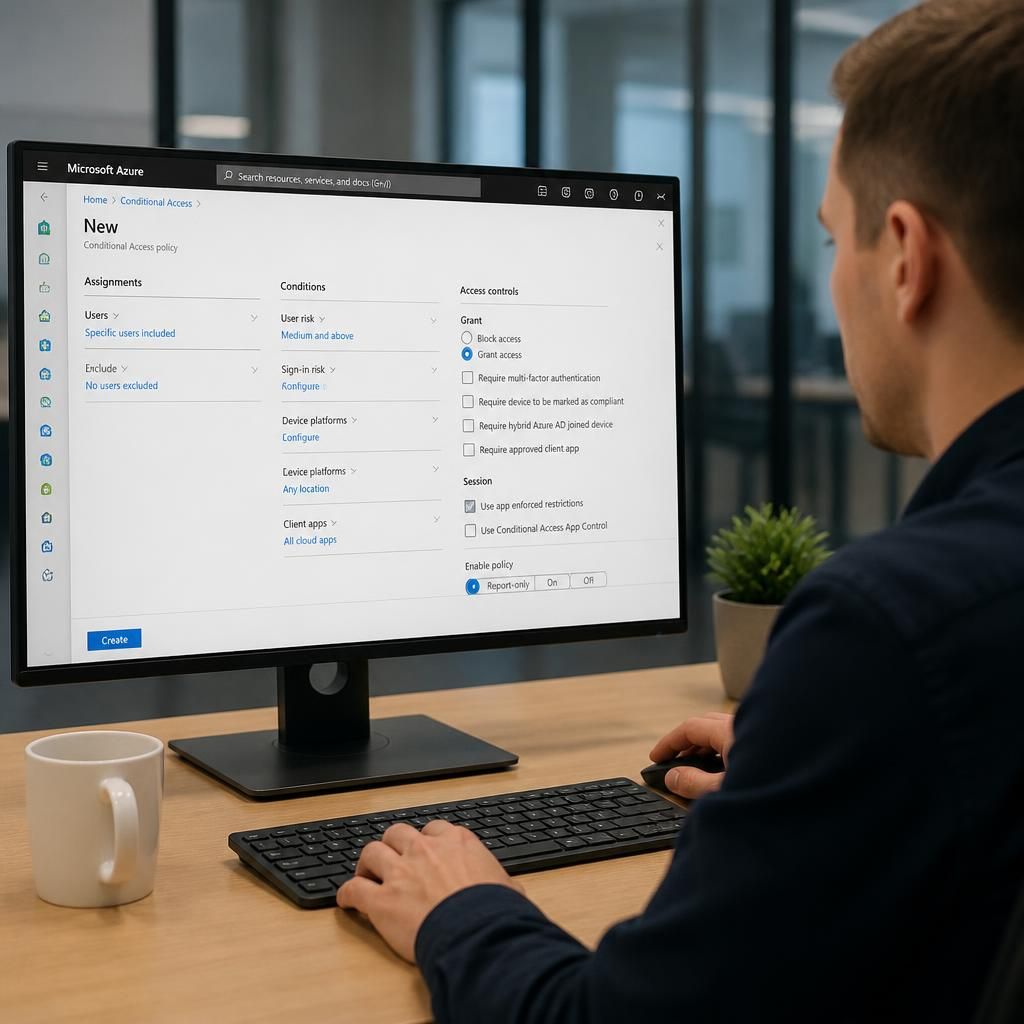
Training should begin with the structure of a Conditional Access policy. Administrators learn to distinguish the policy scope from the access decision, then configure requirements such as requiring stronger authentication, blocking access or applying additional restrictions. This distinction is important because a policy can be technically valid while still producing an unintended result if its assignments or controls are too broad.
A thorough course also explains how multiple policies apply at the same time. Administrators need to understand that a user may be affected by several policies and that the resulting access requirement reflects their combined effect. Training therefore covers how to review overlapping rules, identify conflicting objectives and avoid creating separate policies that are difficult to interpret or maintain.
- Scope: which identities, groups, applications or sessions are included.
- Exclusions: which accounts or services must be left out for a defined operational reason.
- Conditions: the signals that determine when the policy applies.
- Access controls: the action required when the conditions are met.
- Policy state: whether the rule is disabled, monitored or enforced.
Good training gives particular attention to exclusions and emergency administration. Exclusions should be limited, documented and reviewed rather than used as a convenient way to bypass a control. Administrators also learn why emergency access arrangements must be planned before stricter policies are enabled, with their use monitored and their credentials protected separately from ordinary user accounts.
Conditional Access training commonly uses a staged deployment process. A new rule can first be reviewed in a non-enforcing mode to assess which sign-ins would be affected. Administrators then examine the resulting reports, refine the scope where necessary and move to enforcement only after the expected impact is understood. This provides a practical method for detecting unintended dependencies, legacy authentication and service accounts that may need attention.
Another important topic is policy design for different types of access. A rule appropriate for interactive access to a business application may not be suitable for automation, synchronisation or administrative activity. Training helps administrators assess the purpose of each connection, identify unsupported authentication methods and select controls that fit the access pattern instead of applying one broad rule to every scenario.
Courses should also cover the relationship between Conditional Access and wider identity governance. Policy changes need an owner, a stated purpose, a review date and a record of the expected effect. Administrators can then explain why a rule exists, determine whether it is still appropriate when business processes change and remove obsolete exceptions without weakening the overall control framework.
Practical exercises may include analysing a sign-in that has been denied, tracing the policies that applied and checking which requirement was not satisfied. This develops the ability to separate a policy configuration problem from an account, authentication or application issue. Training can also cover the evidence required for an escalation, such as the affected identity, application, policy result and relevant sign-in details.
Conditional Access administration should be tested against realistic scenarios rather than only reviewed in the configuration portal. Useful exercises include onboarding a new group, changing an access requirement, investigating an unexpected challenge and rolling back a faulty policy. The administrator should be able to explain the intended security benefit, the users affected and the checks used to confirm that the change worked as designed.
In this way, Microsoft 365 security training treats Conditional Access as an operational discipline rather than a collection of settings. It develops the knowledge needed to create intelligible policies, control exceptions, assess their impact and maintain them as identities, applications and business requirements evolve.
Microsoft 365 security training also distinguishes session controls from controls applied at sign-in. A policy may allow access initially but still govern how long a session remains valid, whether a user must authenticate again, and whether a browser session can persist. Understanding this difference helps administrators avoid treating one successful sign-in as permanent approval.
Training can use scenarios to assess suitable session settings for different access patterns. For example, an administrator may need to balance user convenience for a managed device against stronger reauthentication requirements for sensitive applications or higher-risk sessions. Exercises should examine the effect on existing sessions as well as new sign-ins, since changing a policy does not necessarily produce the same result for every active connection.
Administrators should also learn to document the reason for a session control, the identities and applications it affects, and the evidence used to verify its behaviour. This makes it easier to distinguish a session-expiry event from a failed authentication, an account problem or an application fault when investigating user reports.