How does Microsoft 365 backup support compliance requirements?
Microsoft 365 backup supports compliance requirements by preserving recoverable copies of business data, applying defined retention policies and helping organisations demonstrate controlled access and recovery processes. It contributes to compliance, but does not by itself guarantee that every legal, regulatory or industry-specific obligation has been met.
Microsoft 365 backup supports compliance by providing evidence that data protection, retention and recovery controls have been defined and managed. It forms one part of a wider compliance framework alongside information governance, access management, staff procedures, risk assessments and documented responses to incidents or data requests. The exact value depends on the organisation’s legal, contractual and sector-specific obligations.
For organisations subject to the UK GDPR and the Data Protection Act 2018, backup arrangements can support the availability and resilience of processing systems. If information is accidentally deleted, corrupted or affected by a security incident, a controlled recovery process can help restore access to business records. This should be assessed alongside the organisation’s recovery objectives and its wider technical and organisational measures.
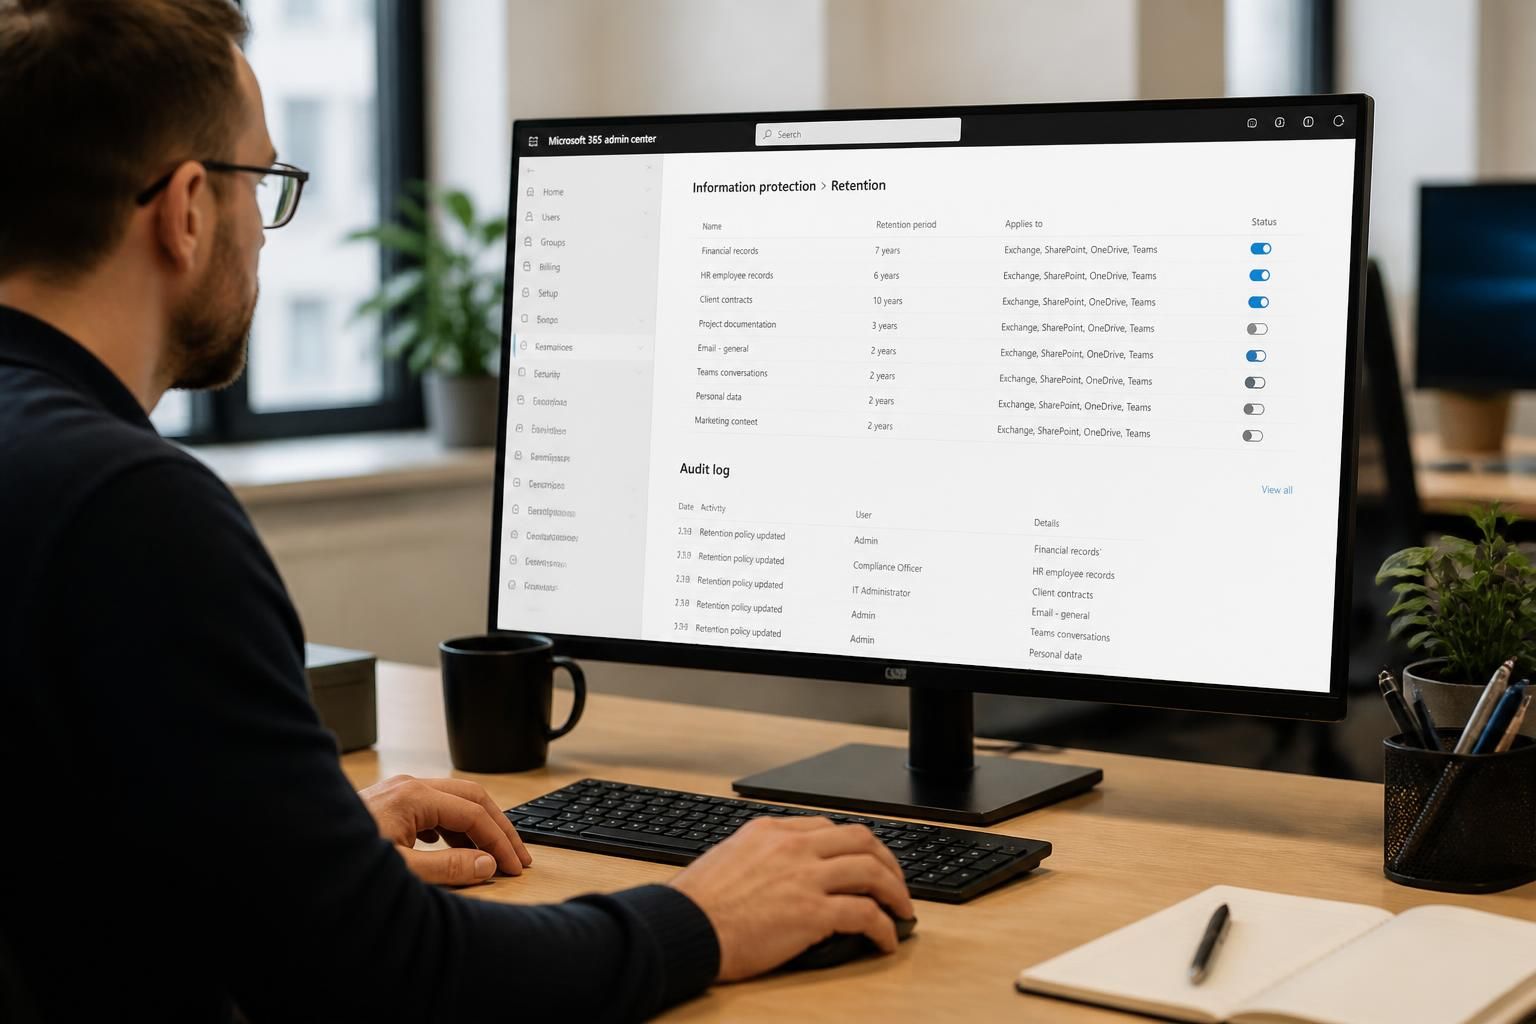
Retention policies are central to compliance. A suitable policy should define:
- which Microsoft 365 workloads and data types are included;
- how long backup copies are kept and why that period is justified;
- when data becomes eligible for deletion;
- who can change retention settings or remove backup data; and
- how exceptions, legal holds and investigations are handled.
Keeping data indefinitely is not automatically compliant. Some organisations need records retained for contractual, regulatory or evidential reasons, while data protection principles may require personal information not to be retained longer than necessary. Backup retention should therefore be documented and aligned with the organisation’s records management schedule rather than selected as a purely technical setting.
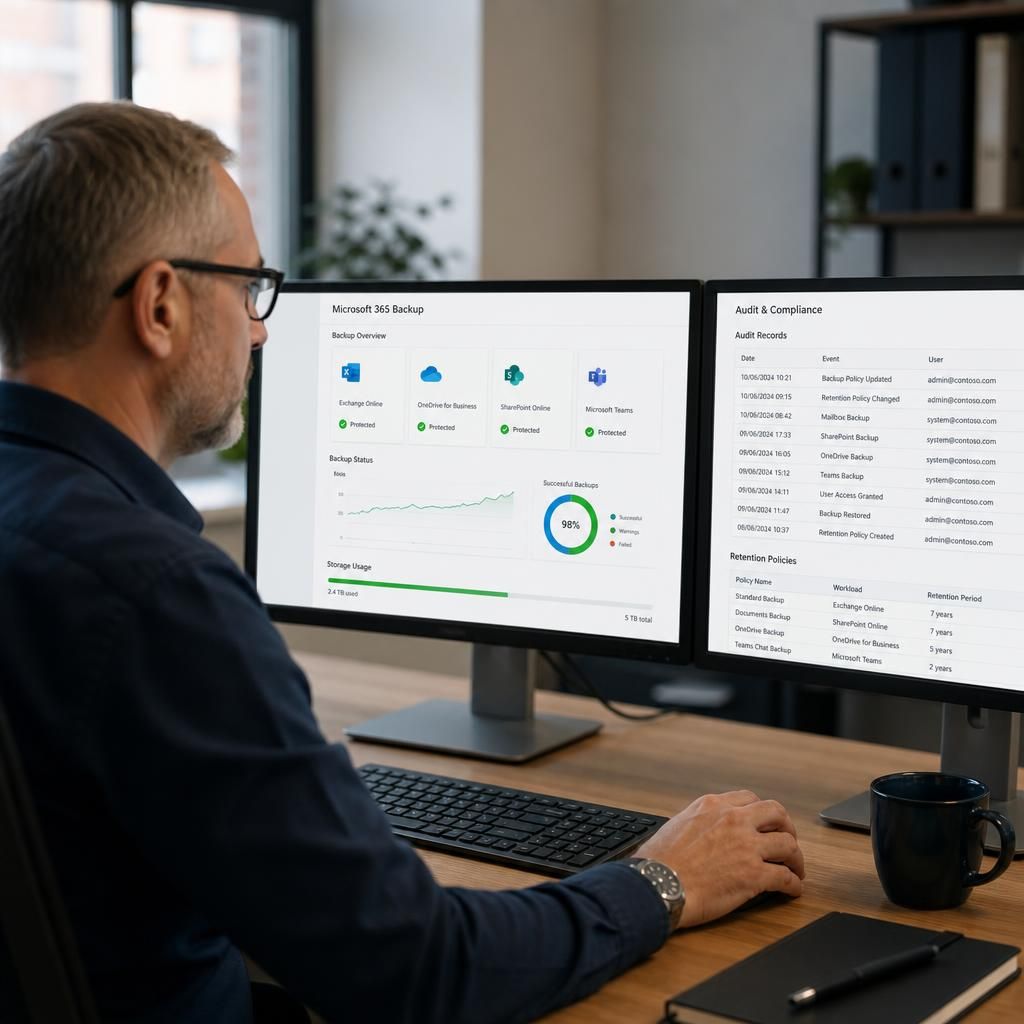
Backup administration can also contribute to accountability. Access should be limited to authorised roles, protected with strong authentication and reviewed periodically. Administrative actions, policy changes, recovery requests and deletions should be recorded where the backup platform supports suitable audit information. These records can help demonstrate that the organisation has applied controlled procedures, although they do not replace a complete compliance audit.
Compliance assessments should examine the full data lifecycle. This includes where backup data is stored, how it is encrypted, who can access it, whether suppliers or subprocessors are involved, and how data is transferred between jurisdictions. Contracts, privacy notices, data-processing arrangements and internal policies may need to reflect the backup service. The organisation should also understand the distinction between Microsoft 365’s native retention features and a separate backup service, because they address different recovery and governance needs.
Backup can support incident management by giving the organisation a defined method for investigating and recovering from deletion, corruption or ransomware. Recovery activity should be authorised, documented and checked to ensure that restored information is complete, appropriate and not reintroducing compromised content. Where a personal data breach occurs, the backup record may assist the investigation, but it does not remove the need to assess notification and reporting obligations.
Organisations should maintain evidence such as backup configuration records, retention schedules, access reviews, recovery logs, test results, supplier due-diligence documents and records of corrective actions. The evidence should show not only that a backup exists, but that its scope, retention, security and recovery procedures have been considered against the organisation’s actual risks.
A practical compliance review therefore asks whether the backup covers the required Microsoft 365 data, whether retention matches documented policy, whether access is appropriately restricted, whether recovery activity is traceable, and whether the arrangement has been reviewed as business and regulatory requirements change. S2 Technology Group can help organisations assess these controls as part of a wider managed IT and cyber security approach, while the organisation remains responsible for determining which obligations apply to its business.
A compliance-focused Microsoft 365 backup arrangement should assign accountability for each protected data set, rather than leaving backup decisions solely to technical administrators. Data owners can confirm which mailboxes, SharePoint content, OneDrive files and Teams-related information support particular business processes, and whether the selected recovery arrangements reflect their importance.
This governance approach helps connect technical settings with documented business requirements. A data owner should approve the relevant protection scope, identify any exclusions, confirm the acceptable recovery position and review changes when a service, process or regulatory obligation changes. Any exception should have a recorded reason, an owner and an agreed review point.
It also creates clearer evidence during an internal review or external assessment. Instead of showing only that a backup job completed, the organisation can demonstrate who decided what required protection and how that decision was evaluated. S2 Technology Group can help structure this review as part of wider IT governance, while the organisation’s appointed owners remain responsible for confirming its compliance needs.