How is IT infrastructure outsourcing priced?
IT infrastructure outsourcing is usually priced according to the scope and complexity of the environment, with costs shaped by factors such as users, devices, servers, cloud services, connectivity, cyber security requirements and the level of support required. Charges may combine a recurring managed-service fee with separate project, migration, licensing or usage-based costs, so an accurate budget depends on assessing the existing infrastructure and agreed service requirements.
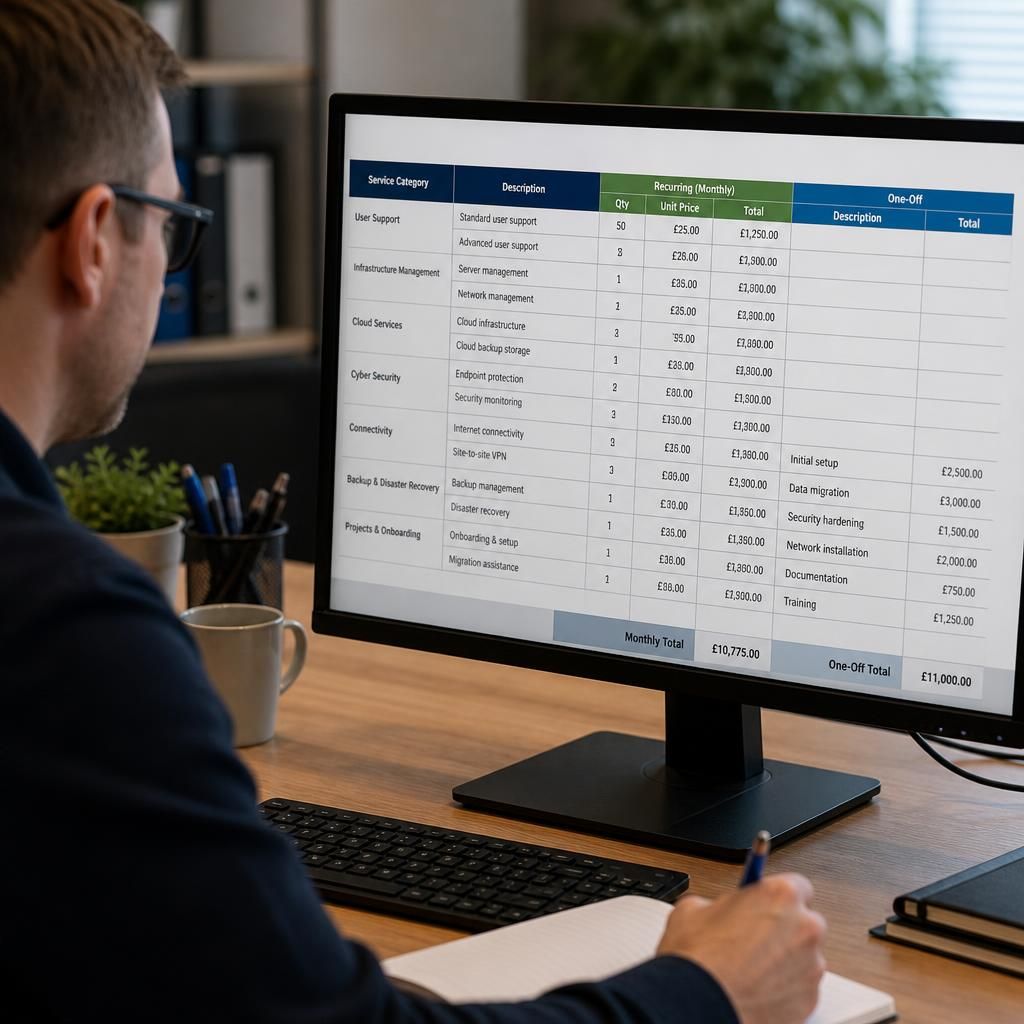
IT infrastructure outsourcing is typically priced through a combination of recurring service charges and one-off implementation costs. The recurring charge covers the agreed management of infrastructure, while separate costs may apply for onboarding, remediation, migrations, hardware, software licences, cloud consumption and other usage-based services. The final price should therefore reflect the infrastructure being managed, the services required and the responsibilities retained by the customer.
Common pricing models
- Per-user pricing: A charge is calculated according to the number of supported users. This can be straightforward where each user receives a broadly similar service, but the agreement should clarify how contractors, temporary workers, shared accounts and leavers are treated.
- Per-device pricing: Charges are based on laptops, desktops, mobile devices, servers, network equipment or other managed assets. This may suit organisations where the number and type of devices are easier to measure than the number of users.
- Fixed monthly pricing: The provider sets a recurring charge for a defined scope of services. This gives the customer a clearer operating budget, provided the contract explains what is included and what counts as additional work.
- Consumption-based pricing: Some services are linked to actual usage, such as cloud computing resources, storage, backup capacity, data transfer or connectivity. These charges can change as business requirements change.
- Hybrid pricing: Many arrangements combine a predictable managed-service fee with variable charges for licences, cloud resources, projects and work outside the agreed scope.
The infrastructure itself is a major cost driver. A small, standardised environment is usually simpler to price than a mixed estate containing legacy servers, several sites, specialist applications, complex networks or systems that cannot be easily replaced. Pricing assessments commonly consider the number of sites, locations of equipment, operating systems, server roles, network dependencies, remote-access arrangements and the extent to which systems are documented.
The condition of the environment also affects cost. If devices are unsupported, security controls are inconsistent, backups have not been tested or documentation is incomplete, the provider may need to carry out discovery and corrective work before routine management can begin. This work is often priced separately because it is not the same as maintaining an environment that already meets the agreed operating standard.
Service scope must be defined precisely. A managed infrastructure fee may cover activities such as monitoring, patch management, maintenance, fault investigation, user administration, backup oversight, network management and technical reporting. It may exclude major upgrades, application development, specialist line-of-business systems, new-site installations, hardware replacement and work caused by changes made by other suppliers. These boundaries prevent a low headline price from concealing substantial additional charges.
Cyber security requirements can add several cost elements. The scope may include security monitoring, endpoint protection, identity controls, vulnerability management, email protection, security assessments, backup safeguards and incident support. The appropriate combination depends on the organisation’s risk profile, regulatory obligations, remote-working arrangements and the sensitivity of its data. Security should be priced as a defined service requirement rather than treated as an unspecified add-on.
Cloud services require particular attention because the management fee and the underlying provider charges may be separate. A quotation should identify whether it includes cloud subscriptions, hosted workloads, storage, backup capacity, licensing, data transfer and administration. It should also explain how increases or reductions in consumption are reflected in invoices, and whether the provider passes through third-party charges at cost or applies a management charge.
One-off costs should be separated from recurring costs. Typical initial charges may include:
- discovery and technical assessment;
- transfer of management from an incumbent provider or internal team;
- network, server or cloud migrations;
- security remediation and configuration work;
- replacement of unsupported equipment;
- deployment of monitoring, backup or security tools; and
- creation or improvement of technical documentation.
These costs may be unavoidable where the existing environment needs preparation, but they should not be confused with the price of ongoing service management. Separating them makes it easier to compare proposals and understand the total cost over the intended contract period.
Contract terms can also influence the price. Relevant points include the length of the agreement, the treatment of additional users and devices, annual price reviews, minimum service quantities, equipment ownership, software licence renewal, project rates and charges for work outside the agreed scope. The agreement should state how infrastructure changes are approved and priced, particularly after acquisitions, office moves, new sites or significant growth.
When comparing quotations, assess the total cost rather than the monthly figure alone. Check the asset and user counts used for the calculation, the included services, exclusions, third-party charges, onboarding work, project assumptions and the process for approving extra work. A useful comparison also asks what happens when usage falls, when equipment is added, or when a service is no longer required.
A sound pricing exercise begins with an accurate inventory and a clear service specification. The provider should understand the current infrastructure, business requirements, security expectations, planned changes and responsibilities on both sides before proposing a charge. For a small or medium-sized organisation without a full internal IT team, this approach helps turn a broad outsourcing proposal into a defined operating budget with identifiable recurring and one-off costs.
Retained responsibilities can materially affect the price. An organisation that keeps some IT work in-house may need a different arrangement from one transferring complete infrastructure management to a provider. The quotation should identify who is responsible for activities such as user support, access approvals, supplier liaison, onsite tasks, change authorisation and technical escalation.
This is often described as a co-managed arrangement. It can reduce the provider’s scope, but only when the division of work is practical and clearly documented. If responsibilities are unclear, tasks may be duplicated, delayed or treated as chargeable additional work. Pricing should therefore be assessed alongside a responsibility matrix showing which party owns each operational activity and what happens when the retained team is unavailable or lacks the required expertise.