
How does small business backup support compliance requirements?
Small business backup supports compliance by helping your organisation protect personal and business-critical data, recover it after loss or disruption, and demonstrate that appropriate safeguards are in place. A suitable approach should define what is backed up, how data is protected, how long it is retained, who can access it and how recovery and testing are recorded.
Small business backup supports compliance requirements by providing controlled, documented and recoverable copies of information that an organisation is responsible for protecting. It is not, by itself, proof of compliance or a substitute for a wider information-security framework. Its value is that it supplies technical safeguards and evidence that can support obligations under the UK GDPR, the Data Protection Act 2018, contractual security terms and sector-specific requirements.
For personal data, the backup process should be considered part of the organisation’s processing activities. This means the business should understand which personal data enters the backup system, where it is stored, who can administer it and which suppliers can access it. The organisation’s privacy information, records of processing and internal policies should reflect this where appropriate. A backup copy should not become an uncontrolled archive of information that the business no longer needs.
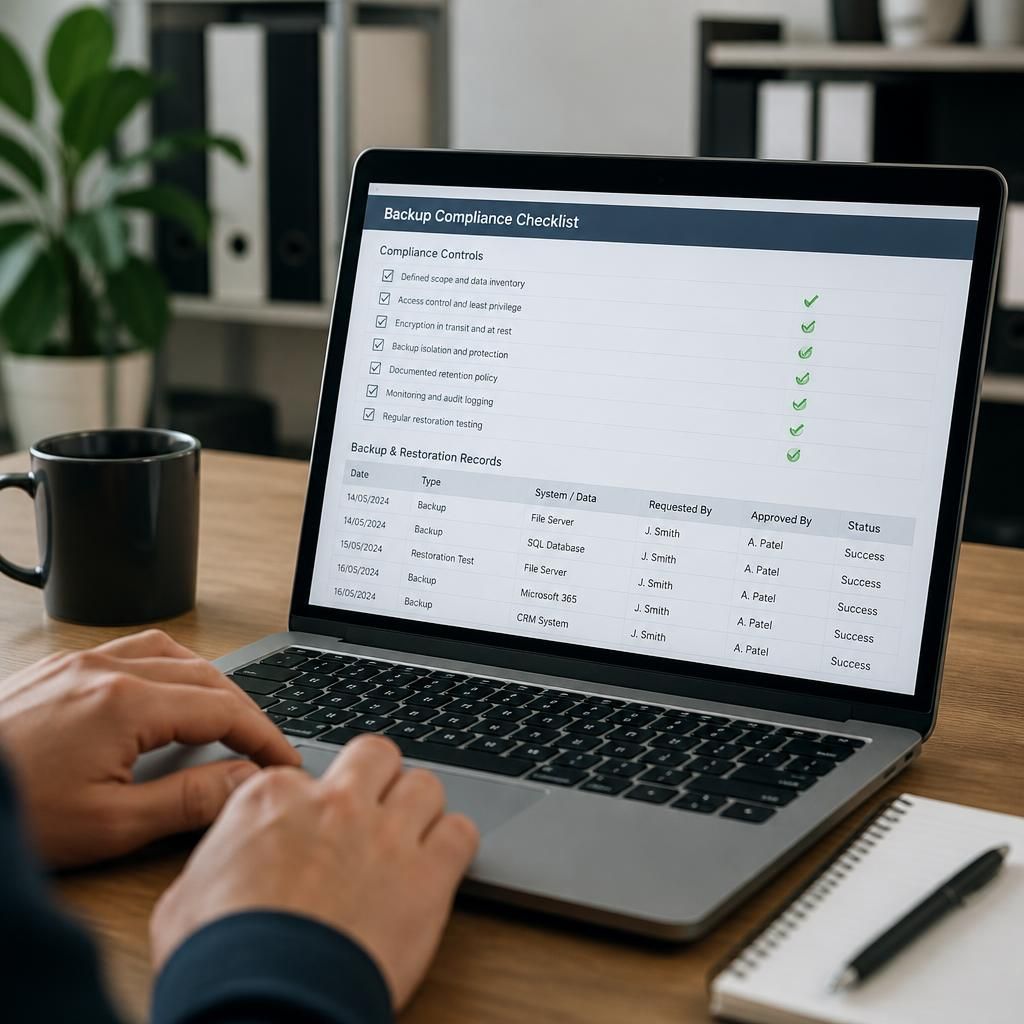
A compliance-focused backup arrangement normally includes the following controls:
- Defined scope: identify the systems, applications, devices, databases and file locations that contain information covered by legal, regulatory or contractual obligations. Exclusions should be documented rather than assumed.
- Access control: restrict backup administration and restoration rights to authorised individuals, using separate accounts, strong authentication and a least-privilege approach. Privileged activity should be attributable to a named user wherever possible.
- Encryption: protect backup data during transfer and while stored, with appropriate management of encryption keys and administrative credentials.
- Separation from production systems: maintain backup copies in a way that limits the effect of a compromised user account, malware infection or administrator credential. This can include isolated, offline or tamper-resistant copies where appropriate to the organisation’s risk.
- Documented retention: link retention periods to legal, contractual and operational needs. Keeping every copy indefinitely can increase exposure, while deleting copies too soon can undermine recovery and record-keeping requirements.
- Monitoring and evidence: retain relevant records of backup activity, failures, administrative changes, restoration exercises and exceptions. Evidence should be understandable to someone reviewing the control independently.
Retention requires particular care under data-protection rules. The original record may need to be deleted or amended while older backup versions still contain it. Organisations should therefore define how backup copies are handled when a retention period expires, data is deleted, or an individual makes a valid rights request. Depending on the system, the appropriate approach may be scheduled expiry, restricted use of older copies, or removal during the next controlled backup cycle. The process should be documented and applied consistently.
Compliance also depends on the backup provider and its supporting infrastructure. Due diligence should cover the supplier’s security measures, subcontractors, processing locations, access arrangements, breach-notification responsibilities, deletion process and contractual terms. Where a provider processes personal data on the organisation’s behalf, the relevant controller and processor responsibilities should be recorded in a suitable data-processing agreement. International transfers may require additional assessment and safeguards.
A backup plan should align with the organisation’s wider risk assessment and business continuity arrangements. For example, a business may need to show that its backup design reflects the importance of payroll, customer records, production data or financial information, rather than applying identical treatment to every file. The required recovery capability, retention approach and security controls should follow that assessment.
Auditors, customers and regulators may look for evidence rather than a statement that backups exist. Useful evidence can include:
- an approved backup and retention policy;
- a current inventory of protected systems and data categories;
- records of access reviews and privileged-account changes;
- backup and restoration logs;
- records showing how failed jobs or exceptions were investigated;
- supplier assessments and relevant contractual documentation;
- records of recovery exercises and resulting improvements; and
- documented handling of obsolete backup sets and data-deletion requests.
Backup evidence should also be protected from unauthorised alteration. If logs can be edited by the same account that performs backup administration, they provide weaker assurance during an investigation or audit. Separating operational permissions from review permissions, retaining appropriate audit trails and regularly reviewing exceptions makes the evidence more credible.
The practical test is whether the organisation can explain its backup decisions and show that they are implemented consistently. A small business should be able to identify the information it must protect, justify its retention approach, demonstrate who can control the backups, and produce records showing that the arrangement operates as intended. Professional IT support can help translate these requirements into documented controls, but the organisation remains responsible for understanding the obligations that apply to its own data, contracts and sector.
Controlled restoration is an important part of compliance evidence. A backup may be securely stored, but the organisation must also control what happens when data is restored. The restoration process should specify who can approve it, which destination may receive the data, how access is restricted and how any temporary or duplicate copies are removed afterwards.
This is particularly relevant where restored information contains personal, confidential or commercially sensitive data. A documented restoration record should identify the reason for the request, the data involved, the person authorising it and any follow-up action required. These controls help demonstrate that backup data is used for a defined business purpose rather than accessed or copied without oversight.
Discuss your small business backup compliance requirements
Discuss your small business backup compliance requirements with S2 Technology Group to identify practical improvements for your organisation. Bring your current backup arrangements and relevant contractual or sector requirements for an informed review.