What connectivity is needed for virtual IT solutions?
Virtual IT solutions need a reliable internet connection with sufficient bandwidth, low latency and stable performance for cloud applications, hosted desktops, file access and online collaboration. Secure remote access, suitable network equipment and a resilient connection may also be required, with the exact specification determined by the number of users, applications and business-critical workloads.
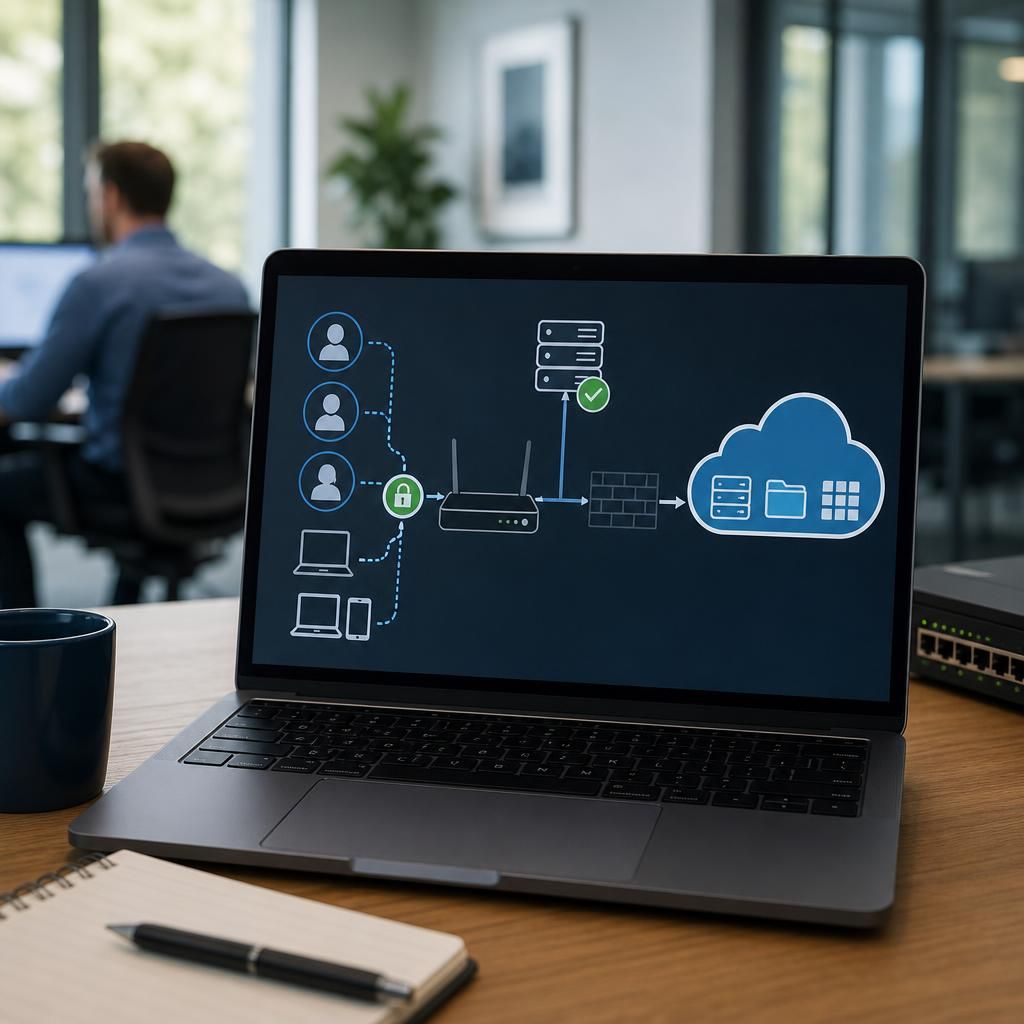
The connectivity required for a virtual IT solution depends on how users, applications and data are hosted. A basic setup may need dependable access to cloud services, while a hosted desktop or virtual application environment requires connectivity that can support continuous interactive use. The assessment should therefore consider the complete network path, not just the advertised download speed.
Bandwidth planning. Available capacity must account for concurrent users and the type of traffic they generate. Email and browser-based applications usually create less demand than hosted desktops, video meetings, large file transfers, cloud backups or graphics-intensive applications. Upload capacity is equally important where staff save files to cloud platforms, use voice and video services, or transfer data between offices and hosted systems. Capacity should be assessed at busy periods rather than from an average usage figure.
Performance consistency. Interactive virtual environments are affected by variation in network performance. Latency is the time taken for data to travel between a user and the hosted environment; jitter describes changes in that delay, and packet loss occurs when data does not arrive successfully. Excessive variation can make applications feel unresponsive, interrupt voice and video, or cause remote sessions to disconnect. Testing should measure these characteristics to the actual service locations being used, rather than relying solely on an internet provider’s headline speed.
Network layout inside the organisation. The internal network must carry traffic from user devices to the internet connection without creating a bottleneck. Wired connections are often preferable for fixed workstations, meeting-room equipment and other devices that need consistent performance. Wi-Fi design also matters: access-point placement, channel interference, building materials, user density and the number of connected devices can all affect the experience of virtual applications. Guest and non-business traffic should be separated from business systems where appropriate.
Secure access controls. Connectivity should be integrated with the organisation’s wider security design. Firewalls, encrypted remote-access services, identity checks and access permissions help ensure that users reach only the systems and information they are authorised to use. Remote users may also need suitable device security and multi-factor authentication. Security controls should be configured in a way that protects access without routing unnecessary traffic through a central location and introducing avoidable delays.
Traffic management. Quality-of-service rules can prioritise time-sensitive traffic, such as voice, video or interactive virtual sessions, over less urgent transfers. Large updates, backups and file synchronisation may need scheduling or rate limiting so they do not consume capacity during periods of normal work. This is particularly relevant where several sites share a connection or where a small office supports a large number of cloud-dependent users.
Resilience and continuity. A connectivity design should identify what happens if the primary connection, firewall, router, power supply or local network fails. Options may include a separate connection delivered through a different route, automatic failover, documented manual workarounds or alternative access arrangements. A secondary service is only useful if it is sufficiently independent and the failover process has been tested. The design should also account for whether users can continue working if the connection temporarily offers reduced capacity.
Connectivity between sites. Multi-site organisations may need secure links between offices, data platforms and virtual environments. The design depends on whether applications are hosted centrally, accessed directly from the cloud, or shared between sites. Routing, address management and traffic separation should be planned so that a problem at one location does not unnecessarily affect every other location.
Monitoring and testing. Performance should be checked before implementation and reviewed after deployment. Useful checks include usage during busy periods, latency to hosted services, packet loss, wireless coverage, failover behaviour and the effect of large transfers on application performance. Ongoing monitoring can help distinguish a connectivity fault from an application, device or authentication problem, making technical issues easier to diagnose.
For this reason, connectivity specifications should be based on a documented workload assessment rather than a generic broadband package. S2 Technology Group can review the proposed virtual IT arrangement, user locations, application requirements and existing network design to identify constraints and define an appropriate connectivity plan before implementation.
Connectivity for virtual IT solutions also depends on the supporting network services that help users and devices find, reach and authenticate to hosted resources. A connection may be active while access still fails if services such as DNS, identity authentication or time synchronisation are unavailable or incorrectly configured.
DNS allows devices to locate cloud applications, virtual desktops and other hosted systems. Authentication services verify user identities and apply access permissions, while accurate time settings support certificate and security checks. These dependencies should be mapped before implementation so that traffic can reach the required services and failures can be diagnosed accurately.
Organisations should document which services are hosted locally, which are cloud-based and which are required for users to sign in. This helps prevent a design where the primary virtual environment is available but users cannot access it because a separate local service or network dependency is unavailable.