
Does remote managed IT support include patch management?
Yes, remote managed IT support can include patch management: monitoring for operating system and application updates, assessing their relevance, and deploying them remotely according to an agreed policy. This helps address known vulnerabilities and keeps business devices more consistent and supportable.
It can, but the exact scope of patch management depends on the agreed service policy, the devices covered and the organisation’s tolerance for change. A complete process is more than installing updates: it establishes which assets and applications are in scope, evaluates relevant patches, plans deployment, records results and deals with exceptions.
Effective patch management usually begins with an accurate asset and software inventory. This identifies business computers, servers, virtual machines and other managed equipment, together with the operating systems and applications they run. Without this information, devices can be missed, duplicated records can persist, and vulnerable software may remain in use without being recognised.
Updates are then assessed rather than applied indiscriminately. The assessment can consider the severity of the vulnerability, whether the affected software is present, the importance of the device, known compatibility issues and whether the update requires a restart. Security patches may need different treatment from feature updates because they address a specific exposure, while major version changes may require additional testing or licensing checks.
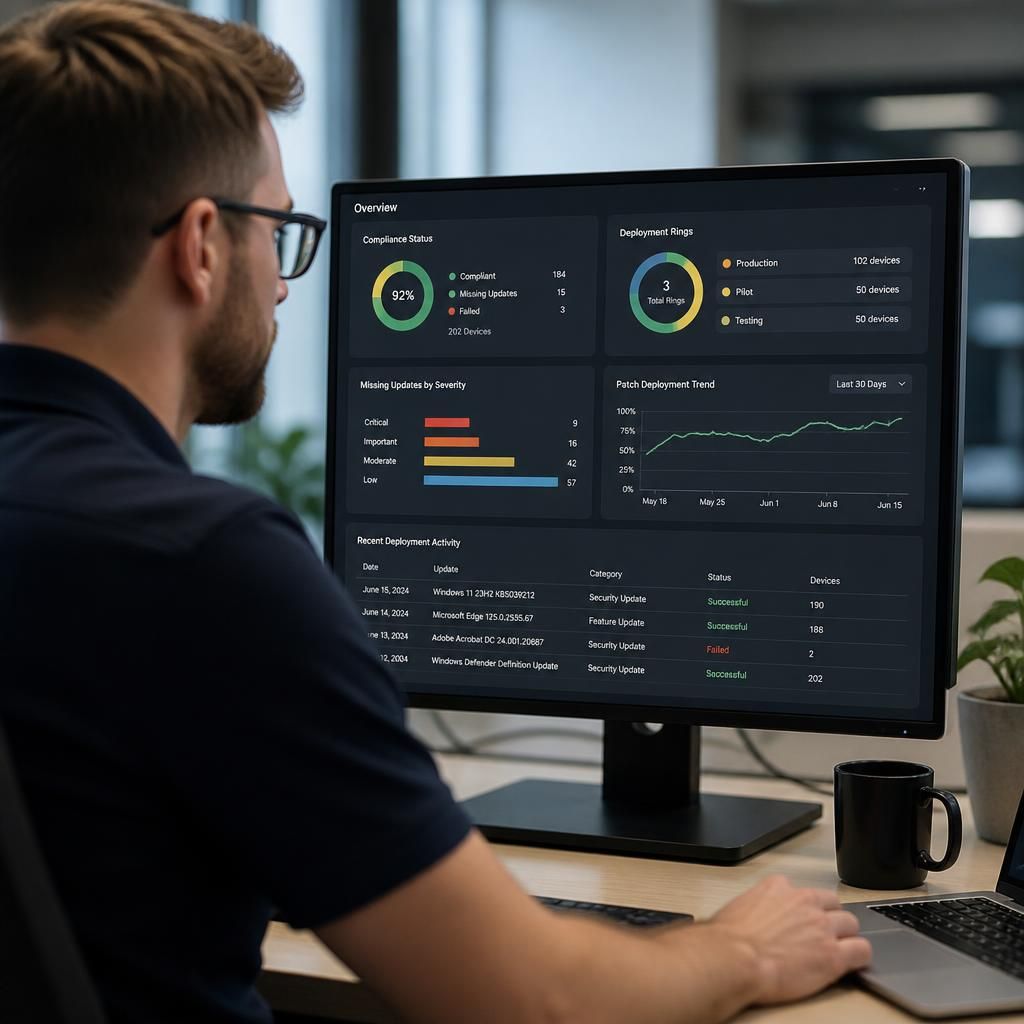
A sensible deployment process uses defined groups or stages. For example, updates may first be applied to a limited set of representative devices, allowing potential application or driver conflicts to be identified before wider deployment. Devices supporting specialist software, production processes or shared business services may require additional validation and a separately agreed maintenance plan. This helps balance the need to reduce exposure with the need to avoid unplanned disruption.
Remote delivery is useful because updates can be coordinated through management tools without requiring an engineer to visit each workstation. However, a remote process still depends on the device being powered on, connected to the relevant management service and in a suitable state for the update. A laptop that remains disconnected, a server with limited maintenance access or an update blocked by local conditions may need further investigation. Failed, deferred or incomplete installations should be recorded rather than treated as successfully patched.
Patch management may cover operating systems and common business applications, but its boundaries should be stated clearly. Depending on the agreement, it might also include selected server software, drivers, firmware, virtualisation components or network equipment. Some specialist applications are controlled by their supplier or require compatibility testing, so they may be monitored and reported on without being updated automatically. Unsupported software presents a separate risk because it may no longer receive fixes and may need replacement, isolation or a documented exception.
Reboots and user disruption should be addressed in advance. A patch policy can define whether restarts require approval, how users are notified, which devices can be restarted automatically and what happens when a restart is repeatedly postponed. It should also specify how urgent security updates are prioritised, how failed patches are retried, and when an exception is escalated for a business decision.
Useful patch-management reporting should show more than a general statement that updates are being handled. Reports can identify:
- the devices and software included in the policy;
- updates installed successfully and the relevant installation dates;
- devices still awaiting updates or restarts;
- failed installations and the reason for failure, where known;
- approved exclusions, unsupported software and compensating controls; and
- items requiring action from the organisation or an application owner.
Patch management does not remove every cyber security risk. Updates can be unavailable for newly discovered vulnerabilities, delayed by compatibility concerns or ineffective against compromised accounts and unsafe configurations. It therefore works alongside access controls, endpoint protection, secure backups, vulnerability review and user security measures.
For a small or medium-sized organisation, the important point is to confirm what the remote managed IT support agreement actually includes: asset types, third-party applications, testing, restart handling, reporting, exclusions and responsibility for specialist systems. S2 Technology Group can use an agreed policy to make patching part of a broader managed IT and cyber security approach, with the scope defined around the organisation’s systems and operational requirements.
Patch management for cloud-based applications is often handled differently from patching a business-owned computer or server. The software provider usually applies updates to the hosted service, while remote managed IT support checks that the service remains within the agreed scope and that related devices, browsers, integrations and security settings are kept suitable for the change.
This distinction should be recorded in the patch policy. It can identify which systems are updated by the provider, which components remain the organisation’s responsibility and what evidence is available after a significant update. Where a supplier announces a change that could affect an integration or business process, the IT provider can help assess dependencies and direct any required testing to the relevant system owner.
As a result, patch management is not limited to remotely installing files. It also involves confirming who controls each update, understanding how changes affect the wider environment and ensuring that responsibility is clear across hosted services and locally managed technology.