
How is downtime managed during a Microsoft 365 migration?
Downtime during a Microsoft 365 migration is managed through careful planning, pre-migration checks and a phased cutover that limits disruption to essential services. Migration tasks are scheduled around business requirements, with user communication, validation and contingency planning used to identify and resolve issues before they affect wider operations.
Downtime during a Microsoft 365 migration is managed by separating the move into controlled technical changes rather than switching every service at once. The objective is to keep users productive while mailboxes, files, identities, devices and business applications transition to the new environment.
The first step is to define what “downtime” means for each workload. Email access, calendars, shared mailboxes, document libraries, authentication, mobile access and line-of-business applications can be affected in different ways. A migration plan should therefore record the expected impact for each service, the users involved and the action required if that service becomes unavailable.
- Email: Mail flow is arranged so messages continue to reach the appropriate environment while mailboxes are being moved. The final routing change is treated as a separate activity from the mailbox transfer.
- Files and collaboration data: Data may remain available in its original location while content is copied, with the final switch restricted to a defined set of libraries, users or work areas.
- Identity and authentication: Sign-in dependencies are checked so that users can authenticate to Microsoft 365 and any connected business systems after the change.
- Devices: Outlook profiles, mobile mail settings, desktop applications and authentication methods are considered separately, as a mailbox migration does not automatically reconfigure every endpoint.
A pilot group is useful before the wider cutover. It should include representative users, shared resources and common device types rather than only technically experienced staff. The pilot can expose problems such as incorrect permissions, missing calendar access, profile prompts, authentication errors or incompatible applications without affecting the whole organisation.
Where the migration method supports coexistence, users can be moved in batches while the remaining users continue working in the original environment. Batch boundaries should reflect business structure and dependencies. For example, a department that relies on shared mailboxes, delegated calendars or a particular workflow may need to move together to avoid broken access arrangements.
Migration workloads also need to be controlled so that data transfer does not consume the network capacity required for normal business activity. Transfer schedules, bandwidth limits and batch sizes can be adjusted according to the organisation’s connectivity and the nature of the data. This is particularly relevant for businesses with remote offices, large document stores or several sites using the same internet connection.
The cutover itself should have a defined start point, sequence and decision criteria. Typical tasks include confirming that the relevant data has transferred, applying the required configuration, updating user access, checking service dependencies and confirming that representative users can work normally. Each task should have an assigned owner and a recorded completion status so that an issue is not missed between technical teams.
Rollback planning is also important. A rollback is not simply restoring a previous setting; it may involve reversing configuration changes, returning mail flow to the previous route, re-establishing access to the source environment or postponing the next migration batch. The practical rollback option depends on the migration method and on whether new data has been created in the destination environment, so it must be established before the cutover begins.
After each batch, technical monitoring and user checks help distinguish a genuine migration fault from a local device or application issue. Useful checks include sending and receiving test messages, opening shared resources, confirming calendar access, testing authentication and checking applications that depend on Microsoft 365 accounts. Issues should be logged by service and severity, with later batches paused if a problem indicates a wider configuration defect.
Businesses can further reduce disruption by identifying periods when particular teams are least dependent on the systems being moved and by avoiding unnecessary changes during the same cutover. A change freeze for unrelated IT work can make faults easier to trace, while keeping source data protected and retaining relevant audit information supports investigation if an unexpected issue occurs.
For small and medium-sized organisations without a dedicated migration team, an experienced IT provider can coordinate these controls as part of the migration service. S2 Technology Group supports businesses around Stourbridge, Kinver, Wordsley, Kingswinford, Kidderminster, Halesowen, Dudley and neighbouring areas with structured Microsoft 365 migration planning, technical coordination and post-cutover checks. The appropriate approach depends on the existing tenant, data volume, identity setup, connectivity, devices and applications in use.
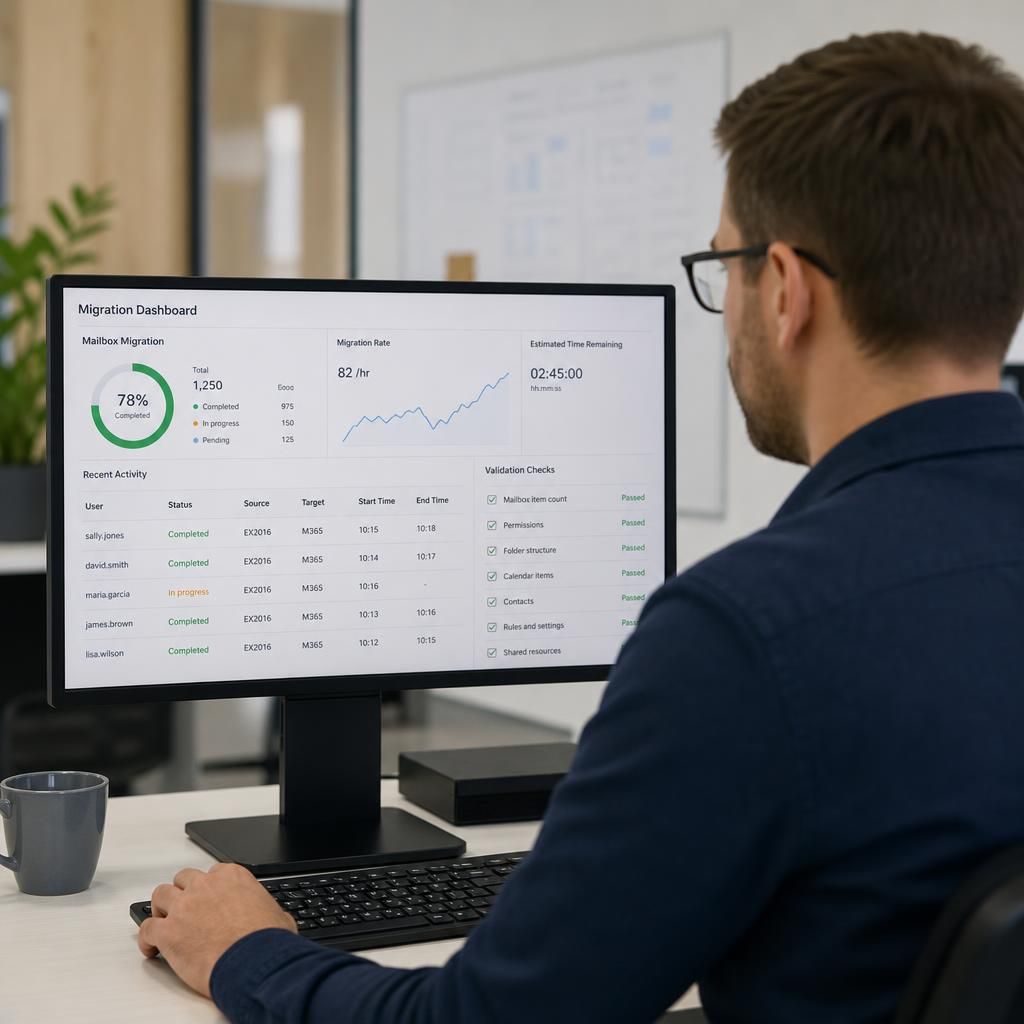
A controlled final synchronisation helps limit the period in which users must stop changing data. Where the migration method supports it, information is copied in advance while the source remains available. A short, agreed freeze then prevents changes during the final transfer, allowing the migration team to capture recent updates rather than copying the entire dataset during the cutover.
Before access is released in Microsoft 365, the final synchronisation is reconciled against the source environment. This includes checking recently changed files, mailbox activity, permissions and shared resources, with any exceptions recorded for investigation. Users are then given clear instructions about which environment to use and when normal editing can resume. This approach makes the interruption a defined control point rather than an uncertain loss of access.