
Does Microsoft 365 security training include audit log analysis?
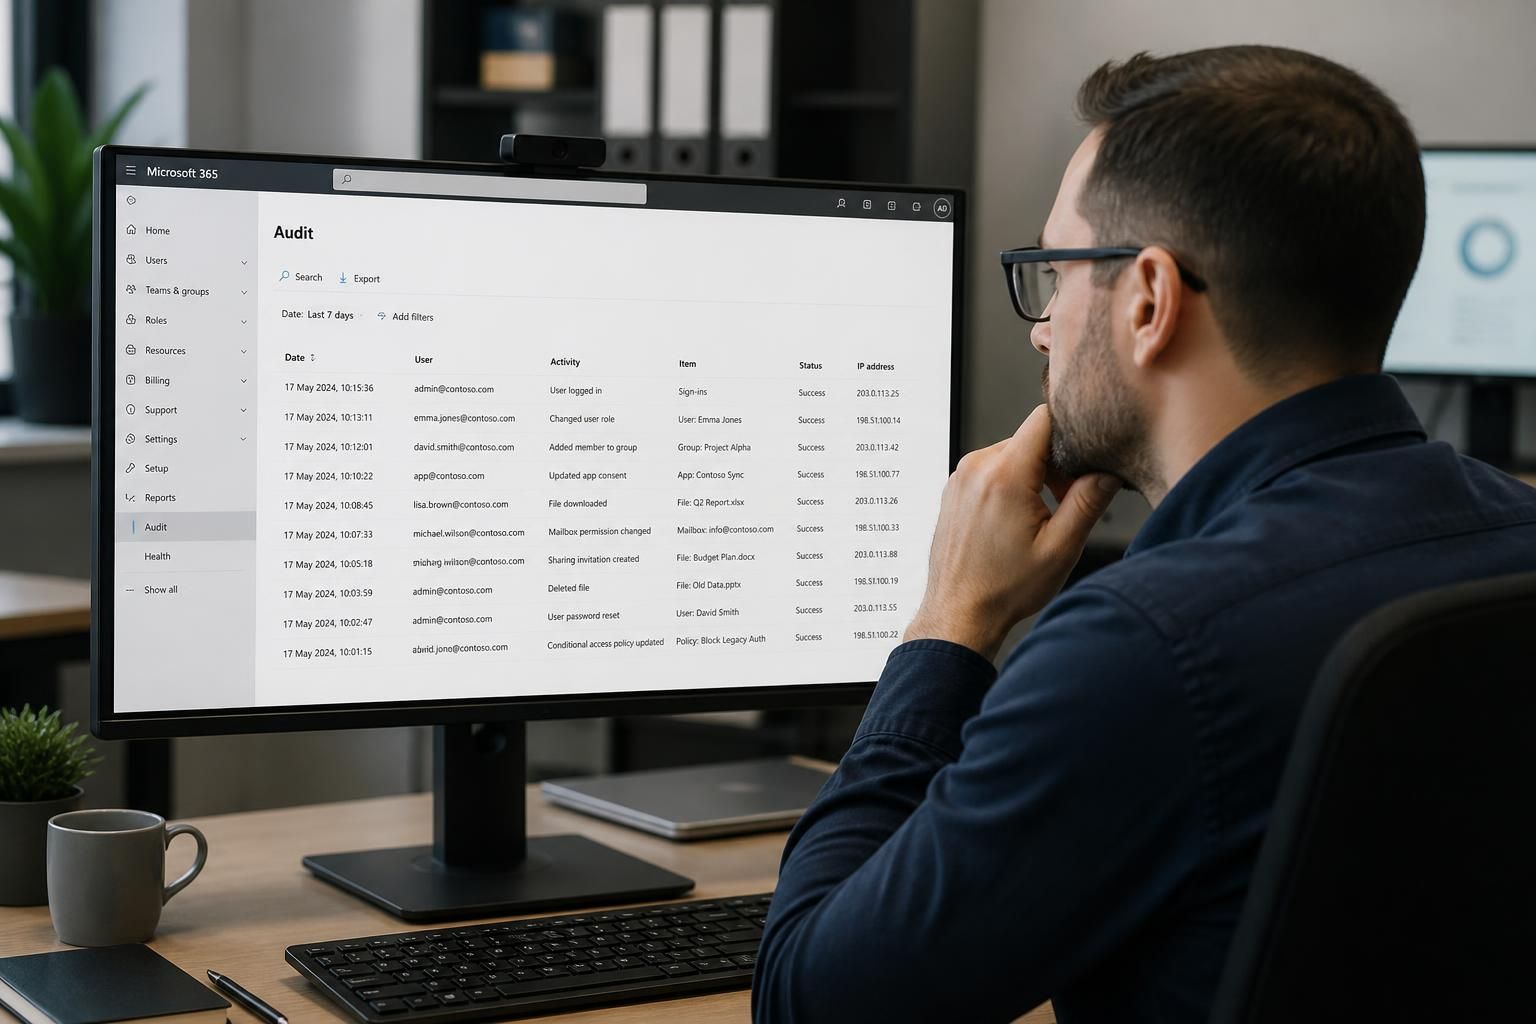
Yes. Microsoft 365 security training should include audit log analysis, covering how to access the Unified Audit Log, filter relevant events, interpret administrator and user activity, and use findings to investigate suspicious behaviour or security incidents.
Microsoft 365 security training should treat audit log analysis as an investigative skill, not simply a demonstration of where to find records. The aim is to help administrators decide which activity matters, establish whether it is expected, and preserve enough context to support a defensible security decision.
A thorough course should explain the types of activity recorded across the tenant and how those records relate to common security questions. For example, an administrator may need to determine whether a privileged setting changed, whether a user accessed or shared information unexpectedly, or whether an application and account were used together in a suspicious sequence. Training should show how to narrow a search without excluding relevant evidence, then widen it when an initial result appears incomplete.
Interpretation is as important as searching. Each event should be considered in context, including:
- the account, role or application associated with the action;
- the time and location recorded for the event, including the effect of time-zone differences;
- the operation performed and the object or setting affected;
- whether the activity was successful, repeated or followed by other changes;
- whether the behaviour matches an approved administrative task, user responsibility or change record.
Training should also cover correlation between events. A single sign-in or configuration change may be legitimate, whereas a sequence involving unusual access, privilege changes and subsequent data activity may require investigation. Learners should practise building a timeline, separating confirmed facts from assumptions, and identifying gaps that require additional evidence rather than treating every unusual event as proof of compromise.
Good instruction includes realistic exercises. These might involve reviewing a suspected account takeover, investigating an unexpected administrator change, or tracing activity after a security alert. The learner should be required to record the search criteria used, explain why particular events are relevant, summarise the findings and recommend the next administrative action. This tests judgement as well as technical navigation.
Audit records also need to be handled carefully. A course should explain retention, access permissions, search limitations and the effect of tenant configuration on what can be found. Learners need to understand that an empty result does not necessarily prove that an action did not happen. Retention periods, unsupported activity types, delayed availability, incorrect filters and insufficient permissions can all affect an investigation. Where evidence may support disciplinary, legal or regulatory action, the process should include controlled access, accurate timestamps, documented handling and appropriate escalation.
Analysis should feed into a wider incident process. Training can show how to move from an event to a proportionate response: validate the activity, protect affected accounts or data where authorised, preserve relevant evidence, notify the responsible security contact, and document the decision. It should also explain when an administrator should stop investigating independently and involve an incident response lead or other specialist.
Administrators should learn to distinguish audit data from other security information. Audit records describe activity after it has been logged; they do not by themselves provide continuous detection, explain every underlying cause or replace access reviews, configuration checks and user reports. Combining these sources produces a more reliable assessment than relying on one event or one search result.
Finally, effective Microsoft 365 security training should revisit audit-log procedures as the tenant changes. New services, altered permissions, revised retention settings and changes to administrative responsibilities can affect both the available evidence and the people authorised to review it. A useful course therefore leaves the team with documented search patterns, investigation templates and a clear process for validating those procedures against the organisation’s own security policies.
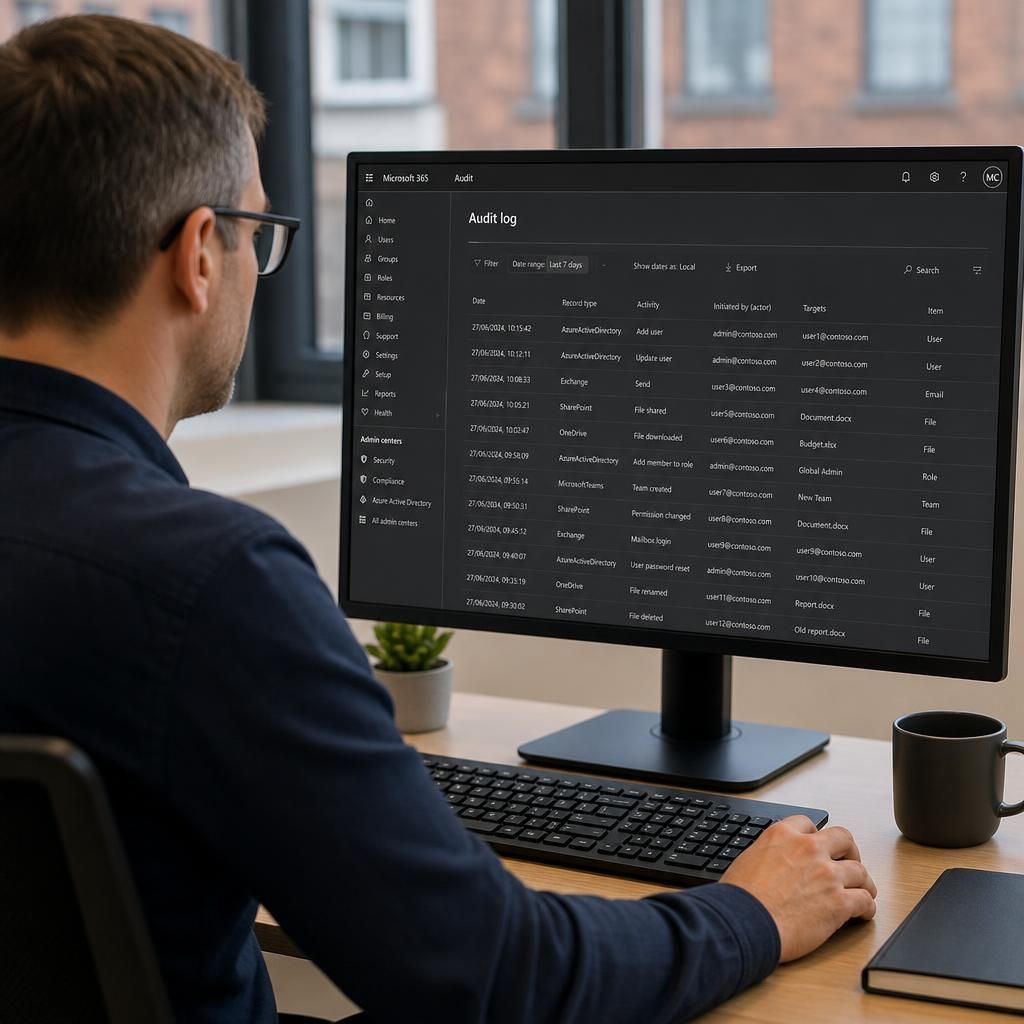
Microsoft 365 security training should also cover the use of audit data for routine governance, not only post-incident investigations. Administrators can review activity against approved changes, access policies and delegated responsibilities to identify exceptions before they become security incidents.
This part of the training should explain how to define a review scope, select meaningful activity categories and record exceptions consistently. A useful exercise might ask learners to examine privileged actions or sharing changes from a defined period, compare them with authorised business activity, and classify each result as expected, requiring clarification or requiring escalation. This helps establish a repeatable review process without treating every recorded action as suspicious.