
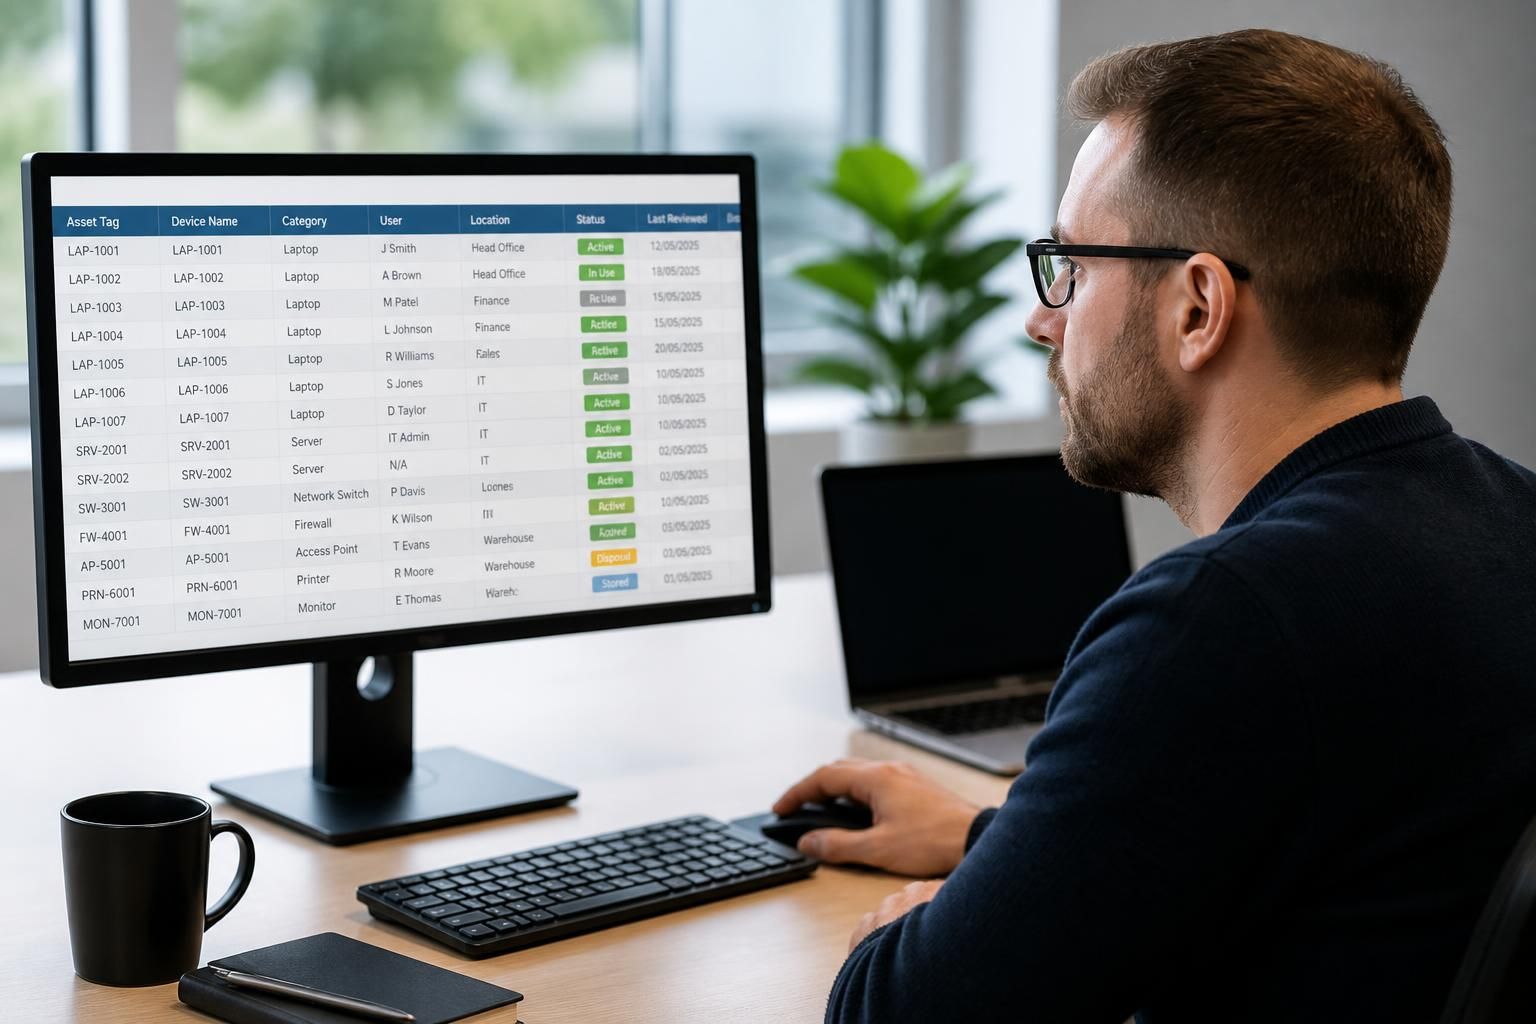
How often should IT asset records be reviewed?
IT asset records should be reviewed on a regular, risk-based schedule, with higher-risk or frequently changing environments checked more often. They should also be updated whenever equipment is purchased, moved, retired, replaced or materially changed, so the register remains accurate for security and management decisions.
For most businesses, IT asset records should receive a formal review at least quarterly, with more frequent checks for assets that hold sensitive data, provide critical services or are exposed to higher levels of risk. A review should compare the register with reliable evidence, rather than simply confirming that the document still exists.
A practical review cycle can be structured according to the importance and volatility of each asset:
- High-risk or business-critical assets: review monthly or at another suitably frequent interval. This may include servers, network security appliances, privileged-user devices, backup systems and equipment supporting essential operations.
- Standard business equipment: review quarterly. This normally covers employee laptops, desktop computers, printers, network equipment and other devices used in day-to-day work.
- Lower-risk or infrequently changing assets: review every six months, provided there is a reliable process for recording changes between formal reviews.
These intervals are starting points rather than universal rules. The right frequency depends on the organisation’s risk assessment, number of locations, remote-working arrangements, rate of staff change, asset lifespan and the sensitivity of the information handled. A business with multiple sites or a rapidly changing device estate may need a tighter cycle than a smaller organisation with a stable environment.
Each review should establish whether the record is complete, accurate and useful for decision-making. Important checks include:
- matching recorded devices to endpoint management, monitoring, security or directory systems;
- confirming the assigned user, department, location and responsible owner;
- checking operating system, firmware and software information where relevant;
- identifying assets with missing serial numbers, duplicate entries or unclear ownership;
- confirming that retired, lost, returned or disposed-of equipment is no longer shown as active;
- checking whether support arrangements, warranty details and lifecycle status remain correct; and
- recording exceptions that require investigation rather than silently changing the data.
Event-driven checks are also important. A formal review should be triggered by a major office move, acquisition, restructuring, device deployment, network redesign, security incident or change in working arrangements. These events can make a previously accurate register unreliable, particularly where equipment is transferred between users or locations.
The review process should have a named owner, defined evidence sources and an audit trail. Changes should show what was amended, who approved it and when the amendment was made. Where an asset cannot be verified, it should be placed into an exception queue with an owner and follow-up action. This prevents uncertain information from being treated as confirmed simply because it remains in the register.
Asset records should also be reconciled with related business processes. For example, procurement records can identify equipment that has entered the organisation, service desk records can reveal devices in active use, and disposal records can support the removal of decommissioned items. Security tools may identify an unmanaged device that the asset register does not contain. Comparing these sources helps expose gaps that a document-only review would miss.
Review frequency should be reassessed when the organisation’s risk profile changes. New regulatory obligations, increased remote access, adoption of cloud services, changes to sensitive-data processing or a rise in unmanaged devices may justify a more frequent schedule. Conversely, a stable asset category may be reviewed less often if automated discovery and strong change controls provide dependable information between formal reviews.
For small and medium-sized organisations, the most effective approach is usually a documented review calendar supported by automated discovery where practical. The important measures are not how often a spreadsheet is opened, but whether unauthorised, missing, duplicated or obsolete assets are identified and acted upon. Accurate records give security, IT and business leaders a dependable basis for access reviews, vulnerability management, replacement planning and incident investigation.
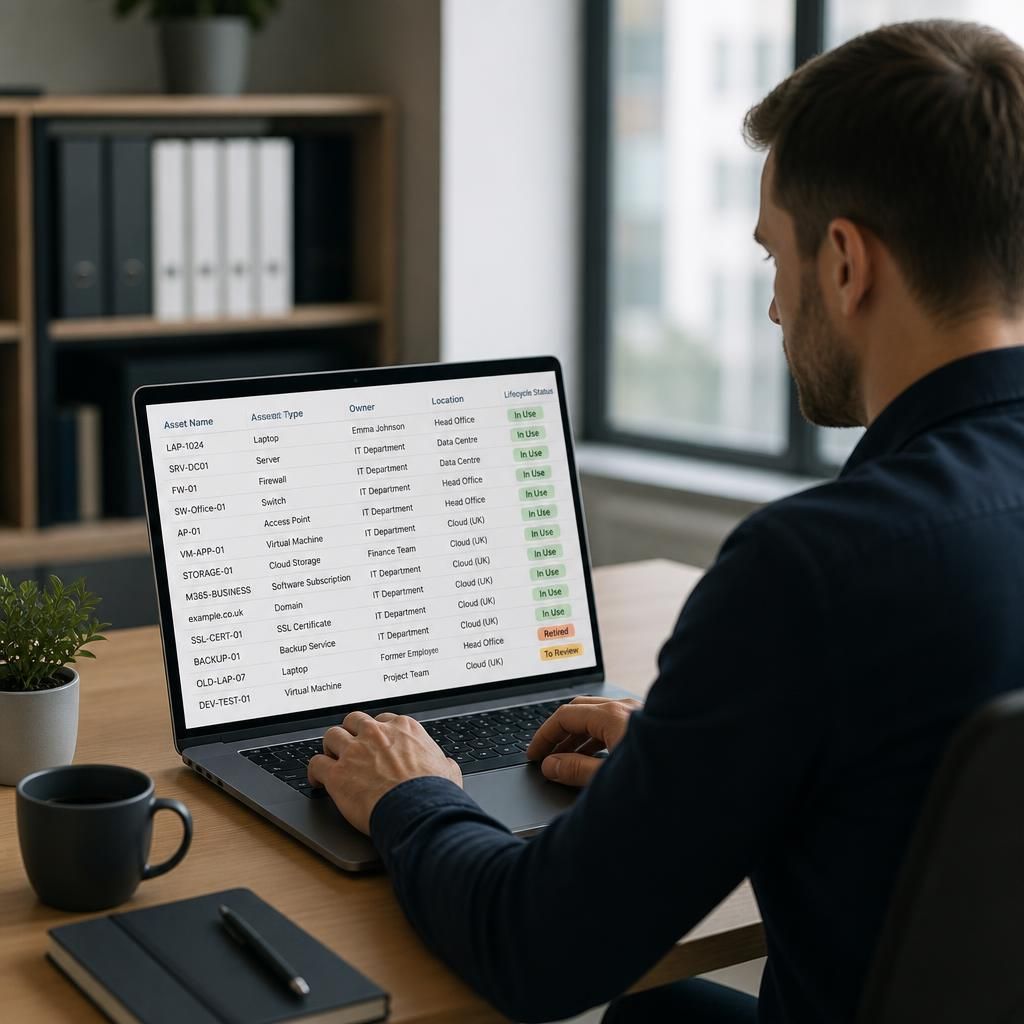
IT asset reviews should cover digital and cloud-based assets as well as physical equipment. A warehouse or office check may confirm that laptops and network devices are present while overlooking virtual machines, cloud storage, software subscriptions, domains, certificates and hosted services that have been added, transferred or abandoned.
For these assets, the review should verify the business owner, purpose, administrative responsibility, access arrangements and lifecycle status. It should also identify resources that no longer have a valid business purpose or are still linked to former staff, projects or suppliers. Including these items gives the register a more complete representation of the technology the organisation relies on, rather than treating the physical device list as the whole asset estate.