
How does IT service management handle service requests?
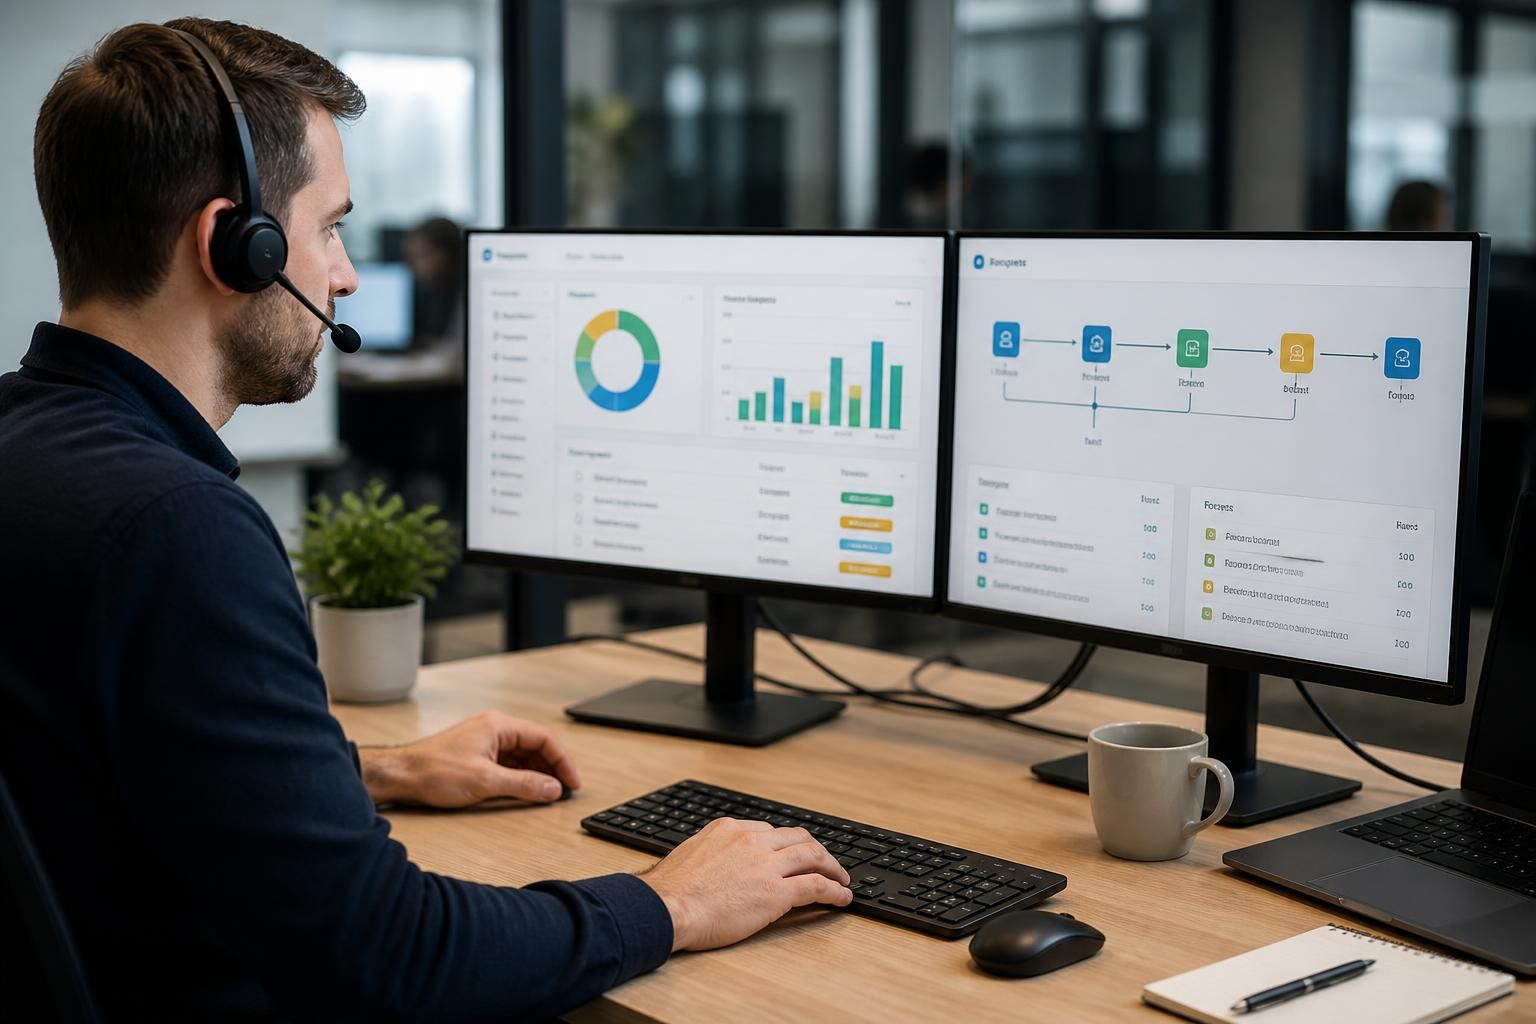
IT service management handles service requests through a defined process: the request is logged, categorised, assessed for priority and approval, assigned to the appropriate person, fulfilled and then closed after confirmation. This creates a consistent record of routine needs such as access changes, software requests and equipment provision, while keeping incidents on a separate process.
IT service management handles service requests by managing them as controlled, trackable items rather than informal conversations. Each request is matched to a defined service, checked against the requester’s authority and business need, fulfilled using an appropriate procedure, and retained as an auditable record.
Service catalogues define what can be requested. A service catalogue gives users and the service desk a clear list of available services, such as new user access, additional software, equipment, shared-folder permissions, mobile devices or changes to an existing service. Each catalogue entry should explain who can request it, what information is required, whether approval is needed, and what fulfilment steps apply. This reduces ambiguity and helps distinguish a routine request from an incident, change or project.
Request capture starts with complete information. A request should record the requester, affected user or service, business justification, required access or equipment, relevant deadlines and any supporting details. Structured forms are preferable to free-text descriptions because they collect consistent information and can apply conditional questions. Requests received through email, telephone or informal messages should still be converted into the organisation’s central service record so that ownership and progress remain visible.
Classification determines the correct workflow. A standard request follows a pre-approved procedure with known risks and repeatable fulfilment steps. A non-standard request may require technical assessment, security review, procurement input or formal change control. If the user is reporting that an existing service is unavailable or degraded, the matter should be handled as an incident rather than a service request. Keeping these categories separate produces more accurate reporting and prevents routine fulfilment work from obscuring service disruption.
Approval should match the risk. Low-risk, pre-authorised requests can follow an agreed approval route, while requests involving privileged access, sensitive information, financial commitment or material system changes require additional scrutiny. Approval records should identify who authorised the request, what was approved and when. A manager’s approval may confirm business need, but it does not replace a technical or security check where the request could increase exposure or affect regulatory obligations.
Prioritisation is based on business relevance. Not every request needs the same level of urgency. The service management process should consider the effect on business operations, the number of people affected, dependencies on other work, security implications and any genuine operational deadline. A request that is important to one individual may not take precedence over work supporting a critical business service. Priority rules should be documented so similar requests are treated consistently rather than according to who submits them or how forcefully they are worded.
Fulfilment uses standard operating procedures. Once the request is authorised, it is assigned to a role or team with the required capability. The procedure may include identity verification, licence checks, device preparation, configuration, testing and user guidance. Where several teams are involved, the record should show the hand-offs and dependencies. Automation can be useful for repeatable tasks, such as provisioning approved access, but automated actions should have suitable safeguards, logging and a way to stop or reverse an incorrect change.
Security controls are part of request handling. Requests to create accounts, alter permissions or access confidential data need stronger validation than straightforward information requests. The service desk should verify the requester’s identity through an approved method and avoid treating an email address alone as proof of authority. Access should be limited to what is required for the role, with time-limited or reviewable permissions where appropriate. Equipment requests should also account for asset ownership, secure configuration and the return or disposal of replaced devices.
Communication keeps expectations accurate. The requester should be able to see what has been received, whether further information or approval is needed, who owns the next action and whether a dependency is preventing fulfilment. Updates should use clear status descriptions rather than vague wording. If the request cannot be completed as submitted, the record should explain the reason and identify an alternative, revised request or escalation route.
Closure confirms that the request achieved its purpose. Before closing the record, the fulfilment team should confirm what was provided, record relevant configuration or asset details, and establish that the requester or designated owner can use the service. Closure should not simply mean that a technician performed a task. It should also capture rejected, cancelled and withdrawn requests with an appropriate reason, preserving an accurate history for audit and future analysis.
Service request management is measured through useful operational data. Reports can examine request volumes by service, recurring request types, approval delays, rework, ageing records, hand-offs and the proportion completed through standard procedures. These measures help identify unclear catalogue entries, training needs, inefficient approval routes and opportunities for automation. They should be interpreted alongside business impact rather than used as a reason to close records prematurely.
For a managed IT environment, this process also provides a practical basis for reviewing user access, equipment allocation, software licensing and recurring administrative work. S2 Technology Group can use service management practices as part of broader IT support, cyber security and cloud management, helping small and medium-sized organisations establish consistent controls without requiring every request to be handled as a bespoke technical exercise.
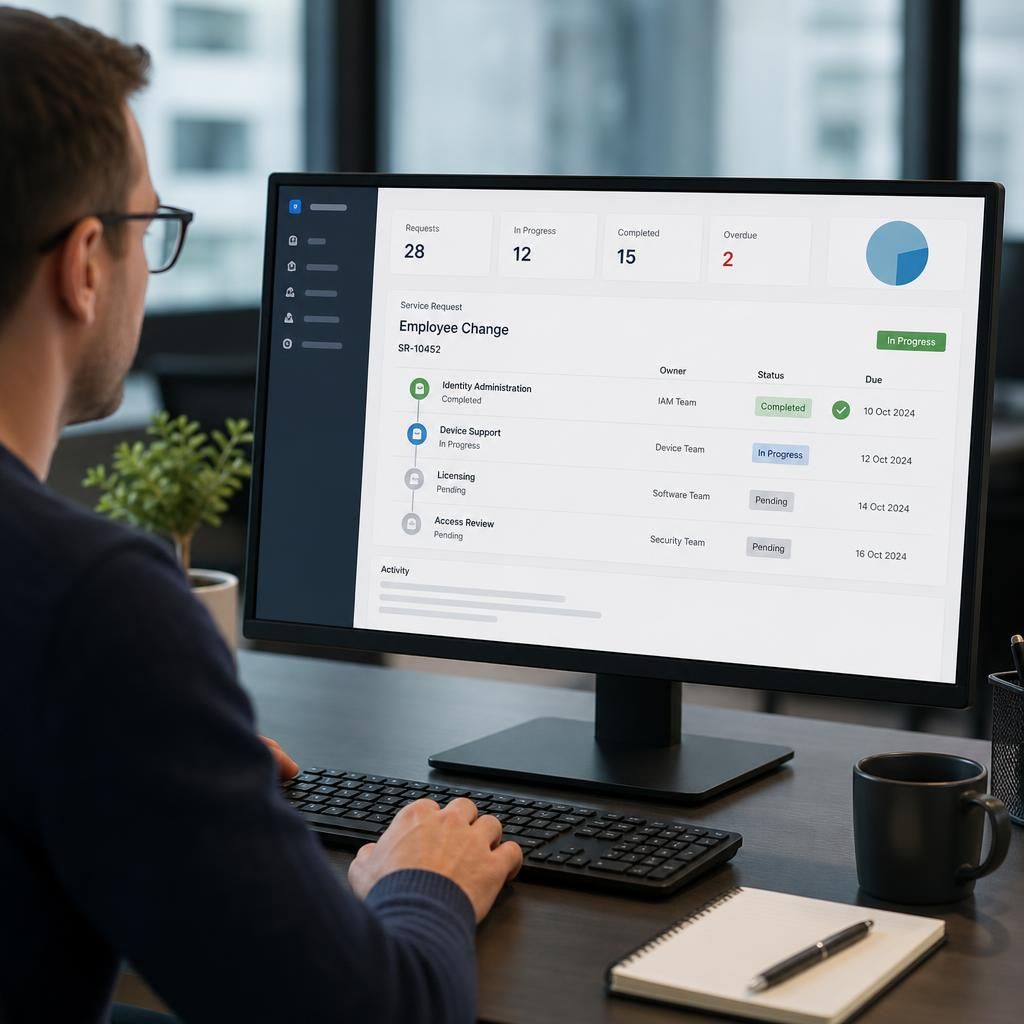
For requests involving several fulfilment activities, IT service management can use a parent request with linked tasks for each responsible team. This keeps related work together without requiring one technician to perform every step. For example, an employee change may involve identity administration, device support, licensing and access review. Each task can have its own owner and completion evidence, while the parent record provides a single view of overall progress.
This structure also makes dependencies visible. A later task should not begin until the prerequisite has been completed and checked, particularly where access, security or procurement is involved. If one task is blocked, the record should show the specific dependency rather than presenting the request as generally unresolved. Once all linked tasks are complete, the service desk can verify the combined outcome with the requester and retain a coherent record of the work.