
What is the difference between a firewall and an intrusion prevention system?
A firewall controls which network traffic is allowed to enter or leave, based on defined rules such as addresses, ports and protocols. An intrusion prevention system (IPS) analyses permitted traffic for suspicious patterns or malicious activity and can automatically block or disrupt detected threats, so an IPS typically complements rather than replaces a firewall.
A firewall and an intrusion prevention system (IPS) serve different security functions: the firewall enforces a communications policy, while the IPS looks for attack techniques within network activity and takes action against them. They are therefore complementary controls, although many modern network security appliances combine both capabilities in one platform.
What a firewall does
A firewall creates a boundary between networks or security zones and applies an administrator-defined policy to connections crossing that boundary. Its decisions may consider source and destination addresses, ports, protocols, connection state, user identity, application type and other contextual information, depending on the firewall’s capabilities.
This makes a firewall particularly useful for controlling exposure. For example, it can restrict access to an internal server, prevent unnecessary outbound connections, separate staff devices from sensitive systems and limit communication between different parts of a business network. A firewall can also provide network address translation, virtual private network functions and logging, although these features do not by themselves make it an IPS.
What an IPS does
An IPS examines network activity for indicators associated with attacks, such as exploit attempts, malicious payloads, protocol abuse, command-and-control traffic or suspicious sequences of behaviour. When its detection criteria are met, it can take preventative action by dropping traffic, terminating a connection, blocking an address or applying another configured response.
Unlike a basic access rule, an IPS decision can depend on the content and behaviour of a session. A connection to an authorised service may still be blocked if the traffic attempts to exploit a vulnerability or carry out an unauthorised action. IPS detection commonly uses signatures, reputation data, protocol analysis and behavioural or anomaly-based techniques. Each approach has different strengths, and detection quality depends on suitable updates, accurate configuration and the context in which the system is deployed.
Key differences between a firewall and an IPS
- Primary purpose: a firewall controls permitted communications; an IPS identifies and disrupts hostile or suspicious activity.
- Decision basis: firewalls generally enforce access and segmentation rules, whereas IPS tools inspect traffic characteristics, payloads and patterns associated with attacks.
- Position in the network: a firewall commonly sits at a boundary between networks, while an IPS is normally placed inline on a traffic path so that it can block activity before it reaches its destination.
- Response to unknown activity: a firewall may allow a connection because it matches an approved rule, while an IPS can still examine that connection for evidence of exploitation.
- Operational risk: an incorrect firewall rule can expose a service or prevent legitimate access; an over-sensitive IPS can interrupt valid traffic through false positives.
The distinction is not absolute. Some firewalls inspect applications and content, and some IPS platforms apply access-control decisions. The product description alone is therefore not enough to establish what protection is enabled. A business should check whether IPS inspection is licensed, configured, operating inline and applied to the relevant interfaces and traffic flows.
Firewall, IDS and IPS compared
An intrusion detection system (IDS) is related to an IPS but normally operates in a monitoring mode. It produces alerts about suspected attacks without automatically blocking the traffic. This can be useful when an organisation needs visibility, wants to validate detection rules or must avoid placing a new control directly in the path of production traffic.
An IPS is designed to prevent or interrupt detected activity, so it requires more careful tuning. Blocking decisions should account for the importance of the affected system, the confidence of the detection and the consequences of disrupting a legitimate connection. Alert-only, detection and prevention modes may be used at different stages of deployment.
Encrypted traffic and inspection limits
Encryption can limit what either control can see. A firewall may be able to identify the destination and connection metadata without seeing the contents of an encrypted session, but an IPS may not be able to inspect the payload for an attack unless traffic is decrypted for inspection. TLS inspection can address this limitation, but it introduces certificate management, privacy, compatibility and processing considerations. It should be designed deliberately rather than enabled indiscriminately.
Inspection also has limits where traffic uses unsupported protocols, custom applications, compression, tunnelling or evasive techniques. Security teams should identify which traffic is inspected, which is excluded and how those exclusions are reviewed.
Do businesses need both?
For most business networks, the practical choice is not firewall versus IPS. A firewall provides the access-control and segmentation foundation, while IPS capability adds a further layer that can detect and disrupt attacks that pass an allowed connection. The appropriate design depends on the network layout, internet-facing services, remote access arrangements, cloud connections, sensitive systems and the organisation’s ability to review alerts and investigate blocked events.
A combined next-generation firewall may provide both functions, but the features still need to be enabled and maintained. A separate IPS may be appropriate where traffic volumes, network architecture or inspection requirements justify a dedicated platform. In either case, the control should be supported by documented rules, current threat intelligence, tested changes, useful logging and a process for handling false positives.
How to assess the protection in place
- Confirm which devices provide firewall enforcement and which provide IPS inspection.
- Review whether prevention is active or whether the system is operating in alert-only mode.
- Check which network segments, applications and encrypted sessions are covered.
- Examine blocked events and high-severity alerts to confirm that detections are being reviewed.
- Verify that rules, signatures, reputation feeds and software are maintained appropriately.
- Test changes in a controlled manner so that legitimate business traffic is not unnecessarily interrupted.
In summary, a firewall determines whether communications should be permitted under the network security policy, while an IPS examines relevant activity for signs of attack and can prevent detected threats. A robust design uses each control for its intended purpose and verifies that the advertised IPS function is genuinely enabled, correctly positioned and monitored.
The practical difference between a firewall and an intrusion prevention system is also determined by where each control sits in the traffic path. A security appliance can contain IPS functionality, but that functionality cannot protect traffic that does not pass through the relevant inspection point.
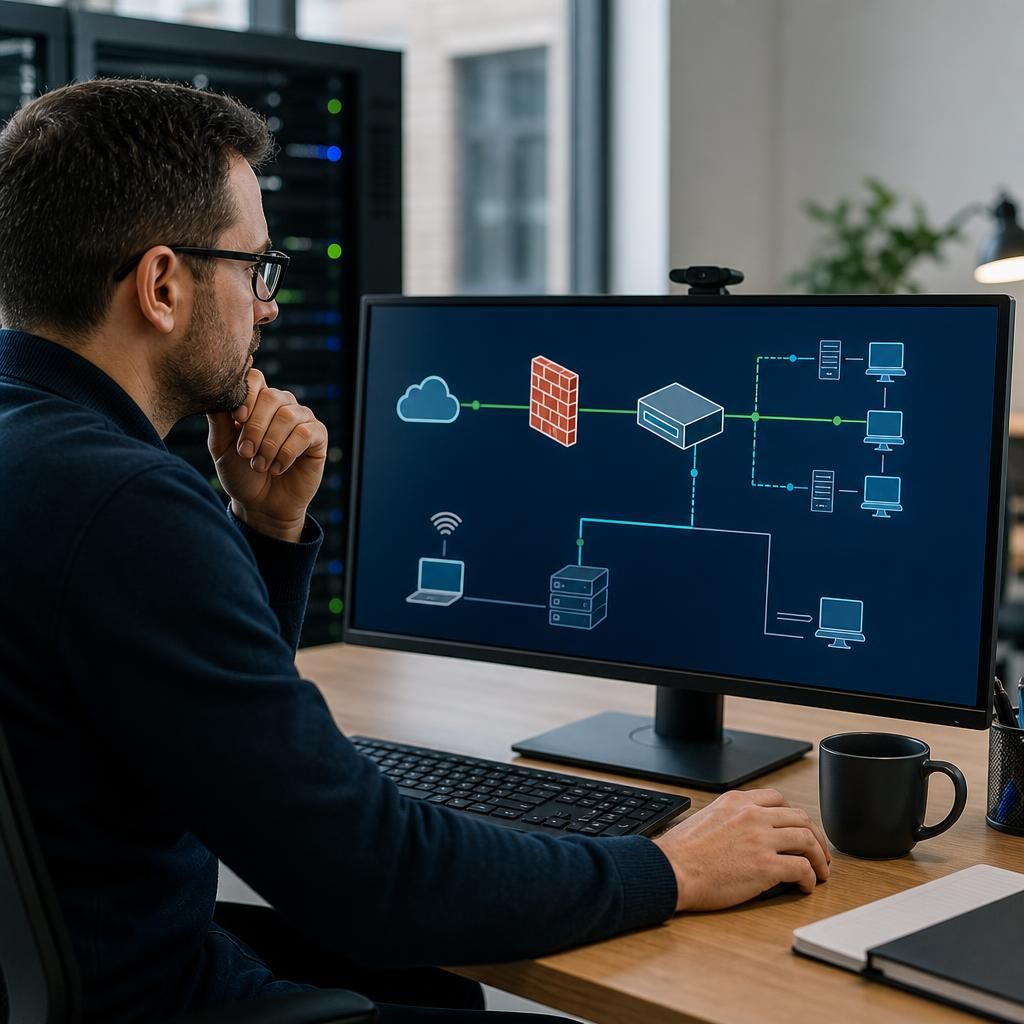
When reviewing a network diagram, trace each important connection from its source to its destination. Check whether the traffic crosses the firewall, whether it reaches the IPS inspection stage, and what happens if the inspection function is unavailable or bypassed. This is particularly important for internal connections between network segments, cloud environments and remote-access pathways, which may follow different routes from ordinary internet traffic.
- Internet traffic may cross the perimeter firewall and IPS before reaching an internal service.
- Traffic between internal systems may need separate segmentation and inspection controls.
- Cloud or remote-access connections may enter through a different gateway and require separate policy coverage.
- A documented traffic path makes it easier to identify connections that are controlled by access rules but not examined for attack patterns.
This distinction prevents an organisation from assuming that one visible security appliance protects every route. Effective protection depends on matching each traffic flow to the control that is intended to govern or inspect it.
Review your firewall and IPS coverage
Ask S2 Technology Group to review whether your firewall and IPS controls are correctly configured for your business’s network and security requirements. Use the findings to identify any gaps in inspection, prevention or monitoring before deciding whether changes are needed.