
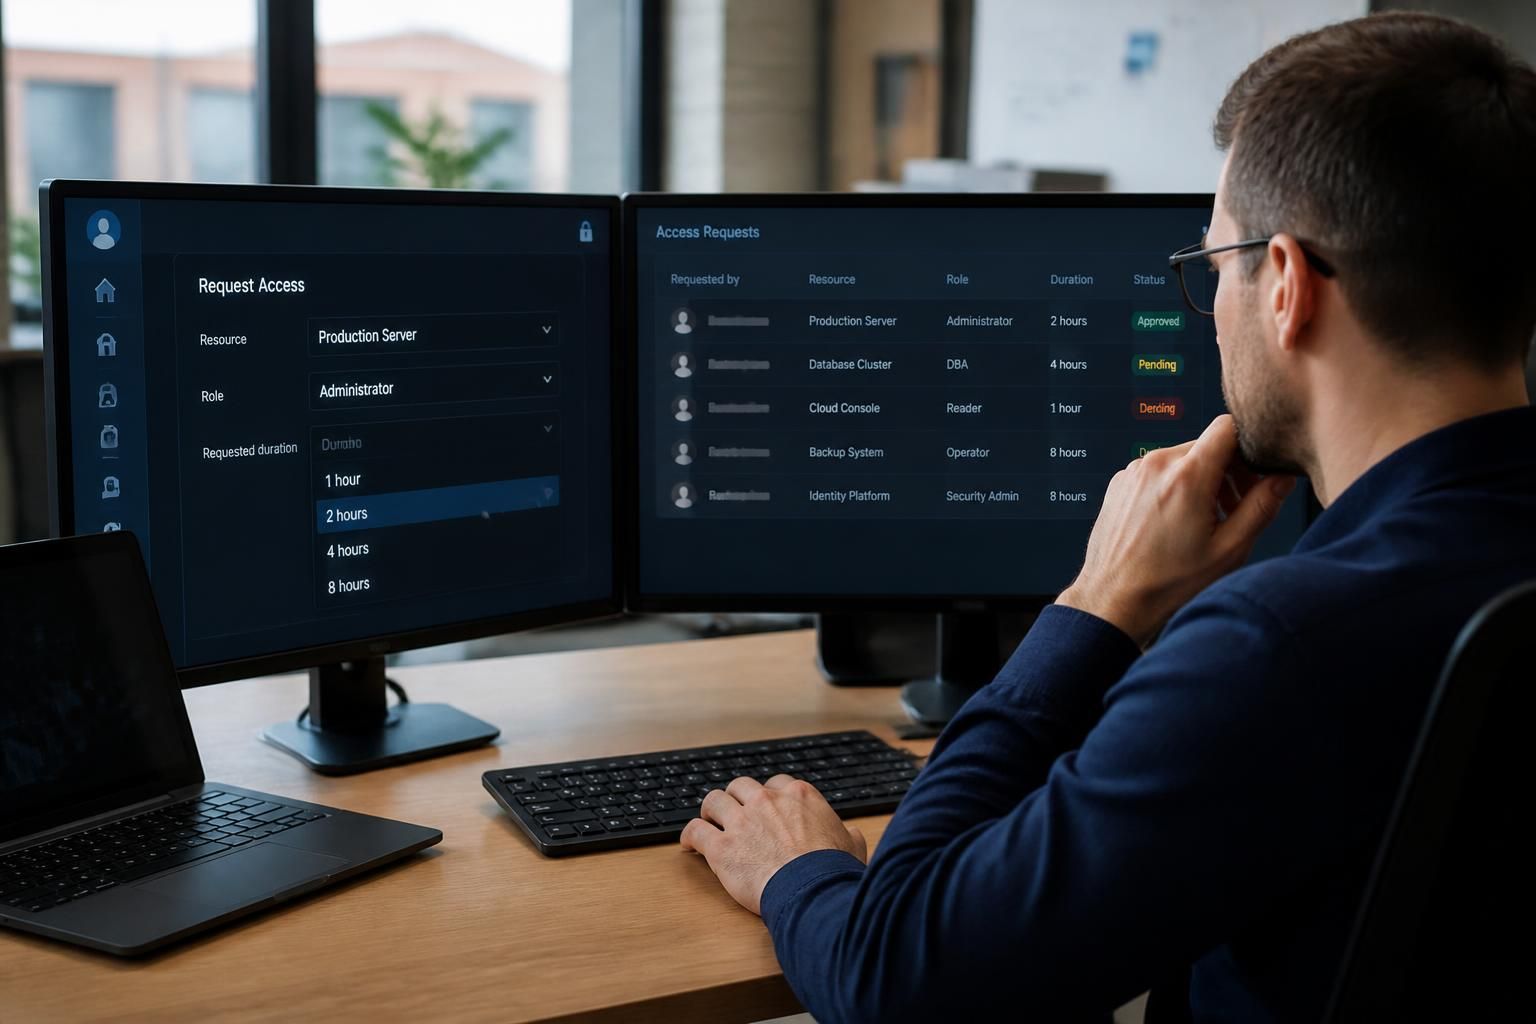
How does just-in-time access reduce identity security risk?
Just-in-time access reduces identity security risk by granting privileged permissions only for an approved task and defined period, rather than leaving them permanently available. This limits standing privilege, narrows the opportunity for misuse or account compromise, and creates a clearer record of elevated access.
Just-in-time access reduces identity security risk by changing privileged access from a persistent entitlement into a controlled, reviewable security decision. The important reduction is not simply that fewer people have administrator rights; it is that those rights are harder to exploit, easier to constrain and easier to investigate when something unusual occurs.
It reduces the value of compromised accounts
A stolen password, session token or privileged identity can give an attacker significant control if elevated permissions remain available indefinitely. Just-in-time controls reduce the usefulness of that identity by separating ordinary access from administrative capability. An attacker who compromises a standard user account may still need to pass additional checks, obtain an approved elevation and operate within defined restrictions before reaching sensitive systems.
This creates an additional control layer between account compromise and high-impact activity. It is particularly relevant where administrators can manage cloud resources, identity platforms, endpoint security, servers, financial systems or production environments.
It limits the blast radius of mistakes and misuse
Permanent administrator rights increase the consequences of accidental changes, unsafe commands and deliberate misuse. Just-in-time access can restrict elevation to a specific system, role, resource group or administrative function. A person carrying out a routine task does not necessarily need broad control across the entire environment.
Useful restrictions may include:
- allowing access to one target system rather than a whole network;
- assigning a narrowly defined administrative role;
- requiring a documented reason for the request;
- requiring approval from an appropriate manager or system owner;
- requiring stronger authentication before elevation;
- preventing access from an unmanaged or unsuitable device; and
- recording the identity, purpose, target and activity associated with the request.
These controls help contain the impact if an authorised action is incorrect or an elevated session is abused.
It improves the privilege lifecycle
Traditional access management often concentrates on granting and removing user accounts. Privileged access needs more precise lifecycle management. A just-in-time process should define how a request is made, who can approve it, what conditions apply, how access is withdrawn and what happens if the task is not completed as expected.
A sound lifecycle normally includes:
- Eligibility: the user may be permitted to request a role without holding that role continuously.
- Request: the user provides a business reason and identifies the required resource or task.
- Decision: an authorised approver, policy or combination of controls evaluates the request.
- Elevation: the system applies the approved permissions and any session restrictions.
- Monitoring: administrative activity is captured and assessed for anomalies.
- Removal: the elevated entitlement is withdrawn automatically or through a controlled revocation process.
- Review: access records are examined to confirm that the privilege was appropriate and used as intended.
This lifecycle prevents access decisions from becoming permanent simply because nobody remembers to remove them later.
It supports stronger separation between normal and privileged activity
Administrators often need a standard identity for email, collaboration and routine work, plus a separate pathway for high-risk operations. Just-in-time access supports this separation by making elevation deliberate rather than allowing everyday activity to take place under an administrator context.
This reduces the chance that a malicious link, unsafe attachment or compromised browser session will automatically inherit extensive permissions. It also makes it easier to distinguish ordinary business activity from privileged activity in audit records.
It creates more useful evidence
Access logs are more valuable when they explain why elevated access existed, who authorised it, which resource was involved and what actions followed. A just-in-time system can link the request, approval, authentication event, session and administrative changes into a single record.
Security teams can use this evidence to investigate suspicious activity, validate internal policies and support compliance reviews. The record should show more than a successful login. It should provide enough context to determine whether the access was expected, appropriate and limited to the approved purpose.
Logging alone does not make access secure. Records need suitable retention, protection against unauthorised alteration and a process for reviewing significant events. Alerts may also be appropriate for unusual elevation requests, repeated denials, access to sensitive resources or activity outside an established pattern.
It works best with risk-based controls
Not every privileged request presents the same level of risk. Access to a test environment may require a different process from access to identity infrastructure or production data. Policies can take account of the target resource, user role, device condition, network context, authentication strength and sensitivity of the requested operation.
For example, a lower-risk request might be approved through an established policy, while a request to change authentication settings could require named approval, stronger authentication and additional monitoring. The objective is to apply proportionate controls without allowing convenience to override the importance of the resource.
It is not a complete control on its own
Just-in-time access does not remove all identity risk. If approval is poorly designed, an attacker may manipulate the request process. If an administrator’s authentication method is compromised, elevation may still be obtained. Excessive roles, weak device controls, unmonitored sessions and shared accounts can also undermine the model.
Implementation should therefore be combined with individual identities, multi-factor authentication, least-privilege role design, secure administration devices, conditional access policies, endpoint protection, session monitoring and tested account recovery procedures. Approval should be based on the sensitivity of the action rather than treated as a routine formality.
Organisations should also identify exceptions carefully. Emergency access may be necessary, but it should use a separately governed process with clear authorisation, strong logging and retrospective review. Service accounts and automated workloads require equivalent attention because they may not be able to complete an interactive request in the same way as a person.
How to assess whether it is reducing risk
Useful measures focus on the quality of privileged access, not merely the number of requests. Review whether:
- standing administrator permissions are being removed where they are not required;
- requests identify a valid business purpose and appropriate target;
- approvers have sufficient independence and authority;
- elevated permissions are limited to the required role;
- access is removed reliably after the approved activity;
- privileged actions can be connected to an individual identity;
- unusual requests and failed elevation attempts are investigated; and
- access policies are updated when systems, responsibilities or risks change.
When these conditions are met, just-in-time access provides a practical way to reduce persistent privilege, constrain administrative actions and improve accountability across identity infrastructure. Its effectiveness depends on the surrounding governance, authentication and monitoring controls, but it is a strong foundation for reducing the opportunity and impact of privileged identity compromise.
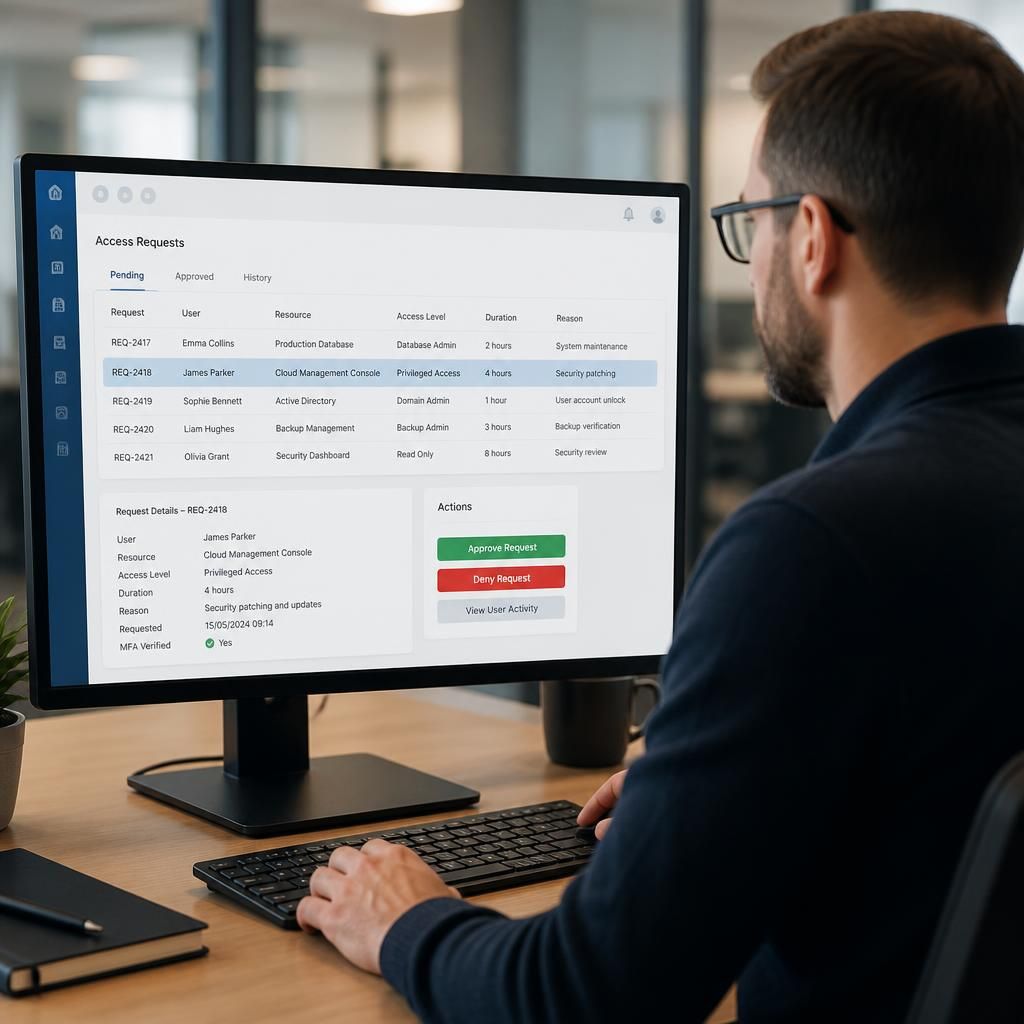
Just-in-time access reduces identity security risk most effectively when expiry applies to the elevated session itself, not only to the permission request. When the approved period ends, the identity management system should remove the role and invalidate associated sessions, tokens or credentials so that administrative capability cannot continue through an already established connection.
This distinction matters because removing a role does not always terminate access that has already been issued. Organisations should confirm how each platform handles session expiry, token renewal, cached credentials and active remote connections. Suitable controls may include:
- setting a maximum elevation duration based on the sensitivity of the task;
- preventing users from extending access without a new authorisation decision;
- revoking active sessions when approval is withdrawn or the time limit expires;
- requiring reauthentication before a privileged session can continue; and
- checking that connected tools do not retain administrative credentials after the task ends.
Testing should include an elevation that is allowed to expire and an access request that is revoked before completion. The results should show whether permissions, sessions and reusable credentials are actually invalidated. This makes the time limit a technical security control rather than an administrative entry in an access record.