What happens after a cyber risk assessment?
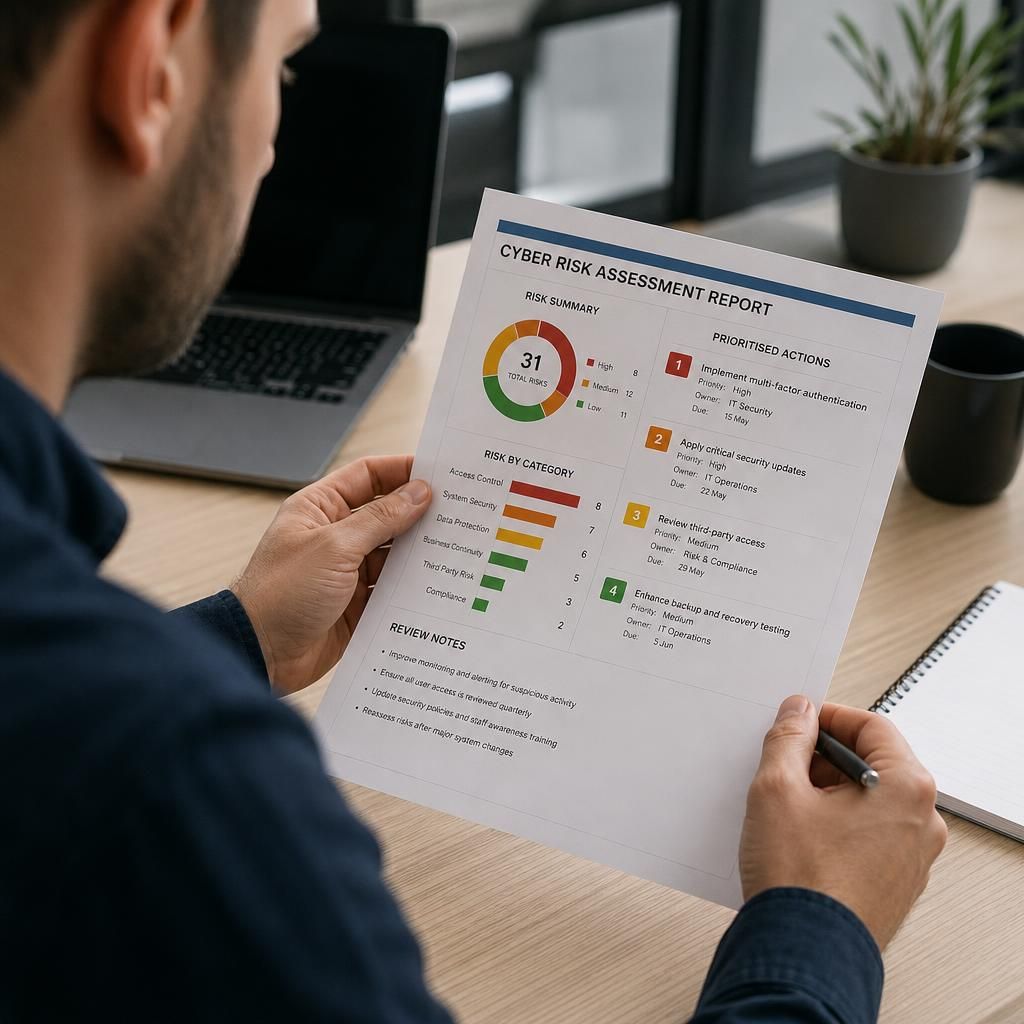
After a cyber risk assessment, the findings are documented and risks are prioritised according to their potential impact and likelihood. The organisation then agrees an action plan, addresses the most important weaknesses, records any accepted residual risk and reviews progress as its systems and threats change.
Once a cyber risk assessment is complete, its findings need to be converted into controlled improvements. The next stage is to confirm what the evidence means, assign responsibility for each required change, implement measures in a sensible order and verify that the changes reduce the identified risk in practice.
First, the findings should be validated. The organisation should check that the assessment reflects its current systems, users, suppliers and operating arrangements. Any inaccurate asset details, misunderstood controls or changes made during the assessment should be corrected before decisions are based on the report. This prevents time and resources being directed towards risks that no longer exist, while ensuring genuine weaknesses are not overlooked.
The results should then be discussed with the people who own the affected services and processes. A technical issue may require action from IT, while a weakness involving payment procedures, staff access, data handling or supplier management may also need involvement from business managers, finance, human resources or senior leadership. Clear ownership matters because a risk cannot be properly managed if responsibility remains with an undefined team.
Typical follow-up actions may include:
- removing unnecessary user, administrator or supplier access;
- applying security updates and replacing unsupported software or equipment;
- strengthening authentication and account management controls;
- separating important systems or restricting communication between them;
- improving backup protection and testing whether data can be restored;
- updating policies, procedures and staff guidance;
- improving logging, alerting and the investigation of suspicious activity; and
- reviewing contracts and security requirements for relevant third parties.
Remediation should be managed as a controlled change rather than a series of isolated fixes. Each action should have a defined scope, owner, dependency and target point for completion. Changes to business-critical systems should be tested, documented and scheduled so that improving security does not introduce avoidable operational problems. Where a weakness cannot be removed immediately, interim safeguards may reduce exposure while a longer-term solution is prepared.
After an action is completed, it should be verified rather than simply marked as closed. Verification might involve checking configuration settings, reviewing access records, examining audit logs, testing backup restoration, confirming that an account has been removed or carrying out a focused technical test. The evidence should show what was changed, when it was changed, who approved it and how its effectiveness was checked.
Some findings also require organisational changes. Staff may need targeted guidance on handling sensitive information, recognising suspicious requests or reporting incidents. Suppliers may need to provide evidence of their own controls. Contracts, onboarding processes and leaver procedures may need revision where they contribute to the risk. These measures address the people and process conditions that technical controls alone cannot resolve.
The assessment may also expose gaps in incident preparation. The organisation should confirm how a suspected compromise would be reported, who can make containment decisions, which systems and contacts are important, and how records would be preserved. If the assessment identified weaknesses in detection or response, those capabilities should be improved and exercised in a controlled way.
Management should receive a clear view of the remaining exposure, not just a list of technical defects. Useful reporting explains which risks remain, what controls now address them, what limitations still apply and what decisions require approval. This gives decision-makers enough context to determine whether further investment, a change in business process or formal acceptance of a remaining risk is appropriate.
Finally, the assessment should become part of the organisation’s security evidence rather than being filed away as a one-off report. Action records, verification results, exceptions and relevant approvals should be retained so that future reviews can measure what has changed. A managed IT partner such as S2 Technology Group can support this process by helping interpret technical findings, coordinate remediation and maintain the security controls that underpin the organisation’s wider risk management.
After a cyber risk assessment, its findings should influence future technology and business changes, not only existing weaknesses. New systems, suppliers, applications and processes can reintroduce the same risks unless security requirements are included before they are approved.
Organisations can use the assessment to strengthen change and procurement decisions by:
- requiring appropriate authentication, access control and logging in new systems;
- checking how proposed suppliers protect information and support incident management;
- reviewing whether new technology increases reliance on a critical service or supplier;
- confirming that backup, recovery and data-handling requirements are included in project plans; and
- requiring a security review before significant changes are introduced into production.
This approach turns the assessment into a reference point for future decisions. It helps prevent the organisation from resolving a known weakness while approving a later change that creates a similar exposure.