
What firewall features matter most for a small business network?
The most important firewall features for a small business are stateful traffic inspection, intrusion prevention, secure remote access, web and application controls, network segmentation, centralised management and clear security logging. Choose a firewall that can handle current and anticipated traffic without unnecessary complexity, while supporting strong authentication, regular rule reviews and reliable updates.
The firewall features that matter most to a small business are the ones that provide effective protection without creating unnecessary administrative work or becoming a bottleneck for legitimate traffic. In practice, selection should focus not only on the security functions a firewall advertises, but also on its capacity, resilience, manageability, compatibility and ability to produce useful evidence when something goes wrong.
Capacity and performance should be assessed using real operating conditions. A firewall’s headline throughput figure may not reflect performance when several security services are enabled. Encrypted traffic inspection, malware analysis, application control and detailed logging can all require additional processing. Assess the expected internet connection speed, number of users, site-to-site traffic, cloud applications, voice or video services and anticipated growth. The firewall should retain sufficient processing capacity when protection features are active, rather than being sized only for today’s basic routing requirements.
Look at the vendor’s performance information carefully and identify whether figures relate to ordinary firewall throughput or to traffic with security inspection enabled. Also check the number of concurrent connections and new connections per second. These measures are relevant to busy networks and help identify equipment that could struggle during periods of increased demand.
Resilience is important even for a small network. A firewall is normally positioned at a critical point between the business and external networks, so a failure can affect internet access, cloud systems and communications. Depending on the organisation’s dependency on connectivity, useful resilience features may include:
- Automatic configuration backup and straightforward restoration.
- Configuration versioning or rollback after an unsuccessful change.
- High-availability support using a secondary appliance or service.
- Separate power arrangements where a single power failure would create unacceptable disruption.
- Clear handling of failed updates, expired certificates and unavailable security services.
Not every small business needs duplicate equipment, but the decision should be based on operational impact rather than the organisation’s headcount alone. A documented recovery method is valuable even where a second firewall is not justified.
Policy control should be precise enough to reflect how the business actually works. Useful controls include rules based on users, devices, services, destinations, schedules and network zones. This allows an administrator to permit a required business function without broadly allowing an entire category of traffic. The firewall should also support explicit deny rules, rule descriptions, ownership information and an orderly way to identify rules that are unused, duplicated or shadowed by an earlier rule.
Identity-aware policies can be useful where access should depend on a person’s role rather than only on an IP address. Device context is also relevant: a managed company computer may reasonably receive different access from an unknown or non-compliant device. These controls should complement, not replace, strong account security and sound endpoint management.
DNS and content-level protection can add an important layer of control. A firewall may be able to block known malicious domains, prevent access to inappropriate categories and identify command-and-control destinations before a connection is established. Check how threat intelligence is updated, how exceptions are recorded and whether administrators can distinguish a deliberate block from a technical failure. Filtering should be tested against the business’s required services so that security controls do not silently interfere with legitimate suppliers, cloud platforms or software updates.
Configuration management is a security feature, not merely an administrative convenience. The platform should support named administrator accounts, role-based permissions, multi-factor authentication and a record of who changed what and when. A small business should not need to share one powerful administrator account among several people. The ability to export a readable configuration, compare revisions and approve changes through a defined process makes troubleshooting and independent review easier.
Updates should be available through a controlled process, with release information that explains security fixes, functional changes and known limitations. It should be possible to schedule or stage an update, verify that it completed successfully and recover if the change causes a problem. The firewall should also continue applying existing policy if a cloud management portal or subscription service becomes temporarily unavailable, subject to the specific design of the platform.
Interoperability prevents the firewall becoming an isolated device. Check support for the network’s required connection types, VLANs, IPv6, site-to-site tunnels, directory services, certificate services and monitoring tools. If the business uses more than one site or relies heavily on cloud applications, confirm that the firewall can exchange routes and enforce consistent policy without introducing manual workarounds. Compatibility should be tested before purchase, especially where older equipment, specialist systems or managed connectivity services are involved.
Useful integration should not mean excessive dependence on a proprietary ecosystem. Ask whether logs can be exported in standard formats, whether alerts can be sent to an existing monitoring or security platform, and whether the organisation can retrieve its configuration and records if its management arrangement changes.
Ease of safe administration is one of the strongest indicators of practical value. A firewall with many advanced options may be unsuitable if routine changes are difficult to understand or easy to apply incorrectly. Look for clear policy ordering, validation before publishing, warnings about conflicts, a safe test or preview function and the ability to make a change with a defined rollback plan. Good documentation should explain not only what a setting does, but also its security implications.
Before choosing a model, document the business’s traffic flows, critical applications, connectivity dependencies, administrator responsibilities and recovery requirements. Then score candidate firewalls against those needs rather than selecting the longest feature list. S2 Technology Group can help small and medium-sized organisations assess these practical requirements as part of a wider approach to managed IT and cyber security, ensuring that the chosen firewall is proportionate to the network it must protect.
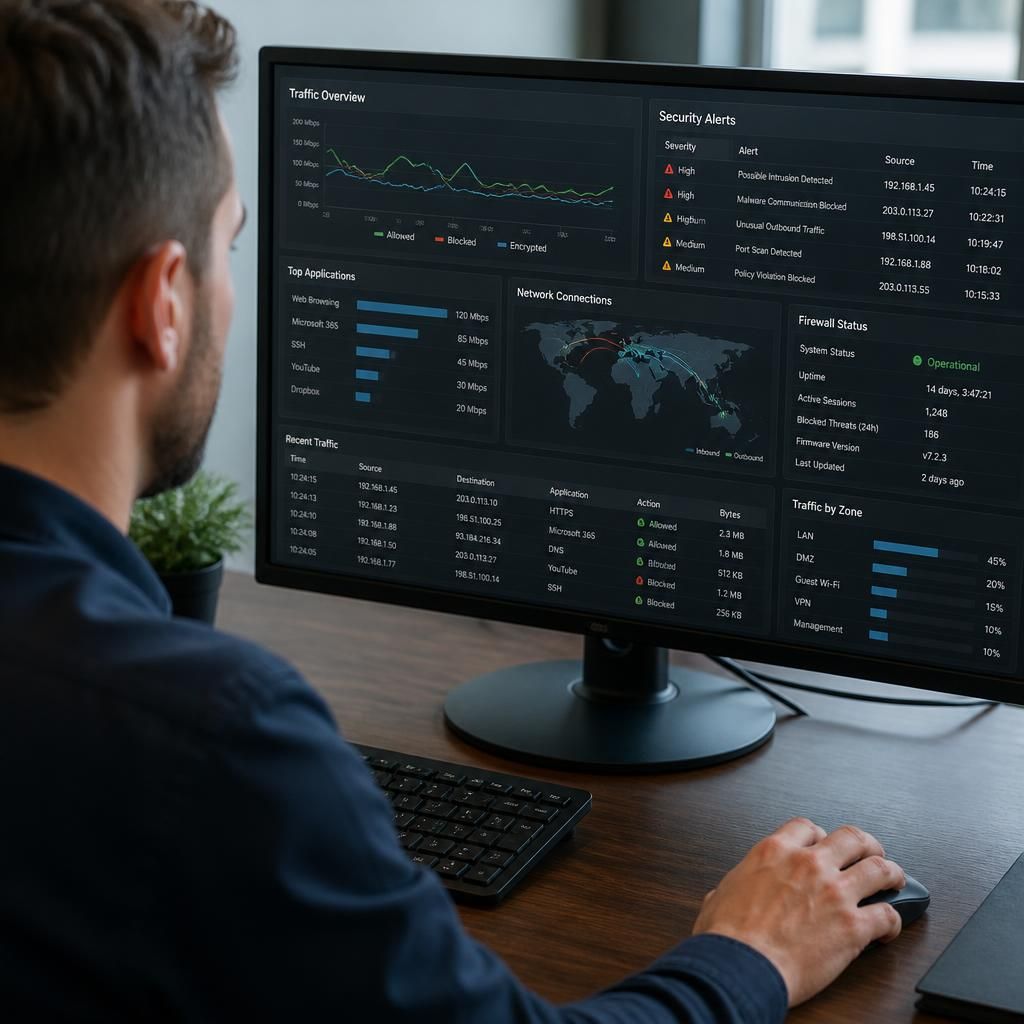
Network segmentation is a valuable firewall feature because it limits which parts of a business network can communicate with one another. Separate zones can be created for staff devices, servers, guest wireless access, voice systems and network management, with traffic between them permitted only where there is a documented business requirement.
Look for controls that make these boundaries clear and maintainable, such as zone-based policies, explicit inter-zone rules and logging of blocked cross-network attempts. Segmentation is most effective when a compromised device cannot freely reach critical systems, while authorised services continue to work through narrowly defined rules. The design should reflect the organisation’s actual systems rather than creating so many zones that administration becomes difficult.
Assess which firewall features your business needs
Ask S2 Technology Group to assess your network’s firewall requirements and identify which features are proportionate to your organisation’s risks, traffic and operational needs. You can then make an informed decision without selecting unnecessary complexity.