
What should Intune training teach about compliance policy exceptions?
Intune training should teach that compliance policy exceptions temporarily or selectively exclude users, devices or conditions from standard compliance requirements. It should cover when exceptions are justified, how to document approval and risk, how to apply them narrowly, and how to review or remove them so they do not weaken security controls.
Intune training should teach that compliance policy exceptions are controlled departures from a device or user’s normal compliance requirements, not a general way to bypass security. A sound training course should explain how to distinguish a genuine operational need from an unmanaged risk, select the least permissive control, and ensure that any exception remains visible to administrators and security teams.
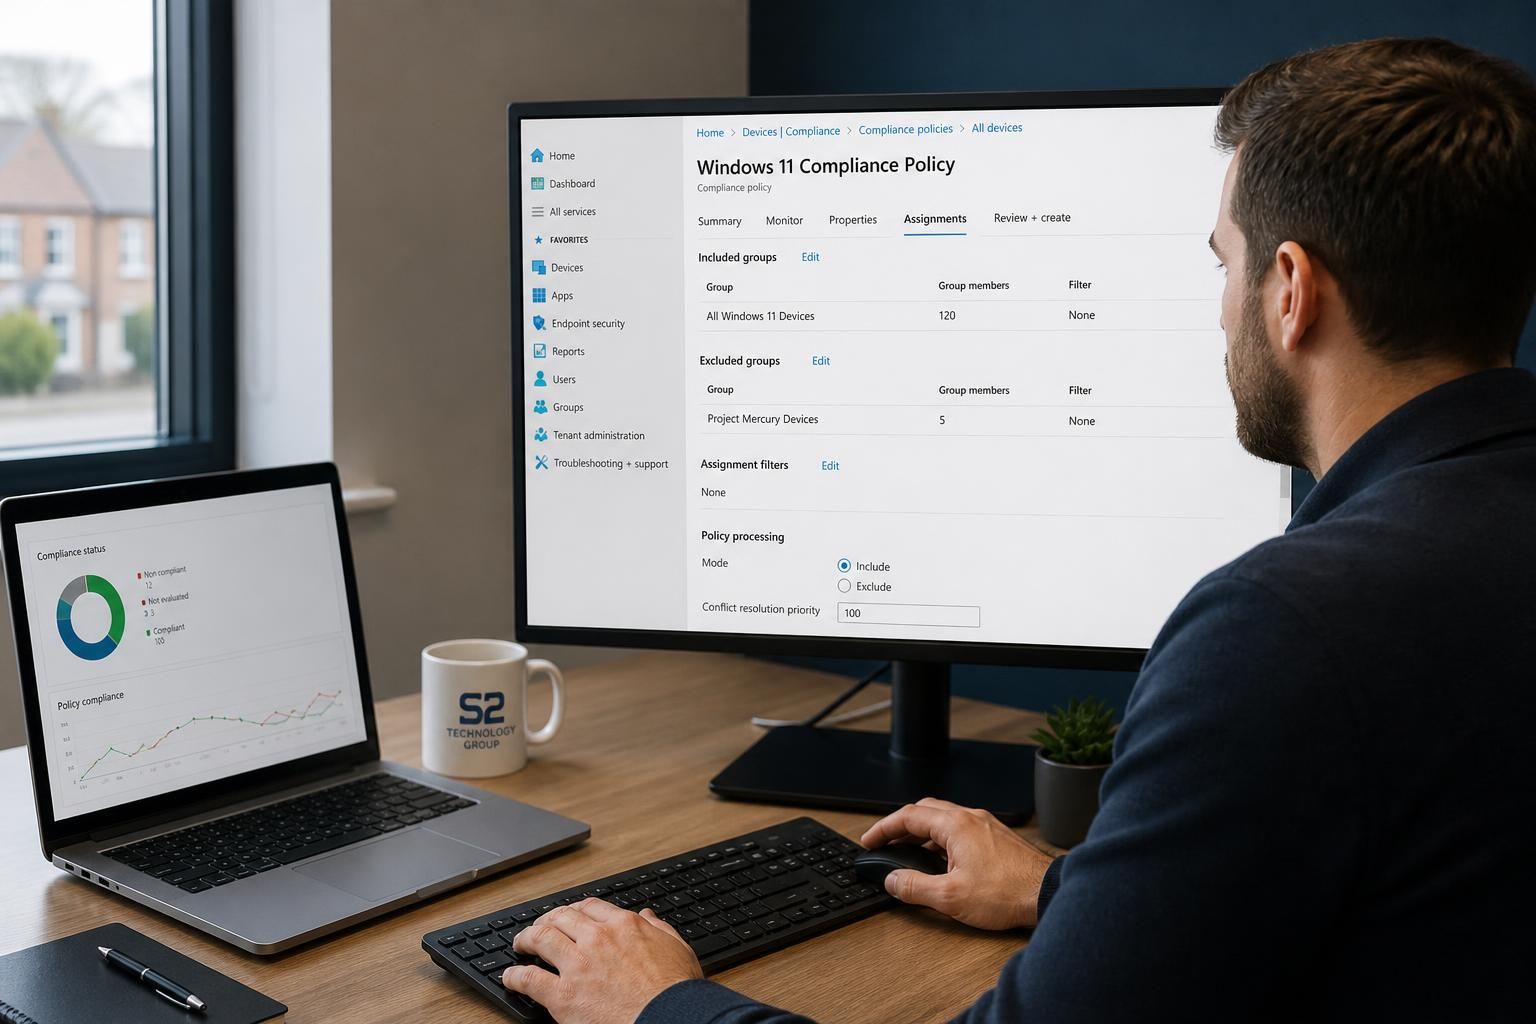
Start by clarifying what counts as an exception. In Intune, an exception may be represented by how a policy is assigned rather than by a single exception setting. Relevant mechanisms can include carefully scoped user or device groups, assignment filters, platform applicability, and different compliance policies for clearly defined populations. Training should explain that these mechanisms change who receives a policy; they do not make an otherwise non-compliant device secure.
The course should also distinguish an exception from a grace period or an action for non-compliance. A grace period gives a user time to correct a condition before stronger enforcement applies. Actions for non-compliance determine what happens when requirements are not met, such as notifying the user or marking the device non-compliant. Neither should be described as a permanent exemption. This distinction matters because a delayed response and an excluded device create different security and audit conditions.
Valid reasons need defined boundaries. Common examples may include a device supporting specialist software that cannot yet meet a new requirement, a staged rollout of a policy, or a temporary technical dependency during remediation. Training should require the administrator to identify the affected user, device, policy requirement and business reason. Broad statements such as a department needs access or the device is important are not sufficient justification on their own.
Exception design should follow the principle of least privilege. A course should show how to limit the scope by using the smallest appropriate group, specific device characteristics or a defined platform, rather than excluding an entire organisation. It should also cover the difference between excluding a device from one requirement and excluding it from the whole compliance policy. Where possible, the narrower option preserves more of the organisation’s security baseline.
Training should cover the interaction between compliance policies and access controls. Conditional Access can use a device’s compliance state when deciding whether access is allowed, but an exception in a compliance assignment can result in the device not being evaluated against that requirement. Administrators therefore need to understand whether an excluded device will still satisfy the access condition, be treated as non-compliant, or be handled by a separate policy. Testing should use representative accounts and devices before a change is applied broadly.
Every exception should have an audit record. The record should contain:
- the policy requirement being varied;
- the users, devices or group affected;
- the business owner and technical approver;
- the reason the normal requirement cannot currently be met;
- the risks introduced and the compensating safeguards;
- the date the exception was approved;
- the review point or expiry condition; and
- the evidence that the change was tested.
Compensating safeguards should be proportionate to the exposure. Depending on the situation, these might include restricting access to particular resources, requiring additional authentication, limiting the device to a managed application, separating a device from sensitive workloads, or prioritising remediation. These controls do not remove the underlying non-compliance, but they can reduce the consequences while a permanent correction is being developed.
A practical course should teach administrators to assess the exception from both the device and access perspectives. They should check the device’s ownership, platform, management state, encryption status, user identity and access needs, then review how the policy is evaluated in Intune reports. They should also confirm that group membership and assignment filters produce the intended result, because an overlapping assignment can cause a device to receive a different policy from the one expected.
Testing should take place in a controlled group before production deployment. Training should demonstrate how to verify policy assignment, review the device’s compliance result, check the resulting access decision and confirm that notifications are understandable to the user. The test should include both an in-scope device and a device intended to receive the exception. This helps identify accidental exclusions, conflicting policies and cases where the exception has no effect because another requirement still causes non-compliance.
Finally, Intune training should explain how to close an exception safely. The owner should confirm that the original condition has been corrected, remove the device or user from the special assignment, and verify that the standard policy is evaluated again. Administrators should retain the approval and test evidence while recording the closure. Exceptions that no longer have an owner, a valid reason or a clear end condition should be treated as governance failures rather than accepted parts of the compliance design.
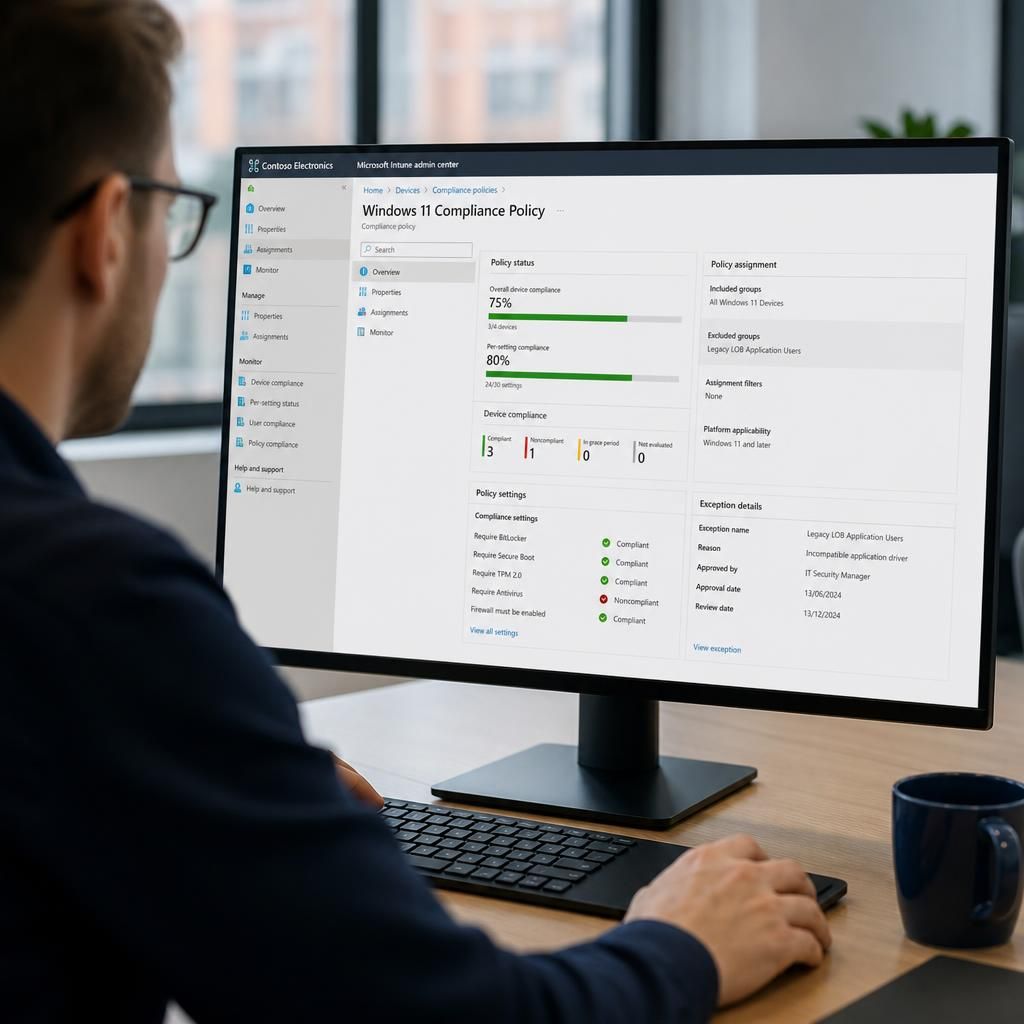
Intune training should teach that repeated exceptions may indicate a poorly designed compliance policy rather than a series of individual business needs. Before approving another exclusion, administrators should check whether the requirement is appropriate for the affected platform, ownership model or user group. If the same limitation affects a legitimate population, the better solution may be a separate policy with its own security baseline and governance, rather than an expanding list of exceptions.
This approach makes the difference between intentional policy design and accidental security gaps easier to identify. Training should encourage administrators to review exception patterns periodically, look for recurring causes such as incompatible configurations or unsupported workflows, and escalate systemic issues for remediation. An exception should remain a specific, explainable decision—not a substitute for correcting a policy that does not reflect the organisation’s operating environment.