How should multi-site businesses design connectivity between locations?
Multi-site businesses should design connectivity as one secure, centrally managed network, combining suitable links between offices with dependable access to cloud applications, shared systems and voice services. Start by mapping traffic, security and availability requirements at each location, then build in network segmentation, resilient connections and capacity for future sites and users.
Multi-site connectivity is the combination of wide area networking, internet access, routing, security and operational controls that allows separate business locations to function as one joined-up technology environment. A sound design should provide each site with the access it needs, direct traffic along an appropriate path, protect communication between locations and remain manageable as the organisation adds users, applications or premises.
Begin with the operating model. Decide which systems are hosted at a central office, in a data centre or in the cloud, and identify where each type of user needs to connect. A manufacturing site may depend on local systems and operational equipment, while a professional services office may generate most of its traffic through cloud platforms. These differences affect the type of connection, routing policy and local network equipment required at each location.
Classify applications by how they behave rather than treating all traffic equally. Voice and video are sensitive to delay, variation in delay and packet loss. Interactive cloud applications need consistent performance, whereas backups and large file transfers can often use less time-critical capacity. This classification supports sensible traffic prioritisation and prevents a single transfer from affecting every other service.
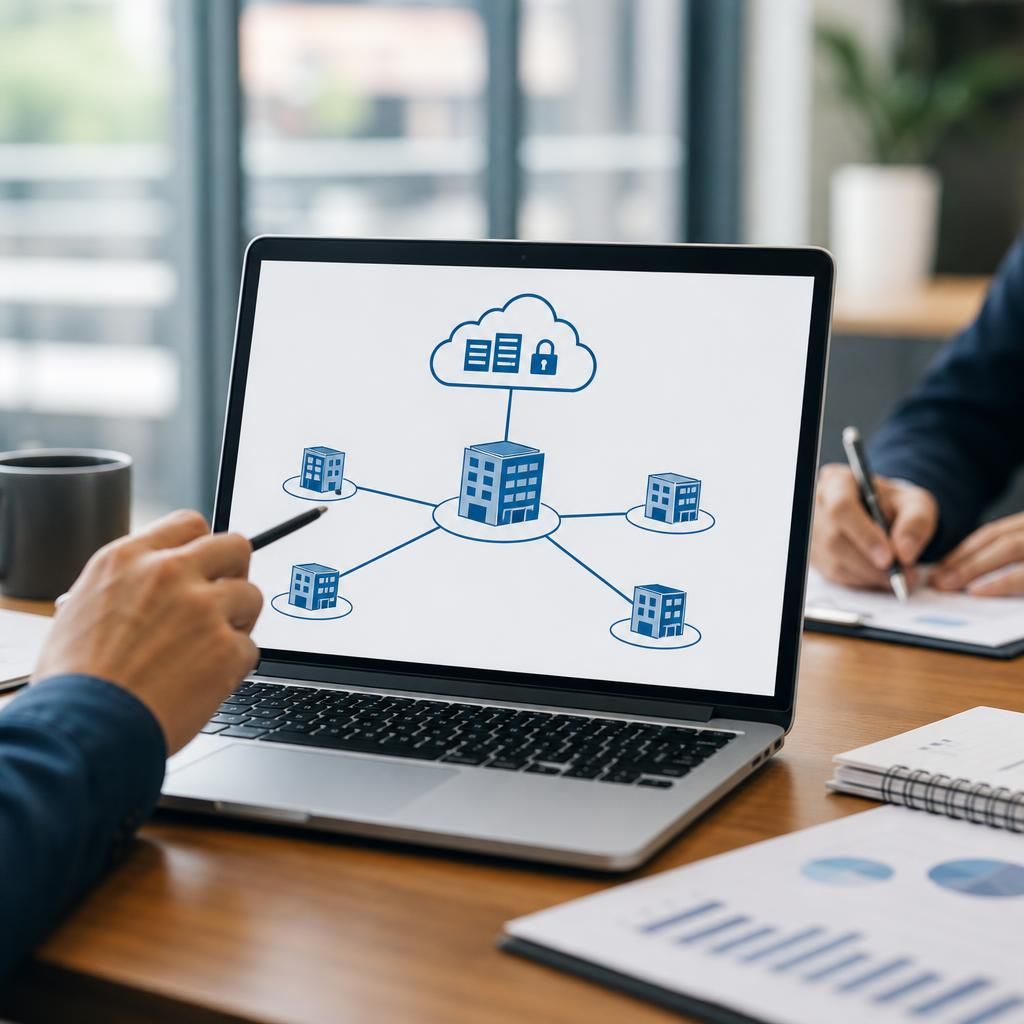
Choose an appropriate network topology. Common approaches include:
- Hub and spoke: branch traffic passes through a central site or security service. This can simplify control, but may create unnecessary detours when a branch needs to reach a cloud application or another branch.
- Full or partial mesh: selected locations communicate directly where the application or workflow justifies it. This can reduce latency, although it requires more careful routing and security administration.
- Internet-based overlay networking: encrypted tunnels or software-defined policies operate over available internet connections. This can provide consistent policy across varied sites, provided the underlying links and monitoring are suitable.
The right model is usually a combination rather than a single pattern. For example, branch-to-branch traffic may need a controlled route, while cloud-bound traffic can be sent directly through a security service at the nearest suitable location. Routing should follow the way the organisation works, not simply the physical location of its servers.
Separate local and wide area responsibilities. The local area network at each site should be designed for its own users, wireless devices, phones, printers, servers and operational equipment. The wide area network then joins the locations without making every local device visible everywhere else. Consistent addressing, documented subnets and central configuration make it easier to apply access rules and troubleshoot faults.
Use segmentation to limit the effect of a compromised account or device. User devices, servers, guest wireless access, voice systems, building controls and specialist equipment should not automatically share the same network. Access between segments should be based on a defined business requirement, with unnecessary east-west traffic blocked. Inter-site access should follow the same principle: a branch should reach only the systems and services it needs.
Design security into the connection paths. Firewalls should enforce policy at suitable boundaries, while encrypted tunnels protect traffic crossing untrusted networks. Administrative access should be separated from ordinary user traffic and protected with strong authentication. Central logging, configuration control and alerting help identify unusual connections, policy changes and repeated failures. Security policies should also account for temporary sites, home-based staff and third parties that require limited access to a particular service.
Cloud access deserves specific consideration. Backhauling every cloud session through one headquarters may concentrate risk and introduce avoidable delay. Direct local internet access can be more efficient, but each site then needs appropriate security inspection, filtering and consistent policy. Organisations should also confirm how identity, DNS, certificates and cloud access controls operate when a site loses its normal route.
Build resilience according to business impact. Not every location needs identical protection. A site that can continue using local processes may require a different arrangement from a warehouse, contact centre or production facility that depends on continuous connectivity. Consider diverse access technologies, separate physical routes, automatic failover and independent equipment where the consequences of an outage justify them. A second link is not genuinely independent if it shares the same duct, cabinet, provider infrastructure or power dependency as the first.
Failover should be tested under controlled conditions rather than assumed from a diagram. Check whether routing changes correctly, whether security policies remain in force, whether voice and cloud sessions recover acceptably, and whether staff know which services are affected. Document the expected behaviour and the steps for returning to the primary path.
Plan capacity from usage patterns. Estimate concurrent activity at each site, including staff, guests, cloud services, voice, video, backups and future devices. Review both download and upload demand, because file synchronisation, hosted desktops, video meetings and cloud backups can place substantial pressure on upstream capacity. Capacity planning should also consider whether traffic is concentrated at particular times and whether a new location will introduce a different workload.
Management is as important as the initial architecture. Use a standard approach for device naming, configuration backups, firmware maintenance, access permissions and change records. Monitor link utilisation, latency, packet loss, availability, tunnel status and critical application performance rather than relying only on whether a circuit appears connected. Alerts should identify trends early, while clear ownership and escalation procedures prevent faults from being passed between connectivity, network and application teams.
Use a staged implementation. A practical sequence is to document current sites and dependencies, define the target topology, test the design at a representative location, migrate in controlled groups and review the results after each stage. Keep an up-to-date network diagram, IP address plan, circuit record, security policy and recovery procedure. Retire obsolete routes and accounts after migration so that the old design does not remain an unmonitored path into the organisation.
For a growing organisation, the best design is repeatable rather than bespoke at every site. Standard site templates, centrally controlled policies and documented exceptions make acquisitions, relocations and new branches easier to integrate. S2 Technology Group can help small and medium-sized organisations assess these requirements and develop managed IT and connectivity arrangements that fit their existing infrastructure and planned growth.
A site survey is a practical part of multi-site connectivity design because the proposed network depends on what each premises can physically support. Before selecting circuits or equipment, document the building entry point, provider hand-off location, internal cabling, comms-room space, power arrangements and the distance to key network equipment.
Check whether existing cabling can support the required link speeds and whether it is separated from sources of electrical interference. At larger premises, note the location of warehouses, production areas, offices and other zones that need network access. This helps determine where switches, wireless access points, firewalls and local routing equipment should be placed, rather than treating the site as a single connection point.
Define the demarcation between the connectivity provider’s equipment and the organisation’s network. Record which party owns each device, cable and power supply, and keep this information with the circuit and network documentation. A consistent survey template for every location makes new branches easier to compare and helps identify physical constraints before they affect the wider connectivity design.