
What happens during the transition to outsourced IT?
The transition to outsourced IT usually involves an initial assessment, agreement of priorities, secure access setup, documentation transfer and staff introductions before responsibility moves to the new provider. Once onboarding is complete, the provider monitors the environment, resolves issues, maintains systems and reviews requirements as the organisation’s technology needs develop.
The transition to outsourced IT is a controlled changeover of responsibility, knowledge and operational processes from an internal team, business owner or previous provider to a new managed IT partner. A well-managed transition does more than connect a provider to existing systems: it establishes who is responsible for each service, confirms how risks will be handled and creates a reliable basis for ongoing support.
The process normally follows several connected stages:
- Defining the transition scope. The business and provider establish which services are moving under outsourced management and which remain internal. This may include user support, Microsoft 365 administration, cloud infrastructure, endpoint management, backups, cyber security controls, connectivity, software administration and supplier coordination. Clear boundaries prevent duplicated work and reduce the risk of an important responsibility being assumed by nobody.
- Building an accurate operating picture. The provider gathers enough technical and business information to understand how the organisation works. This includes identifying critical applications, important business processes, dependencies between systems, key suppliers, sites, users and any technology that requires specialist knowledge. The purpose is not simply to create an asset list; it is to understand what would affect the organisation if a system, account or connection became unavailable.
- Checking risks and urgent issues. Transition work often reveals outdated software, unsupported devices, excessive user permissions, incomplete backups, weak authentication arrangements or undocumented systems. These findings should be separated into immediate risks, planned improvements and lower-priority recommendations. Not every issue needs to be corrected before the changeover, but the business should understand the exposure and agree how each material issue will be addressed.
- Establishing secure administration. The provider creates controlled administrative access using named accounts, appropriate permissions and agreed security procedures. Privileged access should be limited to what is necessary, protected with strong authentication and recorded so that changes can be traced. Former suppliers, leavers and unused accounts should be identified as part of access governance rather than left active indefinitely.
- Testing the information and controls. Important records should be checked rather than accepted without question. Examples include confirming that backups can be completed and restored, verifying that security alerts reach the right people, checking that devices are enrolled in the relevant management tools and testing whether remote access works for the users and systems that depend on it. Testing identifies gaps while responsibility is changing hands, when they can be dealt with systematically.
- Planning the changeover around business risk. Some activities can be completed without disruption, while others may affect users, connectivity or access to applications. A transition plan should identify dependencies, approval points, communication requirements and a fallback approach for changes that do not work as intended. Critical business periods, site moves, system upgrades and other planned changes should be considered so that competing work is not allowed to create avoidable risk.
- Introducing operating procedures. Outsourcing changes how staff report incidents, request access, approve changes and escalate problems. Users need clear instructions on the support channel and the information to include when reporting an issue. Managers also need to understand approval responsibilities, particularly for new accounts, permissions, equipment and software. These procedures should be simple enough to follow consistently and documented for future reference.
- Moving into stabilisation. After the formal changeover, the provider checks whether services are operating as expected and whether any unresolved transition items are affecting users. Early support activity can highlight recurring faults, unclear ownership or training needs. These issues should be recorded, prioritised and assigned rather than treated as isolated tickets, because patterns often indicate a process or configuration problem.
Responsibility should not be considered fully transferred merely because the provider has administrative access. A complete transition also requires a usable knowledge base, agreed escalation routes, current supplier details, records of important configurations and a shared understanding of business-critical systems. Where the previous provider or an internal administrator holds essential knowledge, that knowledge should be transferred in a structured way and checked against the live environment.
The business should remain involved throughout the transition. It needs to confirm which systems are critical, identify regulatory or contractual obligations, approve material risks and make decisions about investment or remediation. An outsourced IT provider can manage technical work, but it cannot determine business priorities without input from the organisation’s leaders and system owners.
Useful transition outputs include a responsibility matrix, an asset and service register, a risk and remediation log, an access-control record, a documented support process, a schedule of planned improvements and a list of outstanding assumptions. These records provide evidence of what was transferred and give both parties a reference point when requirements change.
For a small or growing business, the most important measure of a successful transition is not how quickly the changeover is declared complete. It is whether the organisation knows who owns each responsibility, whether critical systems and risks are understood, whether staff know how to obtain support and whether the new arrangement can be managed without relying on undocumented individual knowledge. S2 Technology Group approaches outsourced IT as an ongoing technology partnership, with the transition providing the foundation for secure, reliable and scalable management.
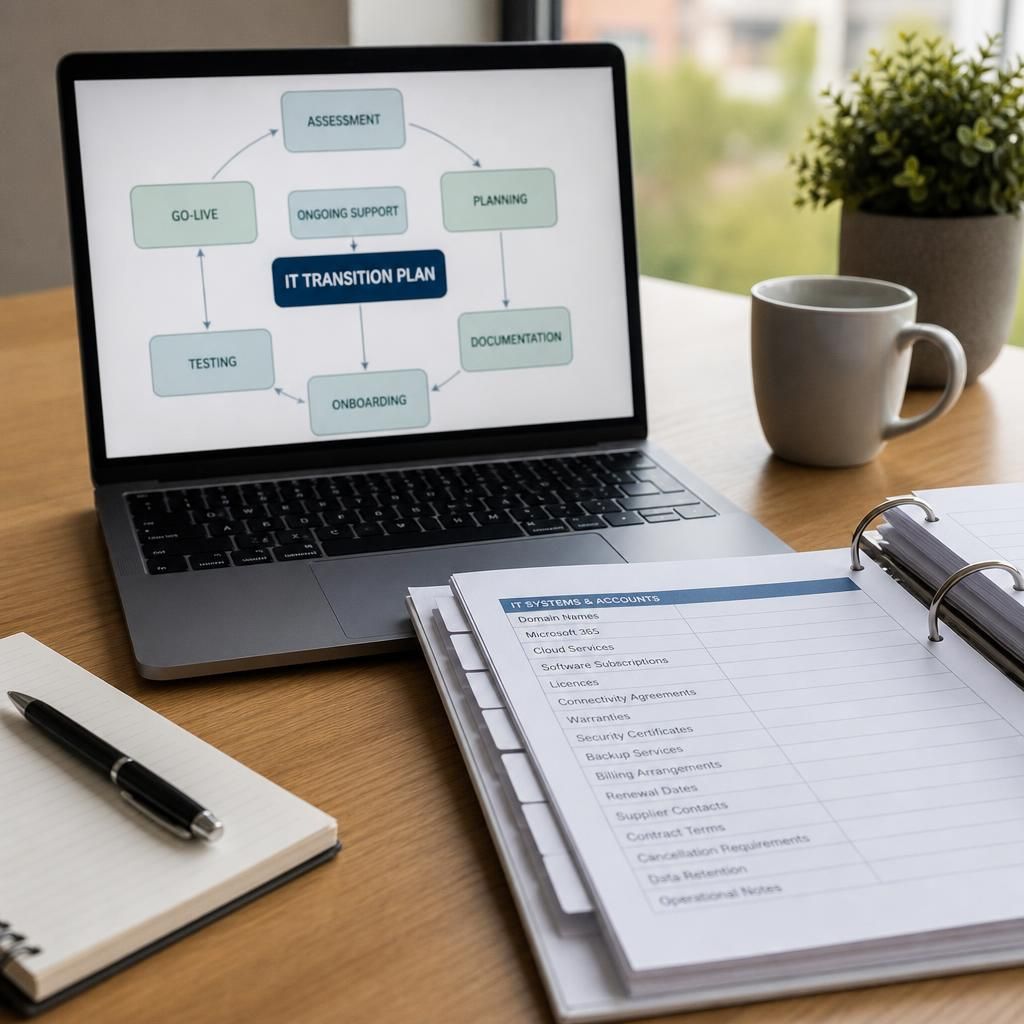
A transition to outsourced IT should transfer commercial control as well as technical responsibility. The business should identify who owns its domains, software subscriptions, cloud services, licences, connectivity agreements, warranties and security certificates, then confirm that renewal dates, billing arrangements and supplier contacts are recorded.
Access to these services should be held through business-controlled accounts wherever possible, rather than depending on an individual administrator or former provider. The handover should also record contract terms, cancellation requirements, data-retention obligations and any services that cannot be changed without affecting other systems. This gives the new provider the information needed to manage the environment without allowing an overlooked renewal or supplier dependency to interrupt an important service.
Discuss your transition to outsourced IT
If you are considering a move to outsourced IT, discuss your requirements with S2 Technology Group to understand the practical steps, responsibilities and priorities involved. A structured conversation can help establish whether the proposed arrangement fits your organisation before any changeover begins.