How is business data securely removed from retired cloud services and endpoints?
Secure removal involves identifying all business data and copies on the retired cloud service or endpoint, applying the provider’s deletion controls, and sanitising or securely wiping local storage before reuse or disposal. The process should also include access revocation, removal of recovery copies where applicable, and documented verification that data is no longer accessible.
Secure business data removal is a controlled end-of-life process that makes information on a cloud service or endpoint inaccessible, unrecoverable and no longer attributable to the organisation. It combines technical erasure with retention decisions, provider controls, access governance and evidence that the retirement was completed correctly.
Start with a data and asset record. Before retiring a service or device, record what it contains, who owns it, where it synchronises and whether copies exist in connected applications. This should include documents, email, databases, collaboration content, browser data, local user profiles, cached credentials, configuration files, encryption keys and exported reports. Asset records should also show the device or cloud account concerned, its business owner, retirement reason and disposal route.
Removal must be checked against the organisation’s retention schedule, contractual duties, regulatory requirements and any litigation or investigation hold. Data subject to a preservation requirement should not be destroyed simply because a subscription or device is being decommissioned. Conversely, retaining unnecessary copies indefinitely increases exposure, so the retirement decision should identify what must be preserved, what may be deleted and who approved the distinction.
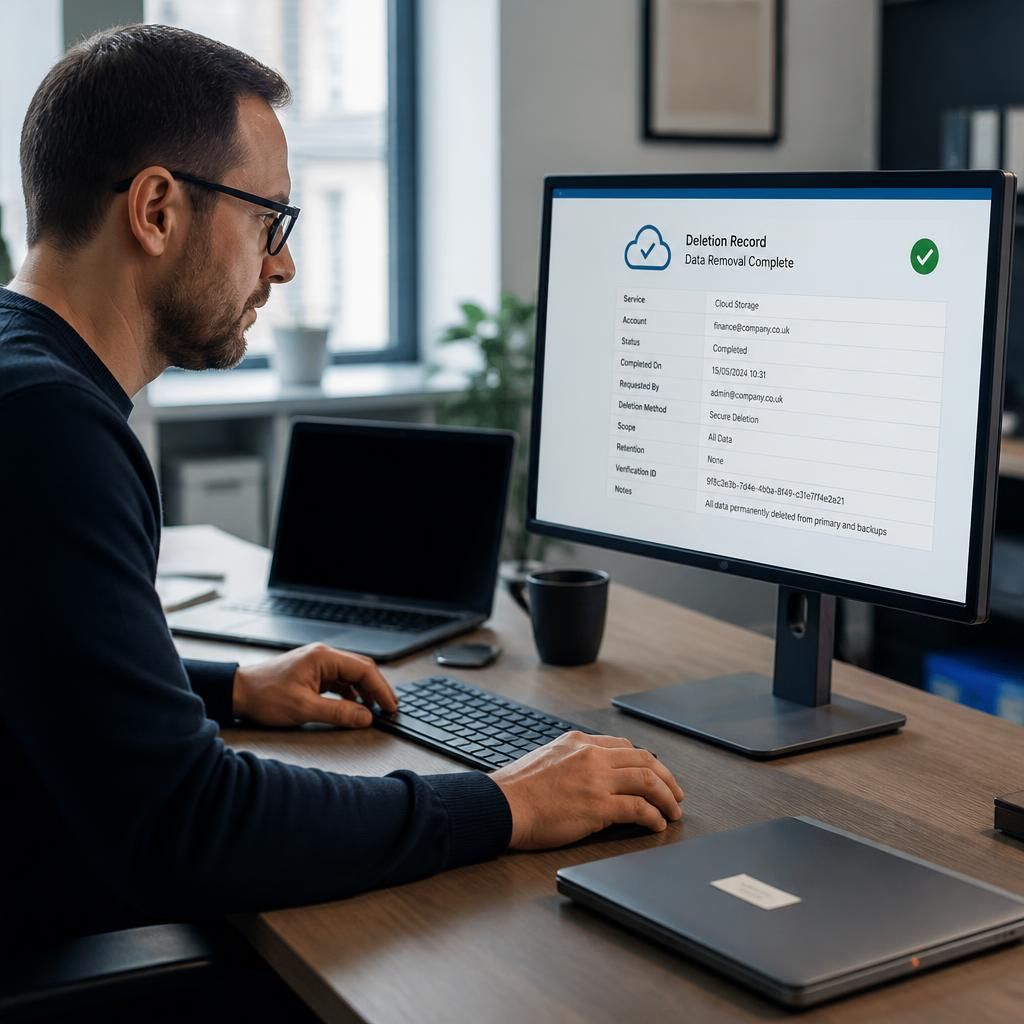
Cloud services require provider-specific checks. Deleting a user, workspace or subscription may only remove the primary view of the information. The service may retain items in recycle areas, version histories, legal holds, audit records, replicated storage or provider backups for a defined period. Administrators should review the provider’s deletion and retention documentation, disable integrations and exports, remove delegated access, and request tenant or account closure where appropriate. Where the provider supplies a deletion report or certificate, retain it with the retirement record and confirm what the evidence does and does not cover.
Connected systems need separate treatment. A file removed from a cloud platform may still be present in synchronised folders, backup products, email attachments, mobile applications, document management repositories or locally downloaded exports. Review application programming interface connections, automation accounts, service accounts and shared mailboxes as well as named users. A cloud service should not be considered retired until dependent systems have been assessed and any authorised copies have been dealt with under the same retention decision.
Endpoint sanitisation depends on the storage technology and its future use.
- For a device being returned or reassigned, remove organisational profiles, management enrolment, certificates, tokens and cached authentication material before applying an approved sanitisation process.
- For hard disk drives, use a method appropriate to the drive and its intended disposal or reuse. A basic file deletion or quick format is not sufficient because it can leave recoverable data behind.
- For solid-state drives, traditional overwriting may not address all flash storage areas because of wear levelling. Manufacturer-supported secure erase or cryptographic erase may be more suitable when properly implemented and verified.
- For failed, damaged or retired media that will not be reused, controlled physical destruction may be appropriate. Record the media identifier and obtain destruction evidence from the responsible disposal process.
- For removable media, phones and tablets, include memory cards, downloaded files, offline application data and device backups rather than relying only on a factory reset.
Encryption reduces the impact of loss but does not automatically prove that data has been removed. Cryptographic erasure can be effective when the relevant data is encrypted and the keys are uniquely controlled, securely destroyed and not recoverable from another system. The method, key ownership and verification result should therefore be recorded rather than treating encryption as a substitute for an approved sanitisation process.
Verification should test the result, not just the action. Useful evidence can include the asset identifier, storage type, sanitisation tool and version, operator, date, method, outcome, exceptions and reviewer. For cloud services, retain provider confirmations, account closure records and relevant retention settings. For endpoints, confirm that the device starts in an expected clean state, cannot access former organisational resources and contains no recoverable business profile or synchronised content. Higher-risk assets may require independent review or specialist media destruction records.
Exceptions should be documented when a service cannot immediately remove a backup, a device cannot be sanitised because it has failed, or records must remain under a preservation requirement. The record should state the residual risk, the data affected, the compensating control, the responsible owner and the date for reassessment. Disposal should then be reconciled against the asset register so that retired accounts, devices and media cannot quietly remain in use.
A repeatable retirement procedure normally assigns responsibility across the system owner, IT administrator, information security lead and records or compliance owner. S2 Technology Group can help organisations around Stourbridge, Kinver, Wordsley, Kingswinford, Kidderminster, Halesowen, Dudley and neighbouring areas review cloud and endpoint retirement controls, document the process and align technical actions with wider security governance.
Secure retirement also requires control of the endpoint or storage media while it is being transferred, stored or disposed of. A device can remain a data exposure risk after sanitisation has been scheduled, particularly if it is awaiting collection or is handled by a third party.
Keep a record linking each device or media identifier to its approved disposal route, handover and final outcome. Restrict access during storage, use an authorised disposal process, and reconcile collection records with the asset register. Where a third party destroys or processes the media, retain evidence that identifies the items covered and the disposal method. This creates a clear chain of custody and helps distinguish completed data removal from a device that has merely been marked for retirement.