
How do cyber security services identify unknown devices on a business network?
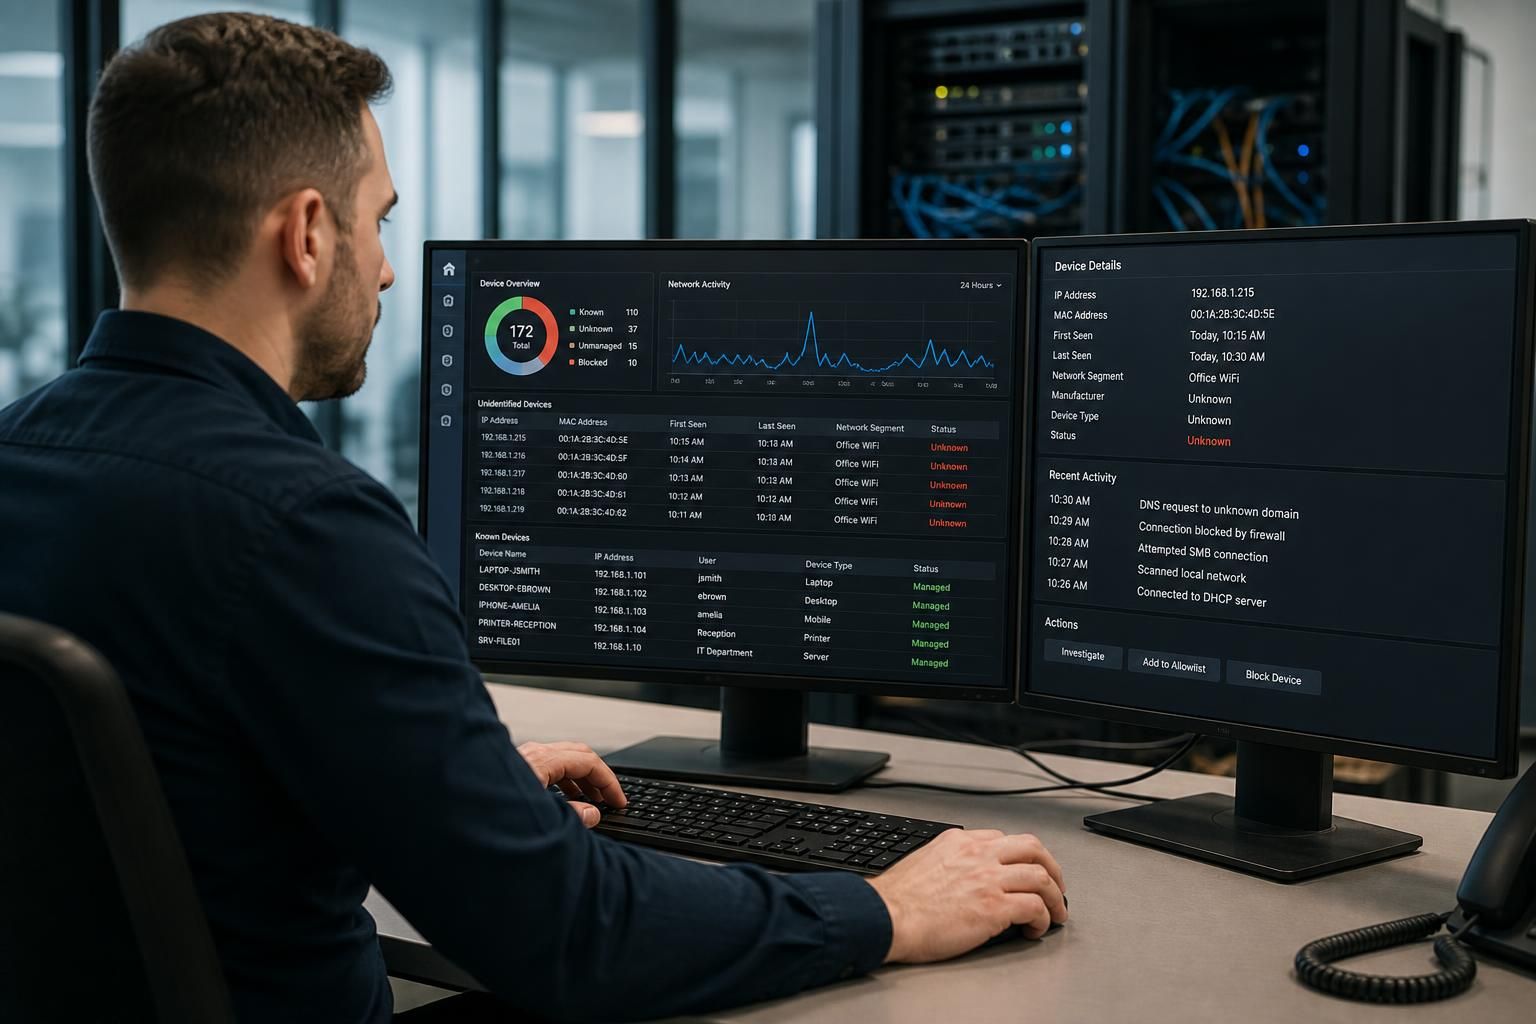
Cyber security services identify unknown devices by comparing network discovery data with approved asset records, using sources such as DHCP logs, switch and wireless controller information, endpoint agents, and IP or MAC address details. They can then assess device characteristics, user or location context and network behaviour to distinguish an authorised device from an unmanaged or potentially malicious one.
Cyber security services identify unknown devices by establishing whether each connection is expected, managed and behaving consistently with the organisation’s security policy. The process combines asset visibility, network access controls, device identity checks and ongoing monitoring, rather than relying on a single IP address or one-off network scan.
Device discovery is only the first stage. A device may appear unfamiliar for legitimate reasons: it could be newly installed, temporarily connected by a contractor, replaced after a hardware fault, or using a different network address. Conversely, a device that appears familiar may still be compromised. Effective identification therefore links the device to an accountable owner, an approved business purpose and an appropriate level of access.
Services commonly compare observed devices with an asset register or configuration management database. Useful records include the device owner, department, physical site, operating system, business function, assigned network segment and management status. A match is more reliable when several attributes agree. For example, a laptop associated with a known employee, enrolled in endpoint management and connecting from its expected office location presents a different risk from an unregistered device using the same address as an approved computer.
Network access control can strengthen this process by checking a device before granting access. Depending on the organisation’s design, checks may include:
- whether the device has an approved certificate or other trusted identity;
- whether required security software is installed and reporting;
- whether the operating system and important applications meet the organisation’s patching policy;
- whether the device is owned and managed by the business;
- whether the user has permission to connect it; and
- whether the connection is being made through an authorised wired, wireless or remote access route.
A device that fails these checks can be placed in a restricted network segment rather than receiving normal access. This containment approach allows limited remediation or registration without giving an unmanaged device a route to sensitive servers, administrative systems or confidential data. Guest and contractor devices can be handled through separate access policies, with permissions limited to the resources required for their work.
Identification also depends on correlating events from different security controls. Authentication records can show which account was used, while firewall, DNS, web filtering and endpoint telemetry can reveal what the device attempted to access. Security monitoring can then look for inconsistencies, such as a device changing location unexpectedly, communicating with prohibited destinations, scanning internal systems, creating unusual volumes of traffic or attempting to use administrative protocols. These indicators do not automatically prove malicious activity, but they can raise the device’s risk level for investigation.
Services may classify devices into practical categories such as approved and managed, approved but non-compliant, known but unmanaged, temporary or guest, and unidentified. Each category should have a defined treatment. A compliant managed device may receive normal access; a known device requiring updates may be restricted until corrected; and an unidentified device may be quarantined or blocked pending verification. Clear categories reduce inconsistent decisions and make exceptions easier to review.
Maintaining accurate records is essential. When equipment is purchased, replaced, retired or moved between sites, its status should be updated in the asset register and associated management systems. Old records should be removed or marked as retired so that a recycled address or former device identifier does not create misleading matches. Businesses should also document approved exceptions, including personally owned devices, specialist equipment and supplier-managed systems that cannot use the standard endpoint controls.
Some equipment is difficult to identify through conventional endpoint methods. Printers, cameras, phones, industrial systems and other embedded devices may not support an agent or modern authentication method. These devices can still be assessed through their network behaviour, manufacturer and model information, location, ownership and required destinations. Where they cannot meet the normal policy, compensating controls may include a dedicated network segment, tightly limited communication rules and removal of unnecessary services.
Unknown-device detection should include an investigation workflow. A useful sequence is to confirm the device’s technical identity, identify the connecting user or responsible team, establish why it is present, review its recent activity, and decide whether to approve, remediate, isolate or remove it. The decision and evidence should be recorded so that recurring unknown devices can be traced to a process problem, such as incomplete onboarding or poor asset disposal.
Businesses should also test detection quality. Reviews can check whether newly introduced devices appear in monitoring, whether retired equipment disappears from approved records, whether restricted devices are actually prevented from reaching sensitive resources, and whether alerts contain enough information for investigation. This helps distinguish genuine gaps in visibility from harmless changes in addressing or routine equipment replacements.
For a small or medium-sized organisation, the practical objective is not to treat every unfamiliar device as an attack. It is to ensure that every connection has an explainable owner, purpose and access level, while suspicious or unmanaged connections are contained before they can provide a route into more valuable systems. Cyber security services can support this through network visibility, policy design, monitoring and regular review of the organisation’s device-control process.
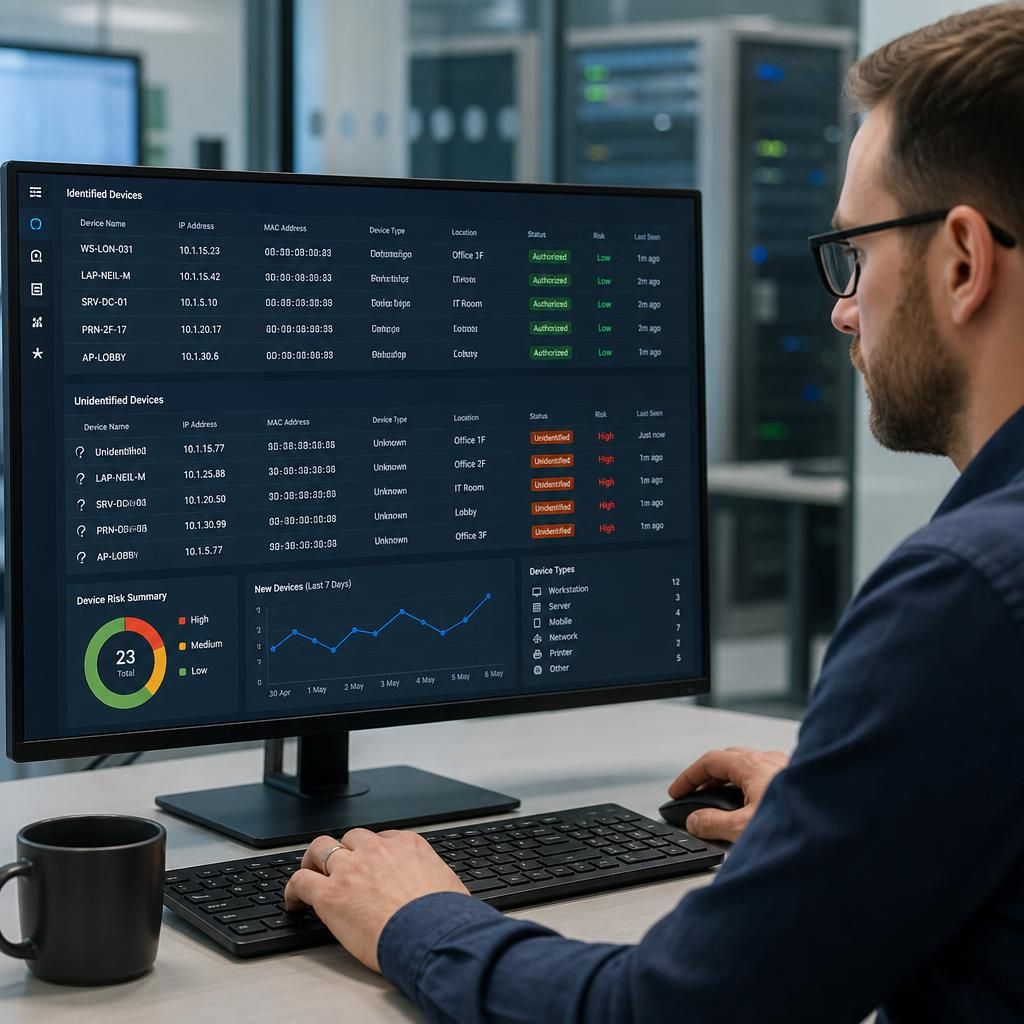
An IP address or MAC address is not, by itself, proof that a device is authorised. Addresses can change, be reused or deliberately copied, so cyber security services use stronger evidence when a connection could be impersonating an approved device.
For example, network access controls may verify a device certificate, its endpoint-management record and the user’s authentication before access is granted. These checks can be compared with the switch port, wireless connection, assigned network segment and device security posture. A mismatch—such as a familiar address appearing on an unexpected port without a valid certificate—can indicate spoofing or an inaccurate asset record and should trigger investigation.
This layered approach helps separate a simple addressing change from an attempt to bypass network controls. It also gives investigators a clearer evidence trail when deciding whether the device should remain connected, be registered correctly or be isolated.