
How is backup integrity verified independently of the backup job report?
Backup integrity is verified independently by checking that stored data can be read, reconstructed and restored, rather than relying solely on a successful job status. This typically combines scheduled recovery tests, checksum or hash validation, verification of immutable copies and review of audit records showing what was tested and when.
An independent integrity check is a control operated outside the backup task itself, with evidence generated by a separate validation process. Its purpose is to establish that the protected data remains usable, complete and consistent even if the original backup software, repository index or administrator account reports a successful operation.
The separation should apply to both the process and the evidence. A useful design prevents the backup task from marking its own work as verified. For example, a separate system, account or scheduled workflow can select recovery points, perform validation and record the results in an audit store that the backup operator cannot alter. The degree of separation should reflect the risk: highly sensitive systems benefit from a separately administered verification environment and restricted access to its records.
Validation can be performed at several levels:
- Storage-level validation: the verification process reads blocks, objects or files from the repository and checks them against their recorded checksums, hashes or other integrity information. This can identify corruption that is not apparent from the backup catalogue.
- Structural validation: the process checks that the recovery point contains the expected file structure, metadata, permissions and dependency information, rather than merely confirming that data can be listed.
- Recovery-point validation: selected data is reconstructed in a controlled location. This tests whether the stored components can be assembled into a usable recovery set.
- Application-level validation: where supported, the recovered data is opened or checked using the relevant application or database validation tools. A database, virtual machine or line-of-business system may appear intact at file level while still containing logical inconsistencies.
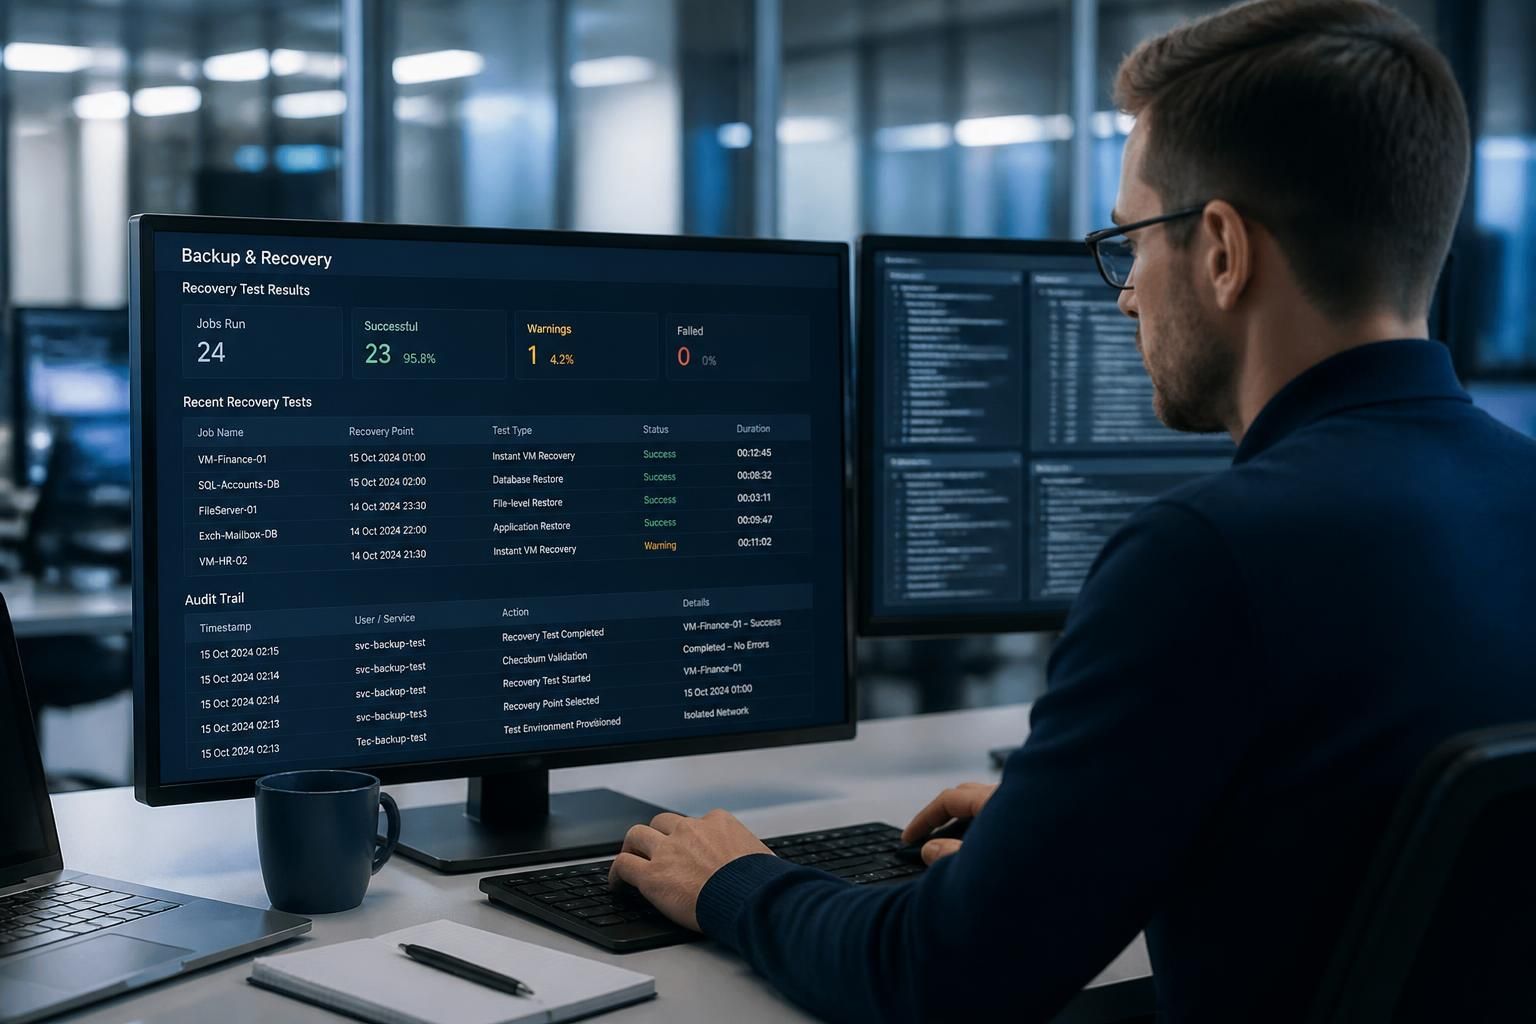
Recovery tests provide stronger evidence than repository inspection alone because they exercise the complete path from stored data to usable information. The test should define what is being recovered, use a representative selection of systems and record whether the result meets the organisation’s recovery requirements. Testing should take place in an isolated environment where recovered systems cannot overwrite production data, connect unintentionally to live services or introduce malware.
Sampling needs to be deliberate. Testing only the newest recovery point may miss corruption affecting older copies, while testing only small documents may not reveal problems with large databases or complex workloads. A sound sample can include different dates, storage locations, data types, criticality levels and backup methods. The selection method should be documented so that it is repeatable and cannot be adjusted solely to produce favourable results.
Immutable or otherwise protected copies require their own checks. Verification should confirm that the copy is still present, that its retention or lock settings have not been weakened, and that the organisation can retrieve it using an authorised recovery path. This matters because a copy may be technically unchanged but still unusable if its catalogue, encryption keys, permissions or retrieval process is unavailable.
Evidence should be sufficiently detailed for another person to reproduce or challenge the conclusion. Records commonly include:
- the recovery point and data set selected;
- the source repository and destination used for the test;
- the validation method and software version;
- the identity or service account that performed each action;
- the start and completion times;
- the files, objects or applications successfully examined;
- any checksum mismatch, missing dependency, permission error or application error;
- the corrective action, owner and final disposition of each exception.
Audit records should be protected from alteration and retained for long enough to support incident investigation, governance reviews and recovery planning. Access should be limited, with separate permissions for performing a test, approving its result and changing the verification configuration. Alerts should distinguish a failed validation from a test that did not run, was incomplete or produced inconclusive evidence; treating all three as a simple success or failure can conceal weaknesses.
When a check fails, the response should not be to rerun it until it passes without investigation. The organisation should determine whether the cause is damaged data, a missing key, an access change, an unavailable dependency, an incorrect test configuration or a failure in the verification process itself. The affected recovery points should be identified, alternative copies should be examined and the issue should remain open until a usable recovery path has been demonstrated.
A practical verification framework therefore combines independent sampling, technical validation, isolated restoration, application-aware checks and tamper-resistant records. The backup job report remains useful as operational evidence that a task ran, but independent verification supplies the separate proof that the resulting data can be trusted for recovery.
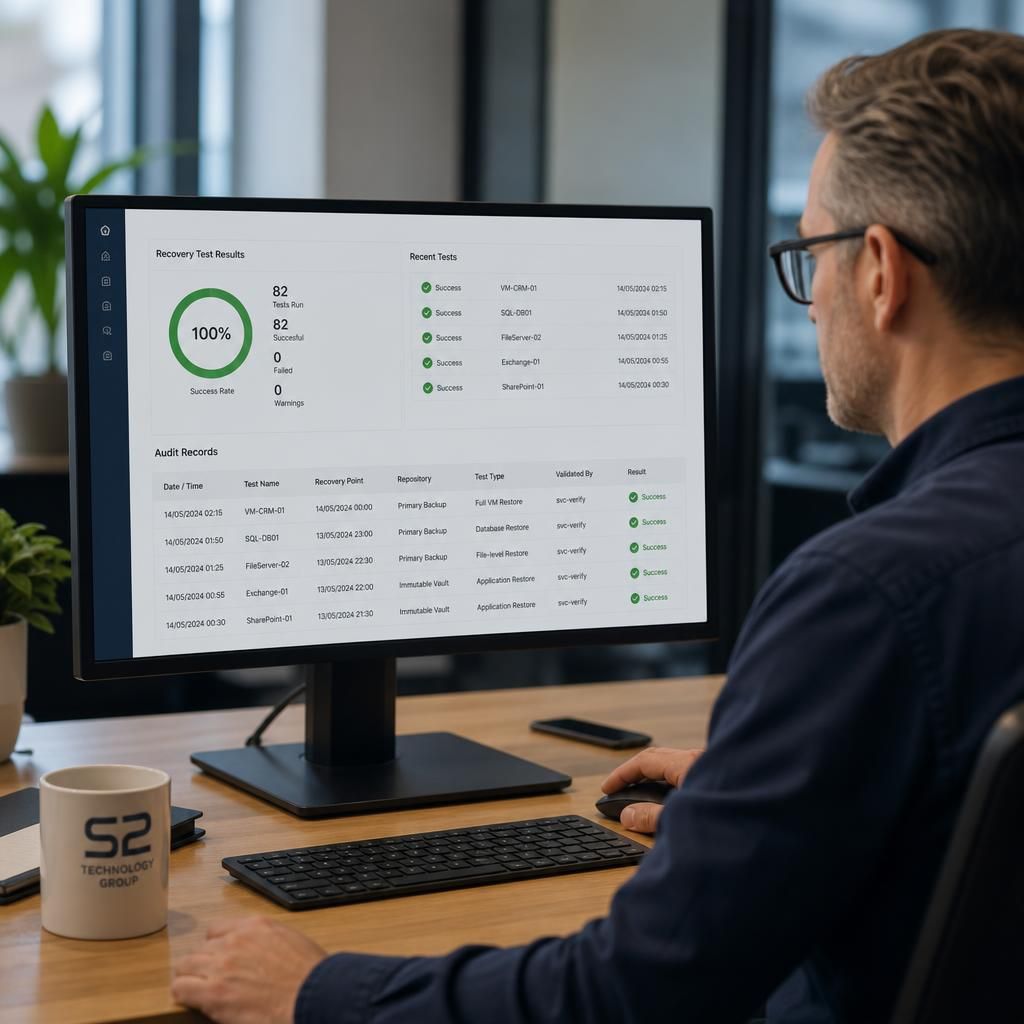
Backup integrity checks should be paired with an independent comparison between the organisation’s live data inventory and the recovery points being verified. This confirms that the systems, repositories and datasets included in the protection policy are still represented in the backup catalogue, including newly created workloads or data moved to a different location.
This distinction matters because a recovery point can be internally consistent while an important dataset is absent from it. The comparison should record newly discovered sources, excluded data and changes in ownership, then route discrepancies for review. It provides evidence that verification covers the intended backup scope, not just the data that the backup system already knows about.
Discuss independent backup integrity verification
Ask S2 Technology Group to review whether your backup verification process provides independent, auditable evidence that recovery points remain trustworthy. The review can identify gaps in validation, access separation and recovery testing for your business data.