Does backup software preserve file permissions during restoration?
Backup software can preserve file permissions during restoration, but this depends on the backup method, source and destination file systems, and whether identity mappings remain consistent. Permissions may need to be remapped or reapplied when restoring to different operating systems, domains, storage platforms or user accounts.
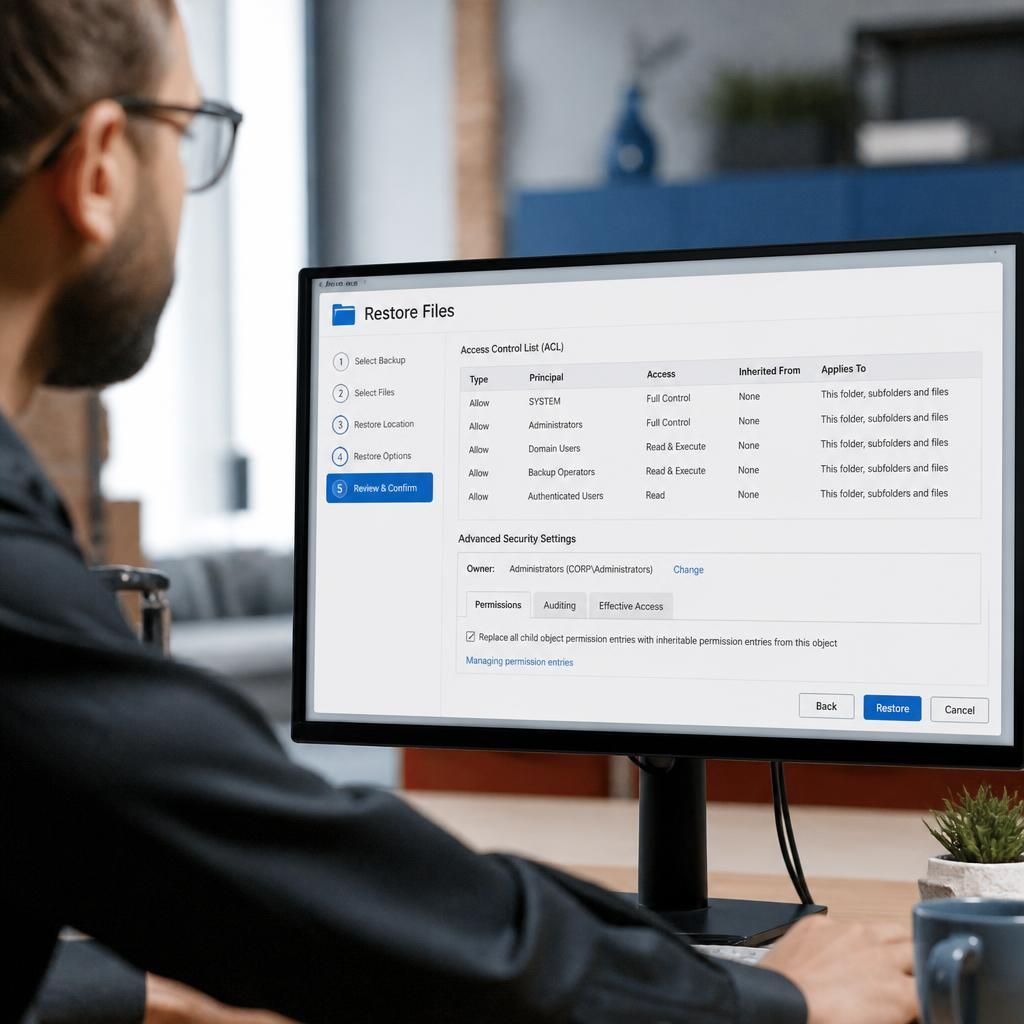
Whether file permissions are preserved depends on which security metadata the backup captures and whether the restore target can interpret it. A complete file restore may include access control lists (ACLs), ownership, auditing information and inheritance settings, while a basic data-only copy may restore the file contents without reproducing its original access rules.
On systems that use Windows security identifiers, permissions are normally linked to user and group identities rather than simply to the names displayed in the file system. If the original directory service and identifiers are still available, restored ACLs can often be applied as intended. If the restore is made into a new domain, a rebuilt server or a different identity system, the stored entries may refer to accounts that no longer exist. Users with matching names may still have different identifiers, so the permissions may need to be mapped to current accounts or groups.
Unix and Linux environments use a different permission model. Restored files can carry an owner ID, group ID, read/write/execute modes and, where used, extended ACLs. A restore to another system can produce unexpected access results if the numerical user and group IDs do not correspond to the same people or services. Special attributes, symbolic links and security contexts may also require separate support from the backup method and destination file system.
The restore destination affects the result in several ways:
- Restoring to the original server: Existing identity services, file-system features and inheritance structures are more likely to match the protected data.
- Restoring to a replacement server: The operating system, directory membership, shared-folder configuration and service accounts should be prepared before permissions are tested.
- Restoring to a network appliance or cloud file service: The destination may support a different subset of ACLs, ownership fields or inheritance rules. Some advanced permissions may be simplified or omitted.
- Restoring individual files: The software may apply the permissions from the backup, inherit permissions from the destination folder, or use the account performing the restore. The selected restore option matters.
- Restoring a complete volume or system: More security metadata can usually be retained, provided the target supports the same file-system and operating-system features.
Permission handling is also influenced by the restore account. An administrator may be able to recover the data but not automatically recreate every ownership or ACL entry. Some platforms require elevated rights to restore security descriptors, change ownership or write protected system locations. A successful copy therefore does not necessarily prove that the original access model has been recovered.
Before relying on a backup for recovery, administrators should confirm that the job includes security metadata rather than only file contents. Useful checks include:
- Reviewing the backup configuration for ACL, ownership, inheritance and extended-attribute support.
- Confirming that the destination file system supports the permissions being recovered.
- Checking how the software handles missing users, groups and service accounts.
- Testing restores for ordinary users, privileged administrators and applications that use shared folders.
- Comparing inherited and explicitly assigned permissions after recovery.
- Recording any required identity mappings or post-restore scripts.
A restore test should examine more than whether a file opens. It should verify that authorised users can access the required folders, unauthorised users remain blocked, group membership behaves correctly, and applications can still read or write their data. Testing should also cover renamed accounts, disabled accounts and files with unique permissions, as these often reveal mapping or inheritance problems.
When permissions cannot be reproduced exactly, the safest approach is to treat the recovered data as restricted until its access rules have been reviewed. Administrators can then apply a documented permission structure based on current roles, remove obsolete identities and check for excessive access. Reapplying broad permissions simply to make the restored files usable can create a security weakness.
Retention and backup design matter as well. Keeping several recovery points can help identify when a permission change occurred, but it does not correct an incomplete backup configuration. Permissions should be included in recovery procedures, alongside data validation, identity services and application testing. S2 Technology Group helps organisations assess backup and restore arrangements so that file access controls are considered as part of wider IT and security planning.
Preserving file permissions does not always preserve the complete access model. A file restored to a shared folder may retain its file-system ACL while the surrounding share permissions, directory-level restrictions or cloud access policies are configured separately. Effective access is determined by how these layers combine, so a user may gain less access than expected, or more access than intended, even when the restored ACL appears correct.
For this reason, permission verification should include the restored share or service configuration as well as individual files. Check both permitted and blocked actions, including browsing folders, opening files, creating new files and modifying existing data. This distinction helps identify whether an apparent permission problem comes from missing file metadata or from access controls that were outside the backup software’s restore scope.