
How are managed backup retention policies aligned with regulatory requirements?
Managed backup retention policies are aligned with regulatory requirements by defining how long different categories of data must be preserved, based on applicable laws, contractual obligations and business needs. The policy should be documented, consistently applied, reviewed when requirements change, and supported by records showing that backups are retained and securely disposed of as intended.
Managed backup retention policies support regulatory compliance by linking backup copies and recovery points to the specific obligations that apply to each type of business data. The policy should distinguish between operational recovery, legal or contractual retention, and secure deletion, because a backup kept for disaster recovery is not automatically a compliant business record.
For UK organisations, the relevant requirements may include the UK GDPR and Data Protection Act 2018, sector-specific rules, contractual commitments, insurance conditions and requirements imposed by customers or professional bodies. These sources do not create one universal backup retention period. Instead, they require the organisation to handle personal and confidential information lawfully, protect it appropriately, and avoid keeping it for longer than necessary. A retention schedule therefore needs to reflect the purpose and sensitivity of the information rather than applying one setting to every system.
- Identify the data: classify personal data, financial information, client records, intellectual property, operational files and system configuration data.
- Identify the obligation: record the legal, contractual, regulatory or business reason for retaining each category.
- Define the recovery requirement: specify which restore points are needed for operational recovery and which copies must be preserved for investigation, dispute or audit purposes.
- Apply suitable controls: restrict access, protect backup copies from unauthorised alteration, and secure data during transfer and storage.
- Define disposal: state when expired copies are removed or rendered inaccessible, including copies held on secondary storage or in long-term archives.
A key distinction is between the retention of a business record and the retention of a backup. A regulated record may need to remain accessible, complete and understandable in its original business context. A backup may contain temporary system states, deleted files, application data and multiple duplicate copies. It can help restore the record, but it does not necessarily satisfy a requirement to maintain a formal record. Organisations should therefore keep authoritative records in the appropriate business system and use managed backups as a controlled recovery mechanism.
Backup schedules also need to account for the way copies are created. A file deleted from live storage may remain in several backup generations. If those copies contain personal data, the organisation should understand how long they remain recoverable and whether the backup platform supports controlled expiry. Where a valid erasure request applies, the organisation may need to remove the data from active systems and explain how it is handled in backups. In some circumstances, data may remain in an isolated backup until its normal expiry, provided the organisation has assessed the risk, prevents its routine use and removes it in accordance with the documented process.
Legal holds require a different treatment. If information is relevant to litigation, an investigation or a regulatory request, ordinary expiry rules may need to be suspended for identified copies. The hold should specify the data, systems and period concerned, identify who authorised it, and include a clear release process. Without this control, an automated retention rule could remove information that must be preserved.
Regulatory alignment also depends on the security of retained backups. Appropriate measures can include encryption, role-based access, separate administrative credentials, protection against unauthorised deletion, and segregation from production systems. The controls should reflect the sensitivity of the data and the consequences of compromise. Retaining information securely for an appropriate period is different from retaining it indefinitely: excessive copies increase the amount of data exposed if an account or system is compromised.
Auditors and customers may need evidence that the policy operates as intended. Useful evidence can include the approved retention schedule, data classification records, configuration reports, access logs, deletion records, exception approvals and records of changes to retention settings. Evidence should show not only what the intended rule is, but also which systems and backup sets it covers. Exceptions should have an owner, a documented reason and an expiry or review point.
Retention policies should be reviewed when the organisation introduces a new application, changes its data processing, enters a new contract, expands into a regulated activity or receives updated legal advice. A managed backup service can support this process by maintaining backup configurations, reporting on job and storage activity, and providing operational records for review. The organisation remains responsible for deciding which obligations apply and approving the retention rules; the service provider implements and administers the agreed technical controls.
Before approving a policy, a business should ask whether every retained backup has a defined purpose, whether personal data can be located within the backup estate, whether legal holds can override automatic expiry, whether access and deletion are controlled, and whether the organisation can demonstrate these arrangements to an auditor or regulator. Those checks help align managed backup with compliance requirements without treating backup storage as a substitute for records management or legal advice.
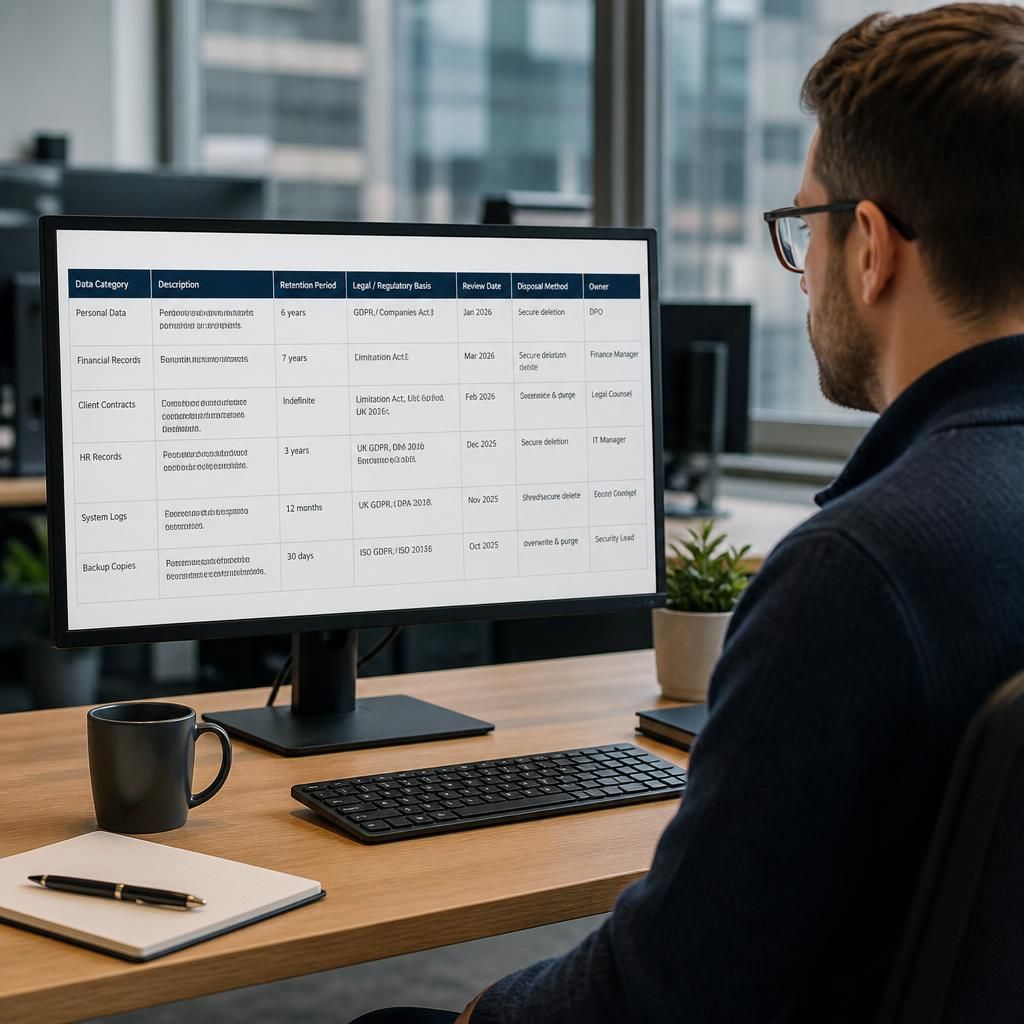
A practical way to validate a managed backup retention policy is to trace representative data through its full lifecycle. Select samples from different systems and confirm that the applicable retention rule is recorded, the expected backup copies are created, the expiry date is calculated correctly, and the data becomes unavailable when the rule ends. This checks that the policy operates in the backup platform rather than existing only as a written document.
The review should also examine changes over time. Retention settings may be altered when systems are migrated, applications are replaced or contractual requirements change. A controlled process should record the previous setting, the approved replacement, the effective date and the person responsible for authorising the change. This creates a clear explanation for why a particular backup set was retained or deleted during an audit.
Where different systems use different retention methods, the organisation should document how the rules correspond. For example, a cloud application, file server and database may expose different backup dates, deletion controls and reporting options. Mapping each system to the relevant policy requirement helps identify gaps before they become a compliance issue.
Discuss Your Managed Backup Retention Requirements
Discuss your managed backup retention requirements with S2 Technology Group to review whether your current arrangements support your organisation’s compliance obligations. We can help identify practical improvements to retention configuration, documentation and ongoing administration.