How easily can your business move away from a cloud server provider?
Moving away from a cloud server provider is usually possible, but the difficulty depends on contract terms, data portability, software dependencies and the destination environment. A controlled exit plan should cover data export, application testing, security, DNS and connectivity changes, user access, backups and final service termination to reduce disruption.
The ease of moving away from a cloud server provider is determined mainly by how portable the organisation’s systems are and how much they depend on provider-specific services. A straightforward move is more likely when workloads use standard formats, documented configurations and transferable licences. It becomes more complex when applications, databases, identity controls or operational processes are tightly integrated with the existing provider.
Contract terms should be examined before any technical work begins. Check the notice period, renewal arrangements, data extraction rights, support available during an exit, charges for transferring or exporting information, and the point at which the provider will remove retained data. The contract should also clarify who owns the data, configurations, documentation and custom development produced during the service. If these details are unclear, resolving them before committing to a move can prevent avoidable disputes.
Portability depends on the type of workload. A virtual machine using common operating systems and standard storage formats may be relatively transferable. A hosted application that relies on proprietary database structures, provider-specific automation or tightly coupled identity services may require more redesign. It is therefore important to identify each business application, its underlying data, its integrations and the technical skills needed to operate it in the proposed environment.
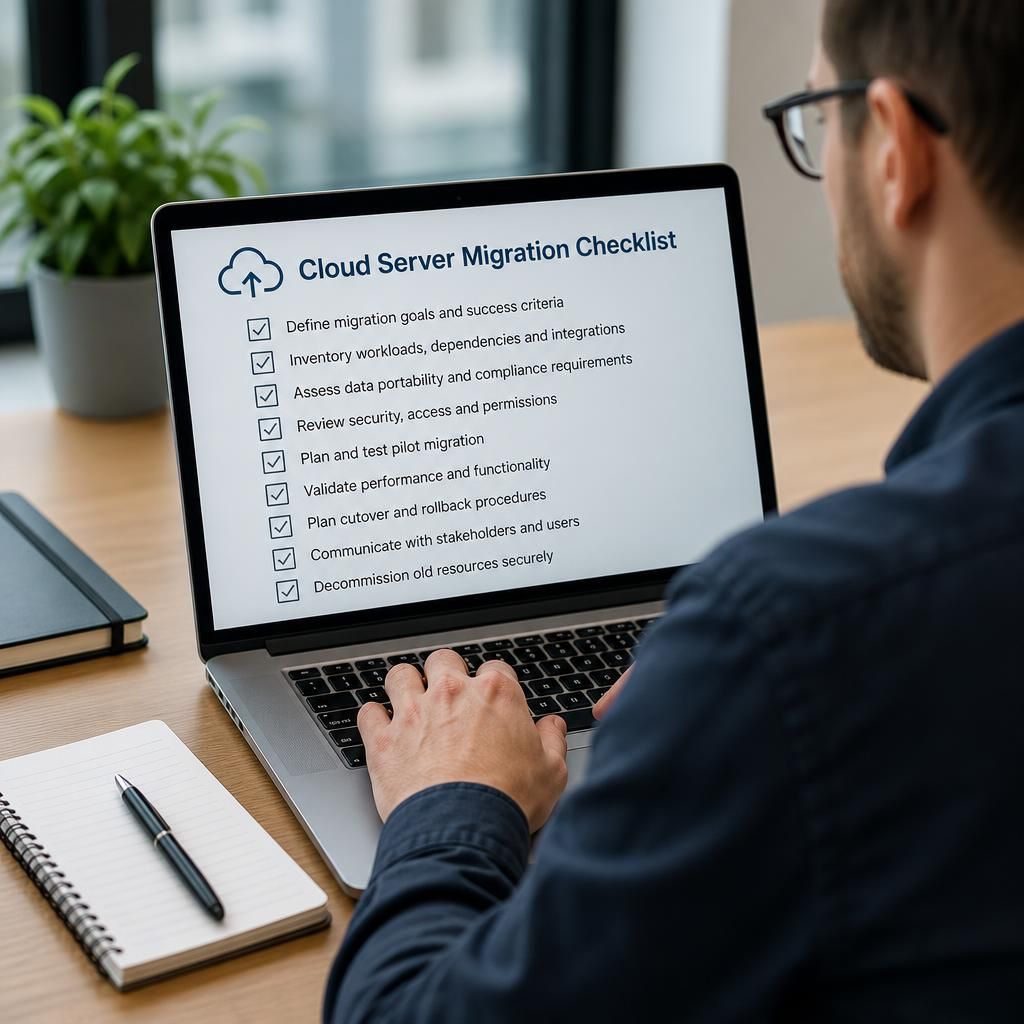
Create an exit inventory that records:
- servers, applications, databases and storage volumes;
- software licences, subscription ownership and renewal dates;
- user accounts, administrative roles and service accounts;
- integration points with finance, customer, production and communication systems;
- configuration files, scripts, certificates and other operational records;
- data retention obligations and information that must be preserved for audit or regulatory purposes.
This inventory provides a basis for estimating the work involved and exposes dependencies that may not be visible from the server environment alone. It should include the business owner for each system, not just the technical contact, because some systems can be moved technically but still require operational approval before they are changed.
A controlled transition needs agreed acceptance criteria. Before the existing service is retired, the replacement environment should demonstrate that users can perform the required tasks, integrations exchange information correctly, permissions reflect business roles and monitoring records expected activity. Validation should cover both normal operation and recovery procedures. Keeping a documented rollback decision and clear ownership for approving the final cutover helps prevent an incomplete migration from becoming a permanent service problem.
Data extraction is often more involved than copying files. Databases may need to be exported in a usable format, timestamps and permissions may need checking, and applications may require a specific import sequence. Large or frequently changing datasets can also create a gap between the initial transfer and the final changeover. The migration plan should define how that gap will be reconciled and how the completeness of the transferred information will be verified.
Provider dependency is a significant source of lock-in. It can arise from proprietary backup formats, unique monitoring tools, specialised networking, undocumented automation or services that have no direct equivalent elsewhere. During the assessment, distinguish between data that can be exported and a complete operating environment that can be recreated. An export may preserve the information without preserving the application logic, permissions or relationships needed to use it.
Security controls must remain effective throughout the transition. Access should be granted according to defined roles, credentials and certificates should be managed deliberately, and former administrative access should be removed once responsibility changes. Evidence of data deletion or retention from the outgoing provider may also be needed, particularly where the business has contractual, legal or sector-specific obligations.
The best time to plan an exit is before selecting a provider. Ask how data and configurations are supplied, whether documentation is kept current, what assistance is available during a transfer, and how the service supports an orderly termination. Maintain copies of essential documentation under the business’s control rather than relying solely on a provider portal. Periodic review of the exit plan is sensible because applications, integrations and responsible personnel change over time.
For a small or medium-sized organisation, the practical question is not simply whether a cloud server can be left, but whether the business can operate the replacement environment with comparable security, access control, resilience and administrative understanding. S2 Technology Group can help assess provider dependency, document the existing environment and plan a managed transition around the organisation’s applications and operational requirements.
A pilot migration is one of the most reliable ways to measure how easily a business can leave its cloud server provider. Instead of moving every workload at once, the organisation transfers a low-risk system or representative application to the proposed destination and assesses the practical results.
The pilot should involve the people who use and administer the system, not only the technical team. It can reveal whether users can access the application correctly, whether connected processes continue to function, and whether the replacement environment is manageable with the available skills and tools. It also provides a more realistic view of the time and effort required for larger workloads.
Choose a pilot that is useful enough to expose technical dependencies but not so critical that an unsuccessful test disrupts core operations. Record the findings, address any weaknesses, and use the revised process for subsequent migrations. This turns provider exit from a theoretical possibility into an evidence-based assessment of the organisation’s actual readiness.