
How can you tell whether a firewall is oversized for your business?
A firewall is oversized when its throughput, connection capacity and security features substantially exceed your business’s current and foreseeable network demands. Signs include paying for unused capability, unnecessary configuration complexity and administration that adds risk without improving protection; assess actual traffic, VPN use, inspection requirements and planned growth before choosing a smaller model.
An oversized firewall is one whose real operating capability is materially beyond the demands of the business, including the traffic it must inspect, the users and sites it must connect, and the security policies it must enforce. The most reliable way to identify this is to compare measured utilisation and operational requirements with the appliance’s capabilities, rather than judging it by its purchase price or headline specification alone.
Start with observed demand. Review several representative periods of firewall data, including ordinary working days, busy periods, software updates, backups, video conferencing and other predictable peaks. Examine bandwidth consumption, concurrent sessions, new connection rates, VPN activity and processor or memory utilisation while security inspection is enabled. A device may appear lightly loaded when only basic routing is considered but operate much closer to its practical limit when it performs application control, malware scanning, intrusion prevention or encrypted traffic inspection.
Measurements should be taken at the points where the firewall is actually under pressure. For example, internet traffic may be modest while site-to-site links, remote access or internal segmentation generate a large number of sessions. Conversely, a business may have high download speeds but little need for complex policy processing. The relevant comparison is therefore the firewall’s performance in the configuration being used, not an uninspected throughput figure from a product datasheet.
Look for unused functions as well as unused capacity. A firewall can be oversized because it includes capabilities that have no place in the organisation’s design. Features such as advanced web filtering, multiple virtual firewalls, extensive high-availability options or large-scale central management may be appropriate in a complex estate but unnecessary for a single, straightforward site. Paying for capabilities that are neither required nor maintained does not improve security; unused features can also broaden the configuration that administrators must understand and govern.
This does not mean that every inactive feature should be removed immediately. Some capabilities may support a planned change, regulatory requirement or future site connection. Each one should have a documented purpose, owner and review date. If no business need can be identified, it is reasonable to question whether the selected platform is proportionate.
Assess the licensing model separately. Oversizing is not limited to the physical appliance. A firewall may be capable of supporting considerably more users, sites or inspection services than the organisation needs, while its recurring subscriptions are priced around those higher limits. Check which licences are actually consumed, whether they are tied to user or device counts, and whether the business is paying for tiers that cannot be used in its current architecture. A smaller platform may still be unsuitable if it lacks a security service the business genuinely requires, so licence comparison must include function, coverage and renewal conditions rather than just the number of permitted users.
Consider the administration burden. Indicators of disproportion include policies, interfaces or integrations that are difficult to maintain because the platform was designed for a far more complex environment. This may show up as duplicated objects, unused zones, dormant VPN definitions, elaborate routing arrangements or multiple management layers with no clear operational purpose. The concern is not complexity for its own sake: poorly understood configuration makes reviews, troubleshooting and change control less reliable. A proportionate firewall should support clear separation of duties, documented rules and an understandable management process.
Separate sensible headroom from excessive headroom. Choosing a device with no spare capacity can create a problem when the business adds cloud services, users, locations or higher-bandwidth connections. Some allowance for foreseeable growth, security inspection overhead and temporary peaks is sensible. The question is whether that allowance is linked to a documented plan. Capacity bought for a vague possibility several years away may be difficult to justify, particularly if the platform will be replaced before the anticipated demand arrives.
A useful assessment records:
- current and forecast internet, inter-site and remote-access requirements;
- the number and type of protected networks, locations, users and devices;
- which inspection and access-control functions are enabled;
- measured utilisation during normal operation and known peak events;
- licences, subscriptions and support arrangements that are actually needed;
- the expected life of the firewall and any planned technology changes; and
- the operational effort required to manage, monitor and audit the configuration.
Do not use low utilisation as the only reason to downgrade. A quiet period, a temporary reduction in staff or a recently completed infrastructure change can make demand appear lower than it really is. Investigate whether traffic has moved to another security control, whether reporting excludes encrypted sessions, and whether high availability or failover changes the available capacity. Also check resilience requirements: a device may need enough capability for a surviving unit to carry the required load if one member of a pair is unavailable.
If the evidence supports right-sizing, compare alternatives by their inspected performance, security functions, management requirements, support model and upgrade path. Test the proposed design against the busiest realistic use case and confirm that logging, authentication, segmentation, remote access and recovery procedures remain suitable. The least expensive device is not automatically the right choice, and a smaller firewall that cannot accommodate required controls is not a sound security decision.
S2 Technology Group can help organisations assess firewall utilisation, configuration scope and planned network changes as part of a wider IT and cyber security review. The outcome should be a documented decision: retain the existing platform with a clear rationale, simplify its configuration, or move to a proportionate alternative without removing controls the business genuinely relies on.
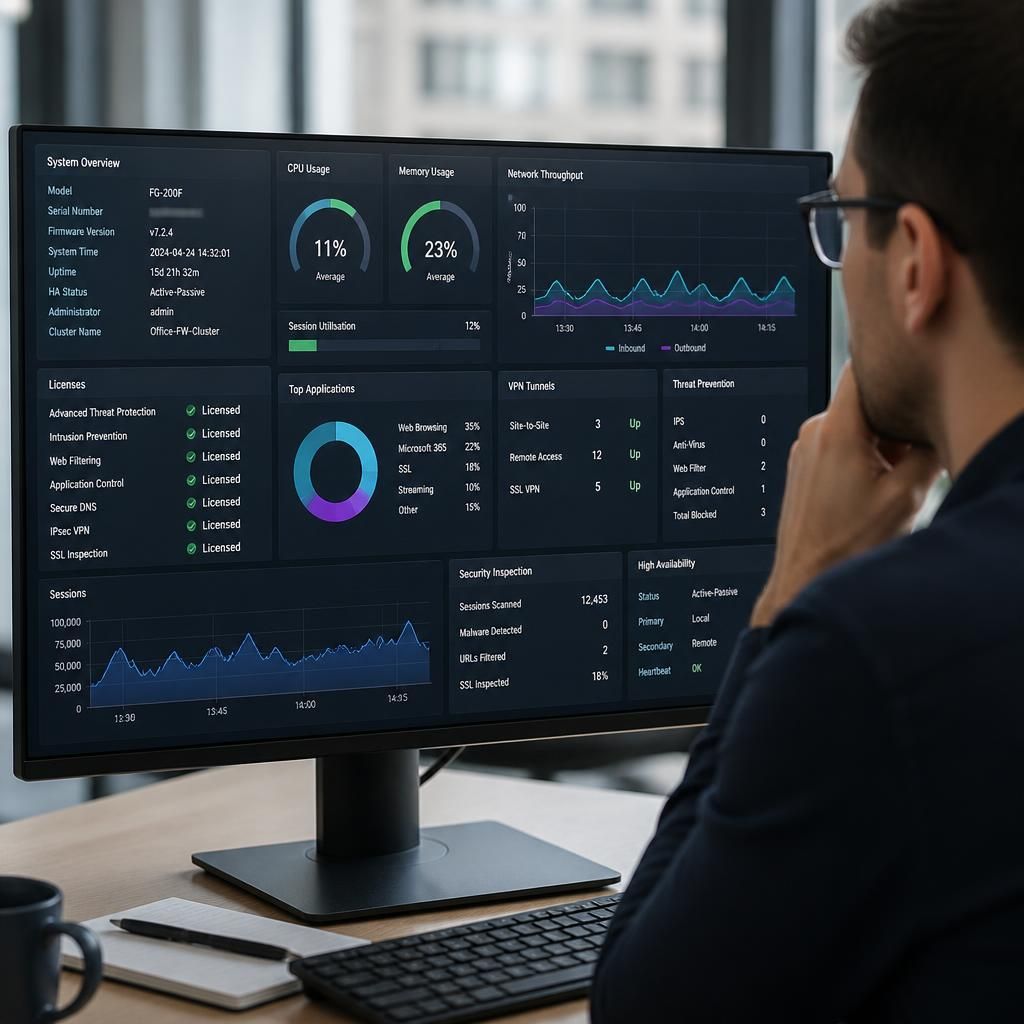
A firewall can appear oversized when its traffic counters are low but still be appropriately specified for the security functions it performs. For example, a platform supporting network segmentation, identity-based access, secure remote connections or detailed event recording may require more processing capacity than basic internet routing suggests. Review which controls are essential to the organisation’s security design before treating low bandwidth as evidence that the appliance is too large.
The assessment should also distinguish between capability that is unused today and capability that is required for resilience. A device may need additional capacity to maintain essential inspection and access controls during a fault, maintenance activity or change in traffic pattern. The right question is therefore whether each part of the specification has a recorded operational or security purpose, rather than whether every feature is constantly active.
Review whether your business firewall is correctly sized
Ask S2 Technology Group to review whether your firewall’s capacity, features and licensing remain proportionate to your business requirements. You will receive a practical basis for retaining, simplifying or replacing the platform without removing controls your organisation relies on.