
What happens to our IT documentation when we change local support providers?
Your IT documentation should remain your business’s property and be transferred securely to the new provider, subject to the terms of your existing agreement. A structured handover should cover network diagrams, asset and software records, support history, backup details, security procedures and privileged-access information, followed by a review to identify gaps, outdated records and credentials that need changing.
Changing IT support providers should include a controlled documentation handover, not simply the forwarding of a collection of files. The outgoing provider should supply the records needed to understand, operate and maintain your environment, while your business should verify the information, control access to it and agree how unresolved issues will be transferred.
Start by defining the handover scope. Ask both providers to agree a written list of the information required for an effective transition. This may include configuration records, warranty and licensing information, supplier contacts, change records, incident notes, policy documents, recovery instructions and details of systems that are managed by third parties. The scope should also identify documentation that is incomplete, held in a portal or stored in a proprietary system.
Documentation is often distributed across several locations rather than kept in one folder. Some records may be held in a service desk platform, password vault, remote monitoring system, cloud administration portal or network management tool. The handover plan should identify each repository, who controls it, what data it contains and how it will be exported. A provider should not treat access to its own platform as a substitute for delivering usable business records.
Check the format and usability of the information. A file can be technically transferred but still be of little practical value if it cannot be opened, searched or updated. Prefer commonly usable formats where appropriate, and request an explanation of any proprietary exports. Diagrams should include enough labelling to identify relationships between equipment, locations and services. Lists should show relevant dates, owners and status rather than consisting only of device names or abbreviated notes.
A useful handover also records what is not known. For example, an undocumented firewall rule, an unconfirmed software subscription or an unexplained connection between two systems should be marked as an open item instead of being presented as complete. This distinction helps the incoming provider prioritise investigation and prevents assumptions from becoming embedded in the new records.
Protect the transfer itself. Documentation can contain commercially sensitive information and details that could assist an attacker. It should be exchanged through an agreed secure method, with access limited to named people who need it. Avoid sending sensitive files or administrative information through ordinary unprotected email. Where information includes personal data, the parties should also consider their data protection responsibilities, retention requirements and whether any records need to be redacted or transferred under specific contractual arrangements.
The outgoing provider should confirm which copies it retains after the contract ends and why. Your business may need to understand how long records are kept for legal, audit or service-management reasons. Any retained copy should remain subject to appropriate security controls, and access should be removed when it is no longer justified. The termination terms should be checked for provisions covering data return, export charges, ownership of work products and deletion.
Use a staged transition rather than waiting for the final day. A practical sequence is:
- appoint an owner within your business for coordinating the handover;
- agree the information list, responsibilities, dates and secure transfer method;
- collect an initial export early enough to expose missing or unusable records;
- give the incoming provider an opportunity to raise questions and request clarification;
- test important information against the live environment before the previous agreement ends;
- record outstanding items, their owners and the actions needed to close them; and
- complete a formal acceptance review and retain a copy of the agreed handover record.
The incoming provider should not rely on documentation without checking it. A controlled review can compare the records with observed configurations, current users, active services and known business requirements. This may identify obsolete entries, undocumented changes, duplicate accounts, unsupported equipment or services that no longer have a clear owner. Findings should be classified by operational and security importance so that critical uncertainties are dealt with before lower-priority housekeeping.
It is also important to separate documentation transfer from access transfer. Administrative access should be reviewed independently, with credentials changed or reissued through the appropriate process and former provider access removed when no longer required. The handover record should show who approved these changes without exposing secret values in ordinary documentation.
Contractual disputes can complicate a transition, particularly where fees, licensing or ownership of records are contested. Businesses should avoid allowing an unresolved commercial issue to obscure operational risks. The agreement should be reviewed early, and specialist legal advice may be appropriate where the provider refuses to release information, personal data is involved or deletion obligations are unclear.
After the transition, documentation should be treated as a maintained business asset rather than a one-off project. Assign owners, define when records must be updated and review them after significant changes such as office moves, cloud migrations, network alterations or changes to key suppliers. S2 Technology Group can help organisations around Stourbridge assess transferred records, identify gaps and establish a more consistent approach to ongoing IT documentation.
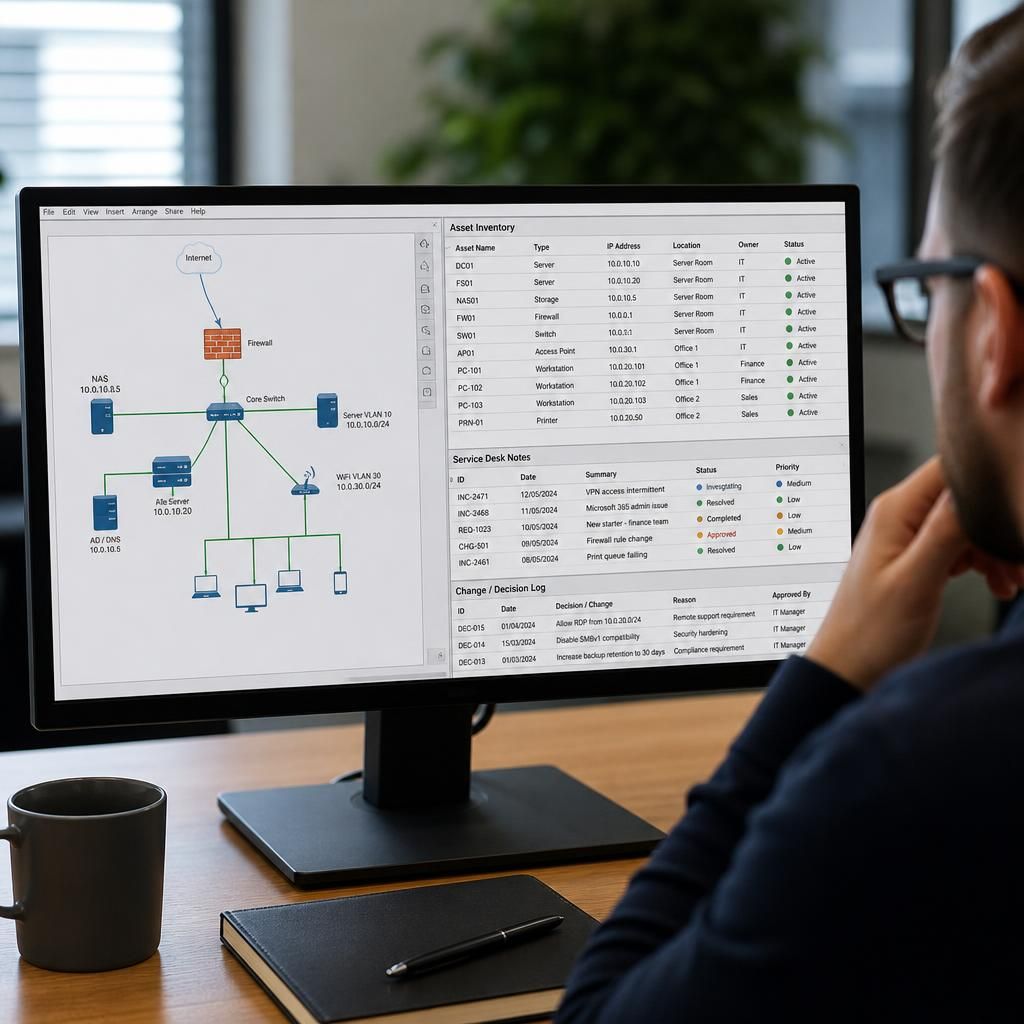
IT documentation should explain not only what is configured, but why important decisions were made. A network rule, system exception or unusual user permission may reflect a deliberate business requirement rather than an error. Where available, include the reason for the decision, the person or role that approved it, any associated risk and the circumstances in which it should be reviewed.
This context helps the incoming provider distinguish intentional arrangements from undocumented problems. It also reduces the risk of a well-meaning change removing a necessary dependency or control. Decision notes can be brief, provided they are linked to the relevant system, configuration record or change reference and clearly marked when the original rationale is unknown.