
How is assessment evidence protected during a cyber risk assessment?
Assessment evidence is protected through controlled collection, encrypted storage and strict access permissions, so only authorised people can view or handle sensitive information. Clear handling procedures also help preserve the evidence’s integrity, traceability and confidentiality throughout the cyber risk assessment.
Assessment evidence is protected through an evidence-handling process that preserves its confidentiality, integrity and provenance from initial identification through to reporting and disposal. This involves collecting only information relevant to the agreed assessment, documenting where it came from, limiting handling to authorised personnel, and maintaining an auditable record of every significant action.
Before evidence is gathered, the assessor should agree the scope, purpose and permitted methods with the organisation. This prevents unnecessary access to personal data, commercially sensitive material or systems outside the assessment boundary. A documented plan should identify the systems, accounts, logs, configurations and other sources that may be examined, together with any restrictions on copying, exporting or retaining them.
Evidence should be collected in a way that avoids changing the original source wherever reasonably possible. For example, an assessor may work from a copy of a log export, configuration file or disk image rather than altering the live system. The source, date, time, method of extraction and person responsible should be recorded. This information helps distinguish original evidence from working copies and allows another reviewer to understand how the material was obtained.
A chain-of-custody record supports this process. It should show:
- what the evidence is and which system or process produced it;
- when and by whom it was collected;
- where it has been held and who has handled it;
- which copies have been created and for what purpose;
- any transformation, redaction, analysis or export applied to it; and
- when it is approved for return, deletion or continued retention.
Integrity checks can help demonstrate that a file or image has not changed after collection. A cryptographic hash may be recorded when evidence is acquired and checked again when it is transferred or analysed. A matching result does not prove that the evidence itself is truthful, but it does provide useful assurance that the copy being reviewed is the same one that was originally captured.
Access should be based on role and necessity rather than general availability. An assessor may need access to technical logs, while a manager may only need the findings and risk summary. Separate permissions for collection, analysis, approval and reporting can reduce the chance of unauthorised alteration or inappropriate disclosure. Access records should be retained so that unusual activity can be investigated and permissions can be reviewed if the assessment team or project scope changes.
Evidence may contain information that is not needed to answer the assessment question, including employee details, customer records, credentials, source code or confidential business information. Redaction, pseudonymisation or filtering should be considered where it does not undermine the assessment. Passwords, private keys and other secrets should not be included in reports; if they are discovered, they should be handled through the organisation’s incident or credential-rotation process rather than reproduced for convenience.
Evidence should be separated from ordinary working documents and clearly labelled according to its sensitivity. This makes it less likely that a sensitive export will be emailed, copied to an unmanaged device or included accidentally in a wider project folder. Transfers should use an approved secure method, with the recipient and purpose recorded. Sending sensitive evidence through ordinary, unprotected messaging or personal storage creates avoidable exposure.
Retention should have a defined business and legal purpose. At the end of the assessment, the organisation and assessor should agree which material must be retained to support audit, regulatory or remediation requirements and which can be securely deleted. Deletion should cover working copies, temporary exports and duplicated files, not just the primary repository. Where evidence is retained, its owner, retention period and access permissions should remain clear.
Reports should contain enough supporting detail for findings to be assessed without unnecessarily reproducing sensitive raw data. For instance, a finding can usually refer to the affected asset, evidence type, relevant date and verification method while omitting full log contents or personal identifiers. The underlying material can be made available to an appropriately authorised reviewer when a finding needs to be challenged or validated.
These safeguards should be reflected in the assessment engagement terms and any arrangements with external analysts or cloud services. The documentation should cover confidentiality obligations, permitted processing, subcontractor involvement, data location where relevant, incident notification and secure disposal. Together, these controls make the evidence useful for defensible risk decisions without turning the assessment itself into an unnecessary source of information risk.
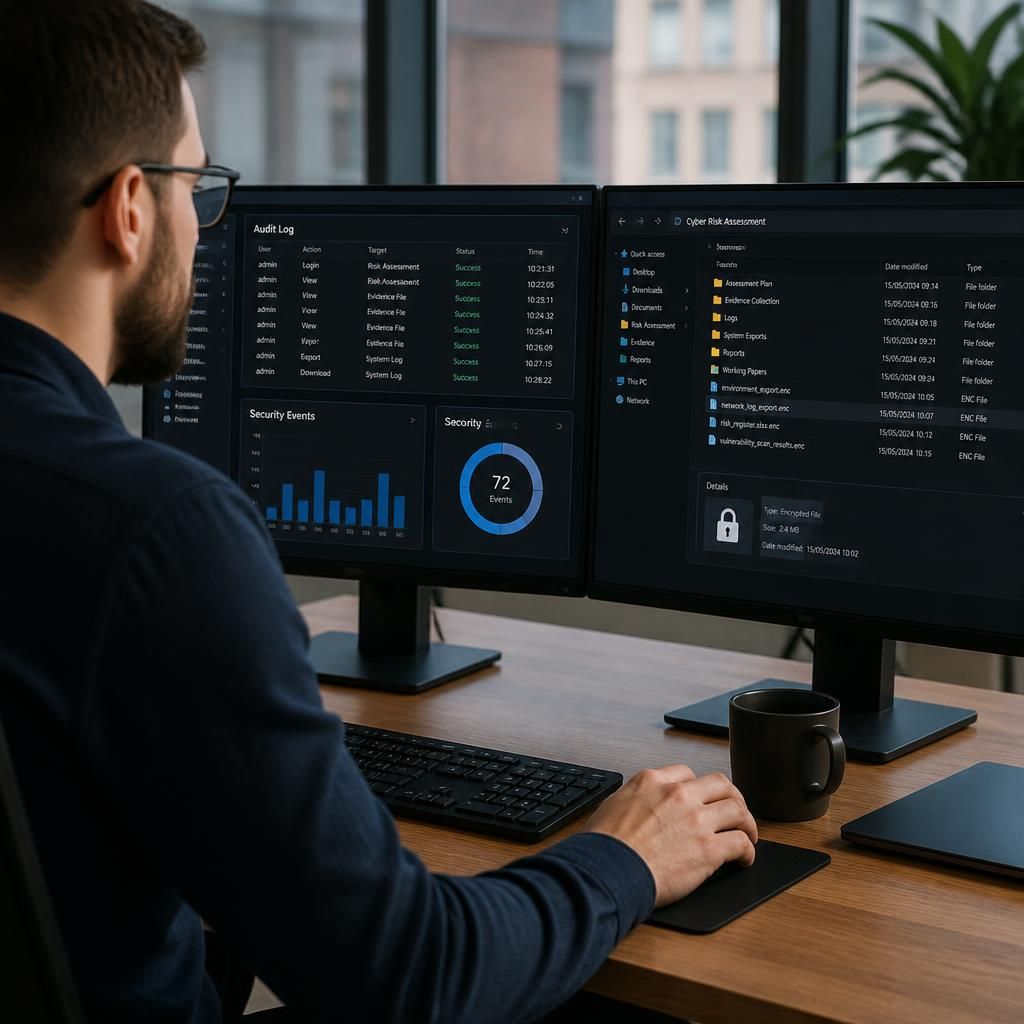
Assessment evidence is also protected by securing the assessor’s own collection and analysis environment, not only the organisation’s systems. Evidence should be handled from an approved, access-controlled device with current security controls, encrypted local storage and automatic screen locking. Personal devices and unapproved applications should not be used for storing, viewing or processing assessment material.
Where practical, collection should use dedicated assessment accounts with only the permissions required for the agreed task. Read-only access can reduce the risk of accidental changes, while temporary accounts, credentials and access tokens should be removed when the relevant work is complete. The assessor should also verify that collection scripts and tools come from a trusted source and record the tool version used, helping the organisation distinguish legitimate assessment activity from unauthorised access.