How are managed cloud IT changes tested before production?
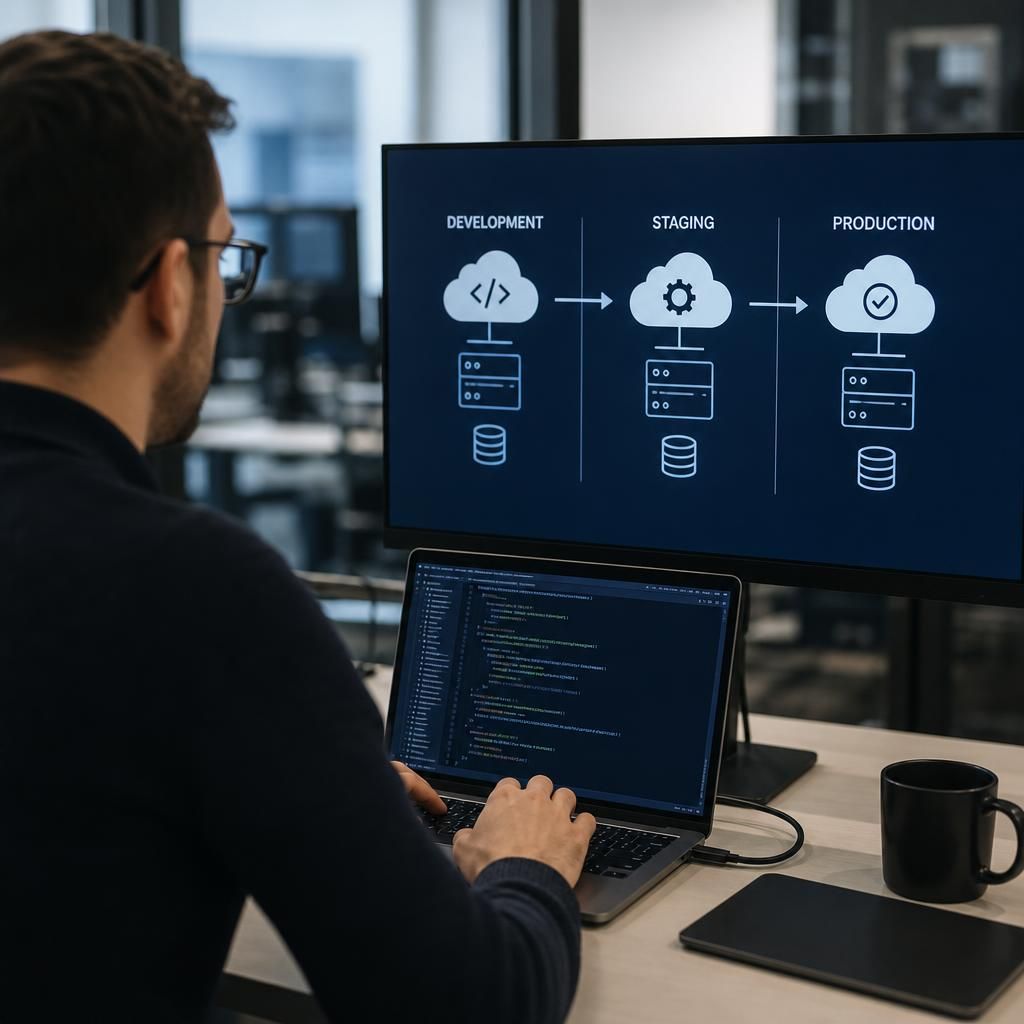
Managed cloud IT changes are tested in a separate staging environment before they are introduced into production systems. Testing typically verifies functionality, security, compatibility, performance and recovery steps, with any issues resolved and the change approved before deployment.
Managed cloud IT changes are tested through a controlled change process that links each proposed alteration to a documented risk assessment, test plan, approval record and rollback method. The aim is not simply to check whether a change works, but to establish what it could affect, how it will be introduced, how results will be observed and what action will follow if the expected result is not achieved.
Testing normally begins with a technical assessment of the proposed change. The IT team records the reason for the change, the cloud resources involved, dependent applications, integrations, identity permissions, network paths and business processes that could be affected. The change is then classified according to its potential impact. A routine configuration adjustment may need a lighter process than a change to identity services, storage, connectivity or a production application.
A written test plan should define:
- the exact configuration or code being changed;
- the conditions that must be met before testing starts;
- the expected results for each test;
- the people responsible for technical checks and business validation;
- the evidence that must be retained; and
- the conditions that would stop or reverse the deployment.
Where infrastructure is managed through repeatable configuration or code, the proposed version should be reviewed before it is applied. This helps identify accidental changes, excessive permissions, incorrect network rules and settings that differ from the intended design. Keeping configuration under version control also makes it possible to compare revisions and identify which change introduced a problem.
Test data needs careful handling. Real customer, employee or financial information should not be copied into a test environment unless there is a documented justification and suitable safeguards. Masked, anonymised or synthetic data is generally safer. Test accounts should use only the permissions needed for the scenario, and temporary resources, credentials and test files should be removed afterwards.
After technical validation, a controlled release may be used instead of changing every user or workload at once. For example, a provider might introduce the change to a limited service, user group or non-critical workload first. Results from that release can be reviewed before the same change is extended. This approach reduces the scope of any unexpected effect and provides evidence from a realistic operating context.
Monitoring forms part of the test rather than being added afterwards. Relevant logs, alerts, audit records, resource health indicators and application-level checks should be reviewed during and after the change. A successful deployment is not necessarily one that produces no error message; it should also leave normal dependencies, access controls, integrations and business processes working as intended.
Business validation is important where a technical change affects how staff work. A nominated user or process owner can confirm that essential tasks still function, such as accessing documents, processing an order, submitting a form or connecting to a line-of-business application. This check complements automated tests, which may not detect a workflow issue that is obvious to the people using the service.
Rollback planning should be specific rather than limited to the instruction to restore the previous version. The plan should identify what can be reversed, what data may have changed, how dependent systems will be handled and who can authorise the action. If a change cannot be safely reversed, the team should define an alternative recovery procedure before production deployment begins.
Once testing is complete, the results, exceptions and decisions should be recorded in the change record. Any failed test should be assessed rather than ignored: it may require a correction, a narrower release, an additional control or cancellation of the change. After deployment, a review can compare the observed outcome with the original objectives and capture lessons for future changes.
For businesses using managed cloud IT services, this evidence-based process provides visibility without requiring an in-house team to reproduce every technical test. S2 Technology Group can support organisations with managed cloud services alongside broader IT management and cyber security requirements, helping ensure that proposed changes are assessed in the context of the business’s existing technology environment.
A staging environment is only useful when it provides a realistic representation of production. Its operating system, application versions, identity controls, network routes, integrations and relevant cloud settings should be aligned with the live environment, while remaining isolated from real users and business data.
Differences between staging and production should be documented because they can make test results misleading. For example, a test may pass with a simulated integration but fail when production relies on an external service, different permissions or a larger workload. Where full duplication is impractical, the test plan should identify which conditions cannot be reproduced and include additional checks for those differences before release.