
What evidence does Cyber Essentials certification require?
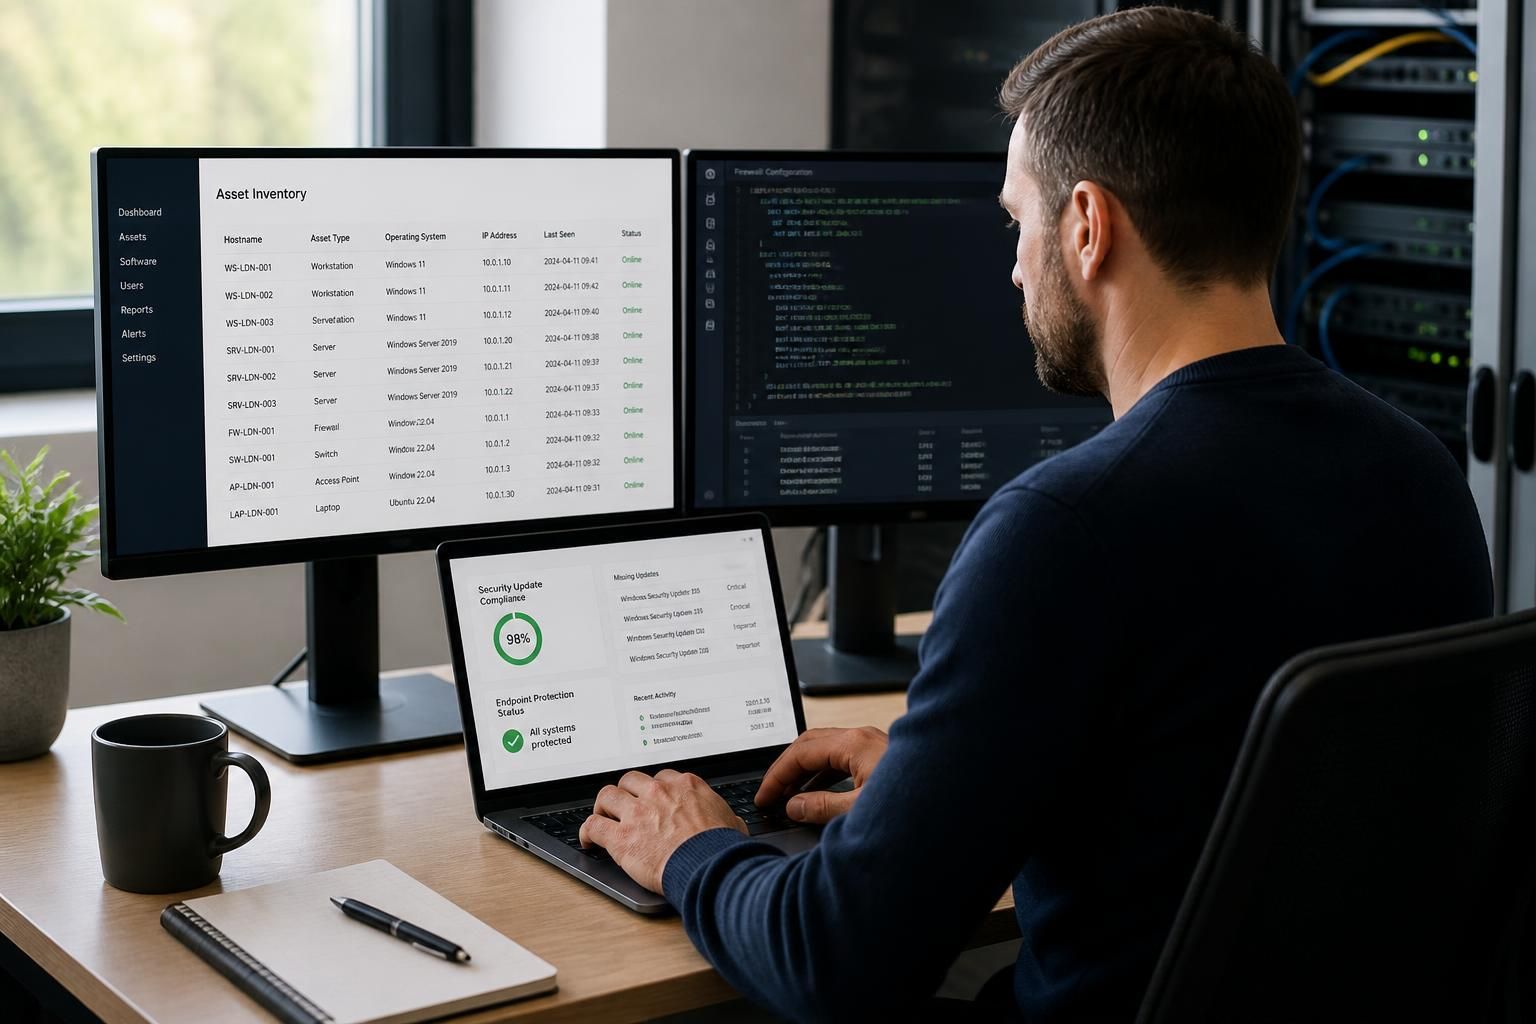
Cyber Essentials certification requires accurate answers to the scheme’s assessment questions, supported by evidence that the organisation has implemented the five technical controls: firewalls, secure configuration, security update management, user access control and malware protection. Useful evidence may include asset inventories, system configurations, update records, access-control settings and relevant security policies.
Cyber Essentials certification requires a completed and accurate self-assessment questionnaire, an authorised declaration and enough supporting information to substantiate the answers. The scheme does not prescribe one universal evidence pack or require every internal document to be submitted automatically. However, an organisation must be able to demonstrate that its answers reflect the systems, devices, users and security arrangements within the agreed assessment scope.
Evidence should show that security measures are actually implemented, consistently applied and maintained. A policy that describes an intended process is less useful on its own than a policy supported by configuration records, system reports or other operational evidence. The precise information requested can depend on the certification body’s assessment process and the answers given in the questionnaire.
Typical evidence includes:
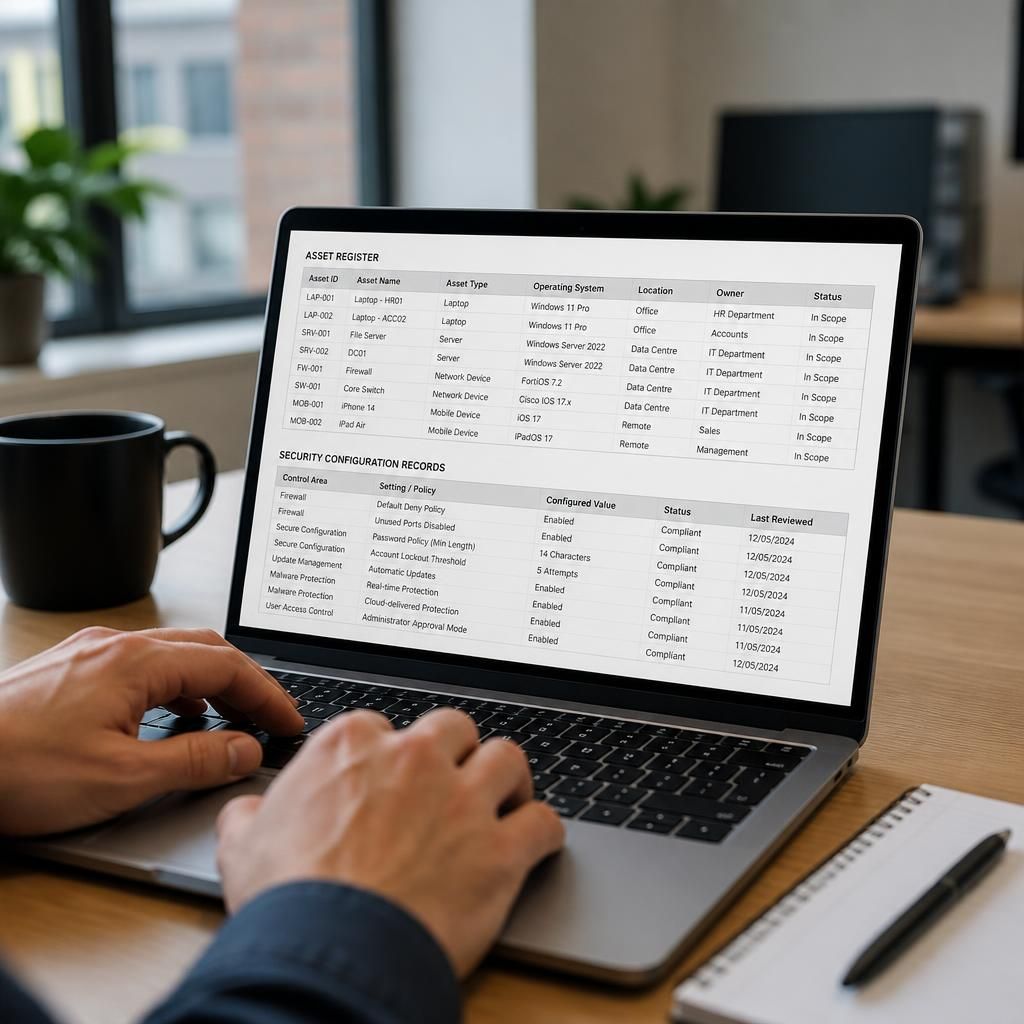
- Asset and scope records: an inventory of in-scope laptops, desktops, servers, network equipment, virtual machines, mobile devices and relevant cloud services. This should make clear which assets are included, who manages them and whether any systems have been excluded.
- Network documentation: firewall or router configurations, network diagrams, lists of exposed services and records showing how unauthorised inbound connections are restricted.
- Device configuration information: security baselines, build standards, hardening checklists and administrative settings for operating systems, applications and network devices.
- Update records: reports from patch-management or endpoint-management tools, update compliance information, exception records and documented treatment of devices that cannot be updated in the normal way.
- Account and privilege records: user lists, administrator accounts, group memberships, joiner and leaver records, access reviews and evidence that standard users do not routinely operate with unnecessary administrative rights.
- Malware-protection information: endpoint security status reports, policy settings, alerts, exclusions and evidence that protection is enabled and monitored on relevant devices.
- Policies and procedures: documented rules for account management, secure configuration, software updates, device use, remote access and handling exceptions. These should be current, approved and understood by the people responsible for applying them.
Evidence may take the form of exported reports, configuration files, screenshots, system-generated logs, asset registers, meeting records or controlled documents. Screenshots should show enough context to identify the system, setting and date where that is relevant. Reports are generally more persuasive when they cover the whole in-scope environment rather than a single example device.
The scope must be evidenced as well as the controls. An organisation should be able to explain how it identified the systems connected to its network, the devices used by staff, remote-working arrangements, hosted infrastructure and services managed by suppliers. If a cloud platform or outsourced service is part of the business environment, the organisation should understand which security responsibilities remain with it and which are handled by the provider. Supplier documentation can support the assessment, but it does not automatically remove the organisation’s responsibility for its own users, devices or configuration.
Where the organisation has made an exception, the evidence should explain what is affected, why the exception exists and what compensating action or remediation is in place. Unsupported software, unusual network connections, shared administrative accounts and devices that cannot receive updates should not simply be omitted from the records. Leaving a weakness out of an inventory can create an inaccurate assessment scope and lead to an answer that cannot be supported.
Evidence should also be internally consistent. For example, the asset register should align with endpoint-management reports, administrator accounts should match access records, and the stated scope should agree with network documentation. Differences do not necessarily mean certification is impossible, but they need to be investigated and corrected or clearly explained before the questionnaire is submitted.
For the standard Cyber Essentials assessment, the key submission is the completed questionnaire and declaration rather than a large document bundle. The organisation is responsible for answering the questions accurately and retaining the records behind those answers. A certification body may seek clarification or ask for additional information, particularly where an answer is unclear, an exception is disclosed or the stated arrangements appear inconsistent.
Cyber Essentials Plus uses the same underlying security requirements but adds an independent technical assessment. In that process, assessors test selected systems and configurations rather than relying only on written answers. Evidence prepared for the basic certification can therefore help organise the environment, but it does not replace the technical checks carried out during the Plus assessment.
A practical preparation process is to:
- Define and document the certification scope before gathering records.
- Compare the asset register with network, endpoint and cloud-management information.
- Review user and administrator accounts, including remote and supplier access.
- Export current configuration and update reports from the systems used to manage devices.
- Record exceptions, ownership and corrective actions rather than relying on informal explanations.
- Check that policies and technical records describe the same arrangements.
- Have an appropriately authorised person review and approve the final questionnaire and declaration.
In short, the strongest evidence is current, traceable and representative of the entire certification scope. S2 Technology Group can help organisations around Stourbridge, Kinver, Wordsley, Kingswinford, Kidderminster, Halesowen, Dudley and neighbouring areas interpret the requirements, identify evidence gaps and organise the technical records needed to support an accurate assessment.
Evidence prepared for a Cyber Essentials assessment should be supplied securely and contain only the information needed to support the relevant answer. Assessment records can include sensitive technical details, personal data and information about privileged accounts, so they should not be circulated through uncontrolled channels or left in broadly accessible folders.
Before sharing a report or screenshot, remove passwords, authentication tokens and unrelated personal information, while leaving enough context for the assessor to understand what the record shows. Keep the original, unredacted version in a restricted location, record who approved the extract and use read-only copies where possible. This approach allows the organisation to substantiate its answers without creating an additional information-security risk.